

IoT_vuln
 c0nyy/iot_vuln
Proof-of-concept exploits for IoT device vulnerabilities, including TOTOLINK login bypass CVEs, with detailed technical analysis and reproduction…
exploitationhardware-iot-securityiot-security+2
c0nyy/iot_vulnProof-of-concept exploits for IoT device vulnerabilities, including TOTOLINK login bypass CVEs, with detailed technical analysis and reproduction…
 redfox-security/digisol-dg-gr1321-s-improper-access-control-cve-2024-4231
Exploit for CVE-2024-4231, an improper access control vulnerability in Digisol DG-GR1321 routers, allowing unauthorized access to sensitive…
 dearpan/cve-2018-9995
Exploit for CVE-2018-9995 targeting DVR devices. Sends a crafted Cookie header to retrieve plaintext admin credentials from the web control panel.
 str0ng4le/cve-2022-30114
Proof-of-concept exploit for CVE-2022-30114, a heap-based buffer overflow in Fastweb FastGate routers. Sends a crafted HTTP Authorization header to…
 exploitwritter/cve-2022-25062
This script exploits a vulnerability (IoF) in the TPLink WR840N router, using a field for injecting code in the module DNS.
 db44k/cve-2020-12124
Proof-of-concept exploit for CVE-2020-12124, a command injection vulnerability in Wavlink WN530H4 routers via the /cgi-bin/live_api.cgi endpoint,…
 vanlam2001/netis-n5vn-ac1200-dos
Proof-of-concept exploit for a buffer overflow vulnerability (CVE-2024-44596) in Netis N5VN AC1200 routers, causing a denial of service by crashing…

 miguelhamal/cve-2019-19393
Proof-of-concept for stored XSS vulnerability in Rittal CMC PU III web management interface, enabling persistent client-side script injection before…
 oiivr/turvan6rkus-cve-2024-3273
Turvanõrkuse CVE 2024 3273 analüüs: D-Link seadmete käsusüst
 redfox-security/digisol-dg--gr1321-s-password-storage-in-plaintext--cve-2024-4232
Proof-of-concept exploit for CVE-2024-4232 targeting plaintext password storage in Digisol DG-GR1321 routers. Demonstrates extraction of credentials…
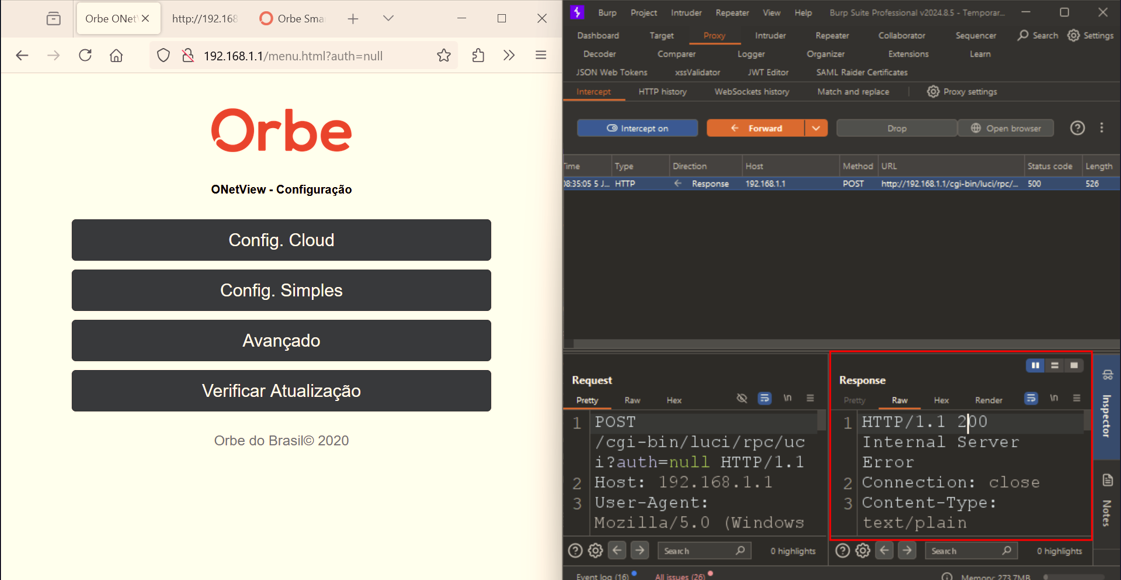 kuk3n4n/cve-2024-57778
An issue in Orbe ONetView Roteador Onet-1200 Orbe 1680210096 allows a remote attacker to escalate privileges via the servers response from status…
 g-rubert/cve-2021-46108
Proof-of-concept for stored cross-site scripting (XSS) vulnerability in D-Link DSL-2730E routers via the username parameter on the maintenance…
 tpdlshdmlrkfmcla/backdoor.mirai.helloworld
backdoor.mirai.helloworld cve2018-20561, cve-2018-10562 해킹
 yarienkiva/honeypot-dlink-cve-2024-3273
Quick and dirty honeypot for CVE-2024-3273
 ajaymt6/ultramangaia
A login bypass(CVE-2019-18371) and a command injection vulnerability(CVE-2019-18370) in Xiaomi Router R3G up to versi…
