
Archived
jboss-autopwn
 spiderlabs/jboss-autopwn
A JBoss script for obtaining remote shell access
command-and-controlexploitationpayload-generation+4
spiderlabs/jboss-autopwnA JBoss script for obtaining remote shell access
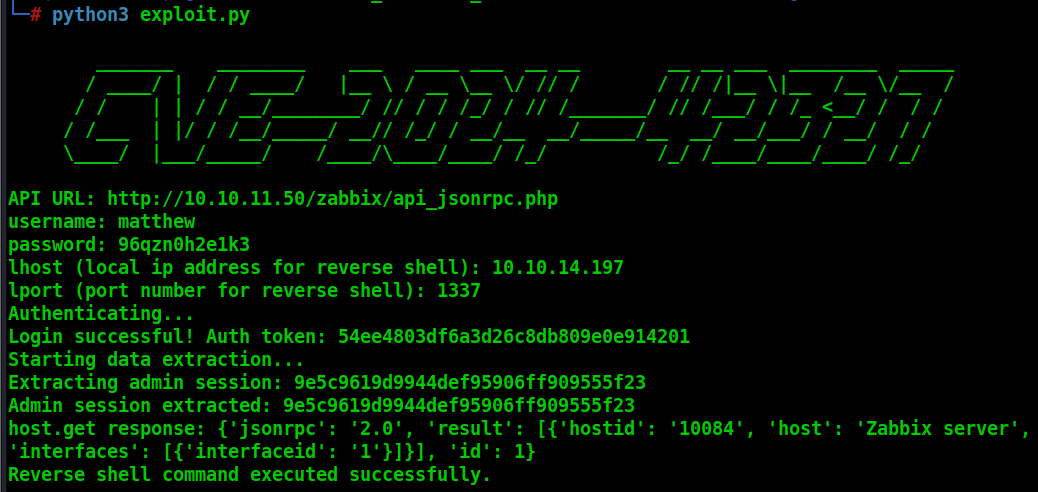 bridgeralderson/zabbix-cve-2024-42327-sql-injection-rce
Exploits Zabbix SQL injection (CVE-2024-42327) to extract admin session and execute commands via API, achieving reverse shell.
 nikn0laty/exploit-for-dolibarr-17.0.0-cve-2023-30253
Reverse Shell POC exploit for Dolibarr <= 17.0.0 (CVE-2023-30253), PHP Code Injection
 can0i0ever0enter/cve-2023-45878
Python exploit for CVE-2023-45878, an unauthenticated arbitrary file upload in Gibbon CMS, enabling RCE via webshell upload and interactive shell…
 kentox493/cve-2026-42945_nginxrift
Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…
 liusec/wp-cve-2016-10033
Docker-based lab environment for WordPress <= 4.6 remote code execution via PHPMailer (CVE-2016-10033), including PoC, webshell upload, and reverse…
 bishben/xwiki-15.10.8-reverse-shell-cve-2025-24893
CVE-2025-24893 RCE exploit for XWiki with reverse shell capability
 cyberdesu/elastix-2.2.0-cve-2012-4869
Python exploit script for Elastix 2.2.0 LFI vulnerability (CVE-2012-4869) enabling remote code execution via Perl reverse shell payload injection.
 hadrian3689/cachet_2.4.0-dev
Python exploit script for CVE-2021-39174 Cachet information disclosure and remote code execution via Twig Server-Side Template Injection, with…
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
 mcorybillington/cve-2025-34322_cve-2025-34323_nagios_log_server
Proof of Concept exploits for CVE-2025-34322 and CVE-2025-34323 in Nagios Log Server
 d4t4s3c/offensivereverseshellcheatsheet
Curated cheat sheet of reverse shell payloads in Bash, Netcat, PHP, PowerShell, Python, Perl, Ruby, and msfvenom, plus webshells, log poisoning, and…
 t3l3machus/hoaxshell
A Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.
 0katz/cve-2019-12476
PoC for CVE-2019-12476, a Windows authentication bypass in ManageEngine ADSelfService Plus that provides an unauthenticated SYSTEM shell via crafted…
 peterpan0927/tfc-chrome-v8-bug-cve-2021-38001-poc
Proof-of-concept exploit for CVE-2021-38001, a Chrome V8 JavaScript engine vulnerability. Demonstrates exploitation via d8 shell with a malicious…
 thecybergeek/cve-2020-5844
Python proof-of-concept for authenticated remote code execution in PandoraFMS 7.0-NG 742, enabling admin users to upload malicious PHP and obtain a…
 maskcybersecurityteam/cve-2022-26134_behinder_memshell
Java-based exploit for CVE-2022-26134 that deploys a Behinder memory shell on vulnerable Atlassian Confluence servers for remote command execution.
 binneko/cve-2025-50286
Authenticated RCE exploit for Grav CMS via plugin upload, demonstrating arbitrary PHP code execution and reverse shell.