

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems Security
General Purpose Utilities
Indicator of Compromise (IOC) Management
OSINT (Open Source Intelligence)
Packet Sniffing & Analysis
Password Cracking
Penetration Testing Frameworks
Phishing Tools
Privilege Escalation
Reconnaissance
Static Analysis
Vulnerability Scanners
Web Vulnerability Scanners
Wi-Fi Auditing
Bluetooth Security
Container Security
Dynamic Analysis (Sandboxing)
Encryption/Decryption Tools
Exploit Frameworks
Identity Management
iOS Security
IoT Security
Memory Forensics
Network Mapping
OSINT for Social Engineering
Password Attacks
Payload Generation
Persistence Mechanisms
Port Scanning
Static Code Analysis (SAST)
Threat Feeds & Aggregators
Vulnerability Analysis
Web Proxies & Interception
Code Analysis
DNS & Subdomain Enumeration
Dynamic Code Analysis (DAST)
Exploitation
Hash Analysis
IDS/IPS Evasion
Impersonation Tools
Lateral Movement
Mobile App Pentesting
Network Forensics
Reverse Engineering
RFID/NFC Tools
SCADA/ICS Security
Scripting & Automation
Serverless Security
Shellcode
Web Application Exploitation
API Security Testing
Configuration Auditing
Data Exfiltration
Debuggers
Forensics
Information Gathering
Mobile Forensics
Network Access Control
Post-Exploitation
Security Virtualization
Phishing
WAF Bypass
Web Security
Fuzzing
Network Security
Steganography
Wireless Security
Data Recovery
Malware Analysis
Digital Forensics
Hardware Hacking
Cryptography
CTF
Penetration Testing
Cloud Security
DevSecOps
Mobile Security
Privacy
Command and Control
Social Engineering
Hardware Security
Utilities & Frameworks
Hardware & IoT Security
Secret Detection
Binary Analysis
Threat Intelligence
Identity & Access Management (IAM)
Supply Chain Security
Authentication
Machine Learning
Intrusion Detection
Papers & Research
Misconfiguration
Subdomain Enumeration
Email Harvesting
Learning & Education
AI-Assisted Reversing
DNS Fuzzing
Red Teaming
Incident Response
Crawler
Curated Resources
Remote Access Tool
Shellcode Generation
Payload Development
Remote Access Trojan
API Security
Anti-Bot
Fingerprint Spoofing
CAPTCHA Bypass
Email Security
DNS Analysis
Chaos Engineering
Learning Paths & Courses
Container Escape
AI Security
Database Security
Firmware Analysis
Anomaly Detection
Log Analysis
Adversarial Attack
Binary Exploitation
Labs & Practice
NewestRelevanceMost popularRecently updated
956 results
noPac preview

noPac

GitHubwaterrr/nopac

Exploiting CVE-2021-42278 and CVE-2021-42287
exploitationexploit-frameworkspenetration-testing+3
64 years ago
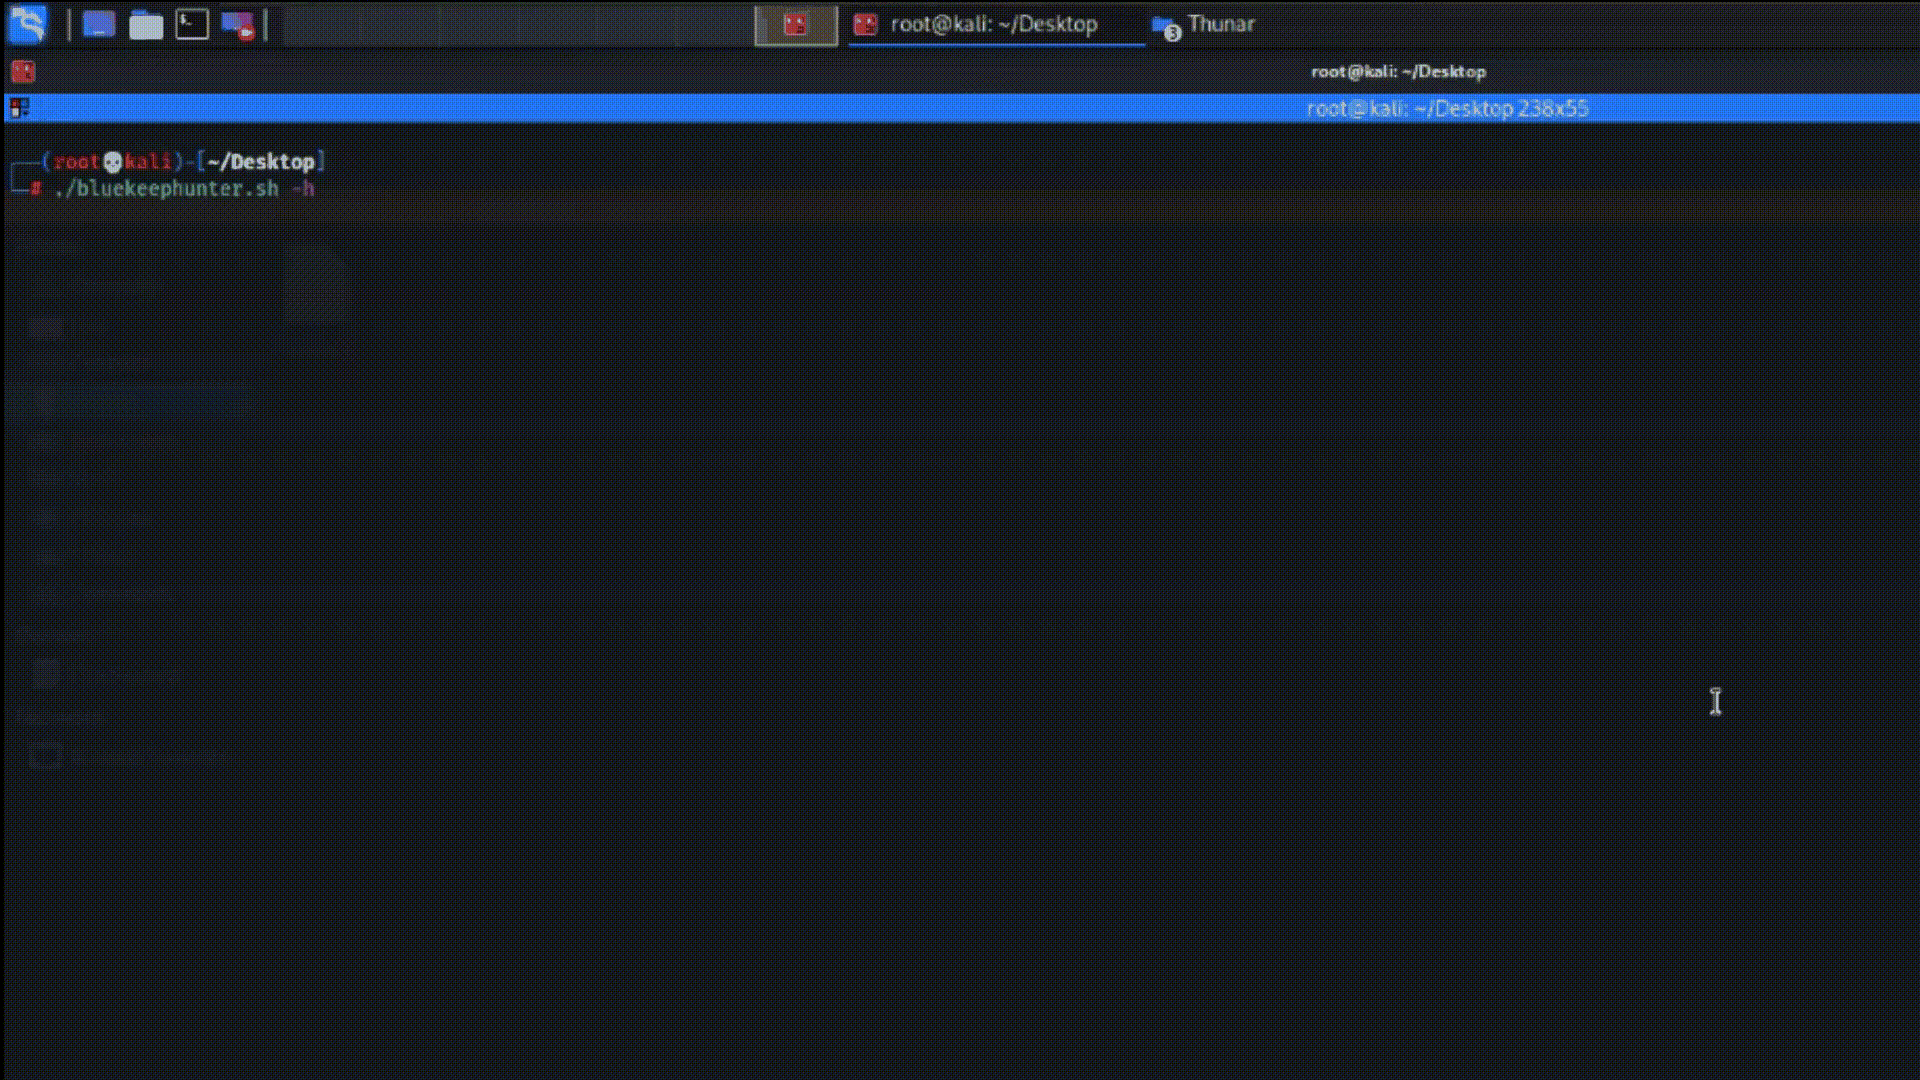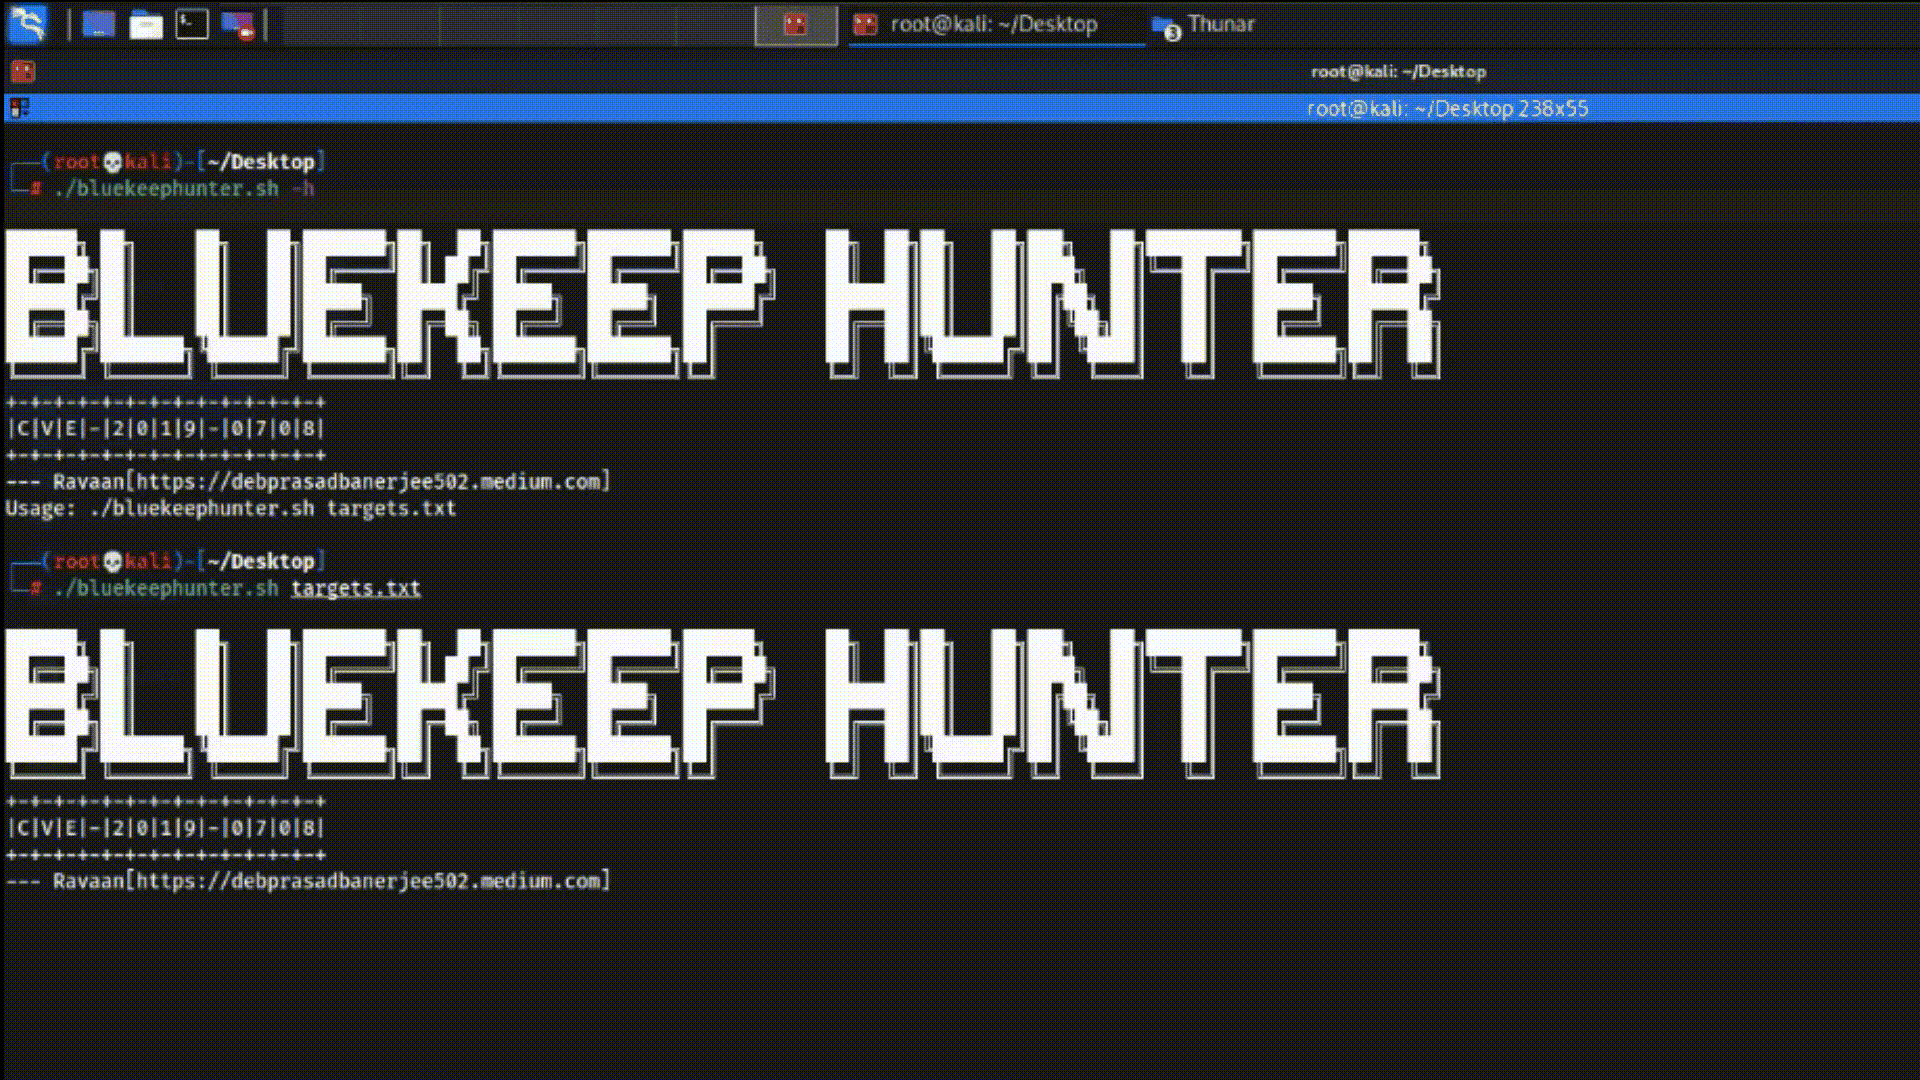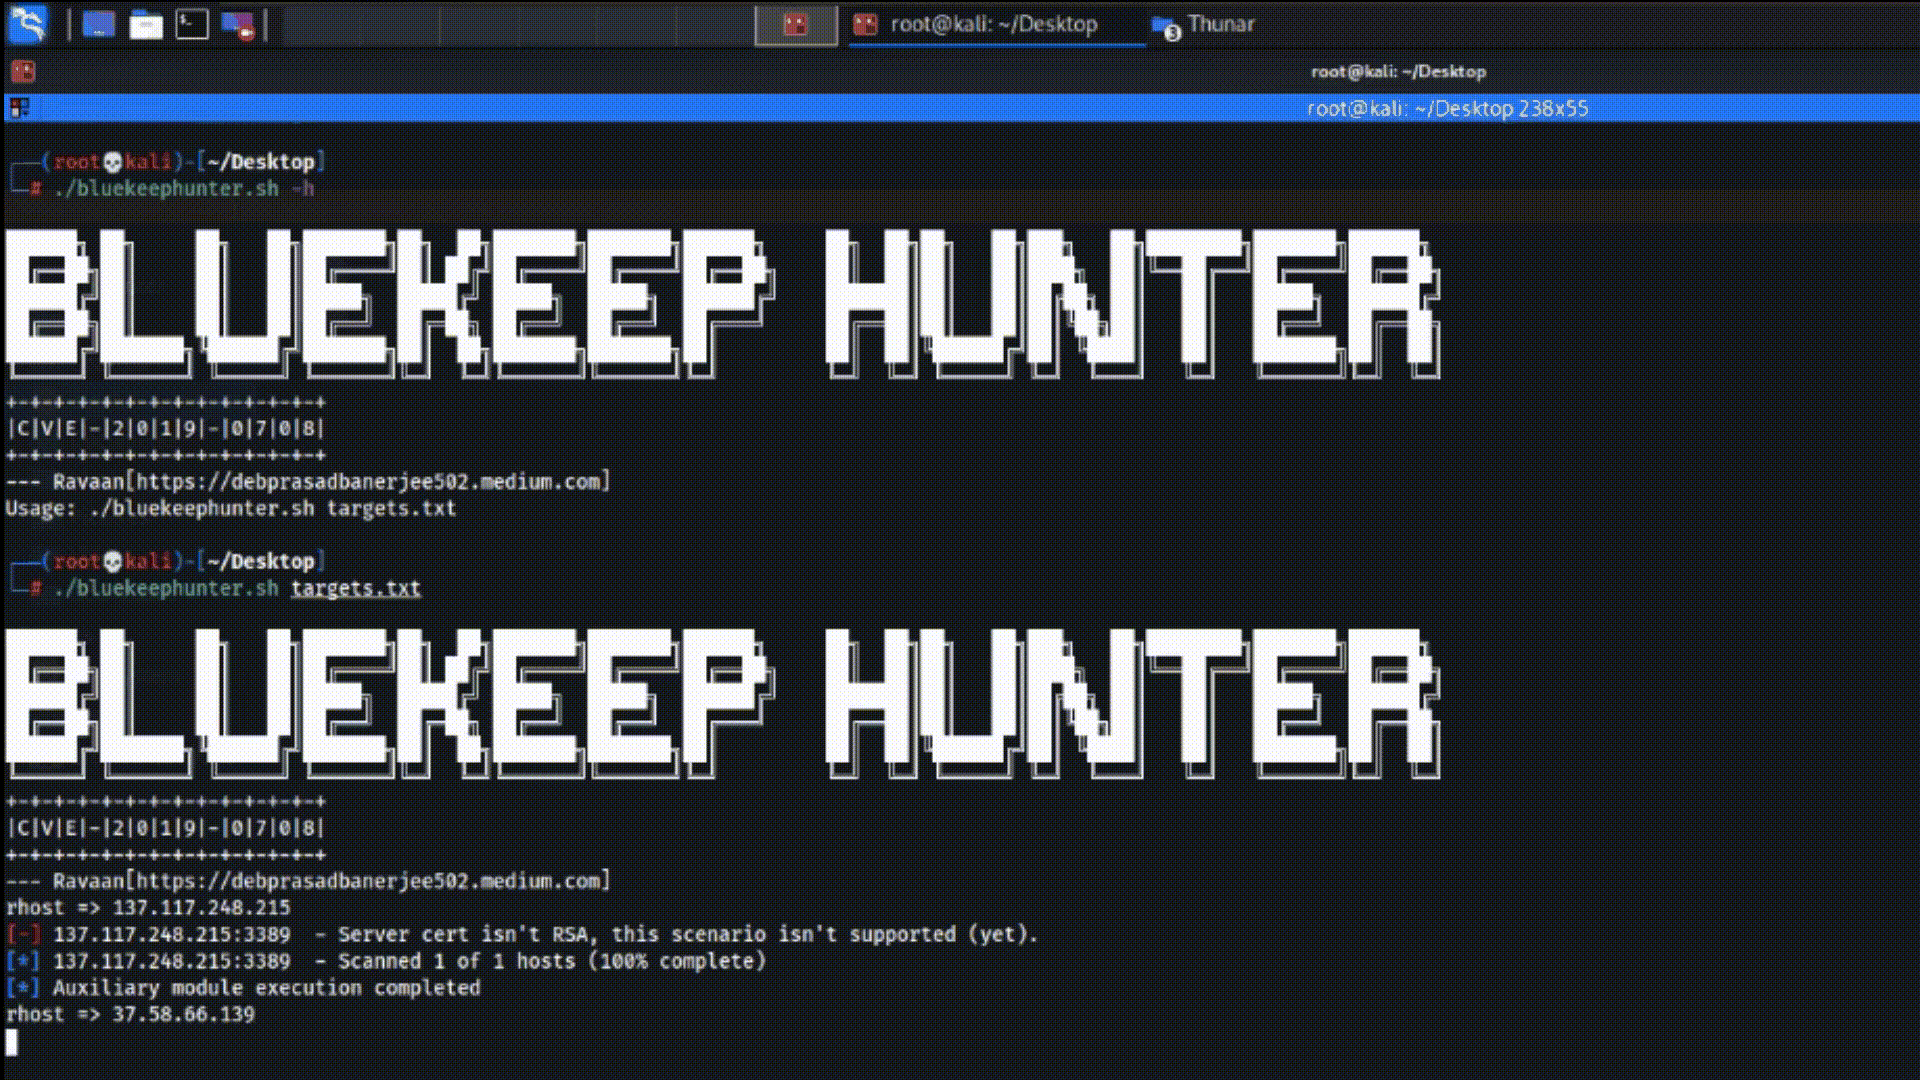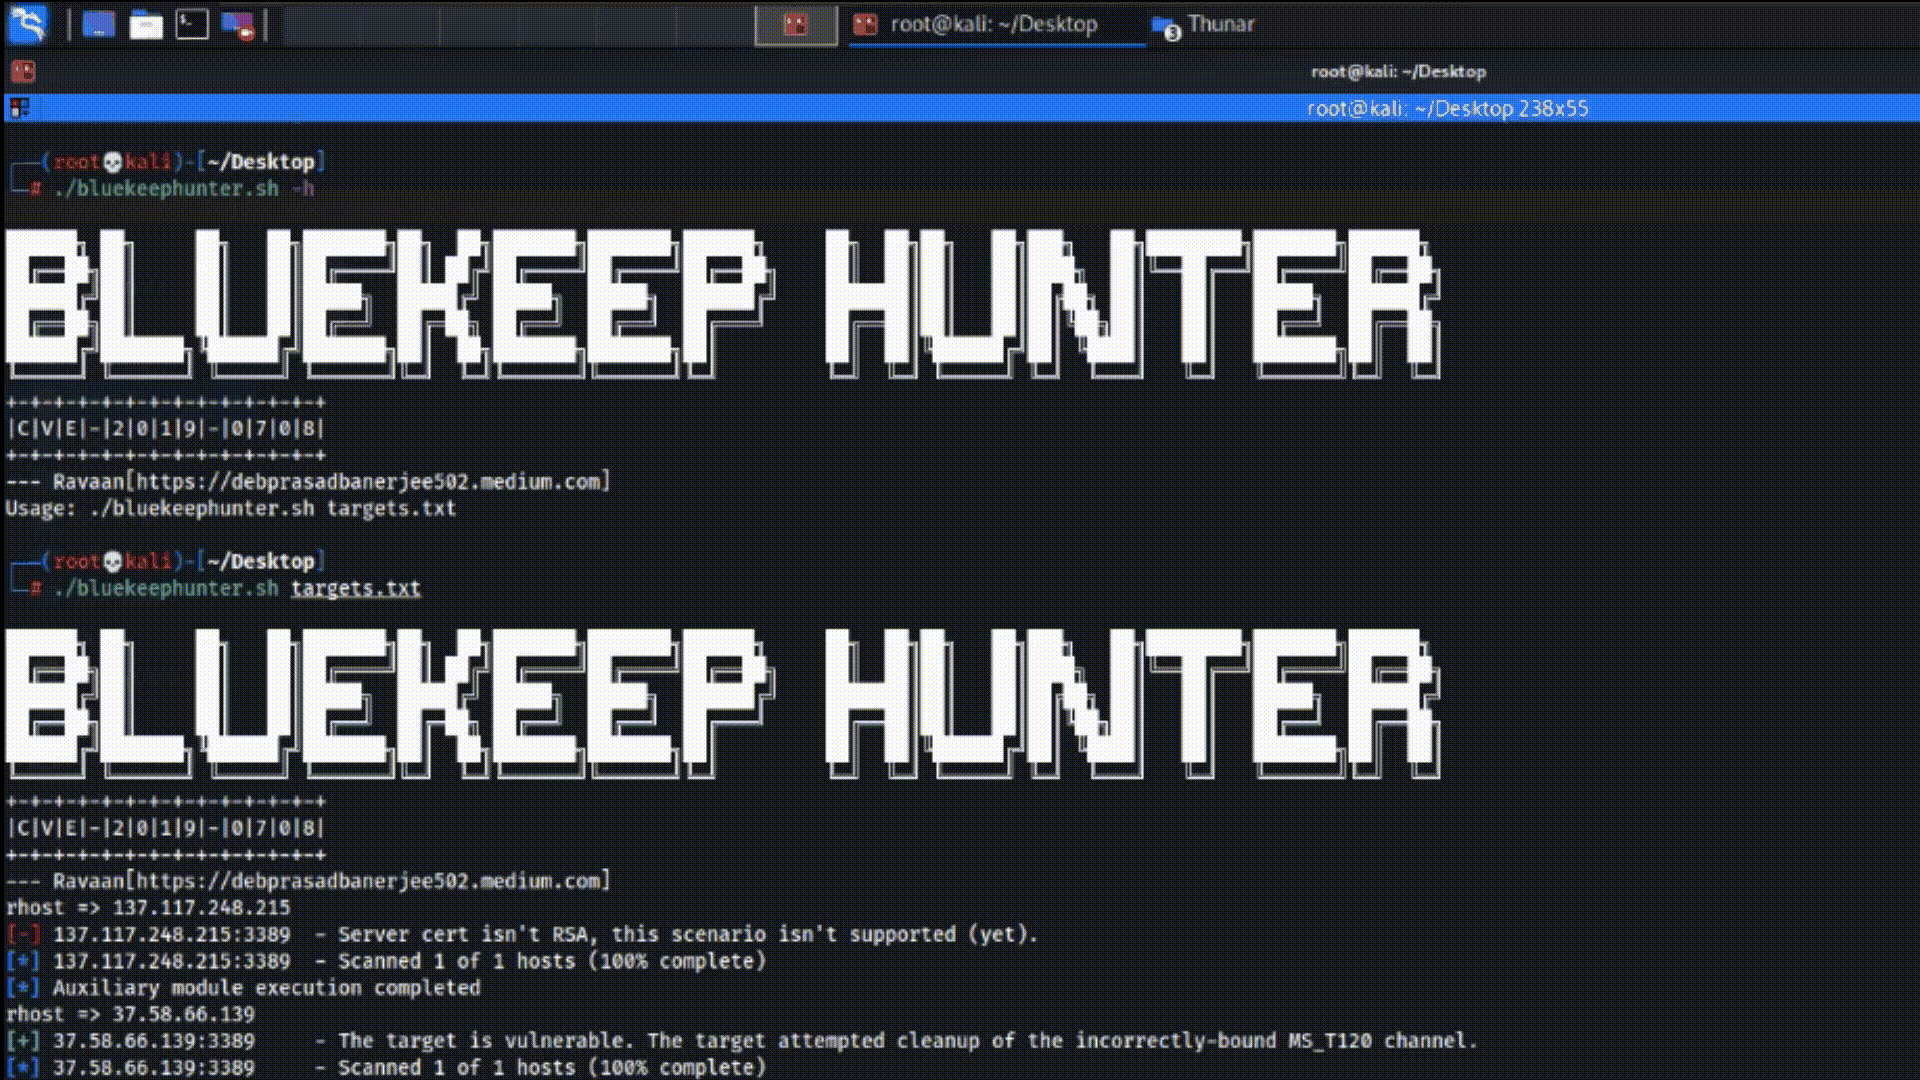
Bluekeep-Hunter preview

Bluekeep-Hunter

GitHubravaan21/bluekeep-hunter

CVE-2019-0708, A tool which mass hunts for bluekeep vulnerability for exploitation.
exploitationexploit-frameworksnetwork-security+3
43 years ago
LAB1-metasploitable preview

LAB1-metasploitable

GitHubaboubacar70/lab1-metasploitable

Exploitation des vulnérabilités sur la version vsftpd 2.3.4 du service ftp (CVE-2011-2523)

exploitationexploit-frameworkspayload-development+3
2 months ago
CVE-2018-4878 preview

CVE-2018-4878

GitHubb0fh/cve-2018-4878

Metasploit module for CVE-2018-4878

exploitationexploit-frameworkspayload-development+3
28 years ago
internal-penetration-testing-project-using-Metasploit preview

internal-penetration-testing-project-using-Metasploit

GitHubabdullah50i/internal-penetration-testing-project-using-metasploit

Initialized & connected PostgreSQL to Metasploit. Reconnoitered 10.1.16.0/24 with Nmap and imported results. Enumerated hosts/services using SYN, SMB…
exploitationexploit-frameworksinformation-gathering+6
3 months ago
p4wned preview

p4wned

GitHubflyingllama87/p4wned

Perforce security research and tools - CVE-2026-6043
exploitationexploit-frameworksinformation-gathering+6
25 months ago
CVE-2013-1081 preview

CVE-2013-1081

GitHubsteponequit/cve-2013-1081

Novell ZENworks Mobile Management - LFI RCE

exploitationexploit-frameworkspayload-development+3
213 years ago
CVE-2016-5639 preview

CVE-2016-5639

GitHubxfox64x/cve-2016-5639

Crestron AirMedia AM-100 Traversal and Hashdump Metasploit Modules
exploitationexploit-frameworksinformation-gathering+3
26 years ago
CVE-2020-5902 preview

CVE-2020-5902

GitHubmurataydemir/cve-2020-5902

[CVE-2020-5902] F5 BIG-IP Remote Code Execution (RCE)

exploitationexploit-frameworkspenetration-testing+3
26 years ago
wp2shell-checker preview

wp2shell-checker

GitHub0xjessie21/wp2shell-checker

WordPress Core Unauthenticated RCE (CVE-2026-63030, CVE-2026-60137)

exploitationnetwork-securitypenetration-testing-frameworks+2
14 months ago
veritas-backup preview

veritas-backup

GitHubhyderpwn/veritas-backup

Metasploit module for exploiting Veritas Backup Exec Agent SHA-auth NDMP vulnerability to achieve remote code execution.
exploitationexploit-frameworkspenetration-testing+2
12 months ago
CVE-2020-0796 preview

CVE-2020-0796

GitHubjulixsalas/cve-2020-0796

Metasploit Auxiliary module for scanning and detecting CVE-2020-0796 (SMBGhost) vulnerability in Windows SMBv3 implementations.

exploitationexploit-frameworksnetwork-security+3
14 years ago
CVE-2019-0708-Msf-- preview

CVE-2019-0708-Msf--

GitHubcream-sec/cve-2019-0708-msf--

CVE-2019-0708-Msf-验证

exploitationexploit-frameworksinformation-gathering+3
17 years ago
CVE-2026-31431 preview

CVE-2026-31431

GitHubxd20111/cve-2026-31431

Documentation and analysis of a local privilege escalation vulnerability in the Linux kernel's authencesn template via AF_ALG and splice(), including…
exploitationexploit-frameworksprivilege-escalation+1
6 months ago
CVE-2021-31800 preview

CVE-2021-31800

GitHublouzogh/cve-2021-31800

CVE-2021-31800 POC

exploitationexploit-frameworksnetwork-security+3
24 years ago
CVE-2026-31431 preview

CVE-2026-31431

GitHubstarxsky/cve-2026-31431

Provides attack source code and sniffing tools for CVE-2026-31431, a kernel vulnerability, along with mitigation instructions including disabling the…
exploitationexploit-frameworkspenetration-testing+1
6 months ago
Copy-Fail preview

Copy-Fail

GitHubp401a-ops/copy-fail

Detects and exploits CVE-2026-31431 (Copy Fail) local privilege escalation on Astra Linux, with Python 3.7+ compatibility and one-liner deployment.
exploitationexploit-frameworkspenetration-testing+2
6 months ago
CVE-2026-31431 preview

CVE-2026-31431

GitHub0xn7y/cve-2026-31431

Logic bug in the kernel's authencesn cryptographic template that escalate privilege

exploitationexploit-frameworksprivilege-escalation+1
16 months ago
Previous1…101112…54Next
Sources curated into a security tool Repositories, feeds, communities and curated indexes flow through selection, classification, enrichment and translation into an illustrative tool record. ISC License Copyright (c) 2026 Lucide Icons and Contributors Permission to use, copy, modify, and/or distribute this software for any purpose with or without fee is hereby granted, provided that the above copyright notice and this permission notice appear in all copies. THE SOFTWARE IS PROVIDED "AS IS" AND THE AUTHOR DISCLAIMS ALL WARRANTIES WITH REGARD TO THIS SOFTWARE INCLUDING ALL IMPLIED WARRANTIES OF MERCHANTABILITY AND FITNESS. IN NO EVENT SHALL THE AUTHOR BE LIABLE FOR ANY SPECIAL, DIRECT, INDIRECT, OR CONSEQUENTIAL DAMAGES OR ANY DAMAGES WHATSOEVER RESULTING FROM LOSS OF USE, DATA OR PROFITS, WHETHER IN AN ACTION OF CONTRACT, NEGLIGENCE OR OTHER TORTIOUS ACTION, ARISING OUT OF OR IN CONNECTION WITH THE USE OR PERFORMANCE OF THIS SOFTWARE. --- The following Lucide icons are derived from the Feather project: airplay, alert-circle, alert-octagon, alert-triangle, aperture, arrow-down-circle, arrow-down-left, arrow-down-right, arrow-down, arrow-left-circle, arrow-left, arrow-right-circle, arrow-right, arrow-up-circle, arrow-up-left, arrow-up-right, arrow-up, at-sign, calendar, cast, check, chevron-down, chevron-left, chevron-right, chevron-up, chevrons-down, chevrons-left, chevrons-right, chevrons-up, circle, clipboard, clock, code, columns, command, compass, corner-down-left, corner-down-right, corner-left-down, corner-left-up, corner-right-down, corner-right-up, corner-up-left, corner-up-right, crosshair, database, divide-circle, divide-square, dollar-sign, download, external-link, feather, frown, hash, headphones, help-circle, info, italic, key, layout, life-buoy, link-2, link, loader, lock, log-in, log-out, maximize, meh, minimize, minimize-2, minus-circle, minus-square, minus, monitor, moon, more-horizontal, more-vertical, move, music, navigation-2, navigation, octagon, pause-circle, percent, plus-circle, plus-square, plus, power, radio, rss, search, server, share, shopping-bag, sidebar, smartphone, smile, square, table-2, tablet, target, terminal, trash-2, trash, triangle, tv, type, upload, x-circle, x-octagon, x-square, x, zoom-in, zoom-out The MIT License (MIT) (for the icons listed above) Copyright (c) 2013-present Cole Bemis Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions: The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software. THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
Repositories
GitHub & GitLab
Security feeds
Blogs, RSS & Atom
Communities
Reddit, X & submissions
Curated indexes
Security lists & trends
Curate & select
Classification
Enrichment
Translation
Fictional tool and repository. The description, categories, stars, forks and views are illustrative examples, not live or verified data. Fictional tool and repository. The description, categories, stars, forks and views are illustrative examples, not live or verified data. {"fictional":true,"name":"Tool","version":"1.0.1","repository":"owner/tool","live_metrics":false,"example_metrics":{"stars":1200,"forks":128,"views":8600}}
Tool
v1.0.1 owner/tool
Discover assets and review
HTTP security headers.
Reconnaissance
Web security
1,200 stars — Fictional example1.2k 128 forks — Fictional example128 8,600 views — Fictional example8.6k
Sources curated into a security tool Repositories, feeds, communities and curated indexes flow through selection, classification, enrichment and translation into an illustrative tool record. ISC License Copyright (c) 2026 Lucide Icons and Contributors Permission to use, copy, modify, and/or distribute this software for any purpose with or without fee is hereby granted, provided that the above copyright notice and this permission notice appear in all copies. THE SOFTWARE IS PROVIDED "AS IS" AND THE AUTHOR DISCLAIMS ALL WARRANTIES WITH REGARD TO THIS SOFTWARE INCLUDING ALL IMPLIED WARRANTIES OF MERCHANTABILITY AND FITNESS. IN NO EVENT SHALL THE AUTHOR BE LIABLE FOR ANY SPECIAL, DIRECT, INDIRECT, OR CONSEQUENTIAL DAMAGES OR ANY DAMAGES WHATSOEVER RESULTING FROM LOSS OF USE, DATA OR PROFITS, WHETHER IN AN ACTION OF CONTRACT, NEGLIGENCE OR OTHER TORTIOUS ACTION, ARISING OUT OF OR IN CONNECTION WITH THE USE OR PERFORMANCE OF THIS SOFTWARE. --- The following Lucide icons are derived from the Feather project: airplay, alert-circle, alert-octagon, alert-triangle, aperture, arrow-down-circle, arrow-down-left, arrow-down-right, arrow-down, arrow-left-circle, arrow-left, arrow-right-circle, arrow-right, arrow-up-circle, arrow-up-left, arrow-up-right, arrow-up, at-sign, calendar, cast, check, chevron-down, chevron-left, chevron-right, chevron-up, chevrons-down, chevrons-left, chevrons-right, chevrons-up, circle, clipboard, clock, code, columns, command, compass, corner-down-left, corner-down-right, corner-left-down, corner-left-up, corner-right-down, corner-right-up, corner-up-left, corner-up-right, crosshair, database, divide-circle, divide-square, dollar-sign, download, external-link, feather, frown, hash, headphones, help-circle, info, italic, key, layout, life-buoy, link-2, link, loader, lock, log-in, log-out, maximize, meh, minimize, minimize-2, minus-circle, minus-square, minus, monitor, moon, more-horizontal, more-vertical, move, music, navigation-2, navigation, octagon, pause-circle, percent, plus-circle, plus-square, plus, power, radio, rss, search, server, share, shopping-bag, sidebar, smartphone, smile, square, table-2, tablet, target, terminal, trash-2, trash, triangle, tv, type, upload, x-circle, x-octagon, x-square, x, zoom-in, zoom-out The MIT License (MIT) (for the icons listed above) Copyright (c) 2013-present Cole Bemis Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions: The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software. THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
Repositories
GitHub & GitLab
Security feeds
Blogs, RSS & Atom
Communities
Social & submissions
Curated indexes
Security lists & trends
Curate & classify
Enrich & translate
Fictional tool and repository. The description, categories, stars, forks and views are illustrative examples, not live or verified data. Fictional tool and repository. The description, categories, stars, forks and views are illustrative examples, not live or verified data. {"fictional":true,"name":"Tool","version":"1.0.1","repository":"owner/tool","live_metrics":false,"example_metrics":{"stars":1200,"forks":128,"views":8600}}
Tool
owner/tool v1.0.1
Discover assets and review HTTP security headers.
Reconnaissance
Web security
1,200 stars — Fictional example1.2k 128 forks — Fictional example128 8,600 views — Fictional example8.6k