

CVE-2014-6271
 zalalov/cve-2014-6271
Shellshock POC | CVE-2014-6271 | cgi-bin reverse shell
command-and-controlexploitationpayload-generation+3
4
zalalov/cve-2014-6271Shellshock POC | CVE-2014-6271 | cgi-bin reverse shell
 dodeepsink/cve-2026-39987.py
This python script exploit the vulnerable marimo /terminal/ws endpoint and returns a interactive shell.
 cristibtz/cve-2025-49619
This script exploits CVE-2025-49619 in Skyvern to execute a reverse shell command.
 cristibtz/cve-2025-62369
This script exploits CVE-2025-62369 in Xibo CMS to execute a reverse shell command.
 cilectiy/cve-2025-49844
CVE-2025-49844
 petergottesman/pwnkit-exploit
Local privilege escalation exploit for CVE-2021-4034 in pkexec, providing a proof-of-concept that drops a root shell on vulnerable systems.
 rop4sh/poc-redis
Proof-of-concept exploit for a Redis vulnerability that spawns a reverse shell, with setup instructions for Docker and netcat listener.
 mr-tuhin/cve-2021-22204-exiftool
Python exploit for CVE-2021-22204 in ExifTool, generating a malicious image that triggers a reverse shell when processed by vulnerable versions.
 haniwa0x01/cve-2022-30023
Authenticated command injection exploit for Tenda HG9 routers. Provides interactive remote shell access via Python script for penetration testing and…
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
 julichaan/cve-2026-39987_poc
Proof-of-concept exploit for CVE-2026-39987, a pre-authentication RCE in Marimo's /terminal/ws WebSocket endpoint that yields an interactive shell…
 laitrungminhduc/cve-2010-3600-pythonhackoracle11gr2
This Python 3 script is for uploading shell (and other files) to Windows Server / Linux via Oracle 11g R2 (CVE-2010-3600).
 robocopsita/cve-2022-0944_rce_poc
Proof-of-concept exploit for SQLPad RCE (CVE-2022-0944) that triggers a reverse shell to the attacker's machine, intended for authorized security…
 mbanyamer/cve-2026-24061-gnu-inetutils-telnetd-remote-authentication-bypass-root-shell-
Proof-of-concept exploit for GNU Inetutils telnetd authentication bypass (CVE-2026-24061) that spawns a root shell via crafted NEW-ENVIRON USER…
 afifudinmtop/cve-2021-21425
Python exploit for CVE-2021-21425 that executes a reverse shell payload against a target IP, with instructions for setting up a netcat listener.
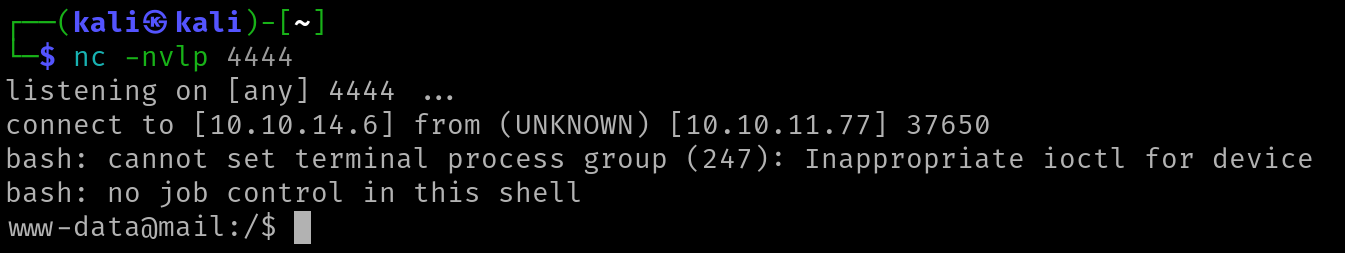 cyberquestor-infosec/cve-2025-49113-roundcube_1.6.10
Authenticated remote code execution exploit for Roundcube 1.6.10 (CVE-2025-49113). Delivers a reverse shell via a crafted PHP payload through the…
 asepsaepdin/cve-2023-38646
Python exploit for Metabase pre-auth RCE (CVE-2023-38646) that establishes a reverse shell for authorized security testing.
 shadow-spinner/cve-2012-2982_python
Python exploit for Webmin 1.580 remote code execution (CVE-2012-2982) that spawns a reverse shell to a specified listener.