
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
18 results
CVE-2019-9053 preview

CVE-2019-9053

GitHubitzr1g/cve-2019-9053

Python exploit for CVE-2019-9053 targeting CMS Made Simple with SQL injection detection and password hash cracking via wordlist, featuring argparse…
educationexploitationpassword-cracking+3
5 months ago
Threaded-CVE-2018-15473 preview

Threaded-CVE-2018-15473

GitHubk3rn3l-32/threaded-cve-2018-15473

A Python 3 reimplementation of the classic CVE-2018-15473 OpenSSH user enumeration exploit, extended with multi-threading, wordlist support,…
educationexploitationinformation-gathering+3
26 months ago
pentest-mcp preview

pentest-mcp

GitHubdmontgomery40/pentest-mcp

NOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR,…
exploitationfuzzingnetwork-mapping+8
1446 months ago
ClaimJumper preview

ClaimJumper

GitHubfevra-dev/claimjumper

Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…

authenticationcryptographyexploitation+6
18 months ago
CVE-2019-9053 preview

CVE-2019-9053

GitHubkalidas-7/cve-2019-9053

Unauthenticated time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9. Extracts admin credentials and optionally cracks password hashes…
exploitationinformation-gatheringpassword-cracking+3
1 year ago
Automated-Next.js-Security-Scanner-for-CVE-2025-29927 preview

Automated-Next.js-Security-Scanner-for-CVE-2025-29927

GitHubferpalma21/automated-next.js-security-scanner-for-cve-2025-29927

This script scans a list of URLs to detect if they are using **Next.js** and determines whether they are vulnerable to **CVE-2025-29927**. It…
exploitationinformation-gatheringreconnaissance+3
21 year ago
CMS-Made-Simple-2.2.9-Unauthenticated-SQL-Injection-Exploit-CVE-2019-9053- preview

CMS-Made-Simple-2.2.9-Unauthenticated-SQL-Injection-Exploit-CVE-2019-9053-

GitHubhf3cyber/cms-made-simple-2.2.9-unauthenticated-sql-injection-exploit-cve-2019-9053-

Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…

exploitationinformation-gatheringpassword-cracking+3
1 year ago
CVE-2024-54772 preview

CVE-2024-54772

GitHubdeauther890/cve-2024-54772

Python-based exploit for CVE-2024-54772 enabling username enumeration on MikroTik RouterOS versions v6.43 through v7.17.2 using wordlist or…

exploitationinformation-gatheringnetwork-security+3
341 year ago
SSH_Enum_CVE-2018-15473 preview

SSH_Enum_CVE-2018-15473

GitHubnestyf/ssh_enum_cve-2018-15473

SSH username enumeration exploit targeting OpenSSH 2.3 through 7.7 (CVE-2018-15473). Enumerates valid users individually or from a wordlist via a…

educationexploitationinformation-gathering+3
1 year ago
CMS-Made-Simple-2.2.9-CVE-2019-9053 preview

CMS-Made-Simple-2.2.9-CVE-2019-9053

GitHubazrenom/cms-made-simple-2.2.9-cve-2019-9053

Exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks the…

exploitationpassword-crackingpenetration-testing+2
32 years ago
CVE-2024-4040-SSTI-LFI-PoC preview

CVE-2024-4040-SSTI-LFI-PoC

GitHubstuub/cve-2024-4040-ssti-lfi-poc

CVE-2024-4040 CrushFTP SSTI LFI & Auth Bypass | Full Server Takeover | Wordlist Support
authenticationexploitationinformation-gathering+3
672 years ago
CVE-2019-9053-exploit preview

CVE-2019-9053-exploit

GitHubdavcwikla/cve-2019-9053-exploit

Working Python exploit for CVE-2019-9053 with optional password cracking via wordlist. Targets web applications via HTTP URI for automated…
exploitationpassword-crackingpenetration-testing+2
2 years ago
CVE-2019-9053 preview

CVE-2019-9053

GitHub4nner/cve-2019-9053

Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
exploitationpassword-crackingpenetration-testing+3
113 years ago
CVE-2018-15473 preview

CVE-2018-15473

GitHub0xrobiul/cve-2018-15473

Python-based exploit for CVE-2018-15473 enabling OpenSSH username enumeration via authentication response oracle, with single-user and wordlist modes.

exploitationinformation-gatheringnetwork-security+3
14 years ago
iPwn preview

iPwn

GitHubbrows3r/ipwn

A Framework meant for the exploitation of iOS devices.
exploitationios-securitymobile-security+5
2335 years ago
rmiscout preview

rmiscout

GitHubbishopfox/rmiscout

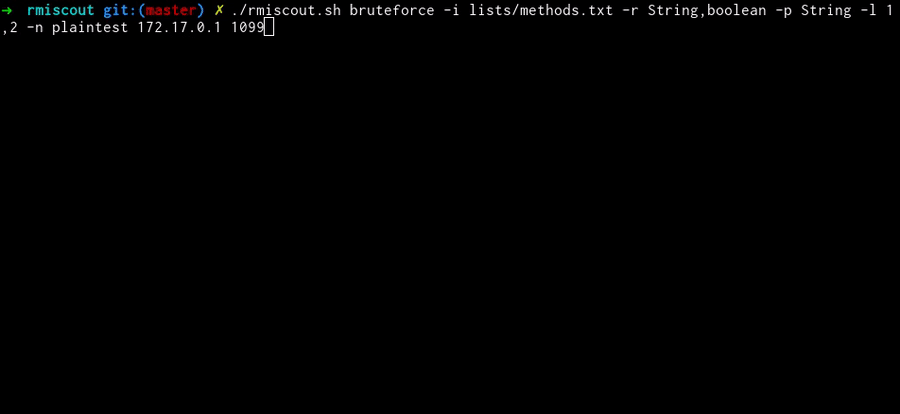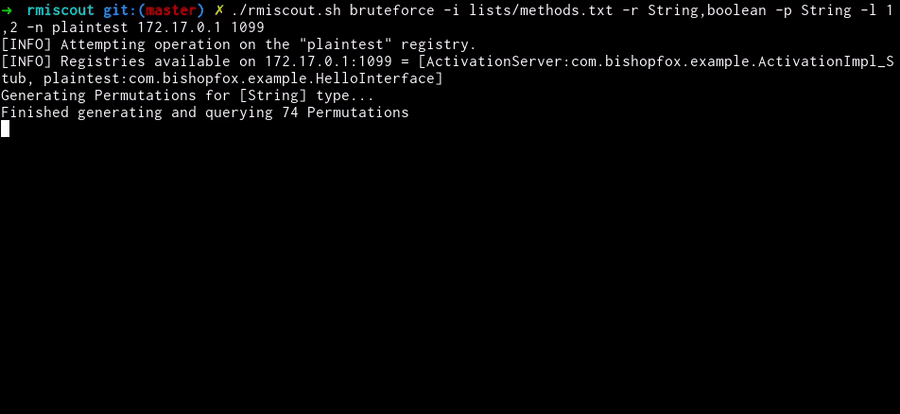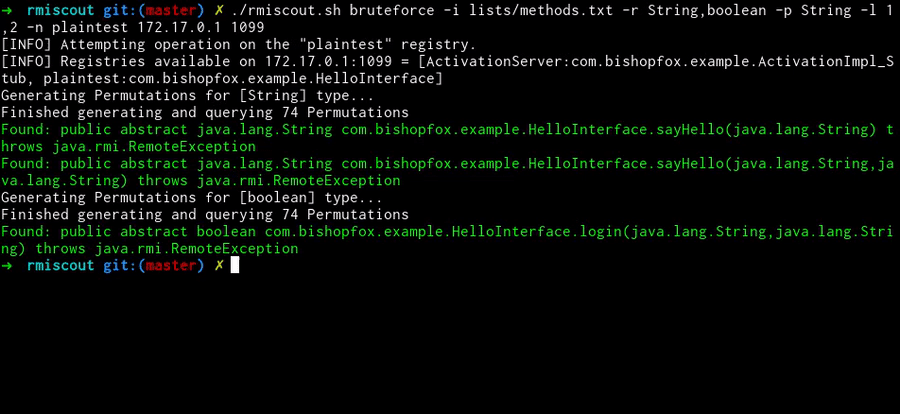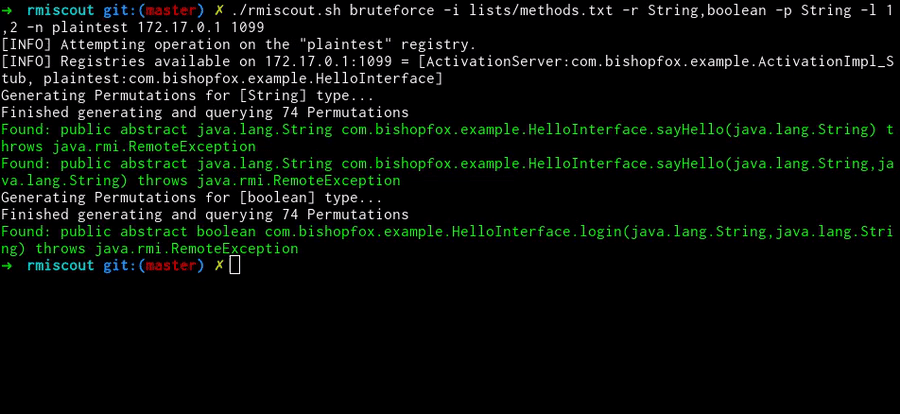
RMIScout uses wordlist and bruteforce strategies to enumerate Java RMI functions and exploit RMI parameter unmarshalling vulnerabilities
exploitationfuzzinginformation-gathering+2
4465 years ago
CVE-2018-15473 preview

CVE-2018-15473

GitHubsait-nuri/cve-2018-15473

OpenSSH 2.3 < 7.7 - Username Enumeration
authenticationexploitationinformation-gathering+3
425 years ago
Bludit-CVE-2019-17240-Fork preview

Bludit-CVE-2019-17240-Fork

GitHubtriple-octopus/bludit-cve-2019-17240-fork

Better version of rastating.github.io/bludit-brute-force-mitigation-bypass/

exploitationpassword-attackspenetration-testing+2
6 years ago