

pixiewps
 wiire-a/pixiewps
An offline Wi-Fi Protected Setup brute-force utility
educationexploitationpassword-attacks+2
wiire-a/pixiewpsAn offline Wi-Fi Protected Setup brute-force utility
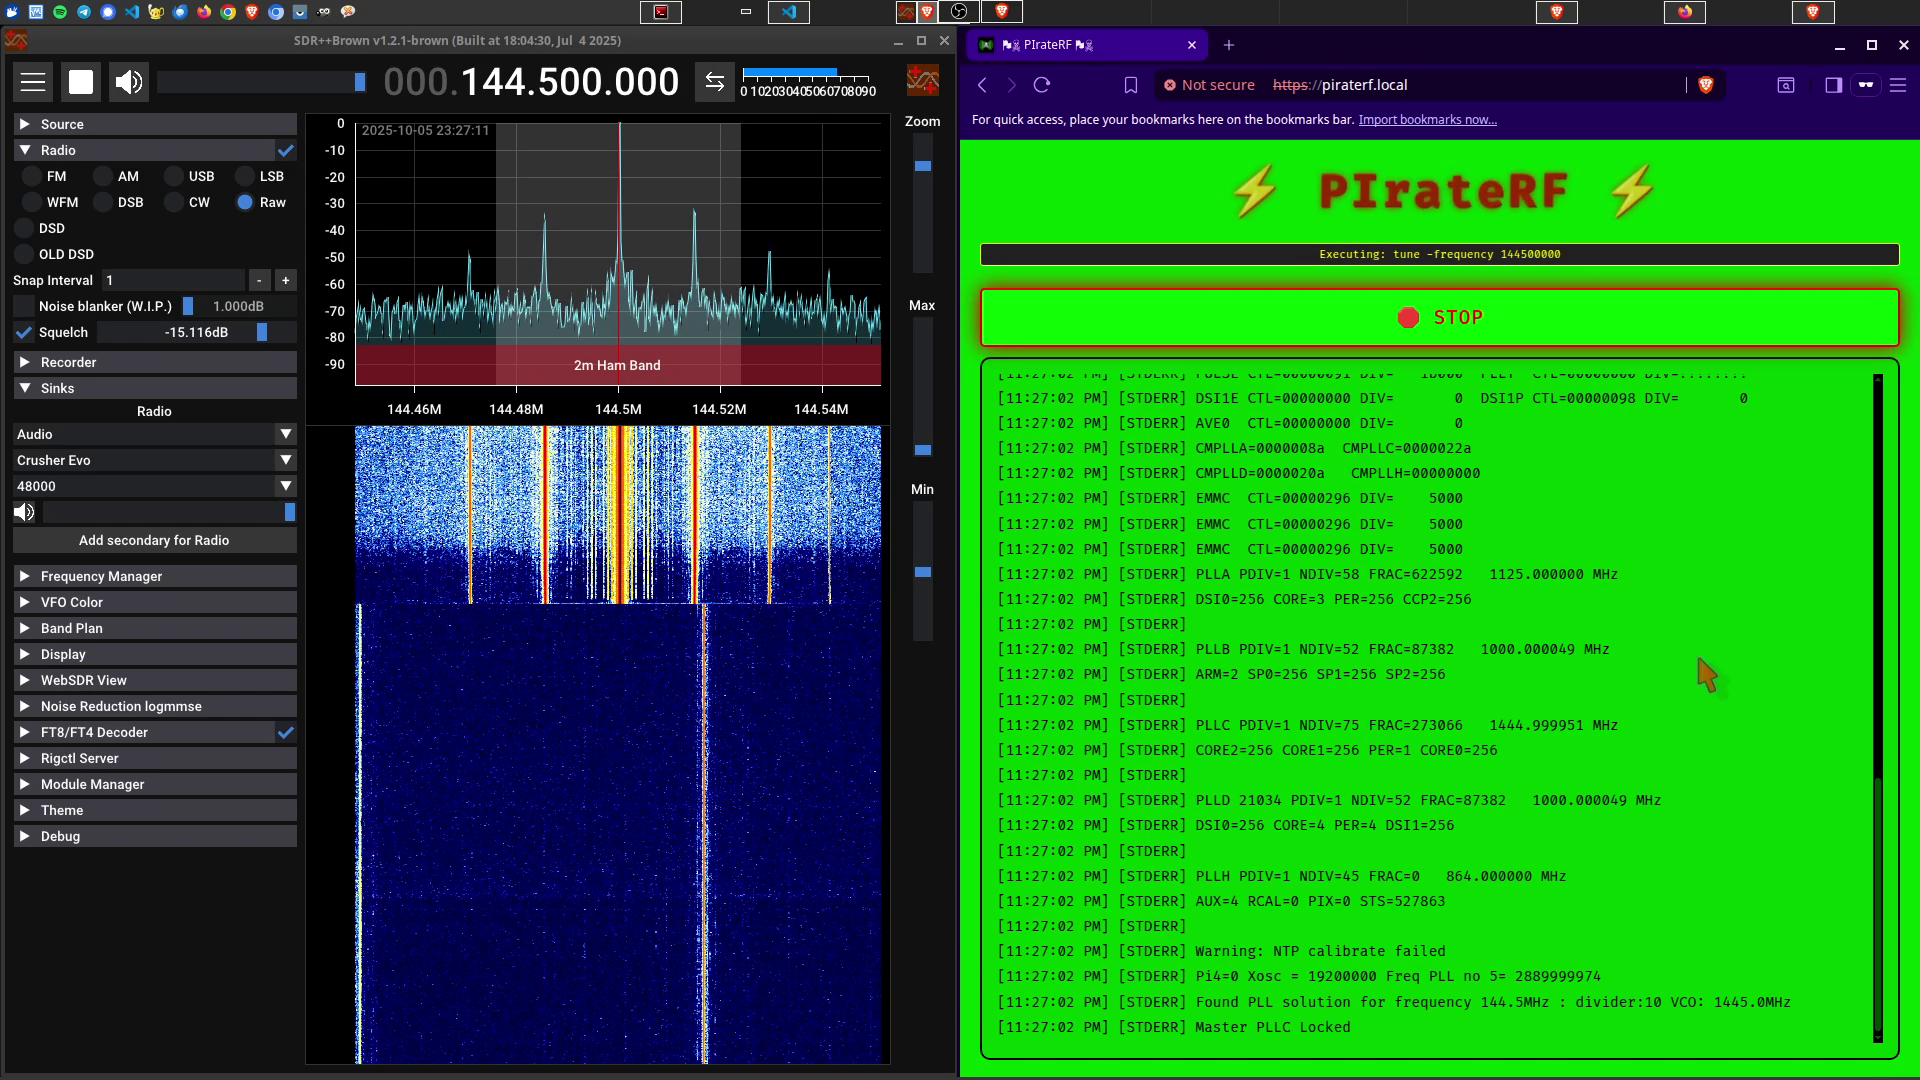 psyb0t/piraterf
PIrateRF transforms your Raspberry Pi Zero W into a portable RF signal generator that spawns its own WiFi hotspot. Control everything from FM…
 wh02m1/cve-2026-78306
Proof-of-concept exploiting DJI drone Bluetooth DUML command injection, sending unauthenticated commands to read credentials, alter Wi-Fi config, and…
 turretsec/u3000py
Python client for the Thinkware U3000 dashcam's local WiFi control protocol, reverse-engineered from the official Android app. PoC tooling behind…
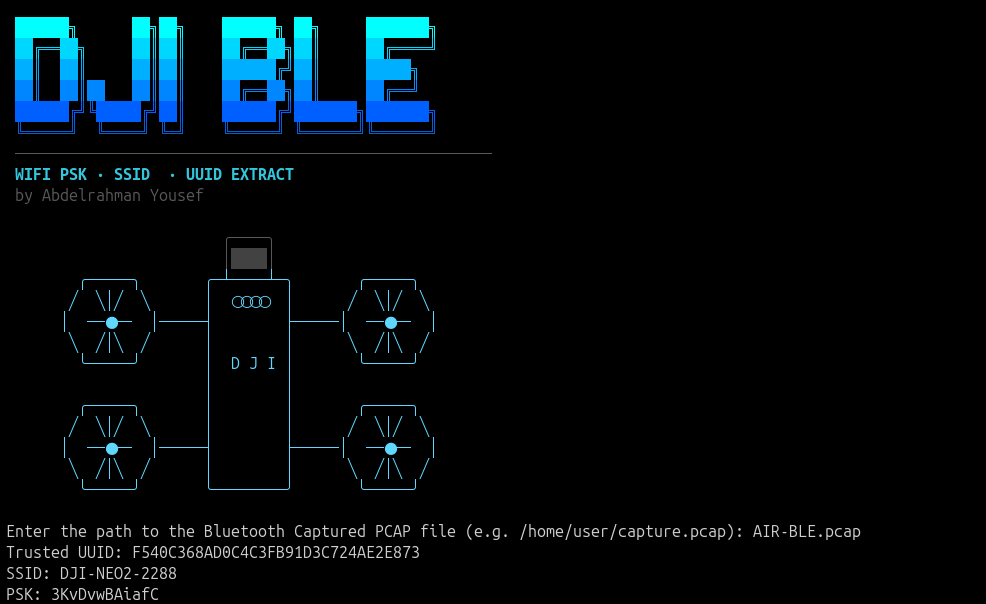 wh02m1/cve-2026-77812
Proof-of-concept that passively sniffs cleartext BLE DUML traffic from DJI drones to recover Wi-Fi PSK and trusted session UUIDs, demonstrating…
 mermehr/mouseserver-1.7.8.5-rce
PoC exploit for CVE-2022-3218 targeting WiFi Mouse Server 1.7.8.5, achieving RCE via keystroke injection and in-memory PowerShell payload delivery…
 ymsniper/kto
Automated Wi-Fi deauthentication tool that continuously scans for clients on a target SSID and kicks non-whitelisted devices. Features whitelist…
 dingo97/cve-2026-20516
Write-up and ADB proof of concept for CVE-2026-20516, a confused deputy flaw in MediaTek Android TV MiracastService allowing local Wi-Fi Direct state…
 george0papasotiriou/cve-2026-11117-wpa2-4-way-handshake-reinstallation-krack-sim-
Python simulation of CVE-2026-11117 demonstrating WPA2 4-way handshake PTK reinstallation and nonce reuse to illustrate the KRACK attack.
 mahmoud-sadder/airstrike
AirStrike is an advanced wireless security assessment framework designed to simplify and enhance Wi-Fi penetration testing through an integrated,…
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
 goultarde/remotemouse-3.008-rce
POC for CVE-2021-35448 based on https://www.exploit-db.com/exploits/49601
 hunt-benito/mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce
Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…
 efchatz/wpaxfuzz
A full-featured open-source Wi-Fi fuzzer
 ottoyrocky/phantom-brain
Red portatil de reconocimiento inteligente con IA offline
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
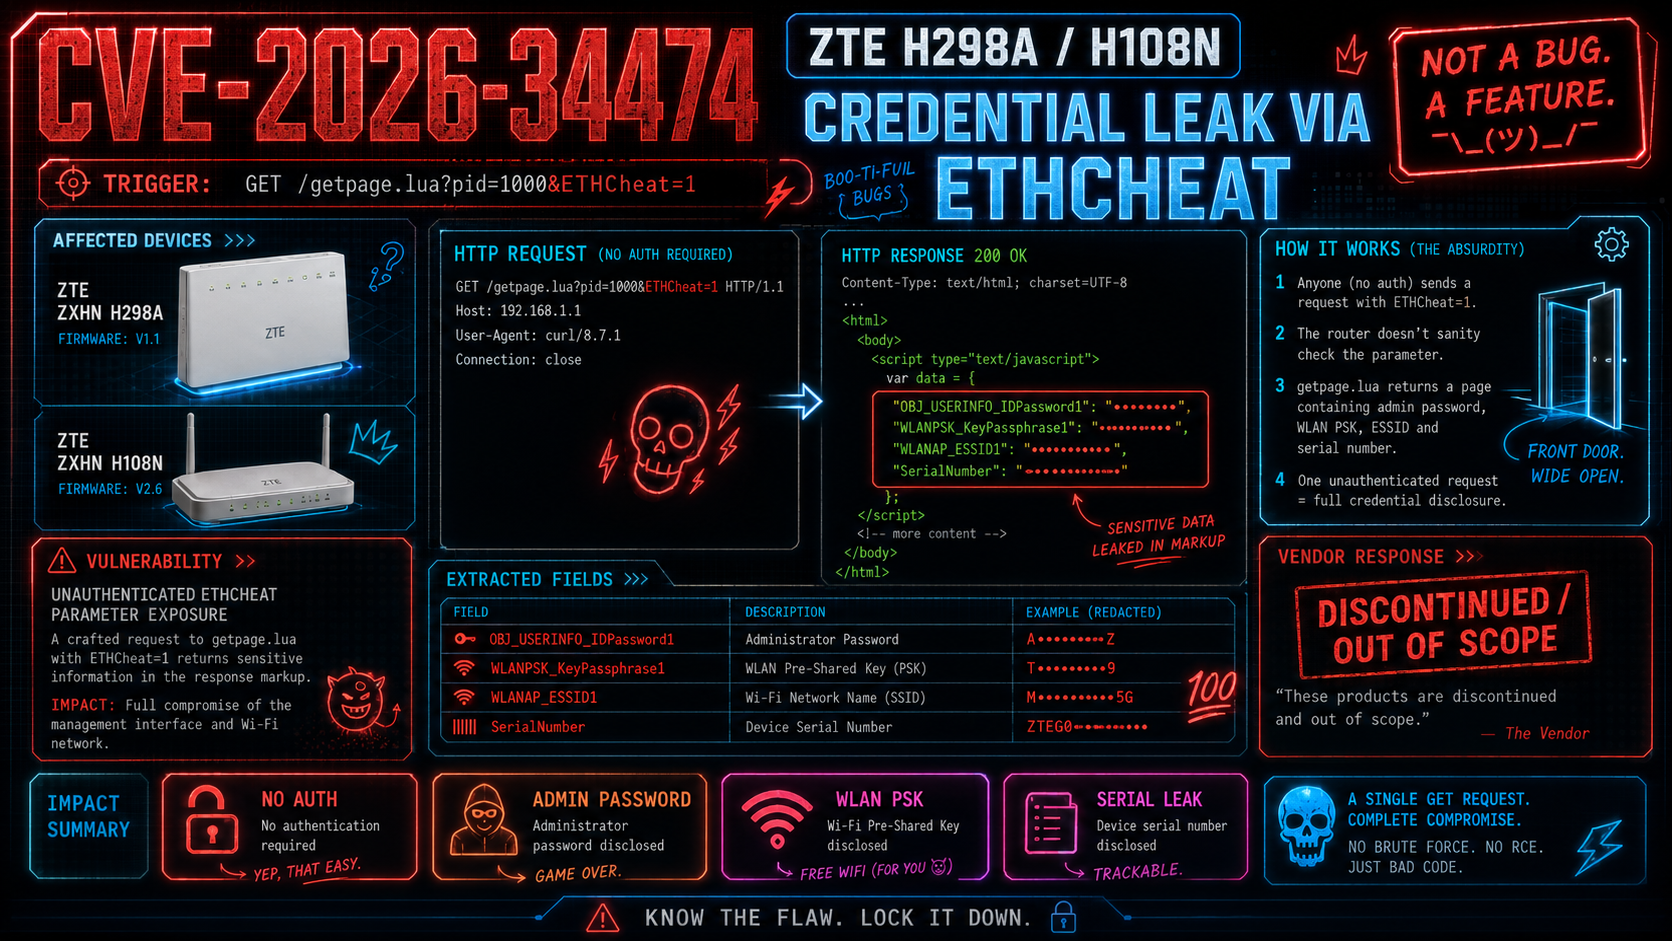 minanagehsalalma/cve-2026-34474-zte-h298a-h108n-sensitive-data-exposure
CVE-2026-34474: unauthenticated ETHCheat=1 requests leak the admin password and Wi-Fi PSK from ZTE H298A/H108N routers.
 masjadaan/cve-2025-29338
Technical advisory and proof-of-concept for a stack-based buffer overflow (CWE-121) in the NXP moal.ko Wi-Fi kernel driver, enabling local kernel…