
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
106 results
sliver-gui preview

sliver-gui

GitHubmr-in4inci3le/sliver-gui

A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…

command-and-controlexploitationlateral-movement+6
219
6 days ago
CVE-2025-38502-Linux-LPE preview

CVE-2025-38502-Linux-LPE

GitHubabraxas/cve-2025-38502-linux-lpe

Research repository for CVE-2025-38502, a Linux kernel BPF cgroup local storage out-of-bounds access via tail calls enabling local privilege…
binary-exploitationeducationexploitation+5
28 days ago
CVE-2026-90782-s2opc-status-clobber preview

CVE-2026-90782-s2opc-status-clobber

GitHubharshrajsinghania/cve-2026-90782-s2opc-status-clobber

Standalone PoC for CVE-2026-90782: status-clobbering NULL dereference in S2OPC alloc_notification_message_items() (DataChange fails, Event succeeds)
binary-analysisexploitationfuzzing+2
13 days ago
CVE-2026-73314 preview

CVE-2026-73314

GitHubbombobombone/cve-2026-73314

Proof-of-concept exploit for CVE-2026-73314, a PayPal REST webhook signature verification bypass in XenForo before 2.3.13, allowing unauthorized…
exploitationvulnerability-analysisweb-application-exploitation+1
18 days ago
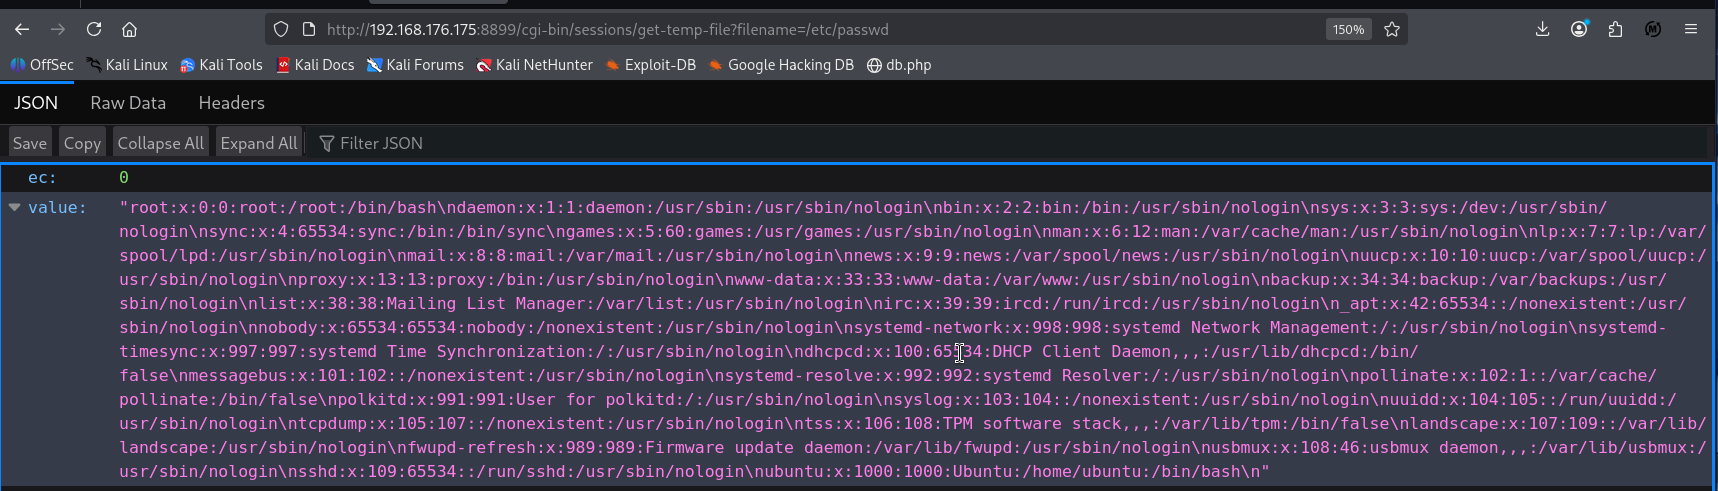
CVE-2025-5880 preview

CVE-2025-5880

GitHubac8999/cve-2025-5880

PoC for a Path Traversal vulnerability in Whistle v2.9.98 via the /cgi-bin/sessions/get-temp-file endpoint. (Unpatched)
exploitationvulnerability-analysisweb-application-exploitation
1 month ago
CVE-2026-23002-5G-NAS-Message-Buffer-Overflow-in-gNodeB preview

CVE-2026-23002-5G-NAS-Message-Buffer-Overflow-in-gNodeB

GitHubgeorge0papasotiriou/cve-2026-23002-5g-nas-message-buffer-overflow-in-gnodeb

Simulated 5G gNodeB NAS parser with stack buffer overflow PoC for CVE-2026-23002; a crafted NAS message triggers remote code execution.
binary-exploitationembedded-systems-securityexploitation+2
1 month ago
CVE-2026-22019-libcurl-HTTP-2-CONNECT-Tunnel-Mixup preview

CVE-2026-22019-libcurl-HTTP-2-CONNECT-Tunnel-Mixup

GitHubgeorge0papasotiriou/cve-2026-22019-libcurl-http-2-connect-tunnel-mixup

Simulates CVE-2026-22019, a libcurl HTTP/2 CONNECT tunnel stream-isolation failure, demonstrating cross-stream data injection and response smuggling…
educationexploitationnetwork-security+2
1 month ago
CVE-2026-22012-Diameter-Protocol-Credit-Control-Bypass-in-5G preview

CVE-2026-22012-Diameter-Protocol-Credit-Control-Bypass-in-5G

GitHubgeorge0papasotiriou/cve-2026-22012-diameter-protocol-credit-control-bypass-in-5g

Python simulation of CVE-2026-22012, showing how a missing Final-Unit-Indication in Diameter Credit-Control allows unlimited quota and service bypass…
exploitationmobile-securitynetwork-security+1
1 month ago
CVE-2026-66066 preview

CVE-2026-66066

GitHubhackspeak/cve-2026-66066

CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing
exploitationinformation-gatheringpenetration-testing+5
31 month ago
CVE-2026-66066 preview

CVE-2026-66066

GitHubshinthink/cve-2026-66066

CVE-2026-66066 — KindaRails2Shell: Rails Active Storage/libvips Arbitrary File Read → RCE. MATLAB/HDF5 dual-identity file → SECRET_KEY_BASE theft →…

exploitationpenetration-testingreconnaissance+3
11 month ago
CVE-2026-11114-Node.js-vm-Sandbox-Escape-via-Proxy preview

CVE-2026-11114-Node.js-vm-Sandbox-Escape-via-Proxy

GitHubgeorge0papasotiriou/cve-2026-11114-node.js-vm-sandbox-escape-via-proxy

PoC exploit for CVE-2026-11114 demonstrating Node.js vm sandbox escape via Proxy to achieve remote code execution against a vulnerable HTTP /eval…
exploitationvulnerability-analysisweb-application-exploitation
1 month ago
CVE-2026-0101-BLE-Address-Spoofing-via-Weak-Resolvable-Private-Address preview

CVE-2026-0101-BLE-Address-Spoofing-via-Weak-Resolvable-Private-Address

GitHubgeorge0papasotiriou/cve-2026-0101-ble-address-spoofing-via-weak-resolvable-private-address

Python PoC for CVE-2026-0101 demonstrating BLE address spoofing via replay of a captured Resolvable Private Address to impersonate a trusted…
adversarial-attackbluetooth-securityeducation+3
1 month ago
CVE-2026-6060-QUIC-Handshake-Amplification-via-Address-Validation-Bypass preview

CVE-2026-6060-QUIC-Handshake-Amplification-via-Address-Validation-Bypass

GitHubgeorge0papasotiriou/cve-2026-6060-quic-handshake-amplification-via-address-validation-bypass

Educational Python PoC for a QUIC address-validation bypass that triggers handshake amplification, including vulnerable server simulation and attack…

adversarial-attackeducationexploitation+2
1 month ago
KindaRails2Shell preview

KindaRails2Shell

GitHub0xsha/kindarails2shell

Single-file PoC for Rails CVE-2026-66066: arbitrary file read, secret recovery, threaded scanning, and conditional RCE via signed image variations.
exploitationlabs-practicepayload-development+4
41 month ago
CVE-2026-66066-POC preview

CVE-2026-66066-POC

GitHubzer0sumgam3/cve-2026-66066-poc

PoC for CVE-2026-66066 in Ruby on Rails
educationexploitationlabs-practice+3
231 month ago
CVE-2026-67184-Unauthenticated-NULL-Pointer-Dereference-Crashes-the-Server-TinyWeb- preview

CVE-2026-67184-Unauthenticated-NULL-Pointer-Dereference-Crashes-the-Server-TinyWeb-

GitHubtheopaid/cve-2026-67184-unauthenticated-null-pointer-dereference-crashes-the-server-tinyweb-

Security Advisory: Unauthenticated NULL Pointer Dereference Crashes the Server (TinyWeb)
educationexploitationpapers-research+2
12 months ago
CVE-2026-53913 preview

CVE-2026-53913

GitHuboscerd/cve-2026-53913

PoC reproducer for CVE-2026-53913 (Apache Camel camel-keycloak): KeycloakSecurityPolicy fails open in the Basic Setup — with no required…
authenticationcode-analysisexploitation+3
12 months ago
cve-2019-5420-POC preview

cve-2019-5420-POC

GitHubwildwestcybersecurity/cve-2019-5420-poc

cve-2019-5420 POC simple ruby script

educationexploitationpayload-generation+3
12 months ago
Previous123456Next