
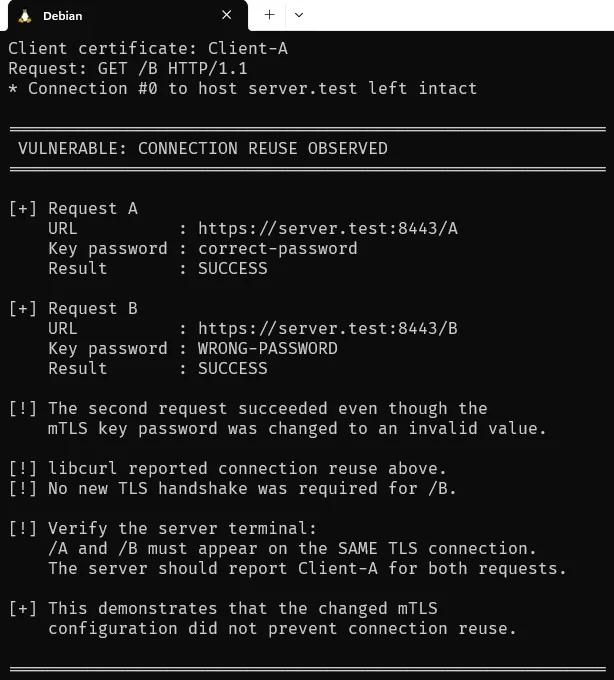
CVE-2026-8932-PoC
 nimaarek/cve-2026-8932-poc
Proof-of-concept reproducing CVE-2026-8932, an incomplete mTLS configuration matching flaw in libcurl connection reuse, with a local lab server and C…
cryptographyeducationexploitation+3
nimaarek/cve-2026-8932-pocProof-of-concept reproducing CVE-2026-8932, an incomplete mTLS configuration matching flaw in libcurl connection reuse, with a local lab server and C…
 baba01hacker666/cve-2026-33032
Python proof-of-concept for CVE-2026-33032 that inspects nginx status and configs, then demonstrates unauthorized config write with reload to deploy…
 george0papasotiriou/cve-2026-22007-ntp-monlist-amplification-over-ipv6
Python PoC for CVE-2026-22007: NTP monlist amplification over IPv6, including a simulated vulnerable server and spoofed UDP reflection attack.
 george0papasotiriou/cve-2026-22004-git-lfs-pointer-poisoning-supply-chain-
Proof-of-concept for Git LFS pointer poisoning, with Bash and Python scripts that create a malicious repository, simulate a rogue LFS server, and…
 george0papasotiriou/cve-2026-21018-opc-ua-authentication-bypass-via-none-security-policy
Proof-of-concept exploit for OPC UA authentication bypass using None security policy, including a simulated server to demonstrate unauthorized…
 royaleybovich/cve-2026-3854-lab
Local intentionally vulnerable lab with a guided workshop and CTF challenges for practicing Git push-option RCE, unsafe deserialization,…
 oscerd/cve-2026-40022
Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths
 jfs-jfs/cve-2026-37073
Proof-of-concept exploit for CVE-2026-37073: unauthenticated SMTP email abuse via incorrect access control in Veno File Manager 4.4.9.
 dahalsamir/cve-2026-23744-mcpjam-rce-exploit
This Python proof-of-concept targets a vulnerable MCP (Model Context Protocol) service exposed by the target application. The vulnerability allows an…
 alisster00/cve-2026-23744-rce
This utility was created during research involving MCPJam v1.4.2. The application exposes an API endpoint that accepts a server configuration object.…
 deepsecurityresearch/cve-2026-2586
Authenticated EL injection exploit for GlassFish/Payara admin console enabling remote command execution via crafted parameters in the virtual server…
 dungsocool/cve-2017-12635_36
Step-by-step lab demonstrating exploitation of CVE-2017-12635 (privilege escalation) and CVE-2017-12636 (remote code execution) against Apache…
 typicalsmc/cve-2025-49132-poc
Proof-of-concept exploit for CVE-2025-49132, a path traversal vulnerability in Pterodactyl panel. Forges session cookies using exposed Redis server…
 d0n601/cve-2025-12721
g-FFL Cockpit <= 1.7.1 - Missing Authorization to Unauthenticated Information Exposure
 ayewo/fortios-ldap-mitm-poc-cve-2019-5591
The default configuration of LDAP on FortiOS v6.0.x to v6.2.0 does not check server identity for LDAP/S leading to MITM attacks. This PoC demos full…
 xiaoxiaoranxxx/cve-2025-56815
Datart 1.0.0-rc.3 is vulnerable to Directory Traversal in the POST /viz/image interface, since the server directly uses MultipartFile.transferTo() to…
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
 slicingmelon/haproxy-cve-2023-45539-poc
HAProxy-CVE-2023-45539-PoC