

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 murrez/cve-2026-100740
Python PoC for CVE-2026-100740, an L2TP Host Name AVP out-of-bounds write in D-Link DIR-895L A1_102b07 tunnel_set_params. Fingerprints the device and…
 pepelux/sippts
Set of tools to audit SIP based VoIP Systems
 sneakynachos/cve-2026-4692-trust-me-im-in-rdm
Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…
 dungsocool/cve-2025-7384
Exploit PoC and root-cause analysis for a critical unauthenticated PHP object injection in WordPress Database for Contact Form 7, leading to RCE via…
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 amnestytech/inside-pegasus
A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…
 martinclauss/exim-rce-cve-2018-6789
This repository provides a learning environment to understand how an Exim RCE exploit for CVE-2018-6789 works.
 deepwoodssec/cve-2026-36522
Proof-of-concept exploit for CVE-2026-36522: unauthenticated NaN injection via MAVLink PARAM_SET in ArduPilot ArduPlane, causing DoS or silent…
 trustedsec/social-engineer-toolkit
The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.
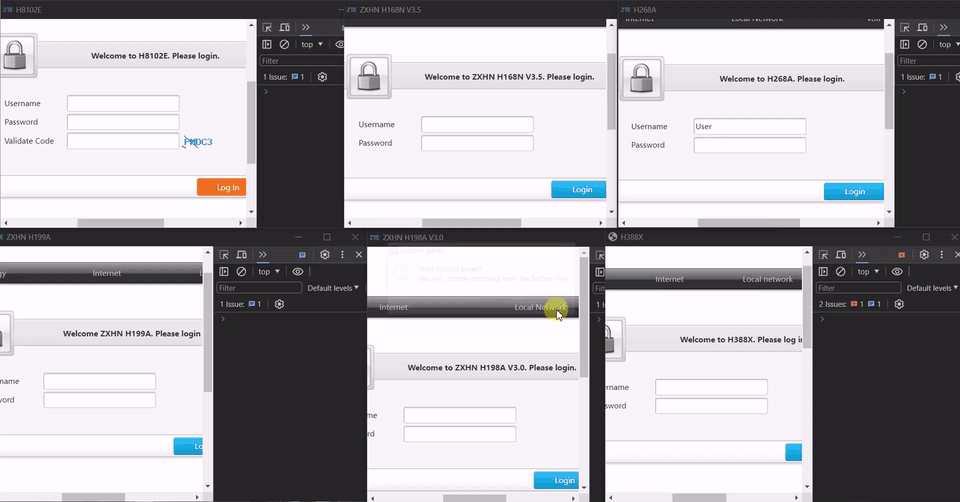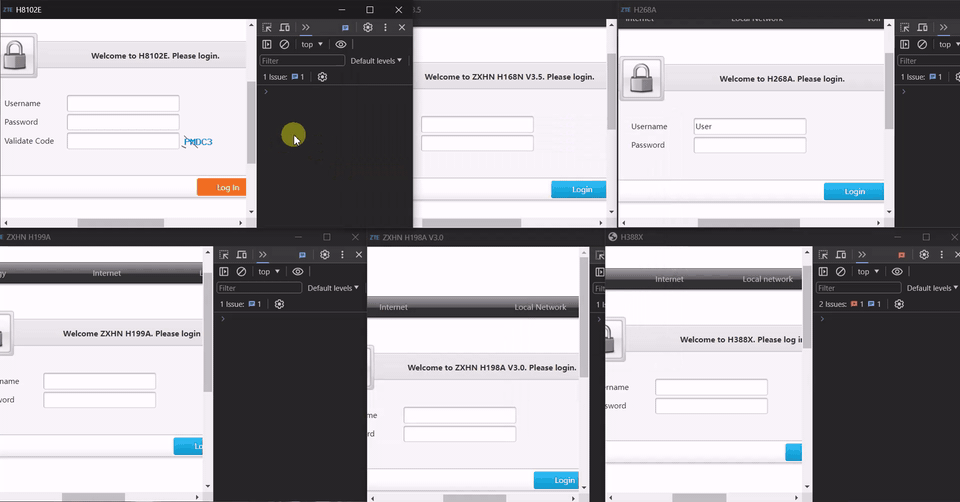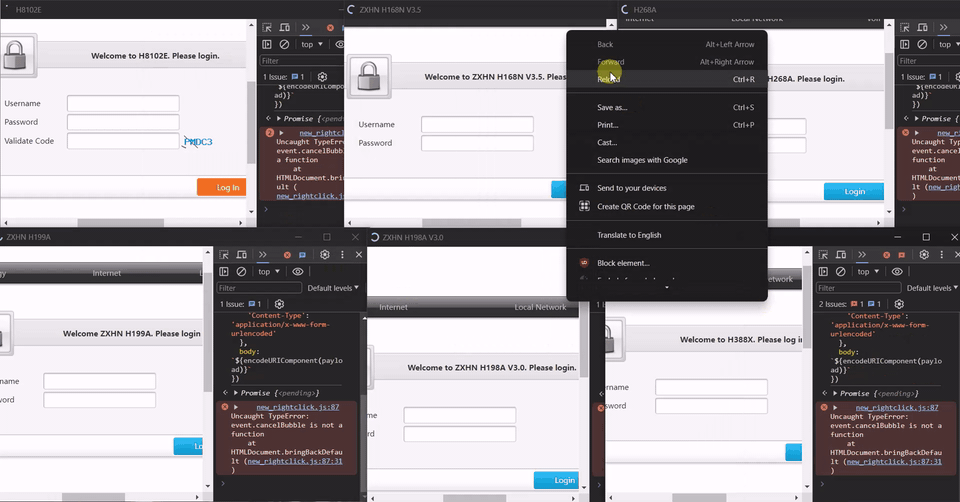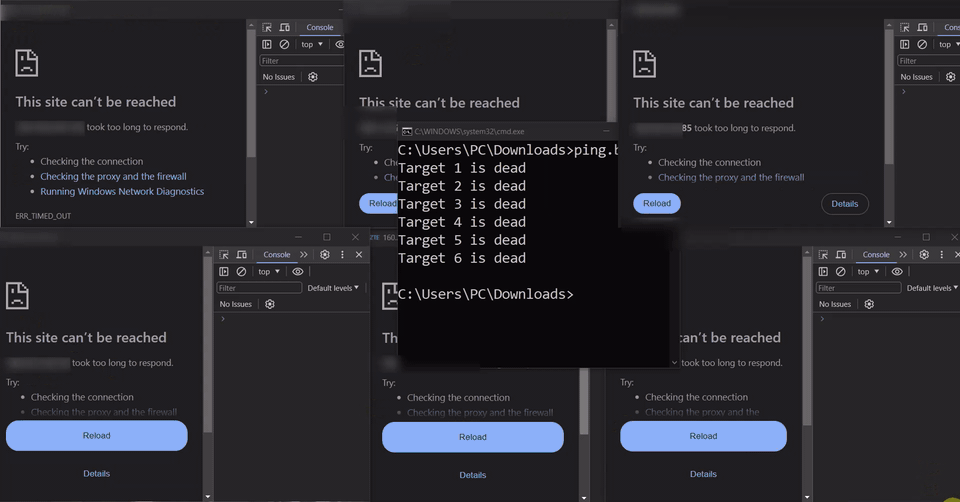 minanagehsalalma/cve-2026-34473-unauthenticated-dos-zte-routers
Technical breakdown of CVE-2026-34473, an unauthenticated denial of service affecting 17+ ZTE router models.
 backline-playground/gogs
Fork of gogs/gogs for reachability benchmark testing (CVE-2024-45337)
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 localh0ste/cve-2025-4138
Tarfile module directory traversal vulnerability ( with overflow crossed Directory ) --> Lead to Privilege escalation
 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
 80ottanta80/cve-2024-32019-poc
Bash script for Privilege Escalation via "ndsudo" (Netdata Local Exploit)
 googleprojectzero/sandbox-attacksurface-analysis-tools
Set of tools to analyze Windows sandboxes for exposed attack surface.