

security-research
 google/security-research
This project hosts security advisories and their accompanying proof-of-concepts related to research conducted at Google which impact non-Google owned…
curated-resourceseducationexploitation+3
4.7k
google/security-researchThis project hosts security advisories and their accompanying proof-of-concepts related to research conducted at Google which impact non-Google owned…
 horkimhab/cve-2025-9974
Educational security research repository for CVE-2025-9974, providing vulnerability awareness material and authorized lab guidance for controlled…
 horkimhab/cve-2026-65660
Educational security research repository documenting CVE-2026-65660 with setup guidance for authorized lab testing and vulnerability awareness.
 aipeacs/sc3010-computer-security
Using Struts2 and PowerShell to recreate CVE-2017-5638 OGNL Injection vulnerability.
 horkimhab/cve-2026-94545
Educational CVE research repository for CVE-2026-94545, providing proof-of-concept material and lab guidance for authorized vulnerability analysis…
 horkimhab/cve-2026-90898
Educational CVE-2026-90898 proof-of-concept repository for authorized security research, vulnerability awareness, and defensive testing in isolated…
 beefproject/beef
The Browser Exploitation Framework Project
 gagaltotal/cve-2026-68376-ubuntu-7.0.0-30-poc
Proof-of-concept exploit for CVE-2026-68376 in Ubuntu kernel 7.0.0-30, leveraging SCTP chunk handling and PTE manipulation to escalate privileges to…
 horkimhab/cve-2026-93485
Educational security research repository for learning and testing CVE-2026-93485 concepts in isolated, authorized lab environments.
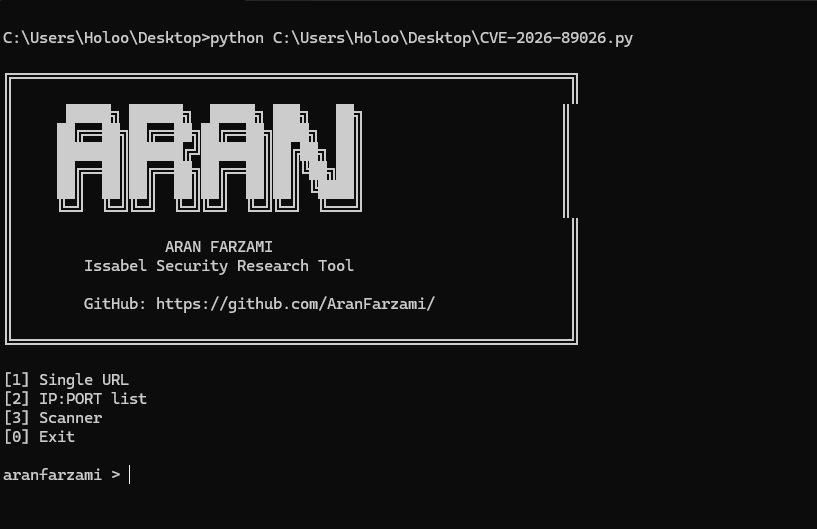 aranfarzami/cve-2026-89026
PoC exploit and scanner for CVE-2026-89026, validating the Issabel PBXAPI authentication bypass via forged HS256 JWTs across single or listed targets.
 horkimhab/cve-2026-74469
Proof-of-concept and educational research repository for CVE-2026-74469 (DiagSpill), providing vulnerability analysis material for authorized lab…
 horkimhab/cve-2026-68121
Proof-of-concept for CVE-2026-68121 (PPPoEject), providing a Python exploit implementation for authorized security research and lab testing.
 horkimhab/cve-2026-81000
Educational CVE-2026-81000 proof-of-concept repository for authorized security research, vulnerability awareness, and controlled lab testing.
 horkimhab/cve-2026-80844
Proof-of-concept and research repository for CVE-2026-80844 (DirtyAH6), providing educational material and lab setup guidance for authorized…
 amulyakaushik/cve-2023-27163-lab
Docker-based lab reproducing CVE-2023-27163 SSRF in Request-Baskets, with exploitation verification, detection script, and network-isolation…
 shambhavim18/cve-2019-15107-lab
Docker-based lab demonstrating CVE-2019-15107, the Webmin unauthenticated RCE, covering deployment, exploitation, detection, and remediation.
 showy-headteacher114/cve-2025-66398
Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.
 chandrimanath04-hue/cve-2024-31218-webhood-lab
Docker-based lab reproducing CVE-2024-31218, an unauthenticated PocketBase admin creation flaw in Webhood, with PoC, detection, and remediation…