

security-research
 google/security-research
This project hosts security advisories and their accompanying proof-of-concepts related to research conducted at Google which impact non-Google owned…
curated-resourceseducationexploitation+3
google/security-researchThis project hosts security advisories and their accompanying proof-of-concepts related to research conducted at Google which impact non-Google owned…
 beefproject/beef
The Browser Exploitation Framework Project
 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
 horkimhab/cve-2026-81000
Educational CVE-2026-81000 proof-of-concept repository for authorized security research, vulnerability awareness, and controlled lab testing.
 horkimhab/cve-2026-68121
Proof-of-concept for CVE-2026-68121 (PPPoEject), providing a Python exploit implementation for authorized security research and lab testing.
 harishsg993010/damn-vulnerable-mcp-server
Damn Vulnerable MCP Server
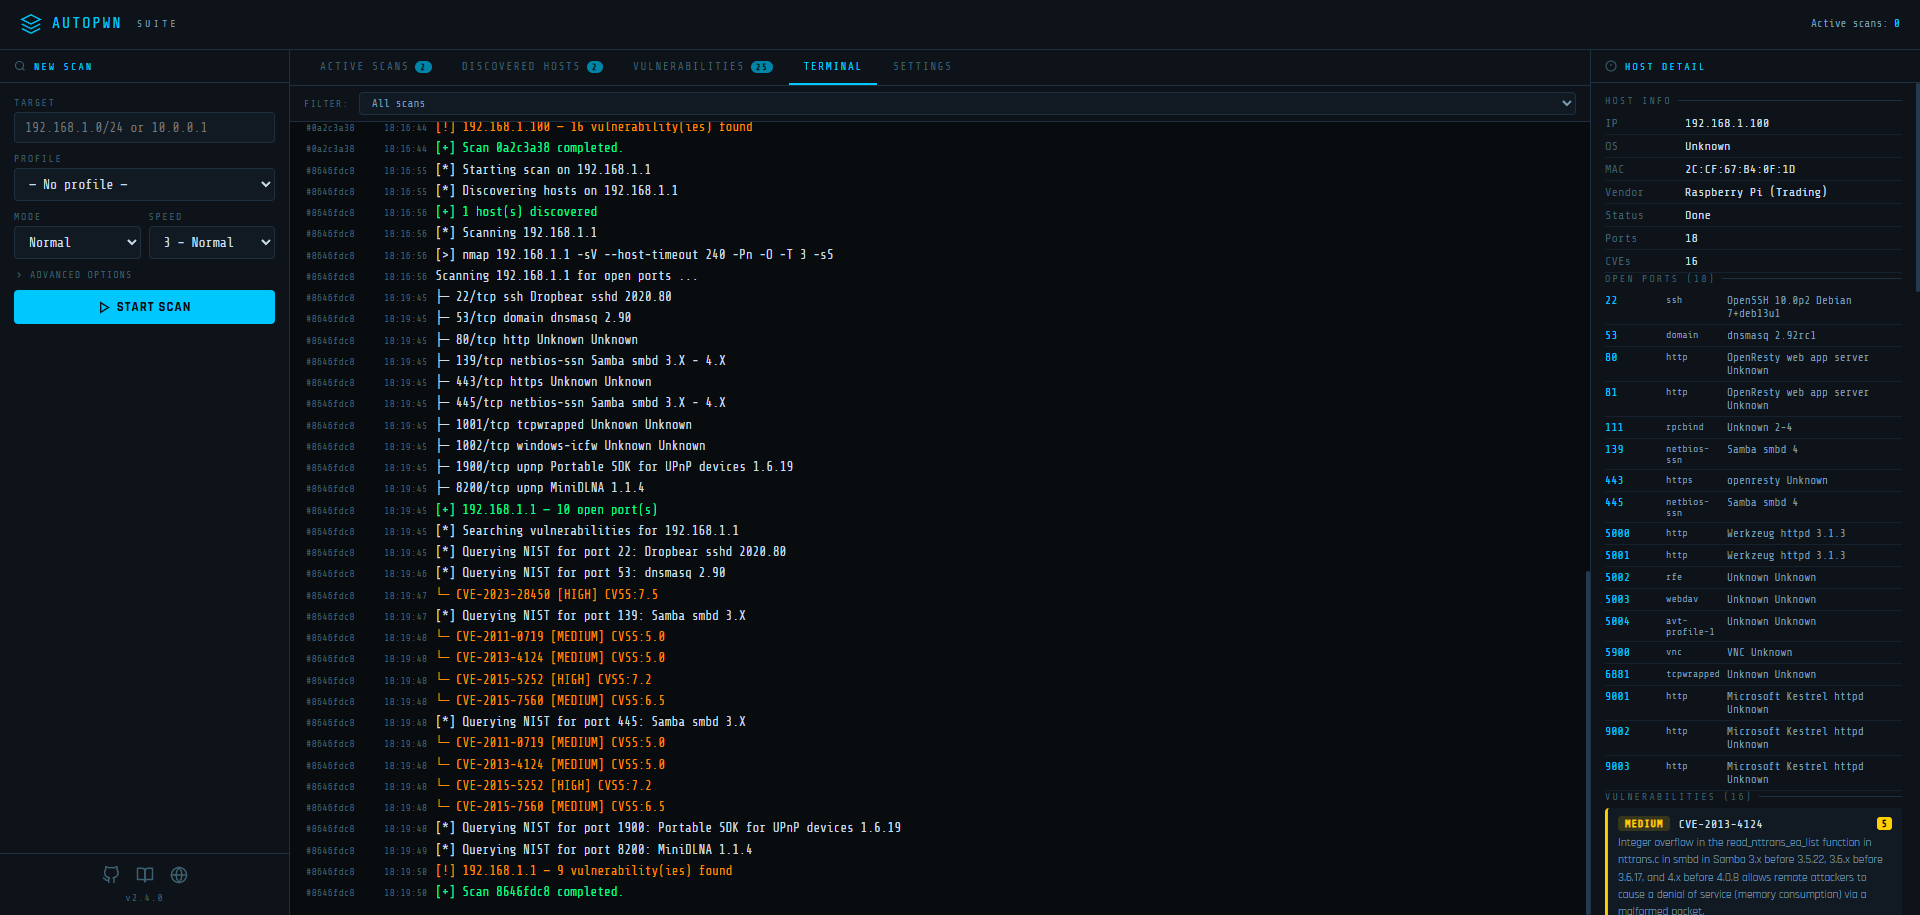 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
 abraxas/cve-2026-52782
Reproduction pack and PoC script for CVE-2026-52782, an authenticated IDOR in OpenProject project storage settings that hijacks Nextcloud/OneDrive…
 sarabpal-dev/ionstack-s22u
CVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
 i014n/pngloader
Hides arbitrary payloads in PNG images using nibble-to-ASCII encoding and Fibonacci LSB steganography, with a C++ loader that extracts and executes…
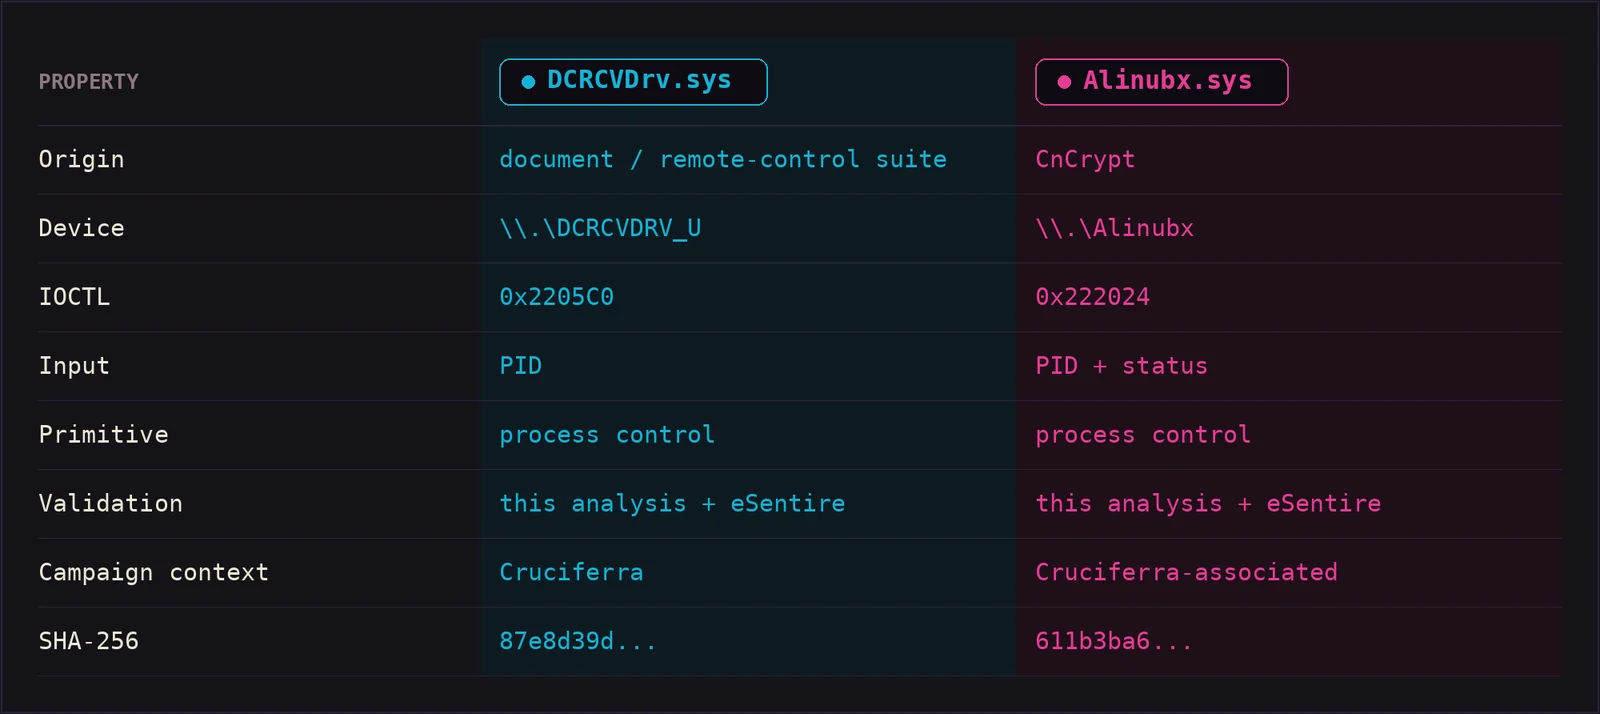 deathshotxd/0xcr0sscrush
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.
 exploit-database/exploitdb
exploitdb // The official Exploit-Database repository
 alexanderzinoni/cve-2022-21449
Educational Python project implementing elliptic curve cryptography (ECDSA, ECIES) and simulating exploitation of CVE-2022-21449, with visualizations…
 horkimhab/cve-2025-64702-more
Proof-of-concept code and research notes for QPACK/HTTP-3 vulnerabilities (CVE-2025-64702, CVE-2026-12523, CVE-2025-13945) for authorized lab testing.
 horkimhab/cve-2026-109618-619
Proof-of-concept code for CVE-2026-109618 and CVE-2026-109619 (php2shell bypass), packaged for authorized lab reproduction and vulnerability research.
 cplusplus17/deco-filepush-disclosure
Disclosure and PoC for a root file read/write flaw in the TP-Link Deco XE75 Pro V3 debug channel (tmpsvr opcodes 0xC456/0xF0), with CVSS analysis and…
 showy-headteacher114/cve-2025-66398
Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.
 geeoon/fault-injection-finder
Automatically find and execute fault injection attacks