

sqlmap
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
api-securityapi-security-testingcrawler+12
sqlmapproject/sqlmapAutomatic SQL injection and database takeover tool
 oscerd/cve-2026-91858
Runnable Spring Boot and Quarkus reproducer for CVE-2026-91858, an XXE in Apache Camel camel-fop via a third-party TransformerFactory, with affected…
 oscerd/cve-2026-85313
Runnable Spring Boot proof-of-concept reproducing CVE-2026-85313, where Apache Camel camel-jetty enableCORS reflects any origin with credentials,…
 oscerd/cve-2026-85250
Runnable XXE proof-of-concept for CVE-2026-85250 in Apache Camel camel-xpath (documentType=InputSource), with Spring Boot and Quarkus affected vs…
 oscerd/security-research
Vulnerabilities I've reported to the Apache Software Foundation: 46 CVEs across 15 projects
 mein-0/knockgiga
Proof-of-concept local privilege escalation exploiting Gigabyte gdrv3.sys IOCTLs to write the SYSTEM token into a user process via an unchecked…
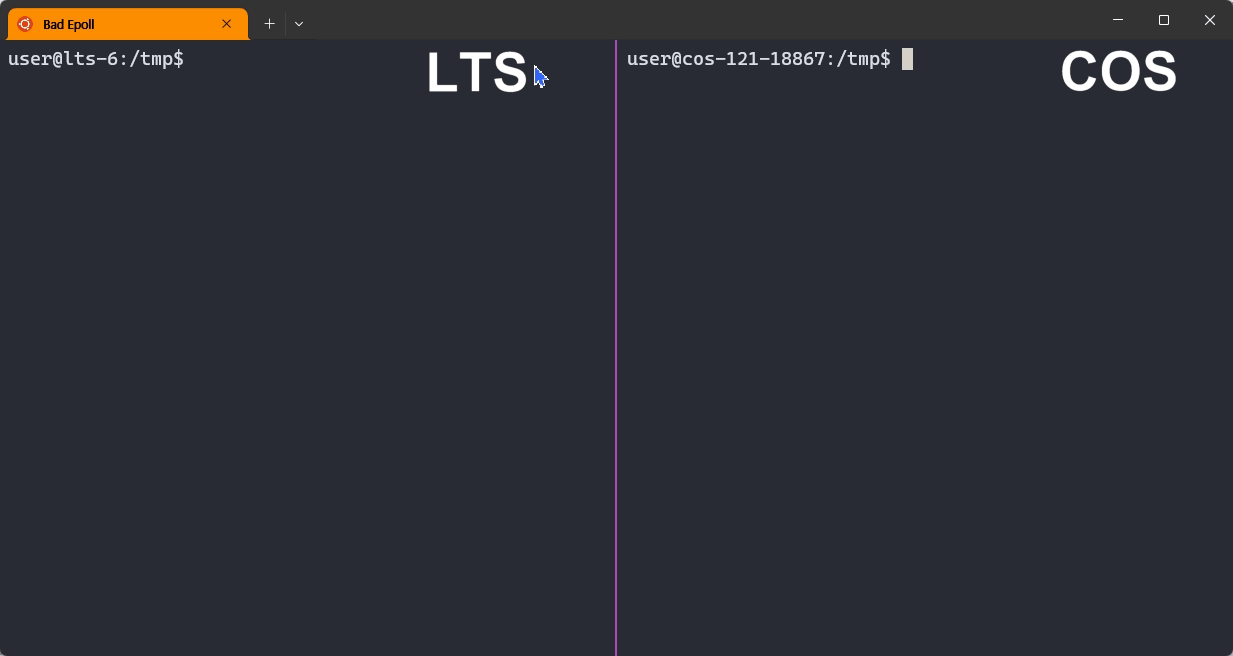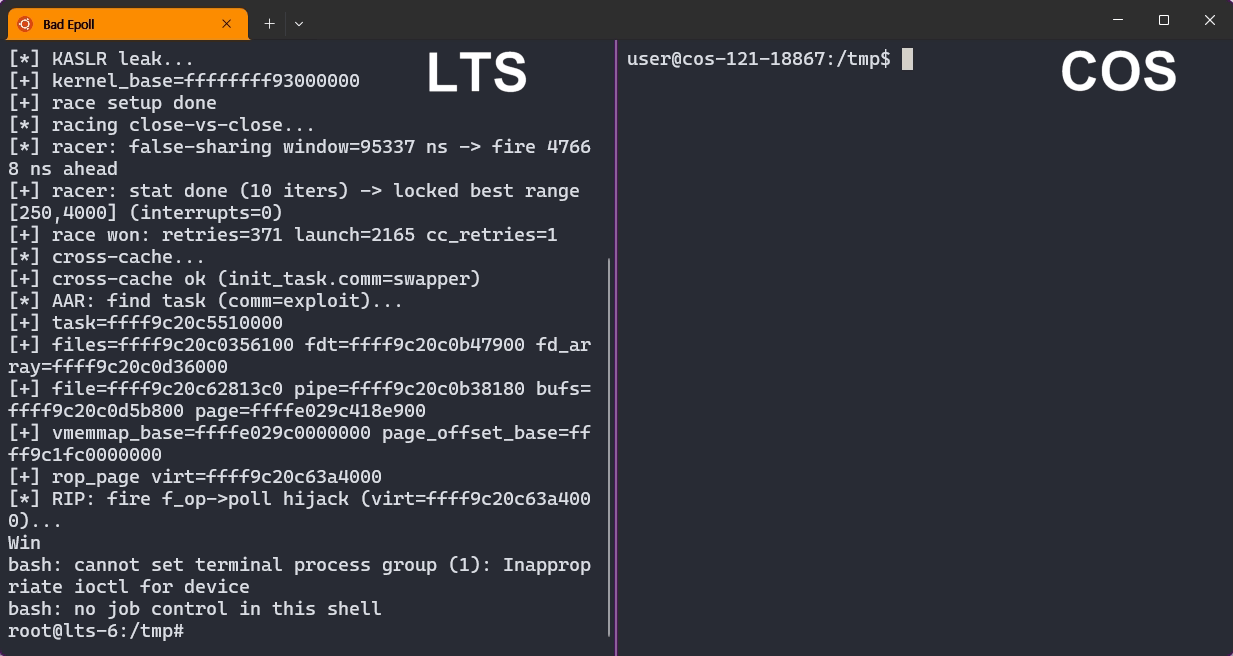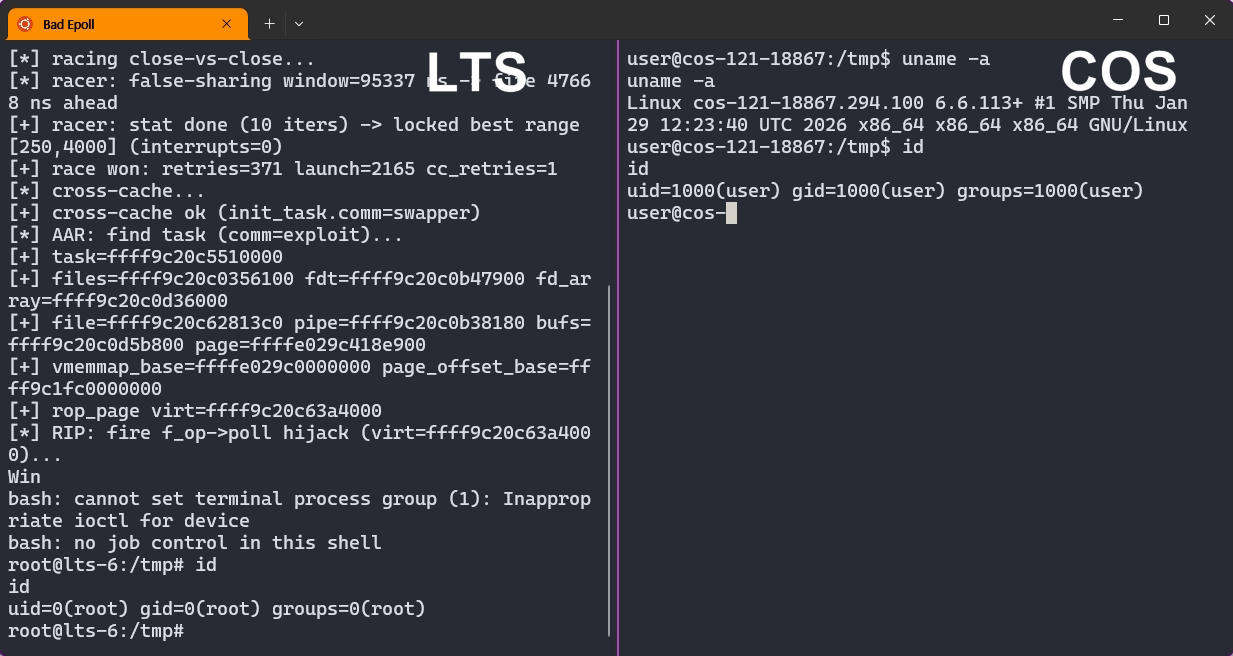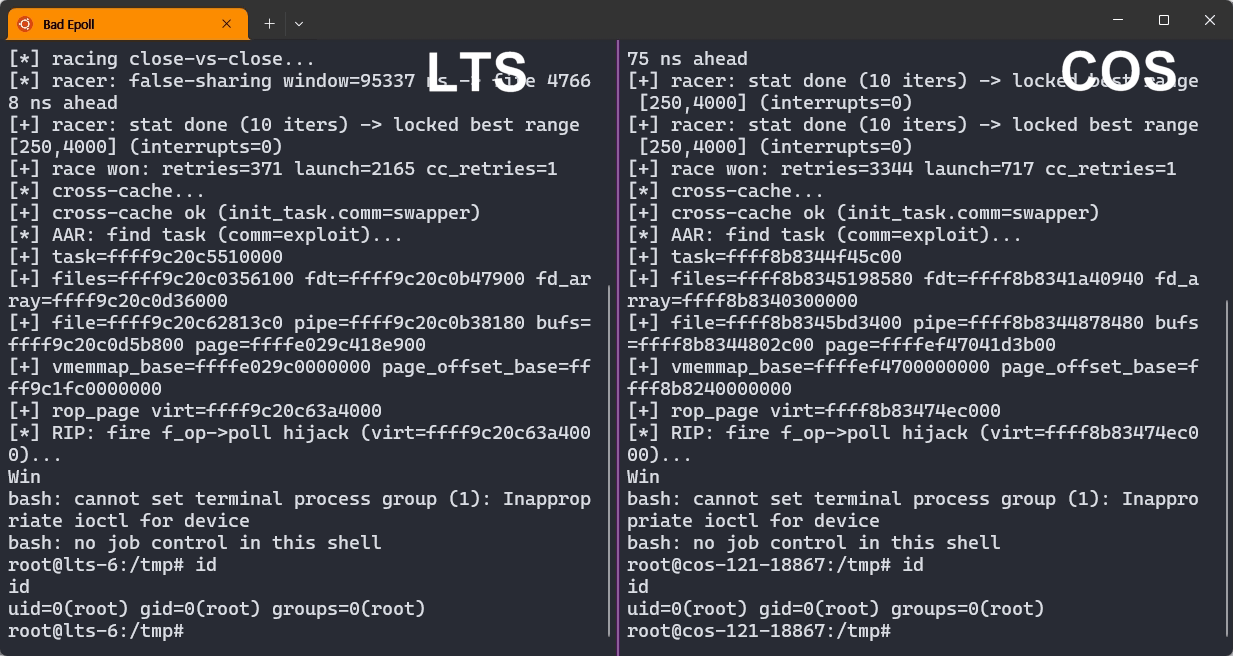 j-jaeyoung/bad-epoll
Linux kernel privilege-escalation exploit for CVE-2026-46242, a race-condition use-after-free in epoll, with 99% reliable root on desktops, servers,…
 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 bcoles/kasld
KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
 abraxas/n8n-function-vm2
Proof-of-concept and lab for an n8n 2.42.0 sandbox escape: hidden Function/FunctionItem nodes execute JS in the main process, giving authenticated…
 deathshotxd/0xkern3lcrush
Advanced PoC & Research for CVE-2026-0828 (Safetica) and CVE-2025-7771 (ThrottleStop). Analysis of BYOVD (Bring Your Own Vulnerable Driver) TTPs for…
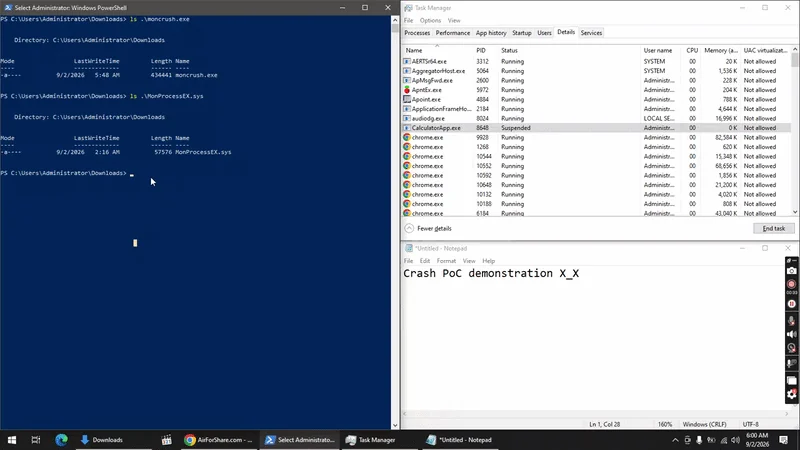 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 r41n3rzuf477/ps-ppl-bypass
Process Explorer vulnerable driver PPL Bypass
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 twosevenonet/injectsetconsole
Proof of Concept for Process Code Injection Without Using WriteProcessMemory
 mgiftson0/linux-env-vars-shellshock-lab
technical research & analysis on linux process execution, SUID privilege escalation, LD_PRELOAD hooking, and CVE-2014-6271 (shellshock).
 whoami-012/cve-2026-96515
Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
 pwardle/not-a-mused
Proof-of-concept exploiting an undocumented Muse dictation endpoint setting, letting a local unprivileged process redirect dictation traffic to…