CVE-2026-53921-PoC-Exploit

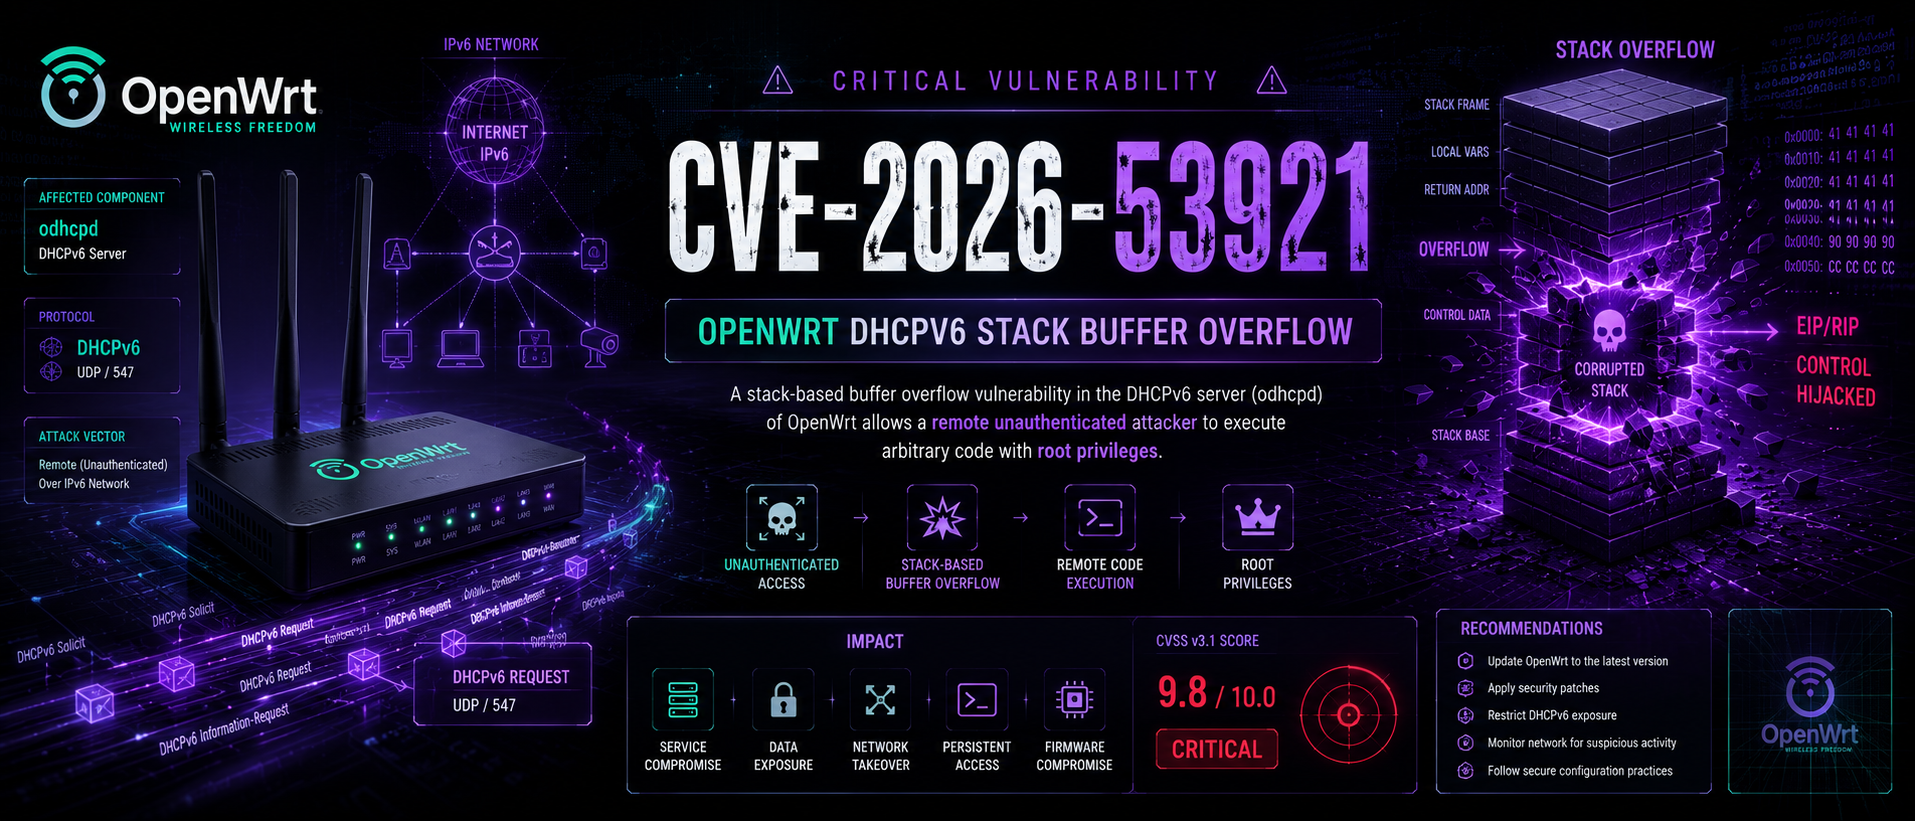
CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…

CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…

iQOO Neo8 (PD2301, 5.10.246 GKI) CVE-2026-43499 GhostLock 适配 · 48 宏 target.h + offsets.json + 15 轮实测 log · 只缺 write layer

Zimbra Collaboration Suite RCE — SMTP log poisoning → swatchdog → OS Command Injection (CVSS 8.9, CISA KEV)

GhostLock (CVE-2026-43499 / IonStack) research for OPPO Find X5 Pro (PFEM10): exploit chain, progress, blocker log, and OPPO 5-series kernel notes

Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…

Proof-of-concept that exploits a Kaspersky driver vulnerability to leak kernel pointers and bypass KASLR on Windows, enabling kernel exploit chain…

Stored XSS in Nagios Log Server 2024R1.3.1

Proof-of-concept for CVE-2026-62735, an integer overflow in http.sys leading to heap overflow and SYSTEM shell. Includes crash log and stack trace…

PoC for CVE-2026-34344, a Windows afd.sys type confusion causing a kernel crash via AfdQueryProviderInfo. Provides trigger code, crash log, and…

Proof-of-concept exploit for CVE-2026-59310, demonstrating remote path traversal via crafted syslog messages to write arbitrary log files on VMware…

Technical analysis and defensive mitigation for a WordPress Core pre-auth XSS-to-RCE chain, including sanitizer bypass, DOM clobbering, JSONP abuse,…

Proof-of-concept checker for CVE-2025-10951, an unauthenticated path traversal in ml-logger, validating arbitrary file read via /glob and /stream…

Python exploit script for Laravel Ignition CVE-2021-3129 RCE, using log poisoning and phar deserialization to execute commands on vulnerable web apps.

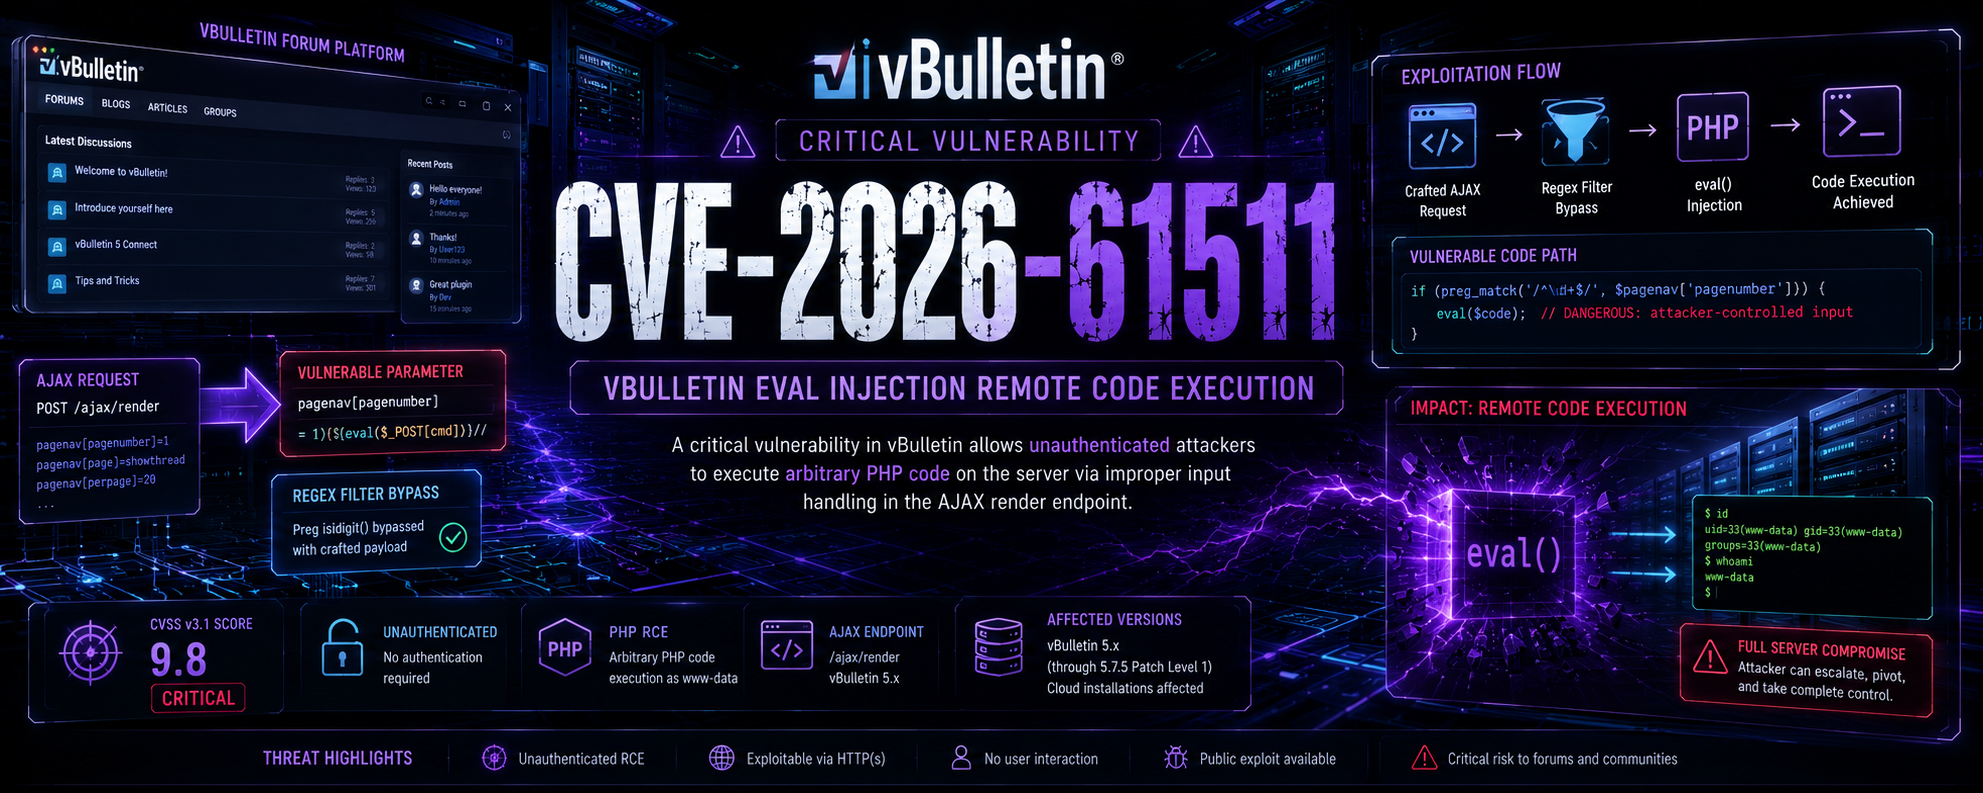
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…

Simulates CVE-2026-21011, a Log4j-style JNDI injection in a custom logger: parses ${jndi:...} patterns and demonstrates LDAP-triggered remote code…

CVE-2026-58025 — MediaWiki Deserialization RCE via Log Entry Import. LogEntryBase::extractParams() unserialize() user-controlled log_params. CVSS 9.8…

PoC exploit for Below privilege escalation (CVE-2025-27591) allowing local root access via symlink manipulation in world-writable log directory.

PoC for CVE-2026-53629, blind SQL injection in the GLPI history log filter