metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…

A standalone python script which utilizes python's built-in modules to enumerate SUID binaries, separate default binaries from custom binaries,…

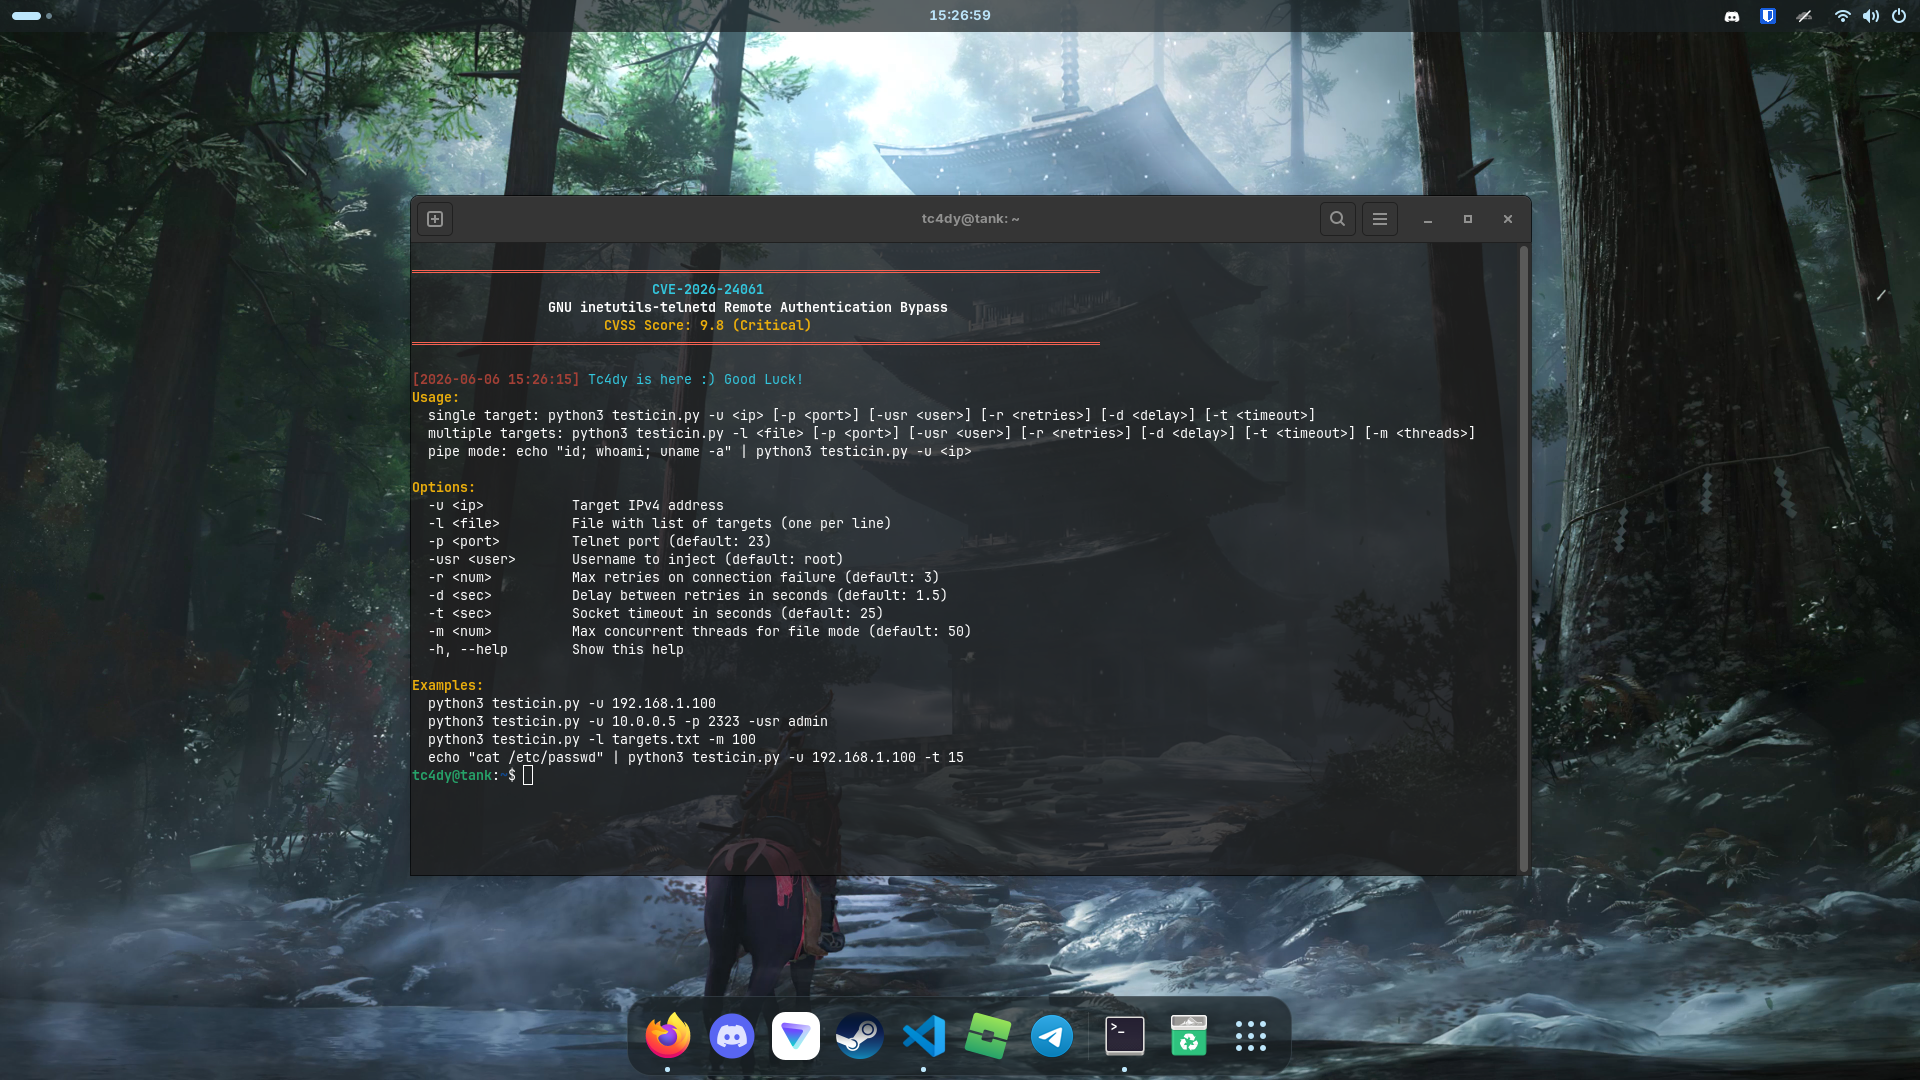
Remote authentication bypass exploit for GNU inetutils-telnetd (CVE-2026-24061) using CRLF injection to gain instant root shell. Supports single/mass…

A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…

Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…

PoC exploit for CVE-2024-4890: Sudo privilege escalation via neecdrestart (>=3.8). Ethical lab-only. Scripts in Python and C.

Signing-key abuse and update exploitation framework

Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…

Black-box remote probe that detects CVE-2026-98432, a Linux IPv4 TCP ireq_opt use-after-free, via differential SYN-ACK option echo, plus static…

PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…

CVE-2026-31431 Copy Fail — Linux kernel LPE tester via MCP

Prometheus v3.15.0 - High - Remote - SSRF - http_sd __unix_socket__ unsanitized Dial leftover of UDS scrape

Kafka Connect 4.3.1 - High - Windows FileStream classpath leftover - unauth file read/write

Proof-of-concept and lab for a GitLab CE webhook SSRF via the 0.0.0.0/8 this-network range, letting a Maintainer reach loopback and read responses…

Proof-of-concept lab demonstrating an authenticated SSRF in Gitea's hostmatcher allow-list, where a webhook to http://0.0.0.1 reaches loopback…

Proof-of-concept lab and exploit client for CVE-2026-59358, demonstrating Cloud Foundry UAA reuse of a user PKCE token as client_credentials Bearer…

Artifacts for the Branch Target Reuse (BTR) Spectre-v2 attack research, including microarchitecture experiments, attack-surface analysis of JIT…