
qyvora-toha3ee
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
exploitationnetwork-securityosint+9
4
qyvora/qyvora-toha3eeGo-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 cyeezy08/kimai-cve-2026-49865-poc
PoC exploits for CVE-2026-52824 (GHSA-jr9p-4h4j-6c58) — Kimai time-tracking default APP_SECRET authentication bypass affecting versions ≤ 2.57.0
 tanasescualexandrugabriel/vulnerability-assessment-and-osint-cve-2012-1823
This repository documents the process of identifying, analyzing, and gathering Open Source Intelligence (OSINT) on a specific security vulnerability…
 crussella0129/tricorne
a Fedora remix focused on pentesting and purple hat tooling
 sobri3195/pegasus-neo
PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…
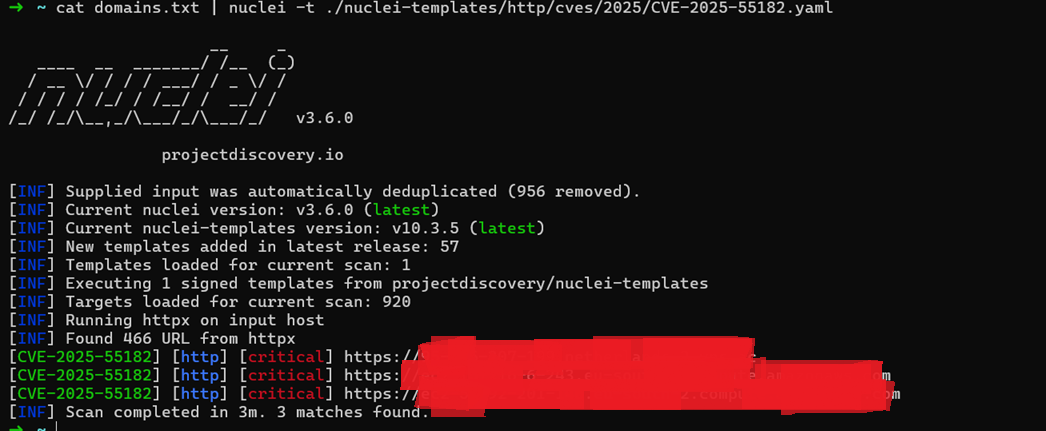 jaycelation/cve-2025-55182
PoC, Hunting React2Shell about CVE-2025-55182
 rdoix/cve-2024-21762-checker
Shodan-based scanner that discovers FortiGate SSL VPN devices and tests them for CVE-2024-21762 vulnerability, displaying organization and country…
 sunny-kathuria/exploit_cve-2022-26134
CVE-2022-26134, an OGNL injection vulnerability exists that would allow an unauthenticated attacker to execute arbitrary code on a Confluence Server…
 andripwn/pulse-exploit
Pulse Secure SSL VPN exploit (CVE-2019-11510) using hosts retrieved from Shodan API.
 649/pingpon-exploit
Exploit for Mass Remote Code Execution on GPON home routers (CVE-2018-10562) obtained from Shodan.
 lukebob-zz/c2-pwn
Uses Shodan API to pull down C2 servers to run known exploits on them.