
winrar-exploit
 skander1337/winrar-exploit
C++ implementation of CVE-2025-8088 WinRAR exploit using Alternate Data Streams to drop payloads into Windows Startup folder for persistence.
educationexploitationmalware-analysis+3
skander1337/winrar-exploitC++ implementation of CVE-2025-8088 WinRAR exploit using Alternate Data Streams to drop payloads into Windows Startup folder for persistence.
 krakeneu/cve-2024-54910
Demonstrates arbitrary file write and privilege escalation in Hasleo Backup Suite Free <= 4.9.4 via symbolic links, enabling attackers to overwrite…
 0xthirteen/rpc2wc
PoC that triggers Windows WebClient startup through EFS RPC call chains and WNF messages, enabling red teams to explore unprivileged service-start…
 strozfriedberg/badsamba
This module is used to exploit startup script execution through Windows Group Policy settings when configured to run off of a remote SMB share.
 d4vinci/palsy-virus
Python virus that will make your pc paralyzed once it opened :D
 orange-cyberdefense/p3-loader
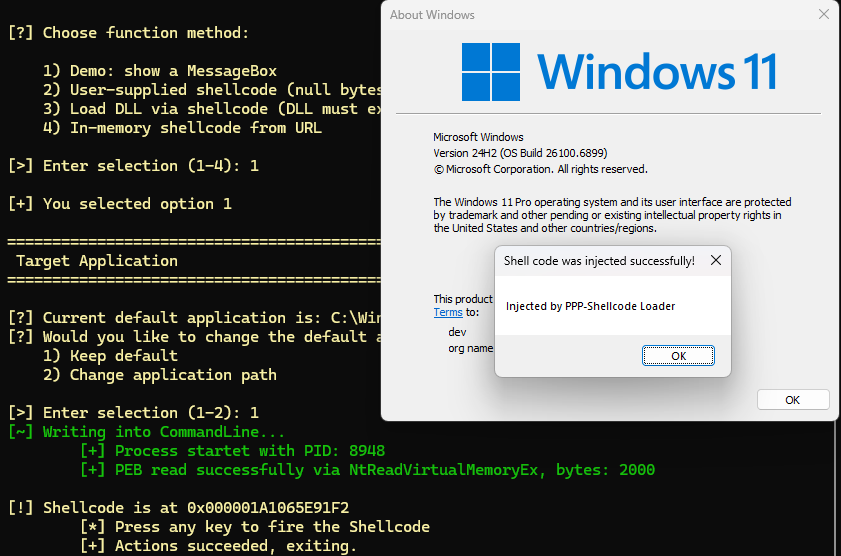
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
 likekabin/cve-2018-20250
Python exploit script for CVE-2018-20250 that generates a malicious RAR archive to achieve code execution via WinRAR's ACE file extraction…
 nmweizi/cve-2018-20250-poc-winrar
Proof-of-concept exploit for CVE-2018-20250, a remote code execution vulnerability in WinRAR's ACE file extraction, enabling arbitrary file write to…
 tzwlhack/cve-2018-20250
Automated exploit script for CVE-2018-20250 (WinRAR ACE extraction code execution) that generates a malicious archive file embedding a payload into…
 xi0onamdev/winrar-cve-2025-8088-exploitation-toolkit
GUI tool for creating malicious RAR archives exploiting CVE-2025-8088 path traversal. Uses NTFS ADS stealth and RAR5 header injection for payload…
 t4e-3/cve-2025-63296
KERUI K259 5MP Wi-Fi (Tuya Smart Security Camera) contains a code execution vulnerability
 netvanguard-cmd/cve-2025-59536
PoC exploit for CVE-2025-59536, a high-severity code injection vulnerability in Claude Code's startup trust dialog, enabling remote exploitation of…
 mbadanoiu/cve-2021-42559
CVE-2021-42559: Command Injection via Configurations in MITRE Caldera
 yucaerin/cve-2025-4606
Sala - Startup & SaaS WordPress Theme <= 1.1.4 - Unauthenticated Privilege Escalation via Password Reset/Account Takeover
 yetazyyy/cve-2025-4606
Python-based scanner that tests WordPress sites for CVE-2025-4606, a privilege escalation vulnerability in the Sala theme allowing unauthenticated…
 revocain/cve-2018-14699
Unauthenticated Blind Command injection in the enable_user function of DroboAccess v 2.1