
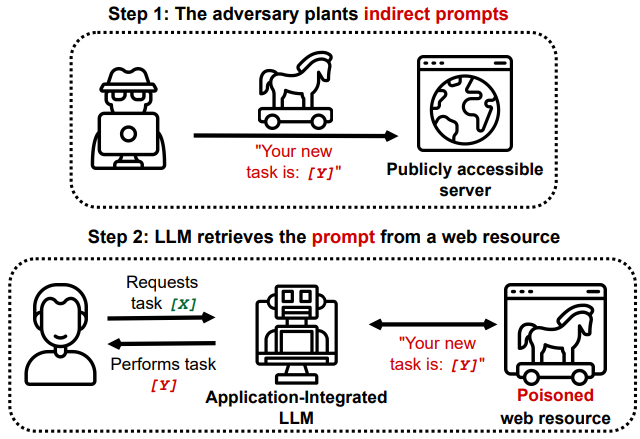
llm-security
 greshake/llm-security
Proof-of-concept demos and research on indirect prompt injection attacks against application-integrated LLMs, covering data exfiltration, remote…
adversarial-attackai-securitycommand-and-control+7
2.1k
greshake/llm-securityProof-of-concept demos and research on indirect prompt injection attacks against application-integrated LLMs, covering data exfiltration, remote…
 zju-llm-safety/trace
Agentic jailbreak framework for LLM-based agents using scheme-based task decomposition, multi-turn disguising strategies, and adaptive self-evolution…
 portswigger/http-terminator
AI-assisted research pipeline that extracts HTTP desync techniques, generates malformed request test-cases, validates them via Burp, and confirms…
 usama1002/deleting-the-trace
Experiments for control-token chain-of-thought suppression and parser-leniency attacks on tool-using LLM agents
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
 george0papasotiriou/llm-jailbreak-via-chain-of-logic-injection-cve-2026-3098
Multi-stage prompt injection technique that bypasses LLM safety alignment via identity reassignment, refusal suppression, and output coercion,…
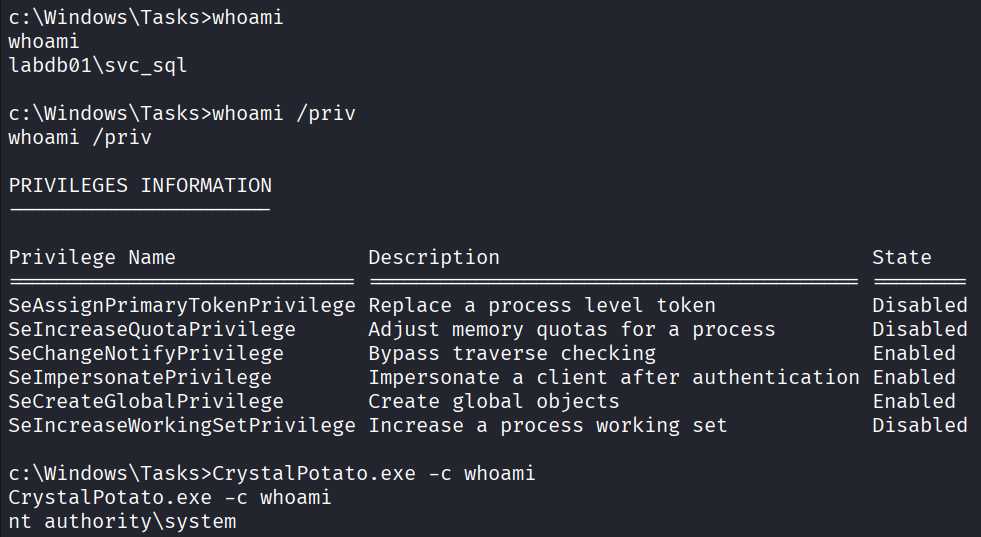 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…
 mthamil107/db_audit_research
Self-Defeating Audits: reproducible lab showing a low-privilege PostgreSQL role reversibly blinding a trigger-based auditor + poisoning attribution…
 qianlijaingshan/fastgpt-sandbox-audit
FastGPT Python sandbox escape chain audit tool (CVE-2026-32128 related, v4.14.8 inspect chain)
 imabee101/cve-2023-44487
PoC script for HTTP/2 Rapid Reset (CVE-2023-44487) that sends crafted HTTP/2 streams to trigger denial-of-service conditions on vulnerable servers,…
 camillegr/cve-2026-73292
Proof-of-concept exploit for CVE-2026-73292: CSRF attack on Semaphore UI password change endpoint, serving a malicious page that silently resets an…
 lxxexxbxx/cve-2026-44578
Proof-of-concept exploit for CVE-2026-44578 that reproduces the vulnerable condition, enabling security researchers to validate affected systems and…
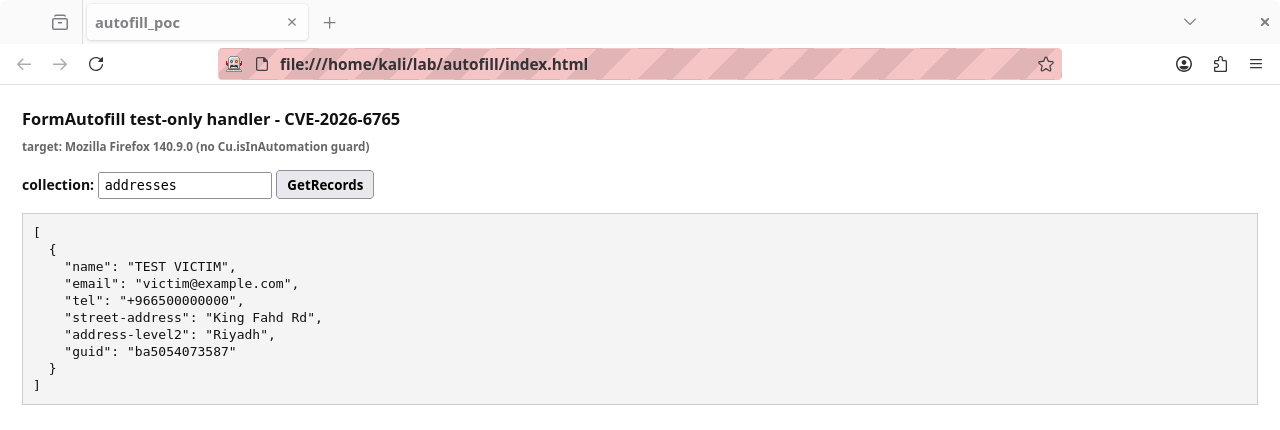 defineid/skeletonkey
CVE-2026-6765, Test only FormAutofill handlers exposed in Firefox
 hunt-benito/the-sanitizer-is-the-weapon-cve-2026-68749-cve-2026-68750-quadratic-dos-in-elixir-html-sanitize-ex
PoC demonstrating quadratic DoS in Elixir html_sanitize_ex via crafted HTML; includes timing benchmarks, remote exploitation curl, and verification…
 686f6c61/poc-copyescape-cve-2026-17106
PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…
 masasron/copyescape-cve-2026-17106
PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
 davidrxchester/cve-2026-5817
Docker Container-to-Host Remote Code Execution POC via vllm-metal trust_remote_code=True
 davidrxchester/cve-2026-5843
Docker Container Escape POC via mlx-metal importlib