stealth_call
 kitsune-de/stealth_call
Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
anti-botdefensive-toolsexploitation+3
7
kitsune-de/stealth_callHeader-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
 t3bik/cve-2026-75898
Proof-of-concept for CVE-2026-75898, an SSRF in RAGFlow's Invoke component. Demonstrates the vulnerability with unmodified source, includes E2E…
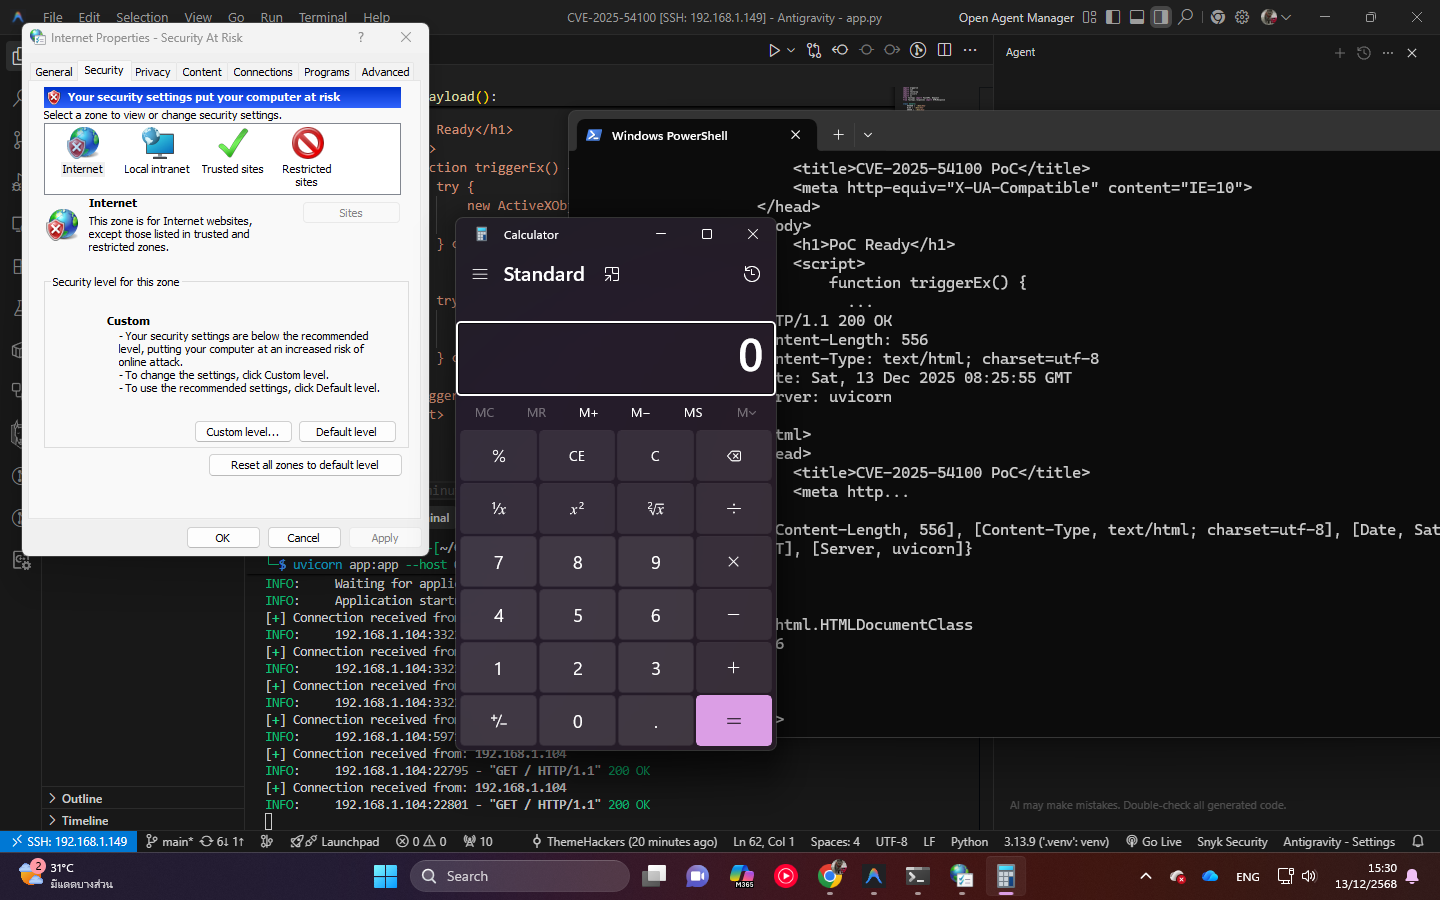 xiaolvchen/cve-2025-54100
CVE-2025-54100(PowerShell 远程代码执行漏洞)
 tntrock/cve-2024-4577_powershell
使用PowsrShell掃描CVE-2024-4577
 ianthinus/cve-2024-4577
Proof-of-concept exploit for CVE-2024-4577, a PHP CGI argument injection vulnerability enabling remote code execution via crafted HTTP requests.
 sh4den/cve-2025-48827
This repository contains a proof-of-concept exploit for CVE-2025-48827, a critical authentication bypass vulnerability affecting vBulletin…
 gabriel-lacorte/cve-2025-7771
Arbitrary Function Call Exploit using the ThrottleStop driver

 comparedarray/printix-cve-2022-29554
A "Mishandling of Input to API" or "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure…
 blueisbeautiful/cve-2025-53691
Remote code execution (RCE) through insecure deserialization
 b1g-b33f/cve-2020-36708
Proof of concept for CVE-2020-36708
 b5null/invoke-badsuccessor.ps1
PowerShell Script to automatically abuse the BadSuccessor vulnerability (CVE-2025-53779)
 000tonio/cve-2021-1675
PowerShell exploit for CVE-2021-1675 PrintNightmare that disables AMSI and creates a local administrator account on vulnerable Windows systems.
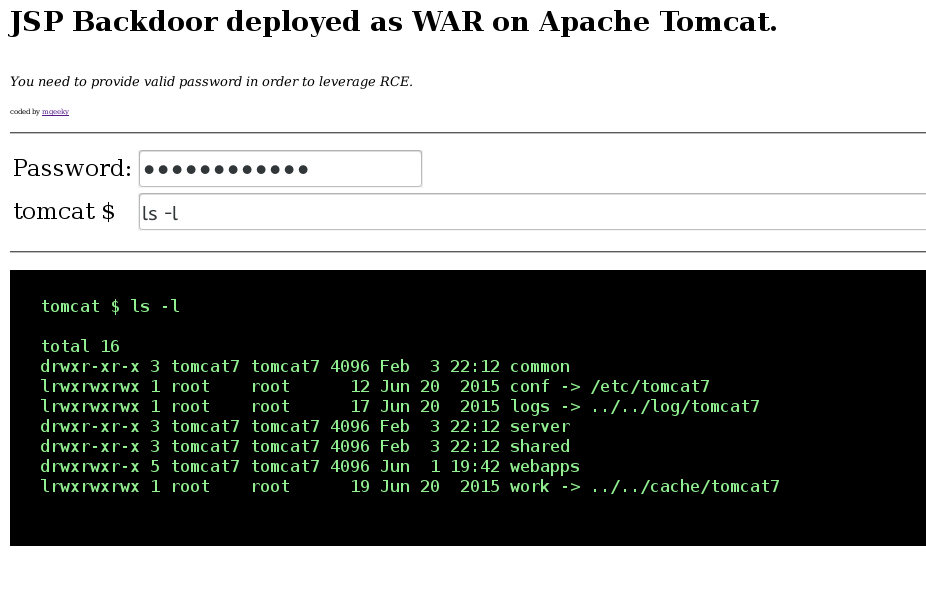 mgeeky/tomcatwardeployer
Apache Tomcat auto WAR deployment & pwning penetration testing tool.
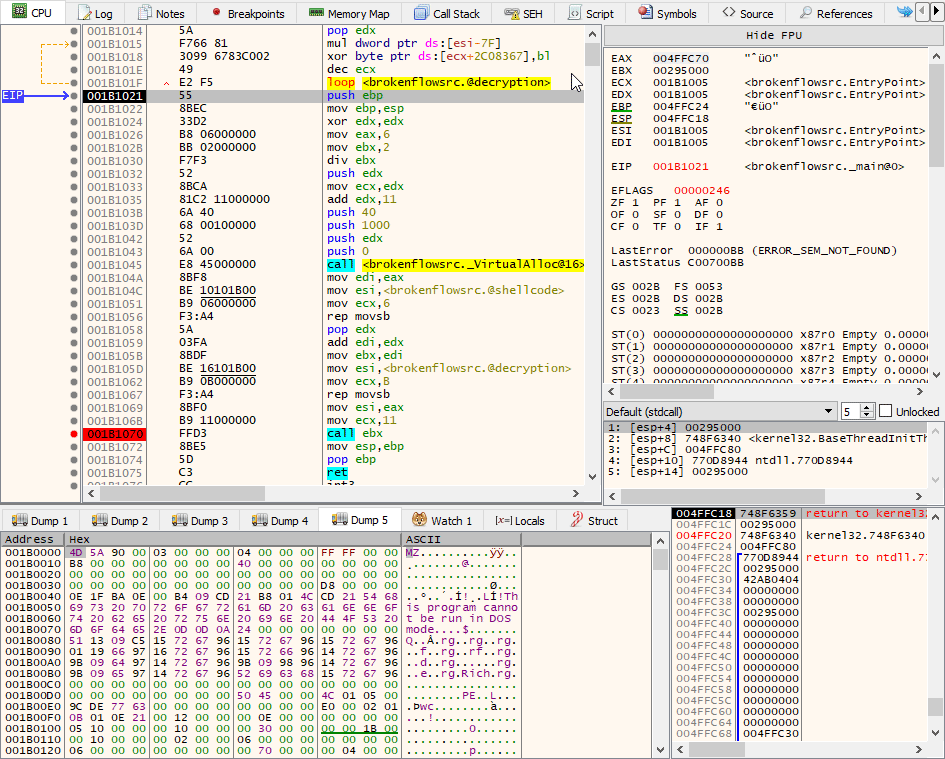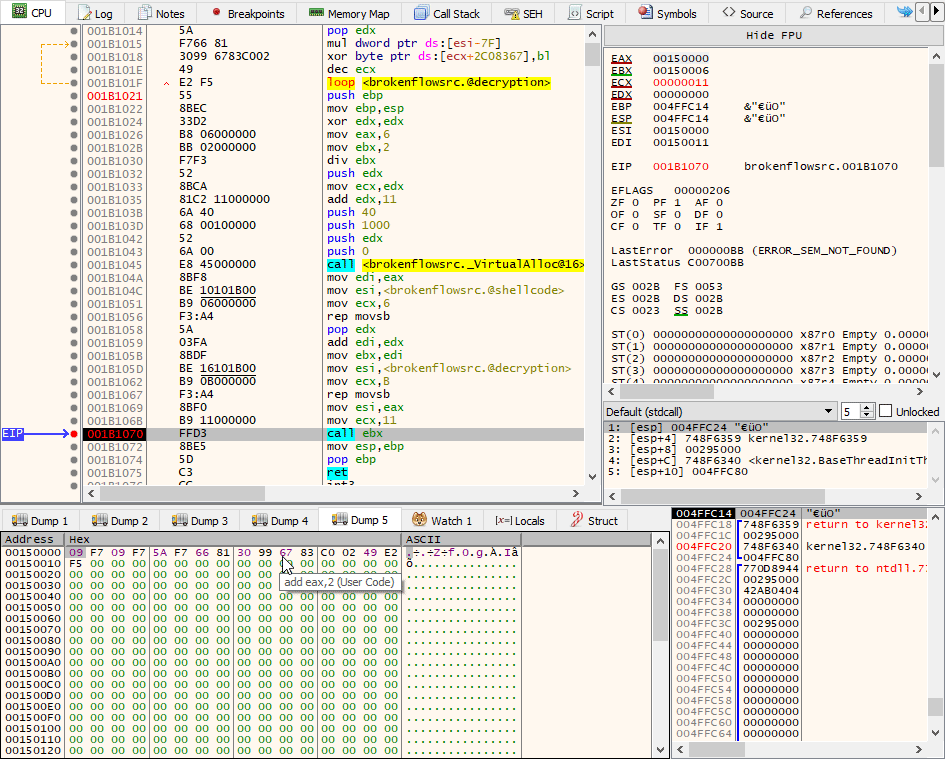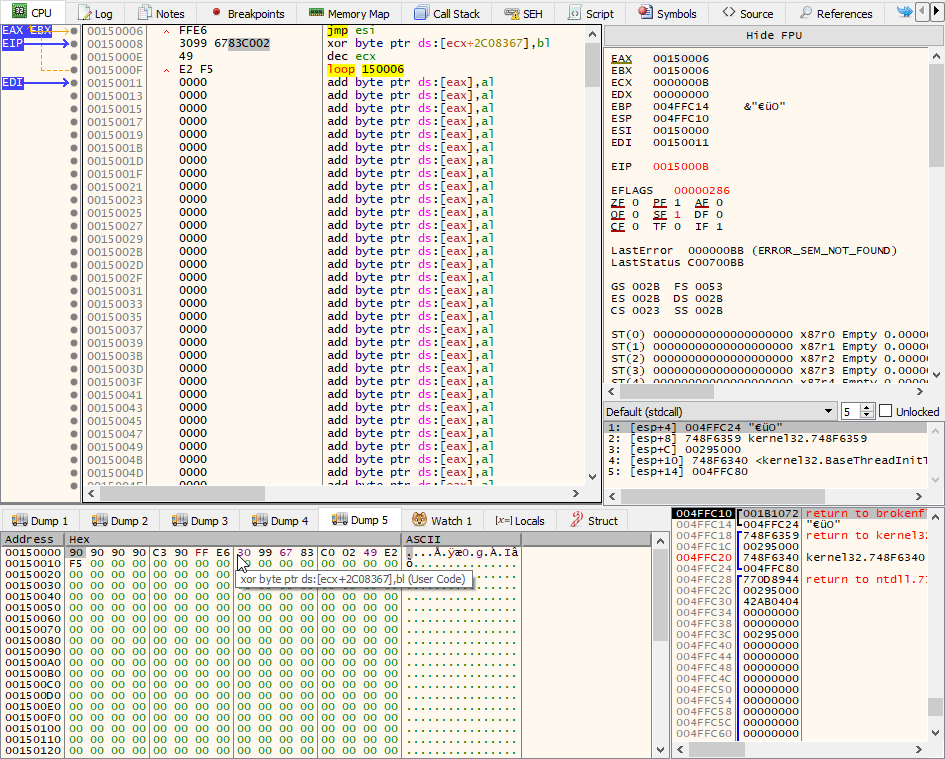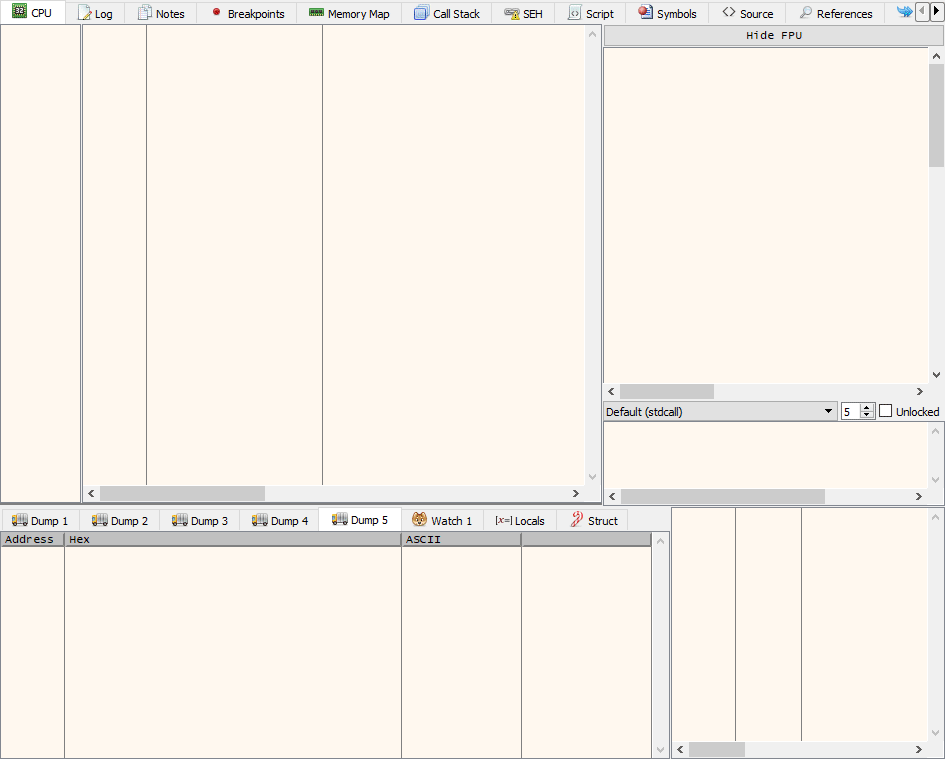 enkomio/brokenflow
A simple PoC to invoke an encrypted shellcode by using an hidden call
 checkymander/sharp-smbexec
C# implementation of SMBExec for remote command execution on Windows targets using NTLM password hashes, enabling lateral movement and pass-the-hash…