

CVE-2026-48907
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
exploitationpayload-developmentpenetration-testing+6
noname-elv/cve-2026-48907Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
 jaycelation/cve-2026-25645
Insecure Temp File Reuse in extract_zipped_paths()
 zerodayvpn/cve-2026-24291
About 2026 Guide: Bypass User Account Control Prompts on Windows 11
 burakacar6/cve-2023-42793-teamcity-unauthenticated-rce
A PoC and automated version detection/exploit tool for JetBrains TeamCity Authentication Bypass & RCE (CVE-2023-42793).
 ternopil-te-te-t4p/cryptoquant-key-gen
Patcher utility that bypasses CryptoQuant premium tier restrictions to unlock advanced analytics and real-time data access, with a Python GUI for…
 withsecurelabs/doublepulsar-usermode-injector
A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…
 null200ok/cve-2026-41940-tool
A comprehensive Python utility to **detect**, **scan in bulk**, and **exploit** the critical authentication bypass vulnerability (CVE-2026-41940) in…
 mbanyamer/cve-2026-25130-cybersecurity-ai-cai-framework-0.5.10
Proof-of-concept demonstrating argument injection leading to OS command injection in the CAI framework's find_file utility, enabling arbitrary…
 krn966/cve-2025-27591
Local privilege escalation exploit for CVE-2025-27591, abusing insecure symlink handling in the below utility's logging to overwrite arbitrary files…
 onedemobird/copy-fail-cve-2026-31431-pythonlower3.10
Python 3.10-compatible implementation of the CVE-2026-31431 exploit, providing a workaround for missing os.splice in older Python versions.
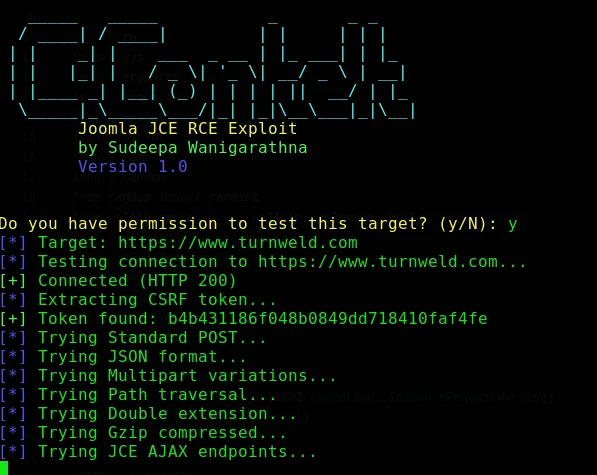 cerberusmrxi/jcezploit-cve-2026-48907
Automated RCE exploit for Joomla JCE (CVE-2026-48907) with interactive shell, batch command execution, file download, and proxy support for…
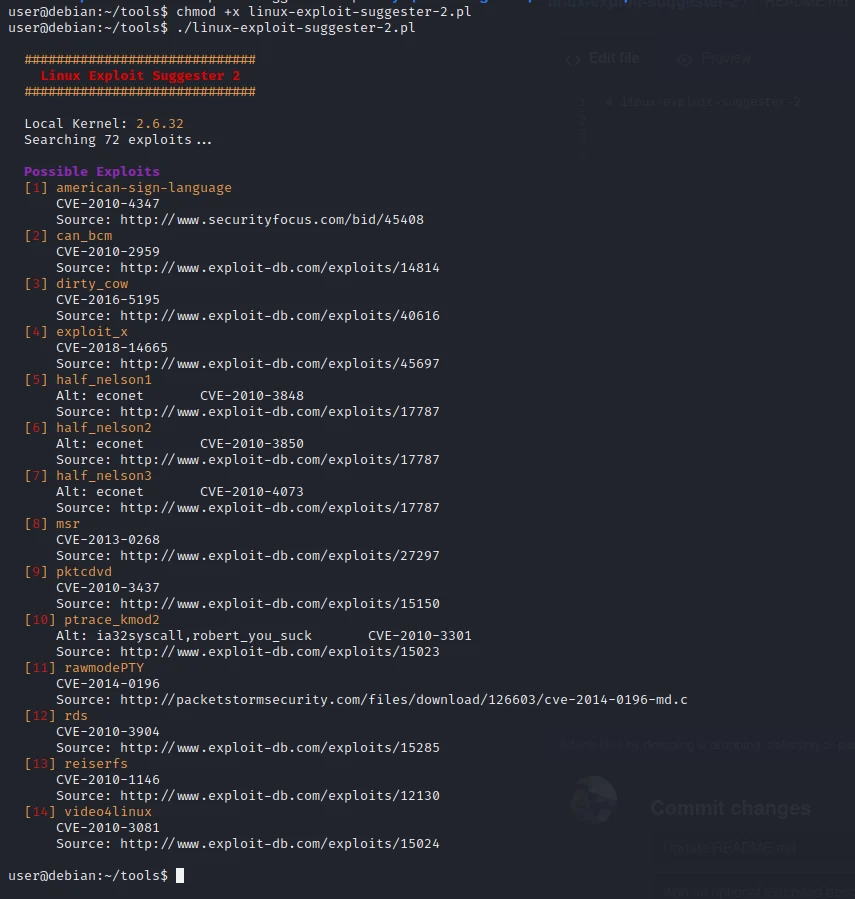 h3x0v3rl0rd/linux-exploit-suggester-2
Post-exploitation utility that scans kernel/OS version and configuration to suggest applicable local privilege escalation exploits.
 whatswrongandwhy/ptrace
Linux ptrace-based process tracing and debugging utility for inspecting system calls, memory, and program execution flow.
 gmh5225/androiddrivesignity
AndroidDriveSignity is a Python utility designed to bypass driver signature verification in Android kernel(ARMv8.3), facilitating the loading of…
 pimpamebanihah/cve-2026-43499-app.s0
Placeholder repository referencing CVE-2026-43499; no source code, documentation, or security functionality is evidenced in the available metadata.
 waawaa/breakcyserver
Red-team EDR evasion utility that terminates security services by abusing Process Explorer driver functionality to bypass PPL and ObRegisterCallbacks.
 yogagymn/xss2shell-cve-2026-64638
Authorized WordPress XSS-to-RCE scanner with concurrent multi-target XSS reflection and version fingerprint detection, plus optional exploitation…
 breakfix/sharpscom
A C# utility for interacting with SCOM