CVE-2026-84118-who-labeled-the-crit-as-a-high

Proof-of-concept for CVE-2026-84118, a SpiderMonkey GC use-after-free leading to out-of-bounds read/write and potential code execution. Includes…

Proof-of-concept for CVE-2026-84118, a SpiderMonkey GC use-after-free leading to out-of-bounds read/write and potential code execution. Includes…

Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…

Proof-of-concept exploit for CVE-2026-6770 targeting Firefox and Tor browsers, demonstrating the vulnerability and enabling security researchers to…

Firefox content->parent srcdoc forge (N-day, bug 2040160): forged PDocumentChannel with SrcdocData on a non-about:srcdoc URI -> attacker HTML served…

Firefox content-to-parent IPDL privilege escalation (N-day, bug 2054416): forged PDocumentChannel with RemoteTypeOverride -> privilegedabout process…

Full Firefox chain: CVE-2026-2796 wasm type confusion -> content-process RCE, plus CVE-2026-2768 parent-process escape analysis (both fixed in…

CVE-2026-74945, Uninitialized heap disclosure via a crafted web font (sec-high)

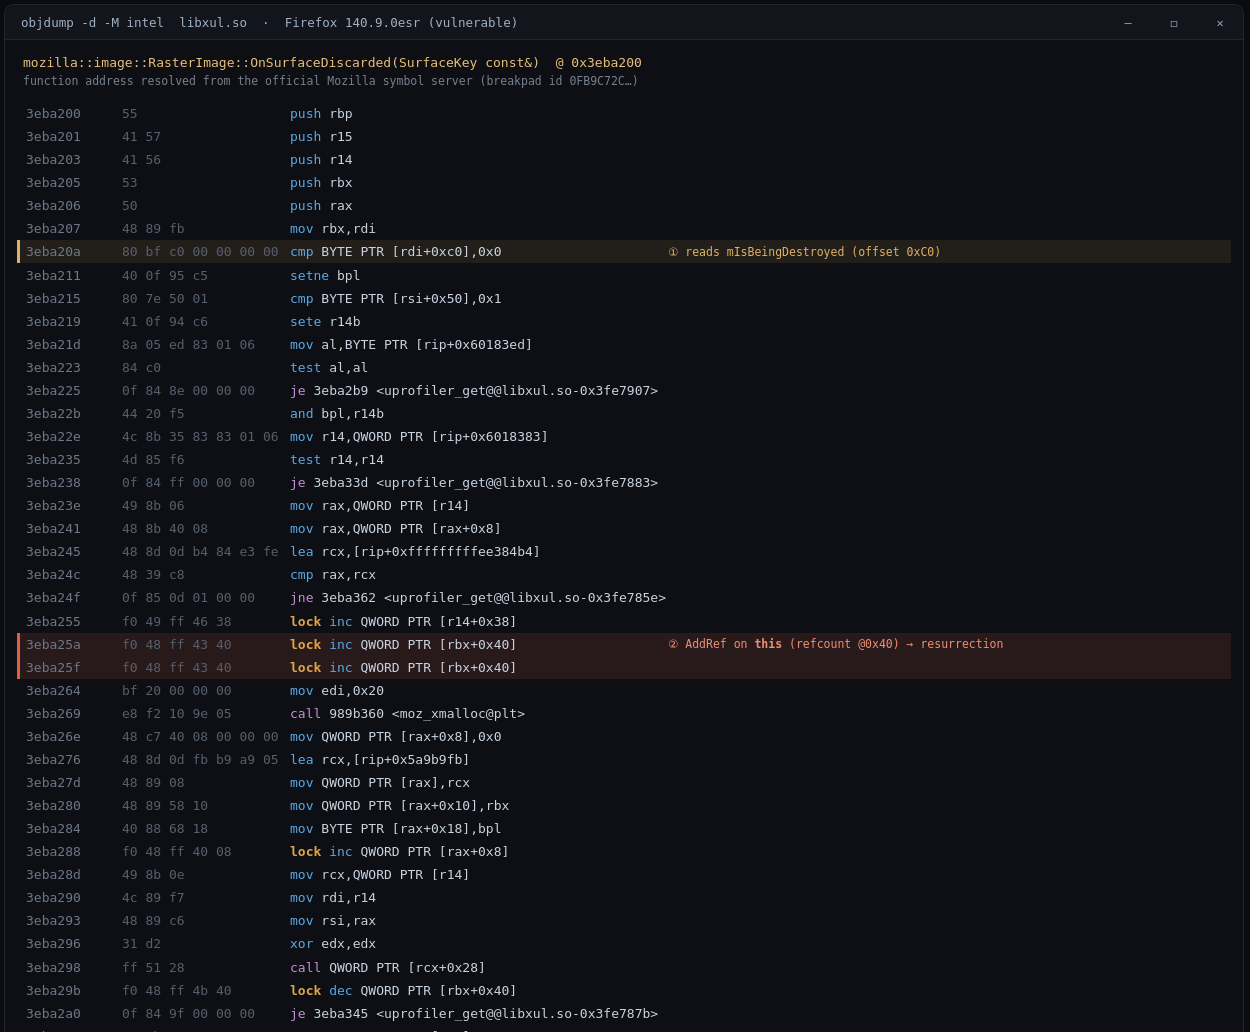
CVE-2026-74943, Use after free in Firefox RasterImage (sec-high)

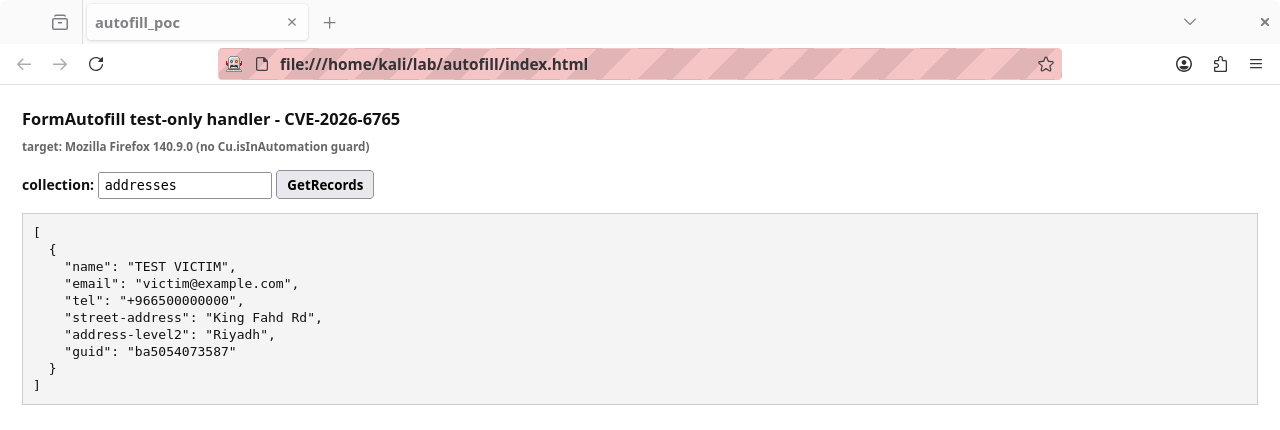
CVE-2026-6765, Test only FormAutofill handlers exposed in Firefox

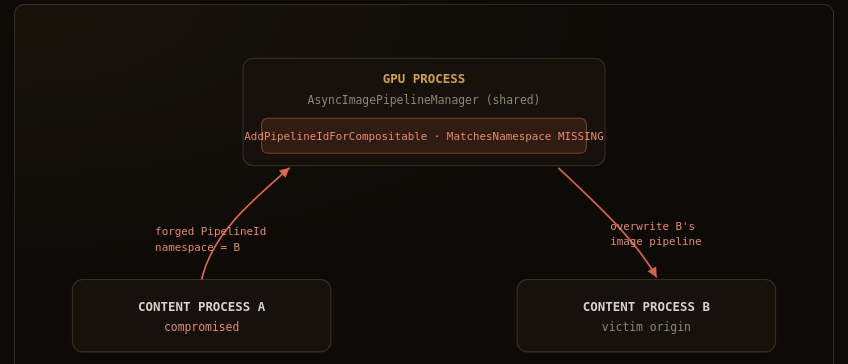
CVE-2026-74970, Fission site isolation bypass in Firefox WebRender

Proof-of-concept exploit chain for Firefox JIT CVE-2026-2764, chaining JIT miscompilation and use-after-free into arbitrary read/write and WASM…

An updated collection of resources targeting browser-exploitation.

A collection of web browser CTF challenges and solutions.

A personalized/enhanced re-creation of the Darkhotel "Double Star" APT exploit chain with a focus on Windows 8.1 and mixed with some of my own…

A personal collection of Windows CVE I have turned in to exploit source, as well as a collection of payloads I've written to be used in conjunction…

Hands-on lab for CVE-2024-4367, demonstrating PDF.js font rendering vulnerability exploitation in Firefox. Includes PoC generator, vulnerable and…

Firefox/Tor Browser 0day exploit analysis (CVE-2024-9680) A UAF in animation timelines leading to RCE. Patched.

Firefox extension for detecting and exploiting CVE-2025-55182 — Prototype Pollution RCE in Next.js React Server Actions