

CVE-2020-0022
 idkwim/cve-2020-0022
Research repository documenting BlueFrag (CVE-2020-0022) Android Bluetooth heap overflow experiments, including GDB crash analysis and memcpy…
android-securitybinary-exploitationbluetooth-security+4
idkwim/cve-2020-0022Research repository documenting BlueFrag (CVE-2020-0022) Android Bluetooth heap overflow experiments, including GDB crash analysis and memcpy…
 v3ilsm1th/cve-2023-45866_wip
Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…
 v3ilsm1th/cve-2024-53027-wip
Proof-of-concept for CVE-2024-53027, a Wi-Fi beacon Country IE denial-of-service vulnerability affecting Qualcomm WLAN chipsets. Includes educational…
 shaikusaf/system_bt_aosp10_r33_cve-2021-0435
AOSP Bluetooth stack repository modified for CVE-2021-0435, providing a patched or vulnerable version for analysis and testing of Bluetooth…
 shaikusaf/system_bt_aosp10_r33_cve-2021-0431
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0431, enabling analysis and testing of Bluetooth vulnerabilities in AOSP 10.
 jjjjjjjj987/cve-2023-45866-py
Python-based proof-of-concept for CVE-2023-45866, a Bluetooth vulnerability, demonstrating exploitation techniques for security research and testing.
 shaikusaf/packages_apps_bluetooth_aosp10_r33_cve-2021-0329
Android Bluetooth package with modifications addressing CVE-2021-0329, a critical remote code execution vulnerability in Bluetooth. Provides patched…
 sgxgsx/bluetoolkit
Modular Bluetooth Classic (BR/EDR) vulnerability testing framework with reconnaissance, exploit modules for 43 public attacks/CVEs, and structured…
 francozappa/bluffs
Toolkit for testing Bluetooth session establishment against forward and future secrecy attacks, using firmware patching, PCAP analysis, and automated…
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 nanopathi/packages_wpa_supplicant8_cve-2021-0326
Source code of wpa_supplicant and hostapd, focused on CVE-2021-0326 vulnerability for analysis, testing, and understanding of Wi-Fi security flaws.
 nanopathi/system_bt_aosp10_r33_cve-2021-0476
Android Bluetooth stack (AOSP 10 r33) containing CVE-2021-0476 for vulnerability analysis, exploitation testing, and security research.
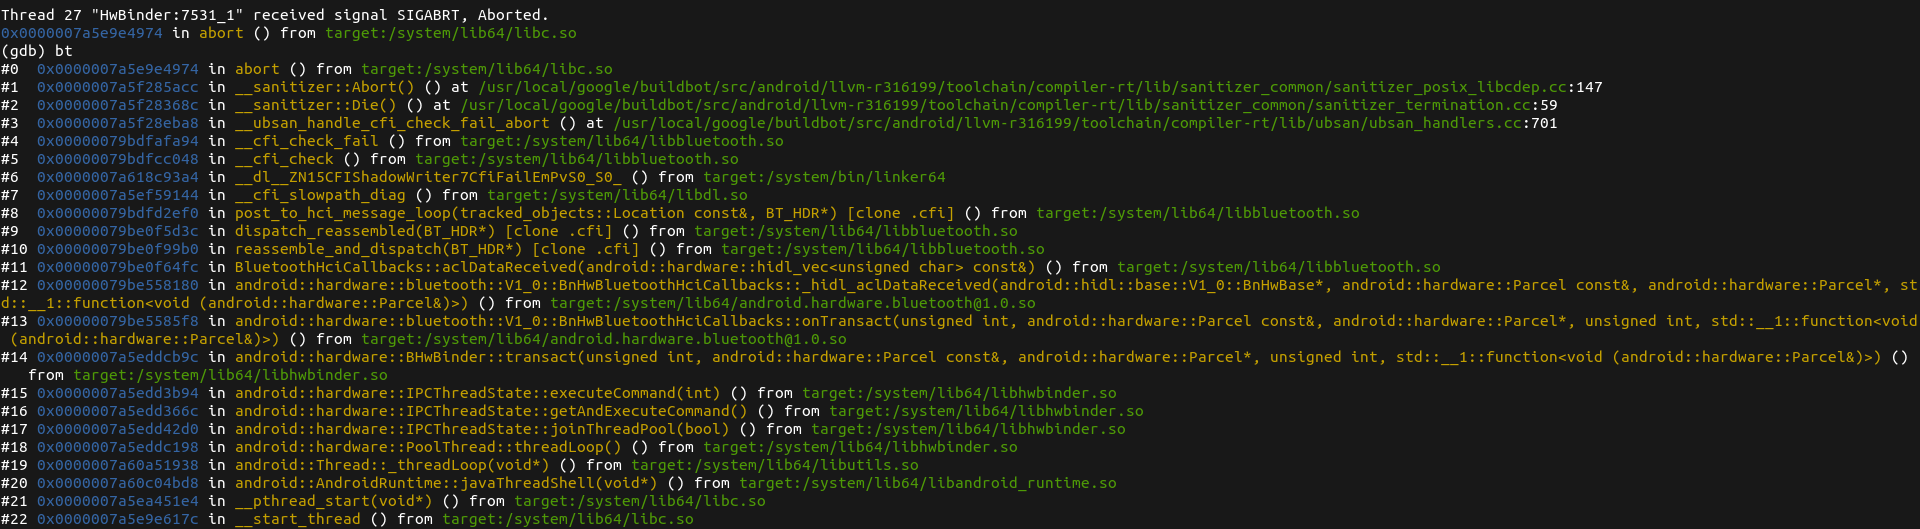 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
 zalexdev/wpair-app
WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…
 nanopathi/system_bt_aosp10_r33_cve-2020-0471
Android Bluetooth stack (Fluoride) with a proof-of-concept exploit for CVE-2020-0471, enabling vulnerability analysis and exploitation testing on…
 nanopathi/system_bt_aosp10_r33_cve-2020-0463
Android Bluetooth stack (Fluoride) with a fix for CVE-2020-0463, enabling security analysis and exploitation testing of Bluetooth vulnerabilities on…
 nanopathi/system_bt_aosp10_r33_cve-2020-0225
Exploit for CVE-2020-0225 in the Android Fluoride Bluetooth stack, enabling remote code execution via a crafted Bluetooth packet. Includes build…
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025