LinusWare-Source-Code-Internal

Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…

Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…

CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.

Static reverse-engineering analysis of movement input heuristics in Source 2 engine, identifying structural edge cases in input automation and jump…

Academic Research Edition - T1: User-mode evasion (obfuscation + syscall gateway), T2: BYOVD kernel bridge, T3: DMA hardware (future work).

Builds a root exploit for vivo/iQOO devices targeting CVE-2026-43499, leveraging kernel techniques like KASLR bypass and CFI manipulation to achieve…

Proof-of-concept exploit for CVE-2026-2763, a use-after-free in Mozilla's JavaScript engine, demonstrating a constrained 1-bit write primitive…

Proof-of-concept for CVE-2026-2441, a use-after-free in Chrome's CSS engine, demonstrating renderer crash and potential sandboxed code execution via…

Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…

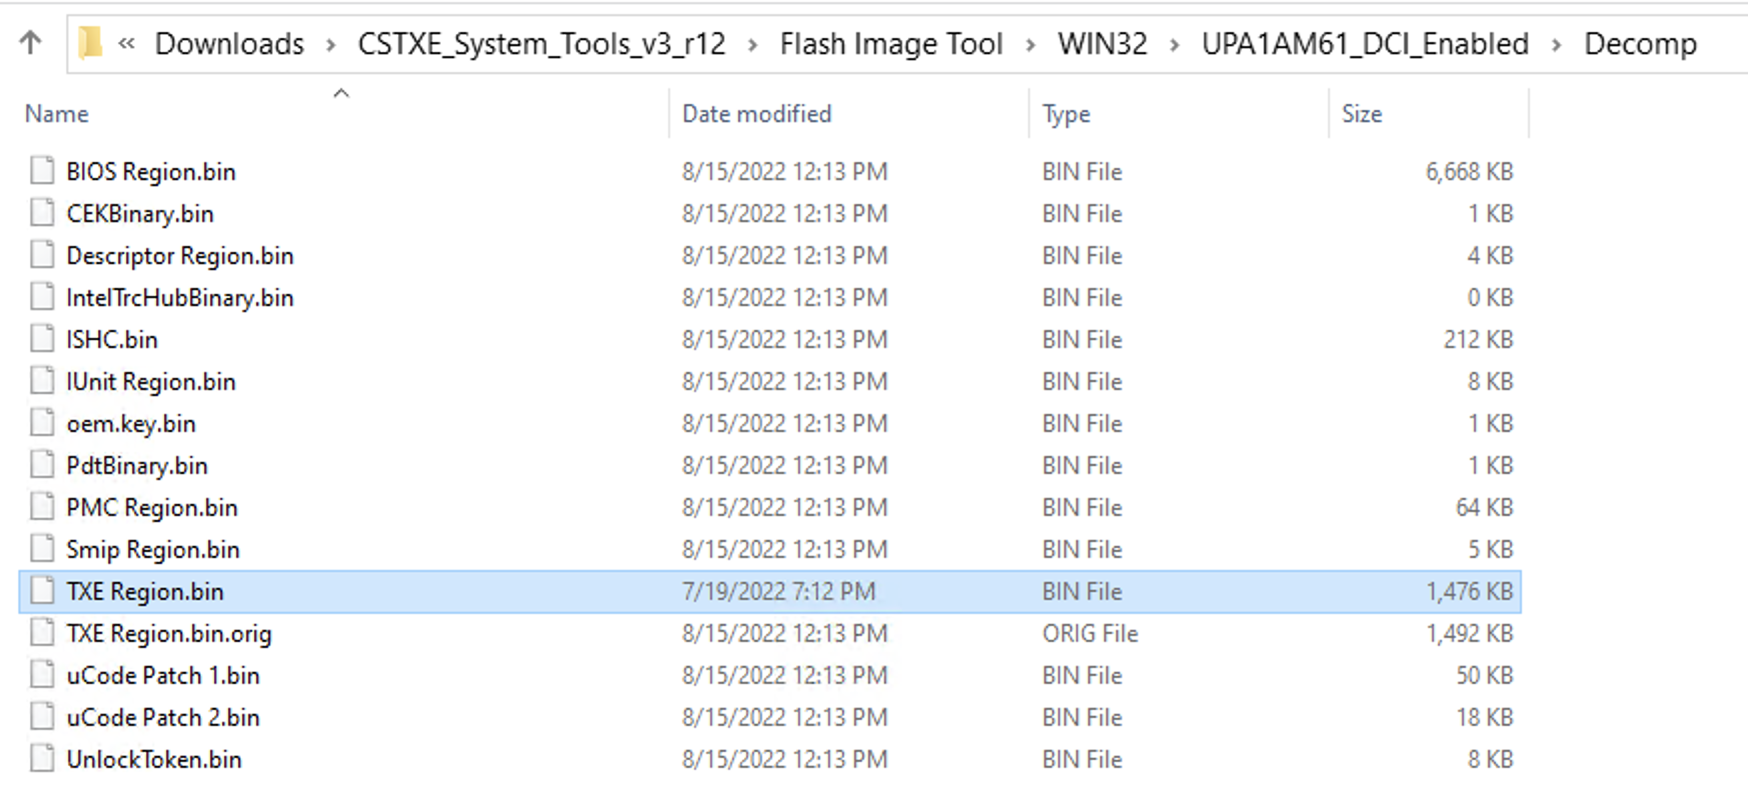
Intel Management Engine JTAG Proof of Concept - 2022 Instructions

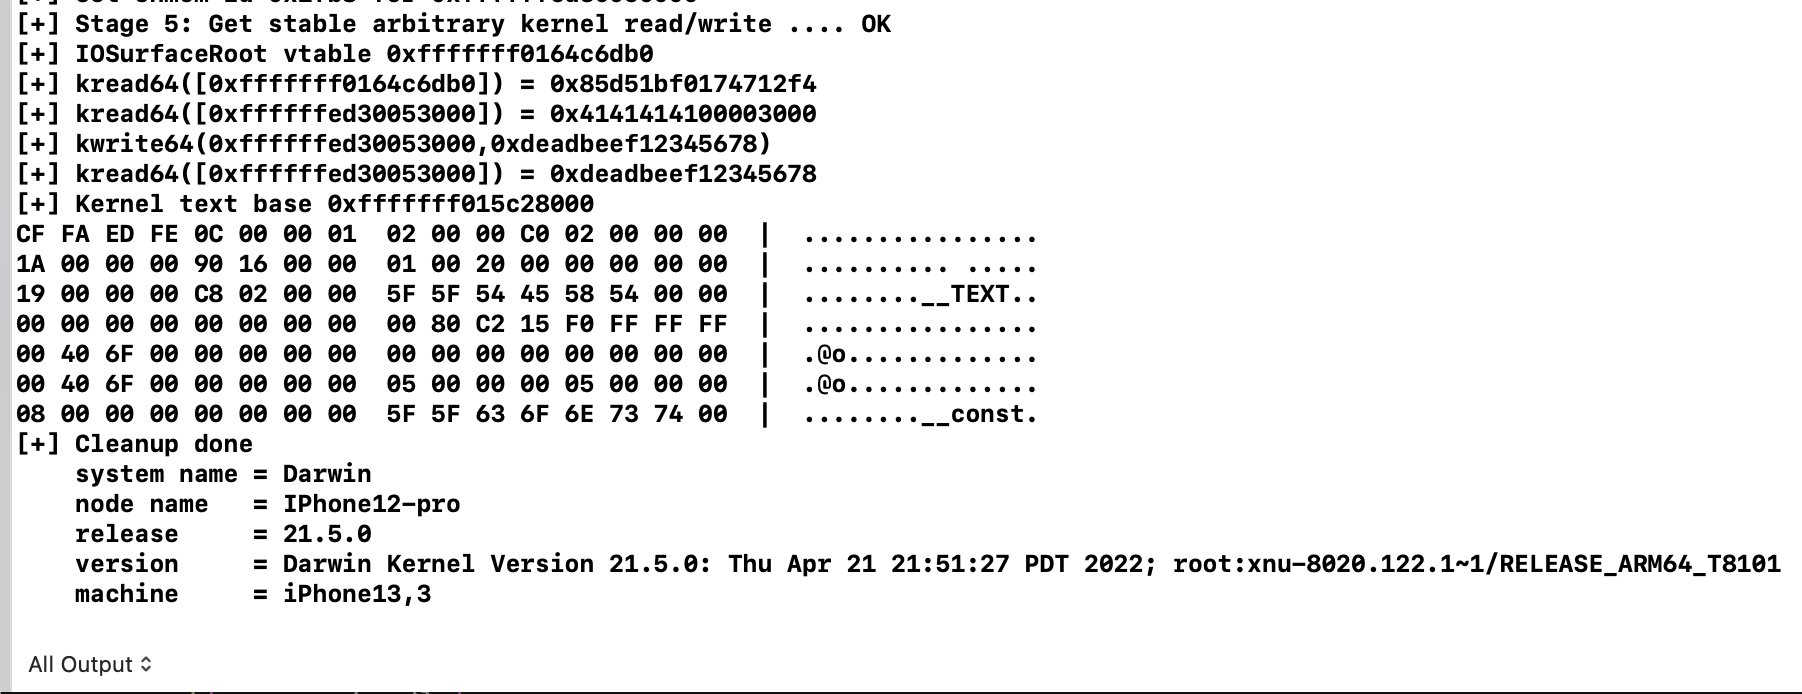
ANE kernel r/w exploit for iOS 15 and macOS 12

bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)

A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…

Penetration testing framework with AI-driven decision engine

A pure-python fully automated and unattended fuzzing framework.

x86 Inline hooking engine (using trampolines)

Technical analysis and exploit demonstration of CVE-2022-32898, a kernel memory corruption vulnerability in Apple Neural Engine driver, with detailed…

Exploit for CVE-2022-25173 targeting Jenkins Pipeline Groovy Plugin's CPS interpreter sandbox bypass, enabling arbitrary code execution within…

Exploit for CVE-2026-14431 providing V8 sandbox read/write primitives via a crafted JavaScript file, targeting Chromium's V8 engine on Linux x64.