

CVE-2026-15667
 cflowsec/cve-2026-15667
Python proof-of-concept for CVE-2026-15667, an authenticated local file inclusion in the WordPress Eventin plugin via the event_layout REST field.
exploitationpenetration-testingvulnerability-analysis+3
cflowsec/cve-2026-15667Python proof-of-concept for CVE-2026-15667, an authenticated local file inclusion in the WordPress Eventin plugin via the event_layout REST field.
 cflowsec/cve-2026-14962
Wordpress Plugin ELEX WooCommerce Request a Quote unauthenticated SQL injection
 jasper2018/cve-2018-20062
Verification script and PoC for CVE-2018-20062, the ThinkPHP 5.0.x invokefunction deserialization RCE, confirming route reachability and capturing…
 4rt-net/mikrotrick_poc
Testing tool for the Mikrotrick exploit (CVE-2026-67276)
 gmh5225/cve_2023_44487-rapid_reset
Python-based testing tool for CVE-2023-44487 (HTTP/2 Rapid Reset) with multiple attack patterns, granular configuration, and monitoring for…
 0xcyp1337/cve-2026-57811
Exploits CVE-2026-57811, an unauthenticated RCE in Realtyna Organic IDX + WPL Real Estate WordPress plugin, enabling shell upload and command…
 burakacar6/cve-2023-42793-teamcity-unauthenticated-rce
A PoC and automated version detection/exploit tool for JetBrains TeamCity Authentication Bypass & RCE (CVE-2023-42793).
 0xcyp1337/cve-2026-63077
Exploit for CVE-2026-63077, an unauthenticated RCE in JetBrains TeamCity via deserialization. Supports mass scanning, multi-threading, and…
 bhanunamikaze/activemq-cve-2023-46604
Non-destructive validator for Apache ActiveMQ CVE-2023-46604. Sends crafted OpenWire packets, uses HTTP callback server to confirm RCE or XML…
 ethicalgrey/phpbb-cve-2026-48611
Automated PoC for CVE-2026-48611 — phpBB OAuth login_link authentication bypass
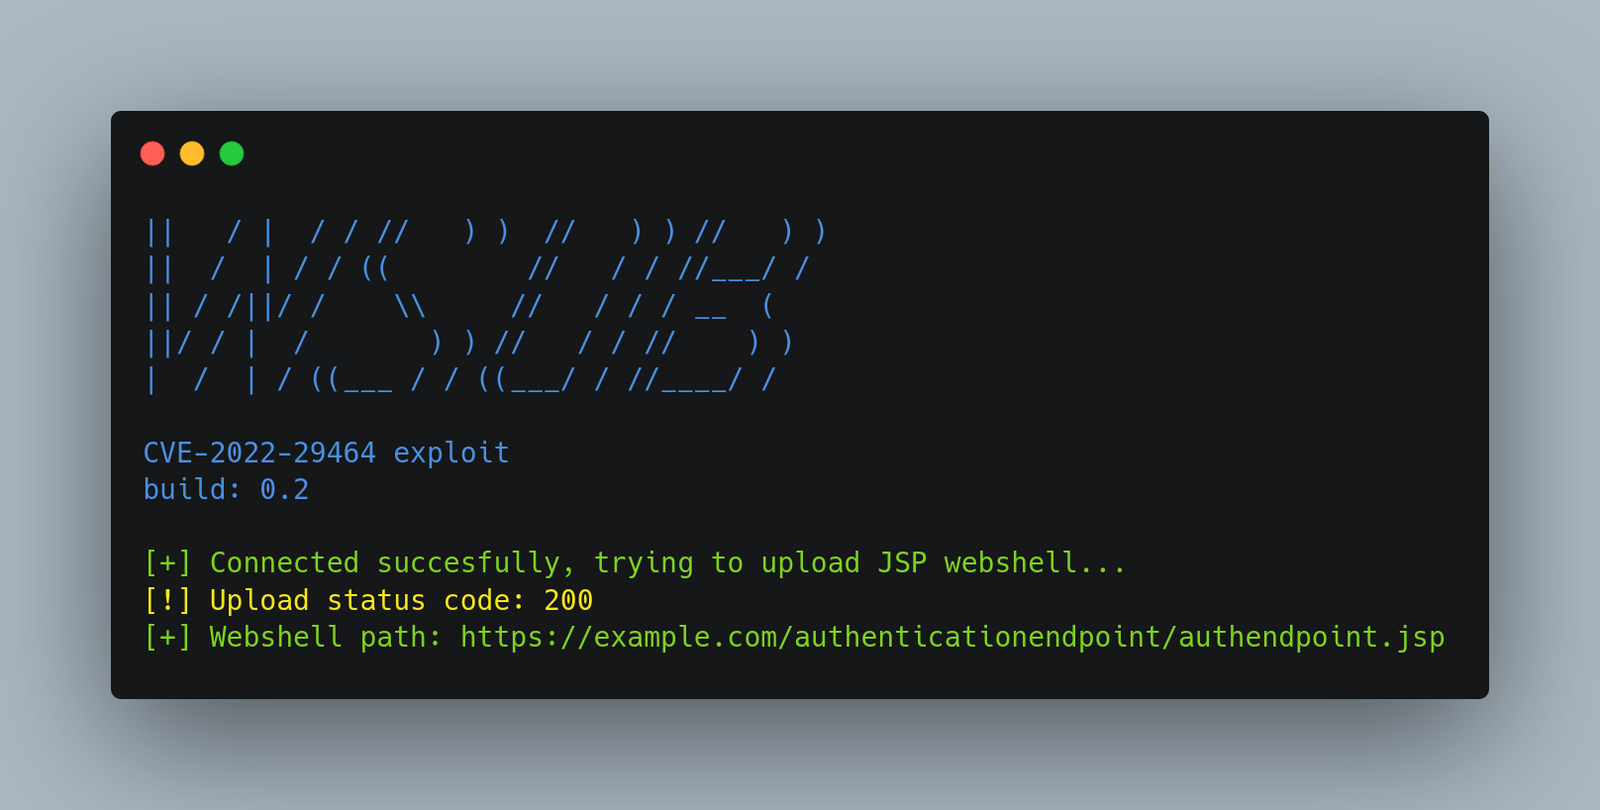 dsssssssm/wsob
Python exploit tool for CVE-2022-29464, enabling unrestricted file upload and remote code execution on vulnerable WSO2 products via directory…
 polosss/by-poloss..-..cve-2026-18080
Exploit for CVE-2026-18080, an unauthenticated arbitrary file upload leading to RCE in ERP Complete HR, Accounting & CRM Suite. Includes Python and…
 d-maggipinto/cve-2026-72898-metabase-sqli
Detector + root-cause analysis for CVE-2026-72898 (Metabase unauthenticated SQLi via reset_password)
 noambouillet/cve-2023-4861-poc
Automated proof-of-concept for authenticated remote code execution in WordPress File Manager Pro (Filester) via arbitrary file upload, including…
 thekawix/cve-2026-41940
Generates detection artifacts to verify cPanel/WHM authentication bypass vulnerability (CVE-2026-41940) and tests targets for exposure.
 rudsarkar/cve-2026-42228
Proof-of-concept exploit for CVE-2026-42228, an unauthenticated chat execution hijacking vulnerability in n8n, with automated scanning and attack…
 maxprog-svg/cve-2026-68820_mass_exploit
Automated local privilege escalation exploit for Windows 10/11 targeting AFD.sys use-after-free to gain SYSTEM, with PPL bypass and EDR evasion for…
 efeanilarslan/cve-2026-42167-exploit
Python exploit for CVE-2026-42167 (ProFTPD mod_sql). Features automated file scanning and timing-based blind data exfiltration.