
nxc-vulnscan
 rvsh3ll/nxc-vulnscan
NetExec module: run every stock Windows vuln-check in one pass (check-only, no exploit)
defensive-toolsexploitationnetwork-security+5
rvsh3ll/nxc-vulnscanNetExec module: run every stock Windows vuln-check in one pass (check-only, no exploit)
 xsuperbug/payloads
Collection of PHP-based attack payloads for web exploitation and penetration testing scenarios.
 ryanpohlner/arcgis-web-shell
ArcGIS Enterprise geoprocessing service that publishes a Python toolbox for command execution.
 gmh5225/plex2shell
CVE-2026-96652 CVE-2026-96654 CVE-2026-96655 CVE-2026-96656
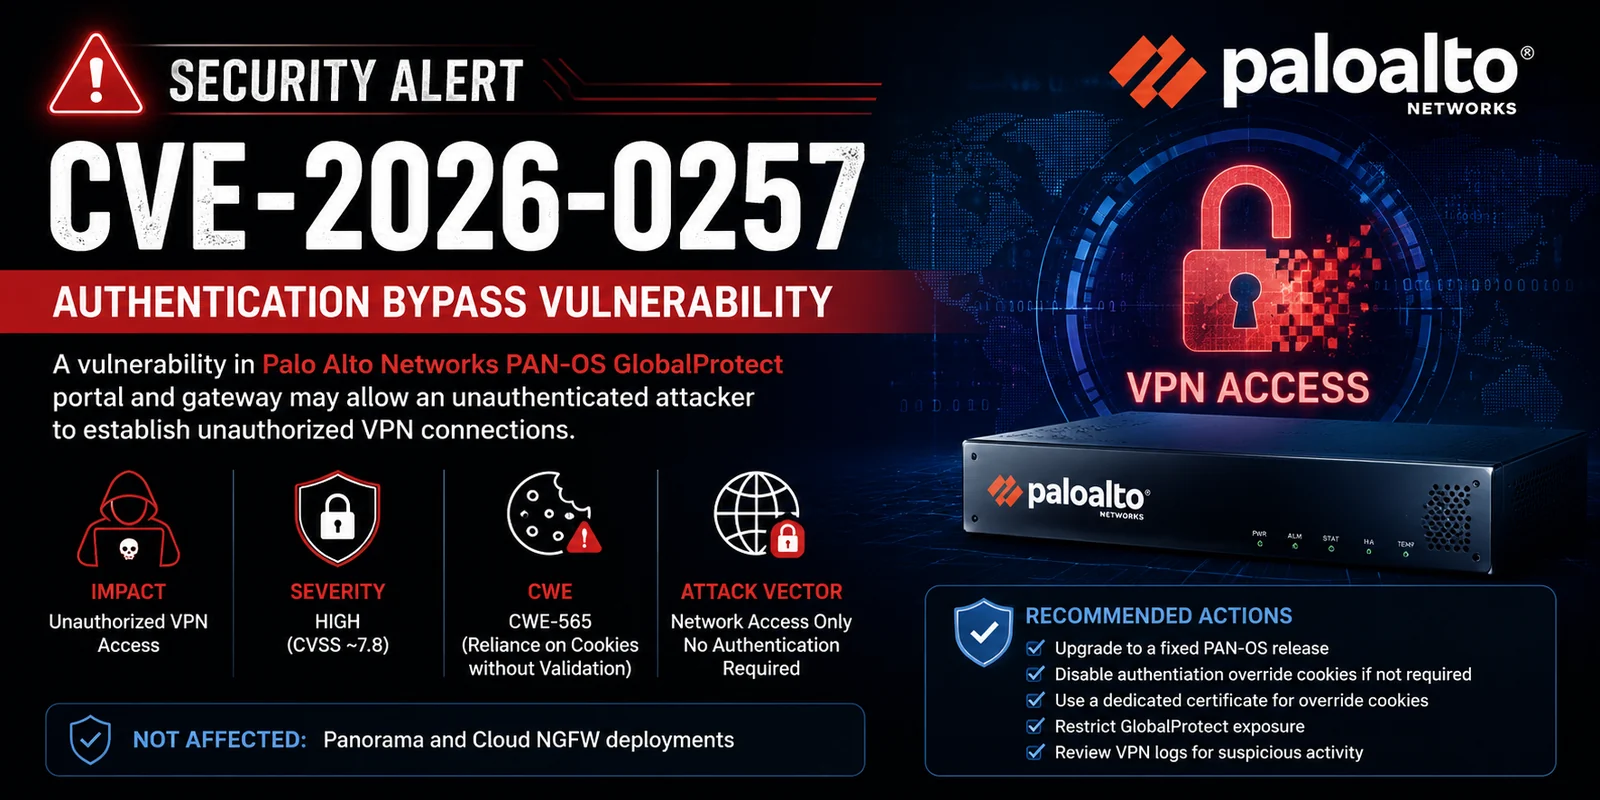 0xredash/cve-2026-0257
Python exploit for CVE-2026-0257 that forges GlobalProtect authentication override cookies to bypass PAN-OS portal and gateway authentication and…
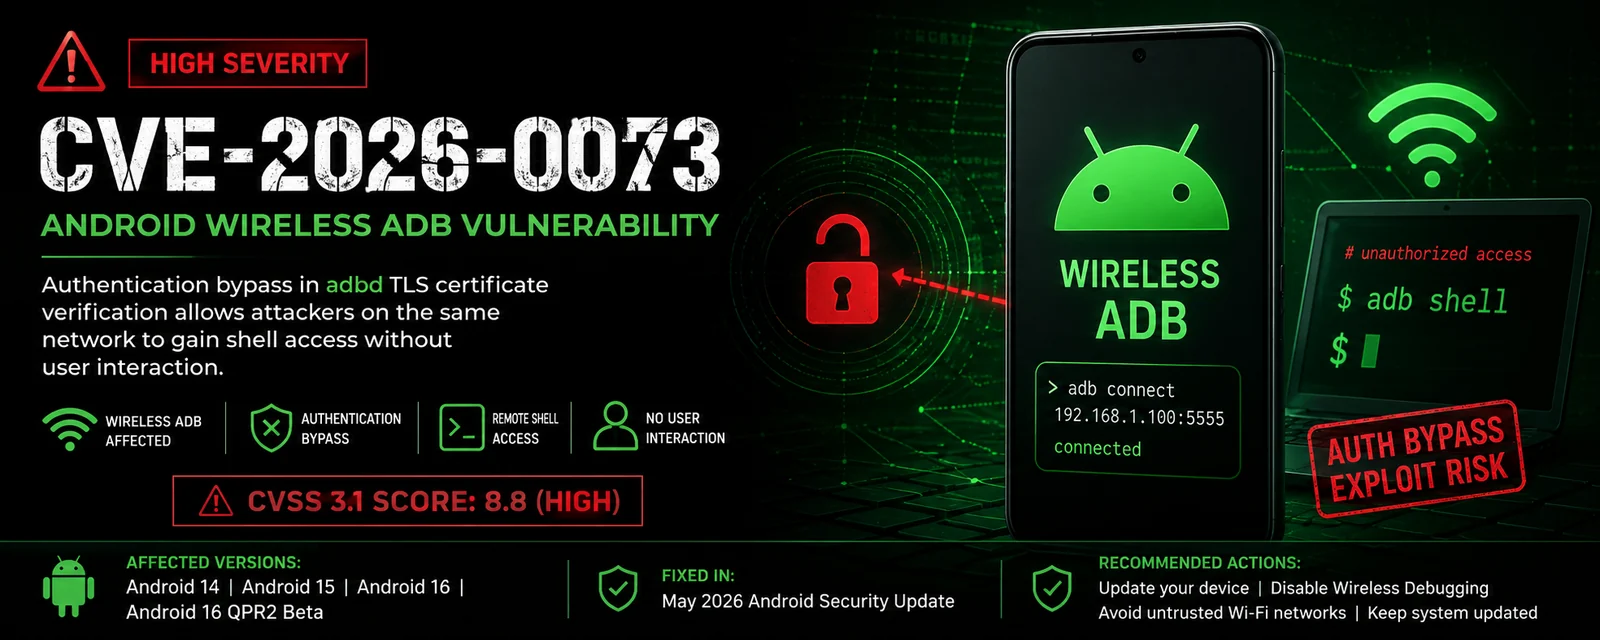 0xredash/cve-2026-0073
C++ proof-of-concept checker and exploit for CVE-2026-0073, an Android Wireless ADB authentication bypass allowing unauthenticated remote shell…
 faicalom/zte-mf904q-reverse-engineering
Open research documentation and source review for ZTE MF904Q bootloader, firmware extraction, and reverse engineering.
 markblah/smsofdeath
Android PoC app that sends a malformed 8-byte WAP Push PDU over SMS to crash com.android.phone remotely, silently dropping calls on the target…
 inforcqb-self/cve-2026-0013-exploit
Proof-of-concept exploit code for CVE-2026-0013, demonstrating the vulnerability for research and validation purposes.
 gameworkerkim/telegram-0-click-rce-security-vulnerability-analysis-report
I have submitted a report on the Telegram sticker vulnerability, SECURITY VULNERABILITY ANALYSIS REPORT Telegram 0-Click RCE vulnerability…
 thejesterrrr/cve-2026-19632
Proof-of-concept code and reproduction details for CVE-2026-19632, demonstrating the vulnerability's trigger conditions and impact.
 0xgh057r3c0n/php2shell
One-click exploit PoC for CVE-2026-109618 and CVE-2026-109619 against vulnerable PHP + Apache mod_php (prefork) targets.
 i014n/pngloader
Hides arbitrary payloads in PNG images using nibble-to-ASCII encoding and Fibonacci LSB steganography, with a C++ loader that extracts and executes…
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 xqi1337/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
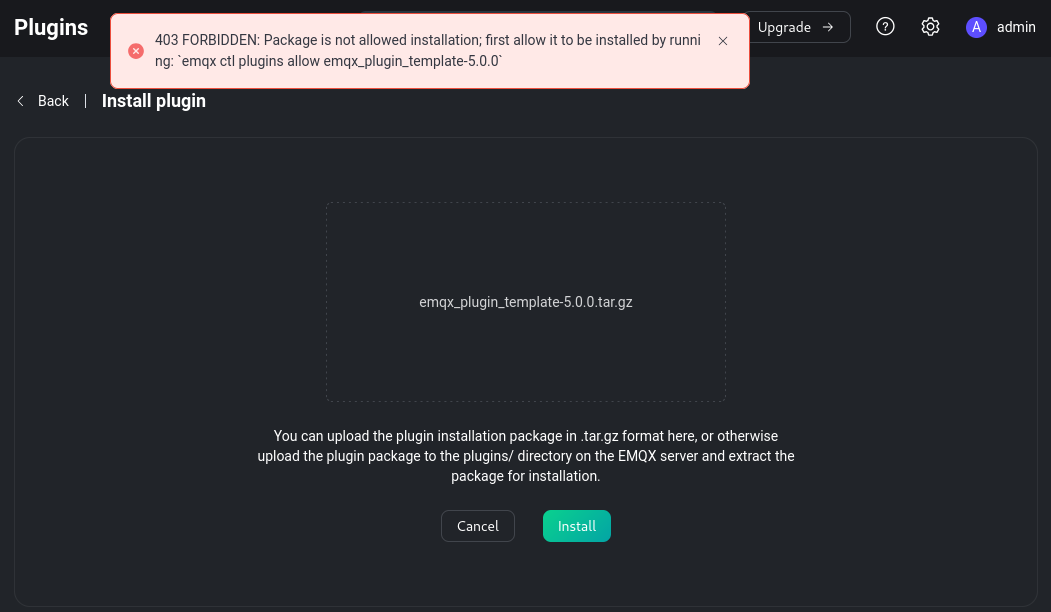 ricardojoserf/emqx-rce
EMQX Dashboard Malicious Plugin leading to RCE
 lotus6/confluencememshell
Confluence CVE 2021,2022,2023 利用工具,支持命令执行,哥斯拉,冰蝎 内存马注入
 csenox/gitlab-exiftool-rce
Python exploit achieving remote code execution on GitLab versions before 13.10.3 by abusing ExifTool DjVu parsing through GitLab Workhorse image…