
CVE-2026-56096
 yairhinkis/cve-2026-56096
Proof of concept and technical write-up for CVE-2026-56096, a blind Solr query injection in TYPO3 EXT:solr enabling unauthenticated field enumeration…
exploitationinformation-gatheringpapers-research+3
yairhinkis/cve-2026-56096Proof of concept and technical write-up for CVE-2026-56096, a blind Solr query injection in TYPO3 EXT:solr enabling unauthenticated field enumeration…
 yahiahamza/cve-2026-25099
Python exploit for Bludit CMS API unrestricted file upload leading to remote code execution, providing command execution and interactive shell for…
 ll104567/cve-2023-5966
Proof-of-concept exploit for CVE-2023-5966, an arbitrary file upload vulnerability in EspoCRM 2.7.4 and earlier, enabling remote code execution via a…
 ilhomjonr/cve-2026-70376
Advisory and Python PoC for Pluck CMS CSRF: fail-open Referer check plus double-extension upload enables webshell deployment and remote code…
 r2qa/cve-2026-17544
Exploit for CVE-2026-17544: PHP bcmath OOB write converted into memory-only RCE, bypassing disable_functions and open_basedir with a runtime…
 iltosec/chyrp-lite-rce-poc
CVE-2026-53767 + CVE-2026-53768 - Authenticated RCE in Chyrp Lite ≤ 2026.01 via uploads_path blocklist bypass and missing extension validation
 murrez/cve-2026-65891
CVE-2026-65891 PoC — Joomla Content Editor file rename vulnerability (auth required, fixed in JCE 2.20.2)
 chrissec2014/amasty-chekout-poc-rce
my poc for CVE-2026-53787
 toanln-cov/cve-2026-66492
The Joomla extension PhocaCommander is vulnerable to Path Traversal in the file upload action - CVSS 6.1
 toanln-cov/cve-2026-66493
The Joomla extension PhocaCommander is vulnerable to Path Traversal in delete, copy, move actions - CVSS 6.4
 toanln-cov/cve-2026-66491
The Joomla extension PhocaCommander is vulnerable to Path Traversal in the getSource function - CVSS 8.2
 t0xodile/crlf-powered-desync-scanner
Burp extension scanner for CRLF injection and HTTP desync attacks, using mutated probes, WAF false-positive checks, and optional…
 hunt-benito/e-is-for-exploit-cve-2026-17543-php-pgsql-sql-injection-backslash-breakout
PoC exploit for CVE-2026-17543: SQL injection in PHP ext/pgsql via backslash breakout, with data exfiltration and admin privilege-escalation payloads…
 george0papasotiriou/cve-2026-4040-race-condition-in-file-upload-leading-to-rce
Reproduces CVE-2026-4040: Flask upload server with TOCTOU race condition and exploit script demonstrating arbitrary remote code execution.
 synacktiv/extloader
A chromium extension exploitation toolkit
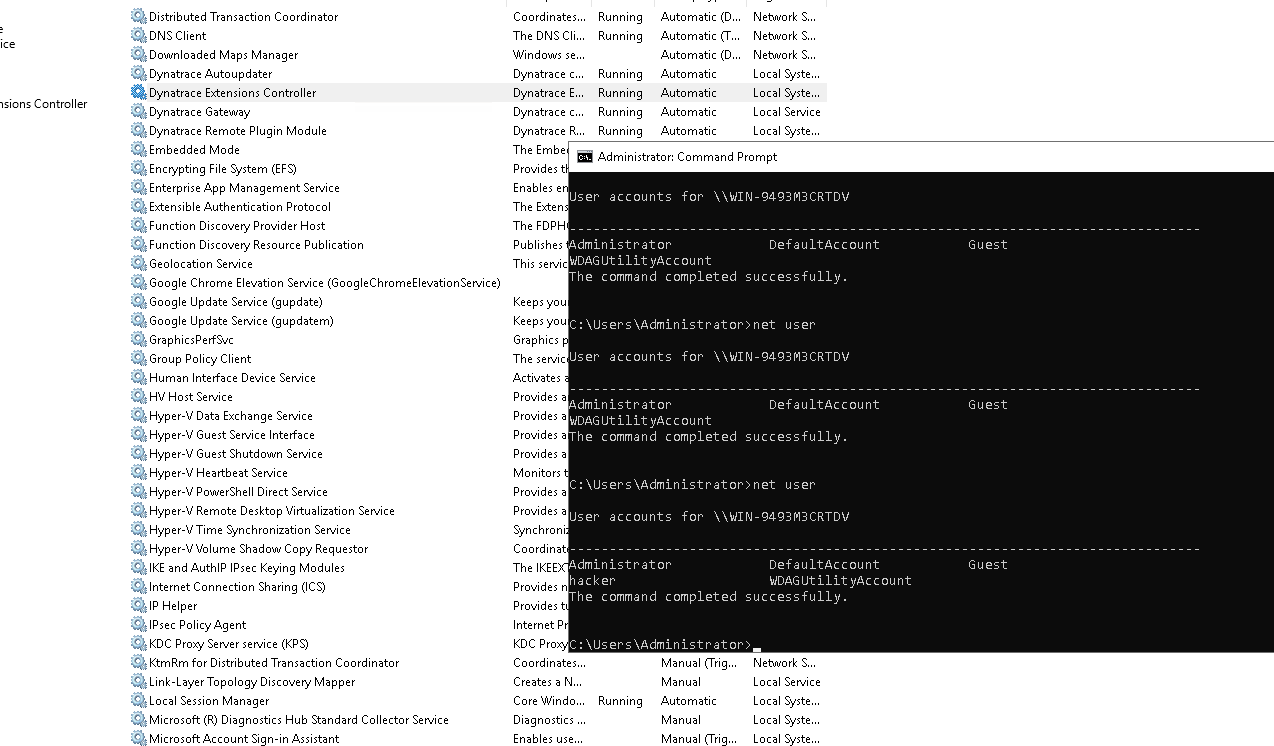 pentastic-be/cve-2025-61304
OS command injection vulnerability in Dynatrace ActiveGate ping extension up to 1.016 via crafted ip address
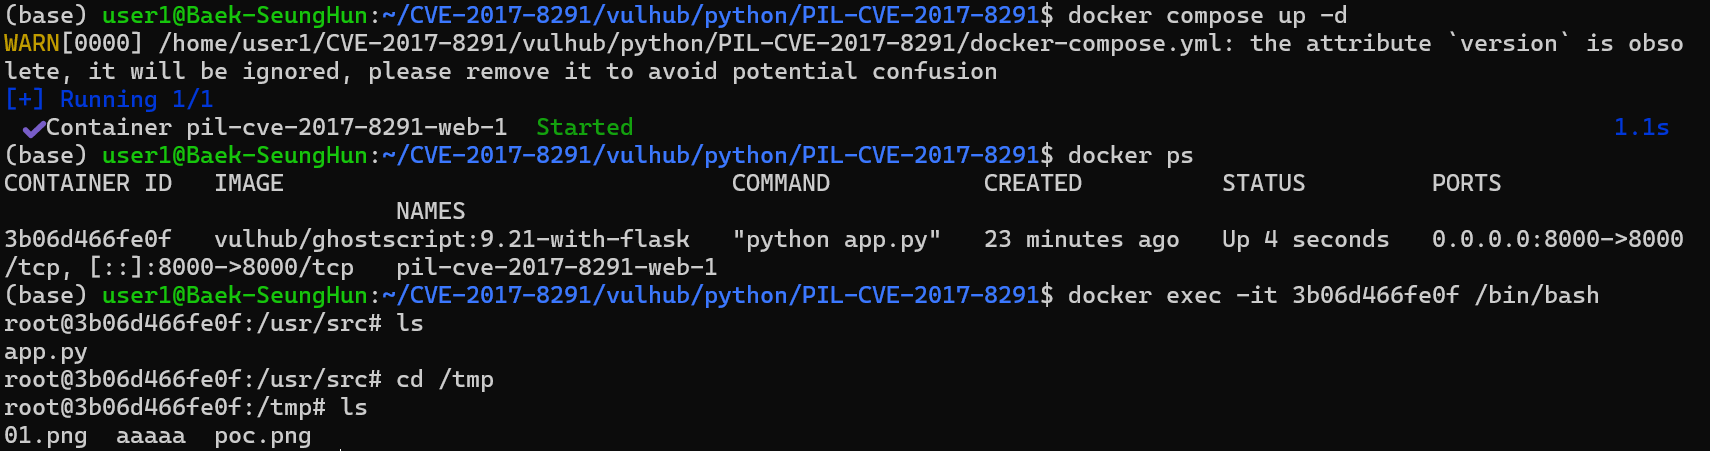 shun1403/pil-cve-2017-8291-study
Educational lab demonstrating CVE-2017-8291 (PIL/GhostScript RCE) via crafted EPS file upload with PNG extension, including Docker setup and PoC…
 xxconi/cve-2026-46275
Python exploit for CVE-2026-46725, achieving unauthenticated remote code execution in TYPO3 ceselector extension via PHP object injection and Monolog…