
AirStrike
 mahmoud-sadder/airstrike
AirStrike is an advanced wireless security assessment framework designed to simplify and enhance Wi-Fi penetration testing through an integrated,…
exploitationnetwork-securitypenetration-testing+3
5
mahmoud-sadder/airstrikeAirStrike is an advanced wireless security assessment framework designed to simplify and enhance Wi-Fi penetration testing through an integrated,…
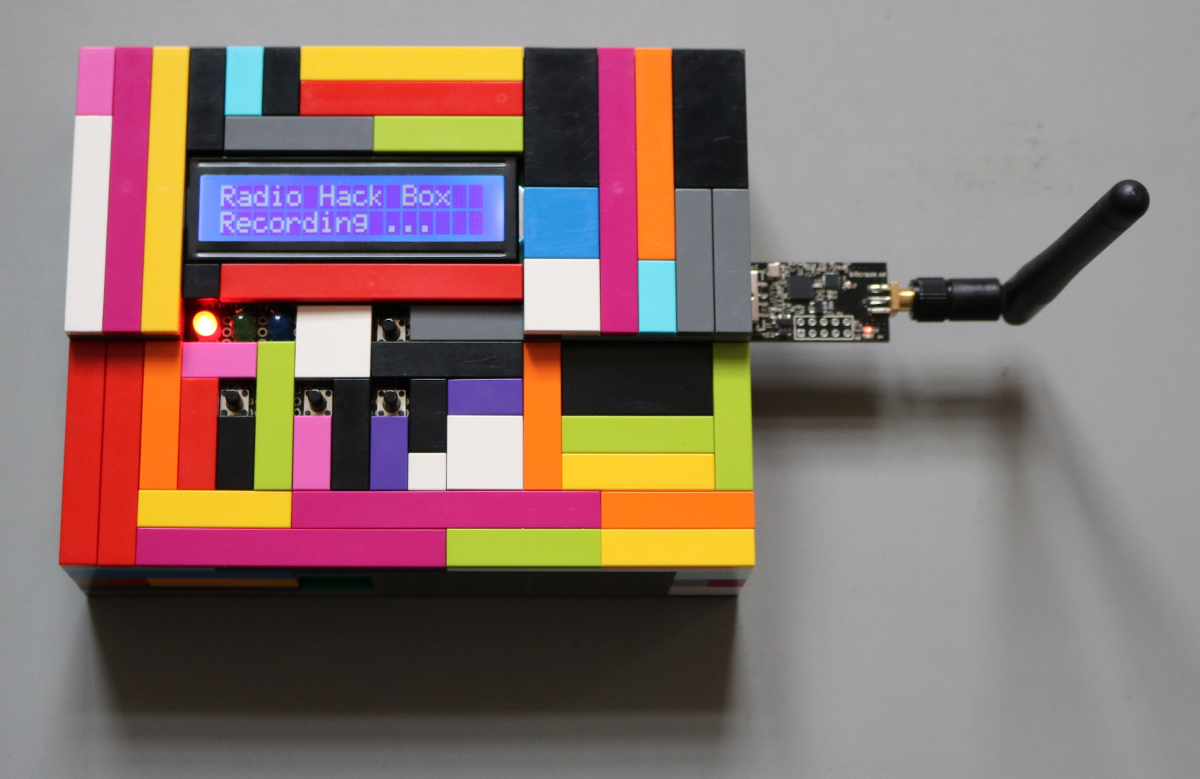 syss-research/radio-hackbox
PoC tool to demonstrate vulnerabilities in wireless input devices
 wh02m1/cve-2026-78306
Proof-of-concept exploiting DJI drone Bluetooth DUML command injection, sending unauthenticated commands to read credentials, alter Wi-Fi config, and…
 vanhoefm/fragattacks
Automated vulnerability tester for Wi-Fi clients and access points, detecting FragAttacks fragmentation/aggregation flaws through frame injection,…
 efchatz/wpaxfuzz
A full-featured open-source Wi-Fi fuzzer
 xswxm/nrf24-injection
A tool set for sniffing devices and launching attacks with Crazyradio
 icsec/airpwn-ng
Packet injection for wifi; simplified.
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
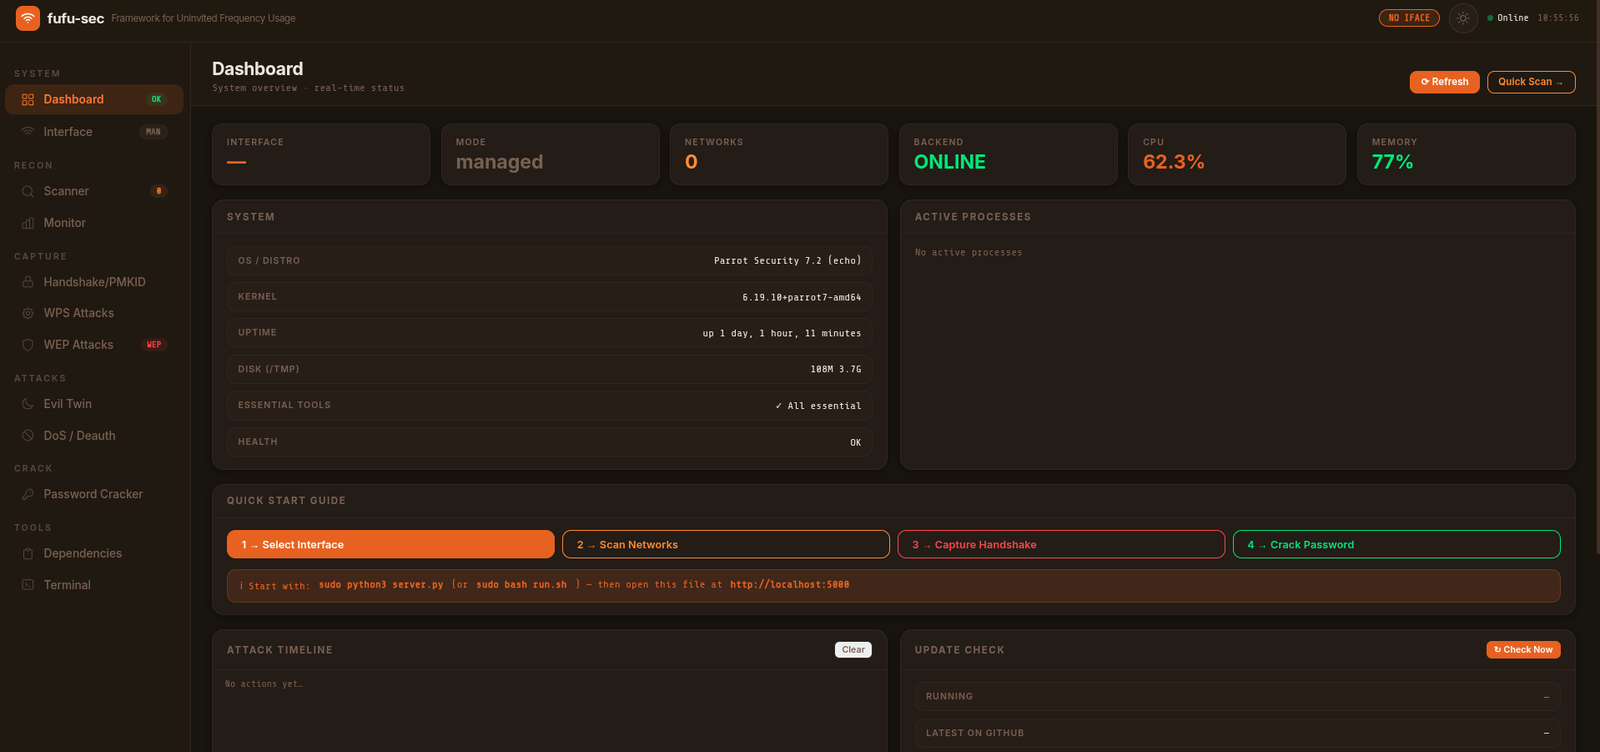 kyllr-qwen/fufu-sec
Framework for Uninvited Frequency Usage
 efchatz/easy-exploits
Curated collection of proof-of-concept exploits for 16 CVEs targeting web applications (ASUS, D-Link, Netgear, TP-Link, Xiaomi) and Wi-Fi WPA3-SAE,…
 risinek/esp32-wifi-penetration-tool
Exploring possibilities of ESP32 platform to attack on nearby Wi-Fi networks.
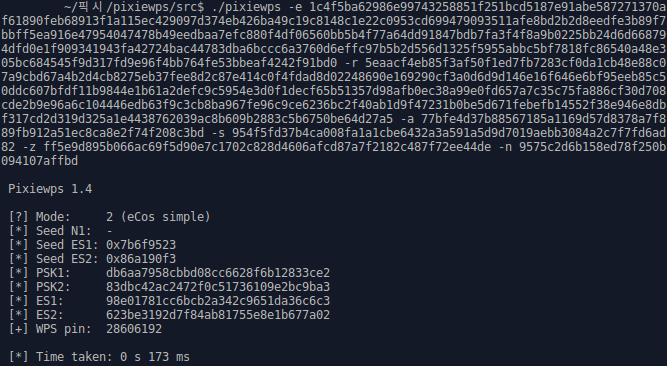 wiire-a/pixiewps
An offline Wi-Fi Protected Setup brute-force utility
 satheesh575555/external_wpa_supplicant_8_aosp10_r33_cve-2021-0516
Proof-of-concept exploit for CVE-2021-0516 in wpa_supplicant on AOSP 10, demonstrating a buffer overflow vulnerability in Wi-Fi authentication.
 ymsniper/kto
Automated Wi-Fi deauthentication tool that continuously scans for clients on a target SSID and kicks non-whitelisted devices. Features whitelist…
 pinecone-wifi/pinecone
Modular WLAN auditing framework for red teams with deauthentication, rogue AP, and WPA handshake capture modules. Features a Metasploit-like CLI for…
 hunt-benito/mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce
Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…
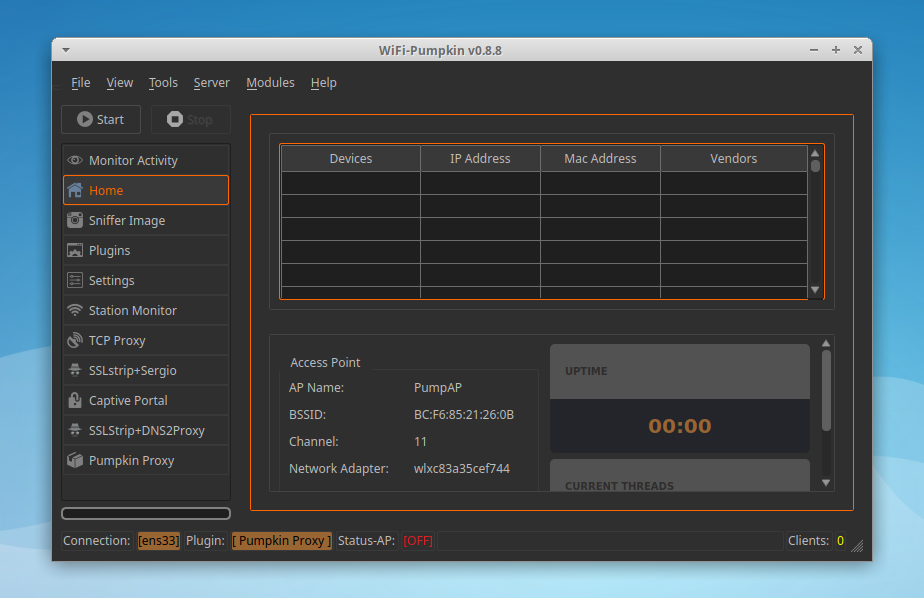 p0cl4bs/wifi-pumpkin-deprecated
DEPRECATED, wifipumpkin3 -> https://github.com/P0cL4bs/wifipumpkin3
 martinpsdev/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…