
wtf
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
binary-analysisdynamic-analysis-sandboxingexploitation+2
1.8k
0vercl0k/wtfDistributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 joshuaprovoste/deserializer
AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 six2dez/pentest-book
Curated penetration testing wiki with daily-updated techniques, scripts, and checklists for reconnaissance, web, cloud, mobile, and…
 kac89/cve-2024-5961
Proof-of-concept exploit for reflected XSS vulnerability in 2ClickPortal versions 7.2.31 through 7.6.4, with a search parameter injection payload.
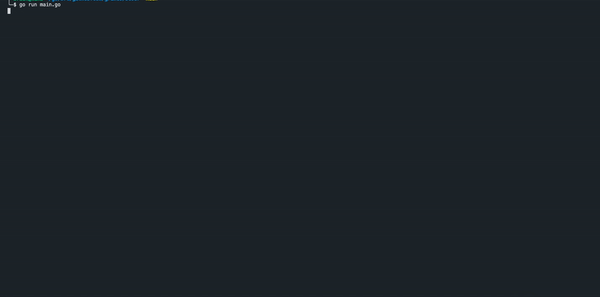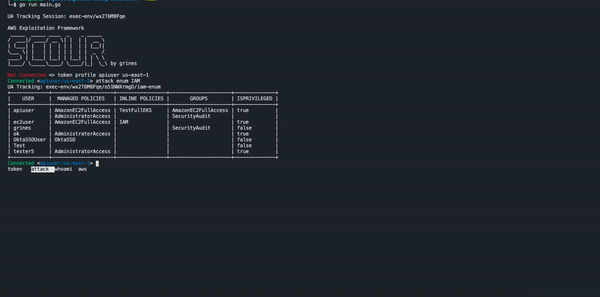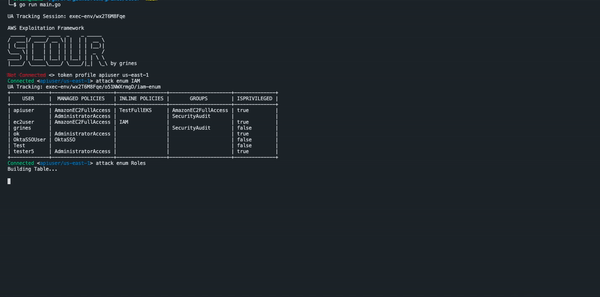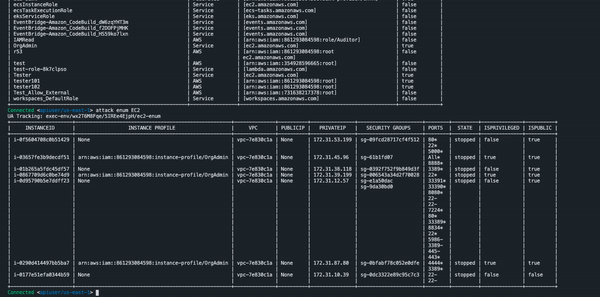 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 h3x0v3rl0rd/cve-2019-5736
Go-based exploit for CVE-2019-5736 (Runc container escape) with a customizable reverse shell payload, designed for penetration testing and red team…
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
 0dinox/cve-2024-415770-ssrf-rce
Automated exploit for CVE-2024-415770: leverages SSRF to achieve RCE, registers an agent on the teamserver, opens a socket, and injects an SSH key…
 nu11secur1ty/python
Curated collection of Python scripts and tutorials for penetration testing, web security, and exploitation techniques, designed for security…
 joshuavanderpoll/cve-2021-3129
Laravel RCE Exploit PoC - CVE-2021-3129 (user-friendly with automatic log path detection)
 yuvvi01/cve-2024-3400
Exploit script for CVE-2024-3400, a command injection in PAN-OS GlobalProtect, allowing unauthenticated remote code execution with root privileges.…
 xtafnull/cms-made-simple-sqli-python3
CMS Made Simple < 2.2.10 - SQL Injection (rewritten for python3), CVE-2019-905
 center-for-threat-informed-defense/adversary_emulation_library
An open library of adversary emulation plans designed to empower organizations to test their defenses based on real-world TTPs.
 sobri3195/-pegasus-suite
A comprehensive security toolkit with 1000+ penetration testing and security assessment tools.
 g0rx/drupal-sa-core-2019-003
Proof-of-concept exploit for CVE-2019-6340 targeting Drupal's RESTful web services module, with curl-based RCE payload and detailed reproduction…
 sam00/poc-cve-2026-32621-apollo-federation-xss-vulnerability
PoC exploit for CVE-2026-32621 demonstrating Apollo Federation deepMerge prototype pollution via crafted GraphQL aliases, with patched-version tests.
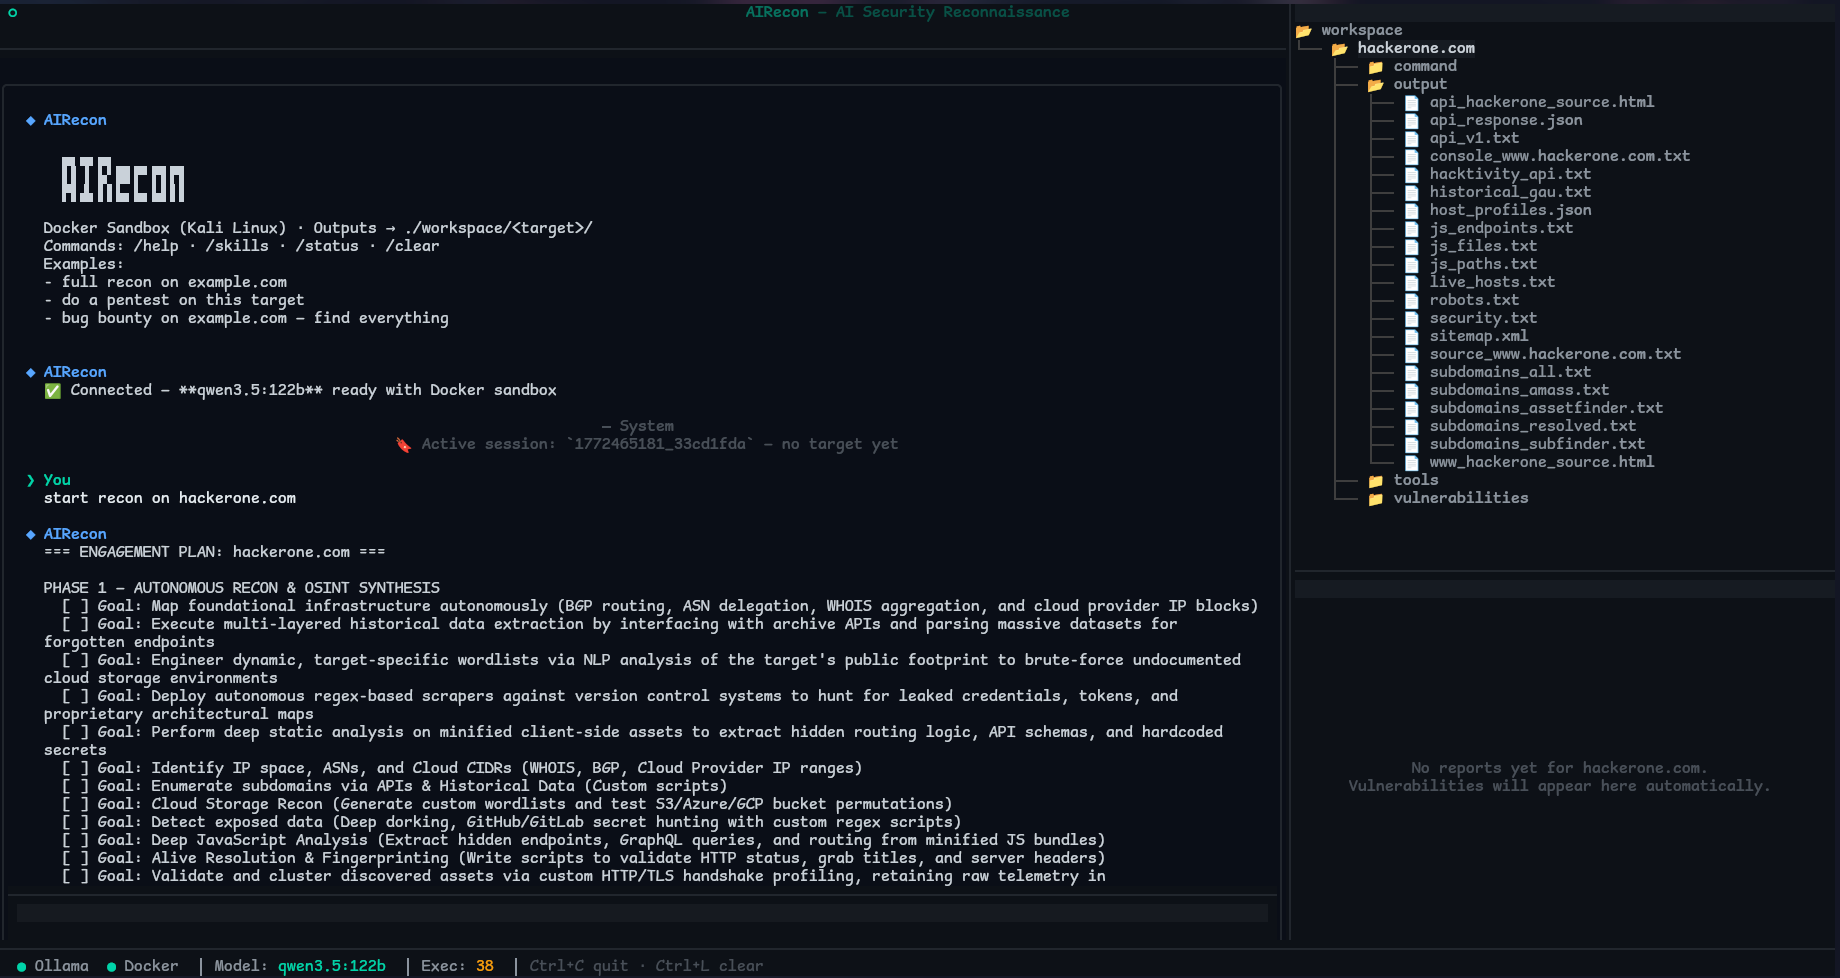 pikpikcu/airecon
AIRecon is an autonomous cybersecurity agent that combines a self-hosted Large Language Model (Ollama) with a Kali Linux Docker sandbox and a Textual…