

w3af
 andresriancho/w3af
Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
exploitationpenetration-testingvulnerability-scanners+3
4.9k
andresriancho/w3afOpen-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 itzexploit/cve-2017-8056
Python-based exploit for CVE-2017-8056 targeting XML-RPC denial-of-service vulnerability in web applications.
 skyllpro/cve-2021-44026-poc
Bug Chain XSS (CVE-2020-35730 and CVE-2023-43770) to SQLi (CVE-2021-44026)
 happynote3966/cve-2018-7600
Exploit for CVE-2018-7600, a critical remote code execution vulnerability in Drupal core. Enables automated exploitation of unpatched Drupal sites…
 karthikuj/cve-2022-31101
Exploit for PrestaShop bockwishlist module 2.1.0 SQLi (CVE-2022-31101)
 cduram/chirp-codeexecution_via_malicious_imagefile
Proof-of-concept exploit for arbitrary code execution through eval() injection in a ham radio programming application, including malicious .itm/.img…
 iczc/ethermint-cve-2021-25837
Proof-of-concept exploit for CVE-2021-25837 targeting Ethermint, demonstrating a critical vulnerability in Ethereum-compatible blockchain nodes.
 hacip/cve-2023-33405
Proof-of-concept exploit for an open redirect vulnerability (CVE-2023-33405) in BlogEngine.NET CMS versions 3.3.8.0 and earlier, demonstrating…
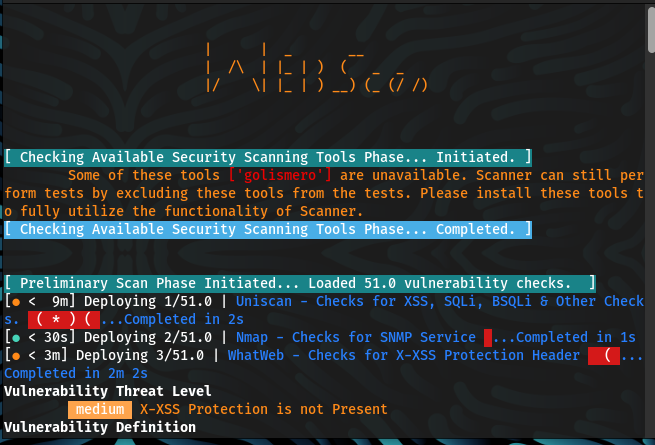 malwareman007/scanner-and-patcher
A Web Vulnerability Scanner and Patcher
 themehackers/cve-2025-29972
CVE-2025-29927 is a critical security vulnerability affecting Next.js, a popular React framework for building full-stack web applications. This flaw…
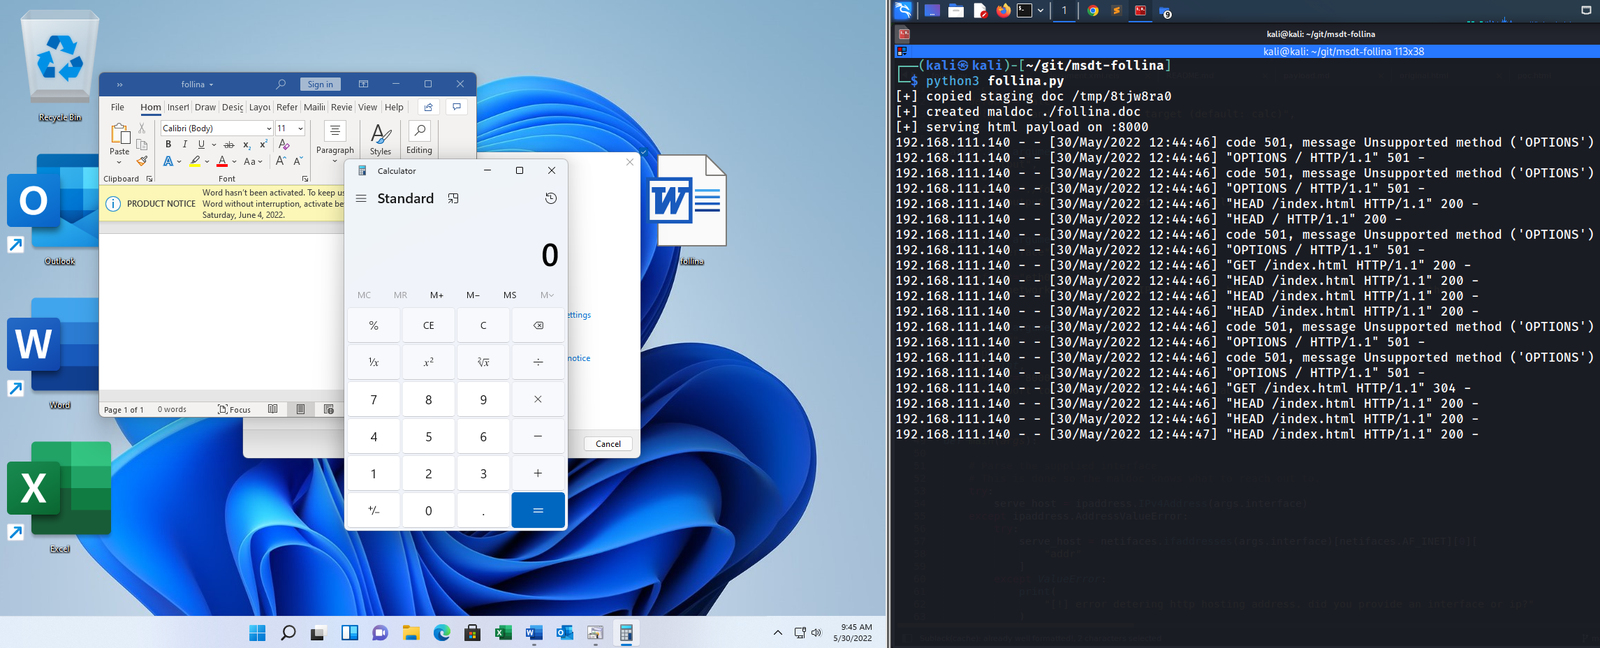 johnhammond/msdt-follina
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
 flaviupopescu/cve-2022-28601
A Two-Factor Authentication (2FA) bypass vulnerability in "Simple 2FA Plugin for Moodle" by LMS Doctor
 0xm4hm0ud/cve-2022-24637
Unauthenticated RCE in Open Web Analytics version <1.7.4
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 chairat095/cve-2022-44268_by_kyokito
Proof-of-concept exploit for CVE-2022-44268, an arbitrary file read vulnerability in ImageMagick, enabling local file disclosure via crafted PNG…
 destr4ct/cve-2022-0739
Proof-of-Concept exploit (SQLI BookingPress before 1.0.11)