
CVE-2023-42326
 bl4ckarch/cve-2023-42326
This is a simple POC to for show the pfsense 2.7 Command injection Vulnerability ( CVE-2023-42326)
command-and-controlexploitationpayload-generation+3
bl4ckarch/cve-2023-42326This is a simple POC to for show the pfsense 2.7 Command injection Vulnerability ( CVE-2023-42326)
 flaviupopescu/cve-2022-28601
A Two-Factor Authentication (2FA) bypass vulnerability in "Simple 2FA Plugin for Moodle" by LMS Doctor
 mrcl0wnlab/simplesapachepathtraversal
Tool check: CVE-2021-41773, CVE-2021-42013, CVE-2020-17519
 menevarad007/cve-2026-37749
Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…
 x3rx3ssec/dvr_sploit
Simple python3 script to automate CVE-2018-9995
 x3rx3ssec/cve-2022-0169
CVE-2022-0169 - WordPress Photo Gallery SQLi PoC
 smokeintheshell/cve-2018-1000861
CVE-2018-1000861 Exploit
 erikwynter/cve-2023-22515-scan
Scanner for CVE-2023-22515 - Broken Access Control Vulnerability in Atlassian Confluence
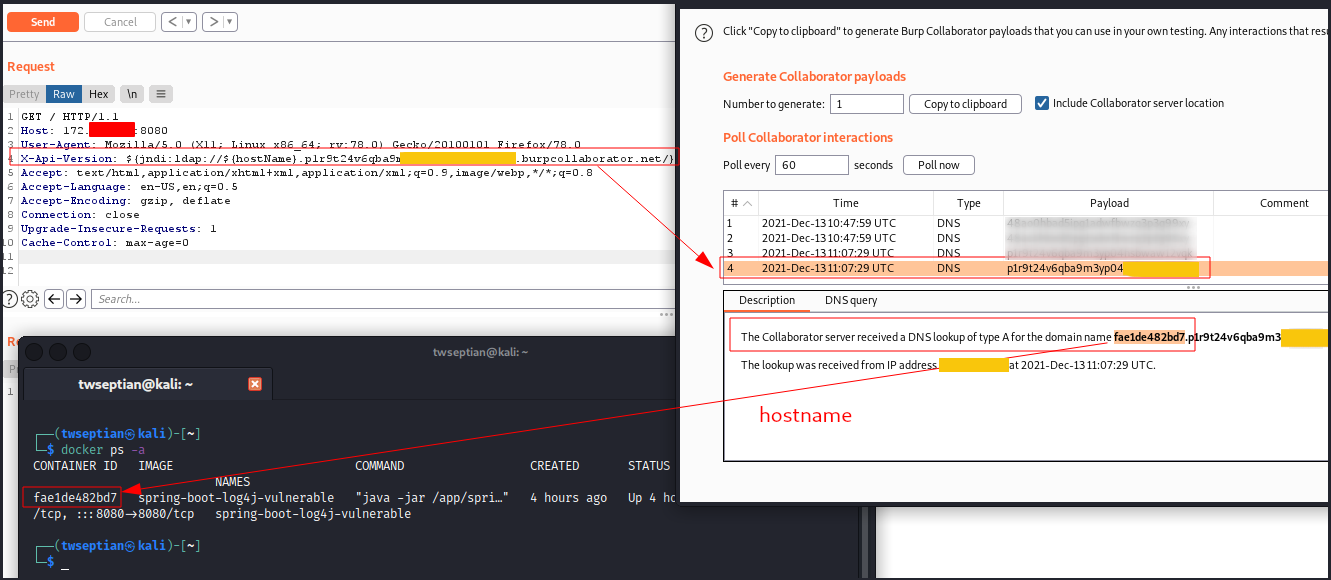 twseptian/spring-boot-log4j-cve-2021-44228-docker-lab
Spring Boot Log4j - CVE-2021-44228 Docker Lab
 h3x0v3rl0rd/cve-2019-9053
Python exploit for CVE-2019-9053 targeting a SQL injection vulnerability in CMS Made Simple. Automates time-based blind SQLi to extract admin…
 jyothsna-git007/cms-made-simple-2.2.10---sql-injection
Google Dork-based scanner for detecting CVE-2019-9053 SQL injection in CMS Made Simple < 2.2.10. Designed for security auditing and patch…
 kaizoku73/cve-2019-9053
CMS Made Simple ≤ 2.2.9 SQL Injection Vulnerability CVE-2019-9053 is a vulnerability found in CMS Made Simple (CMSMS) versions up to 2.2.9, where the…
 xtafnull/cms-made-simple-sqli-python3
CMS Made Simple < 2.2.10 - SQL Injection (rewritten for python3), CVE-2019-905
 caybermods/cve-2026-22812-poc
Python tool to check and exploit CVE-2026-22812 in OpenCode, supporting command execution, file read, and multi-target scanning on ports 4095-4100.
 aaronm-sysdig/cve-2023-50164
Demonstrates detection of CVE-2023-50164 (Apache Struts RCE) with a simple Java app, intended for security testing and educational purposes.
 asal1n/cve-2025-24813
simple exp for CVE-2025-24813
 srvaccount/cve-2021-26855-poc
PoC exploit code for CVE-2021-26855
 amirzargham/cve-2023-0099-exploit
simple urls < 115 - Reflected XSS