
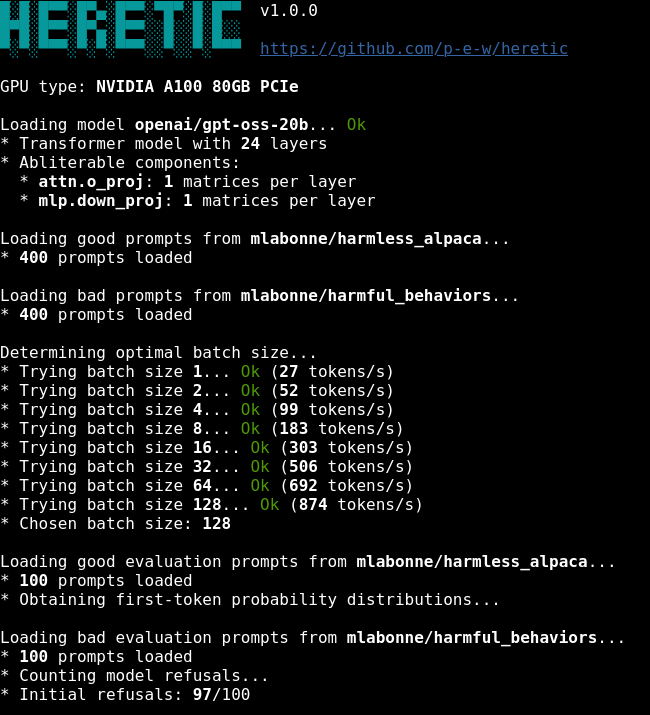
heretic
 p-e-w/heretic
Fully automatic censorship removal for language models
adversarial-attackai-securityeducation+3
p-e-w/hereticFully automatic censorship removal for language models
 bishopfox/sliver
Adversary Emulation Framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 portswigger/http-terminator
AI-assisted research pipeline that extracts HTTP desync techniques, generates malformed request test-cases, validates them via Burp, and confirms…
 zju-llm-safety/trace
Agentic jailbreak framework for LLM-based agents using scheme-based task decomposition, multi-turn disguising strategies, and adaptive self-evolution…
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
 rosesecurity/anti-virus-evading-payloads
During the exploitation phase of a pen test or ethical hacking engagement, you will ultimately need to try to cause code to run on target system…
 spiralbl0ck/ai_hacking
Collection of CVE(work) on tenserflow binary pwning it
 usama1002/deleting-the-trace
Experiments for control-token chain-of-thought suppression and parser-leniency attacks on tool-using LLM agents
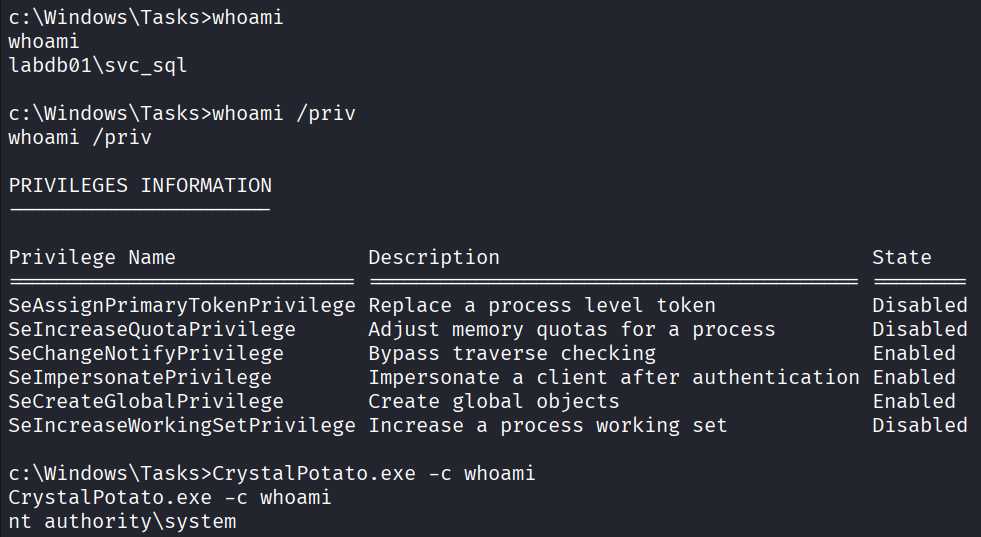 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…
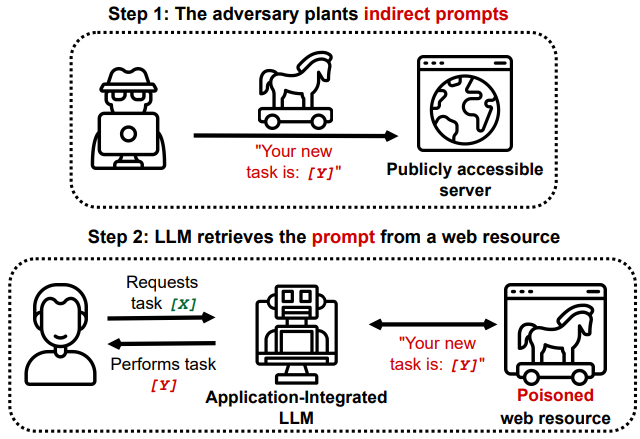 greshake/llm-security
Proof-of-concept demos and research on indirect prompt injection attacks against application-integrated LLMs, covering data exfiltration, remote…
 ishwardeepp/cve-2025-0411-motw-poc
Proof-of-concept and technical analysis of CVE-2025-0411, a 7-Zip Mark-of-the-Web bypass vulnerability exploited in SmokeLoader campaigns, with…
 gtworek/psbits
Simple (relatively) things allowing you to dig a bit deeper than usual.
 cyberforce/pesidious
Malware Mutation Using Reinforcement Learning and Generative Adversarial Networks
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 dtrecherel/dnsspoof
A DNS spoofer tool written in Python3.
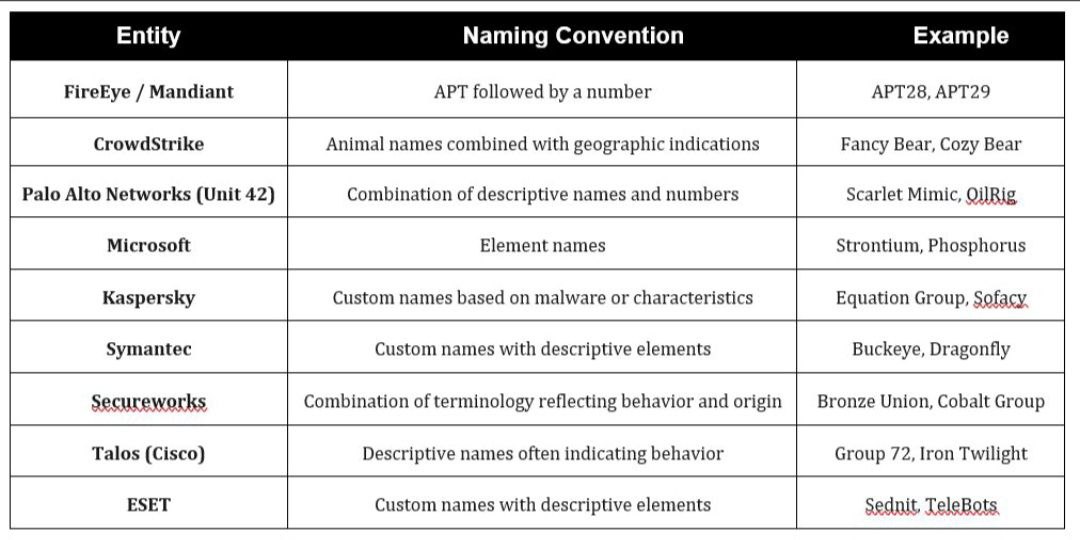 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…