

ghostlock-aak-apk
 oopnv70-lab/ghostlock-aak-apk
GhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
android-securitybinary-exploitationexploitation+5
8
oopnv70-lab/ghostlock-aak-apkGhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
 ggfuchsi-oss/spectrida-reverse_engineering_stack
Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…
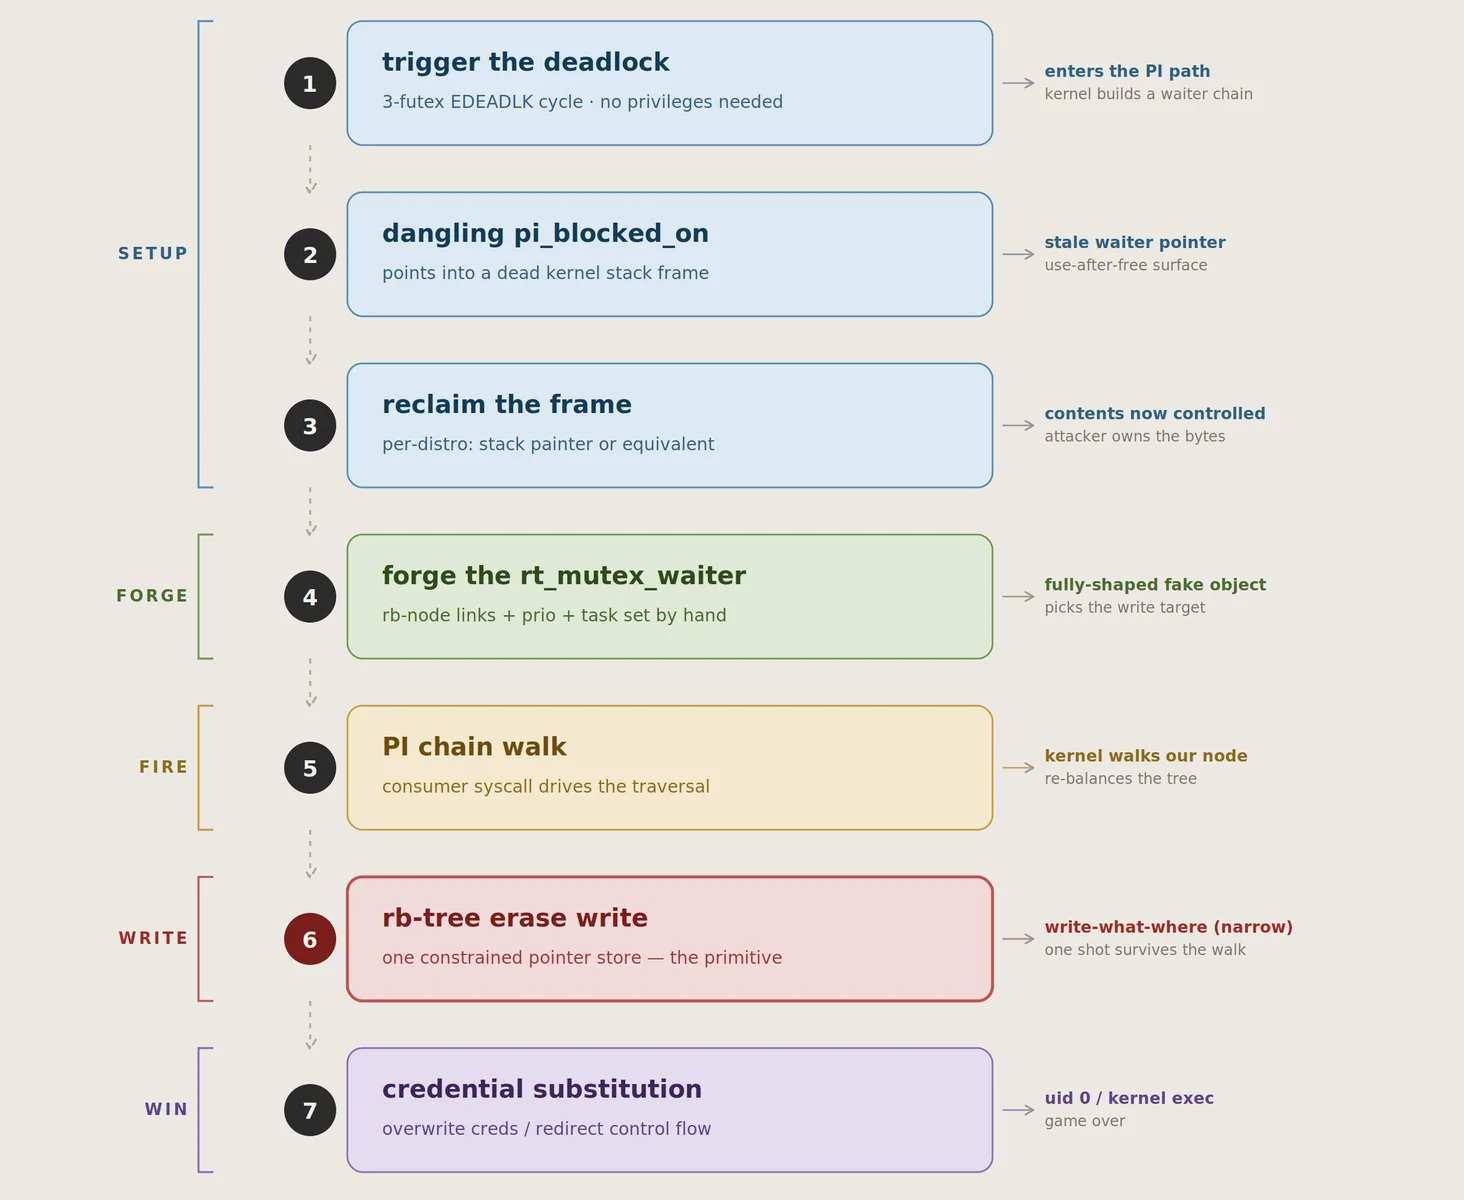 lkeld/cve-2026-43499-poc
Weaponized proof-of-concept for CVE-2026-43499 (GhostLock), a Linux kernel rtmutex bug enabling local privilege escalation. Includes per-distribution…
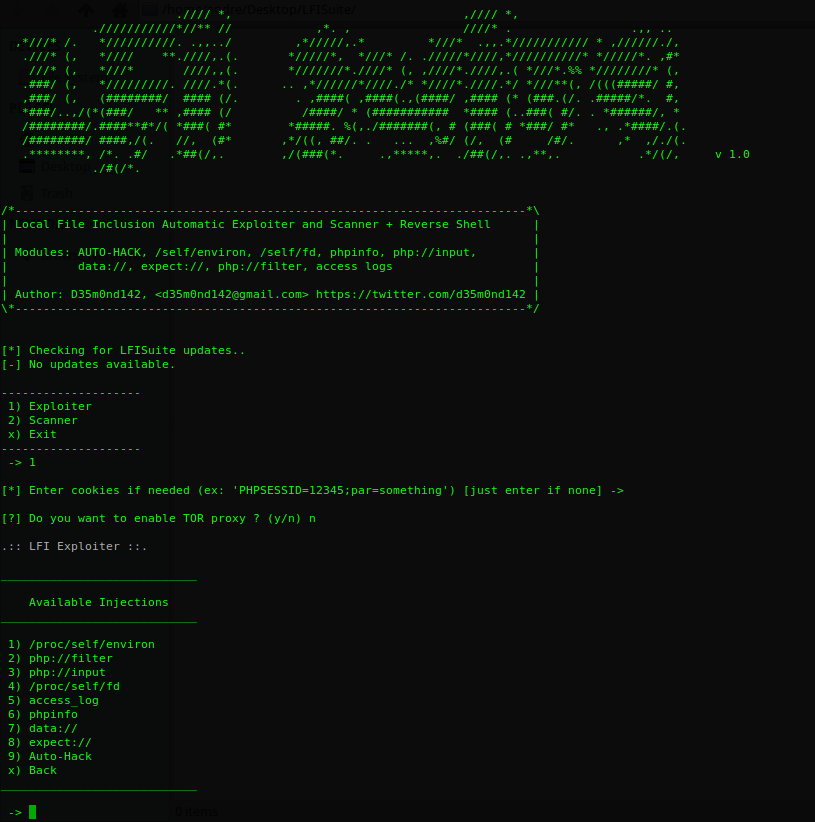 d35m0nd142/lfisuite
Totally Automatic LFI Exploiter (+ Reverse Shell) and Scanner
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 jm33-m0/cve-2021-3156
Go-based exploit for CVE-2021-3156, a sudo heap overflow vulnerability enabling local privilege escalation on Linux systems.
 yijiacloud/ghostlock-oppo-pckm00
CVE-2026-43499 GhostLock futex UAF LPE PoC for OPPO PCKM00 (SM6150) / Linux 4.14.180
 0xblackash/cve-2026-81000
Research repository for CVE-2026-81000 (TUNderflow), a Linux kernel TUN/TAP receive headroom integer underflow enabling local privilege escalation,…
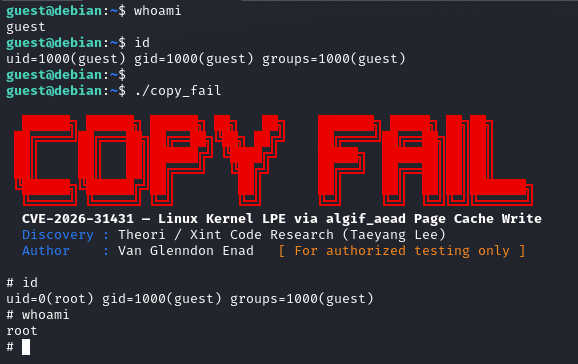 sl4ck0th/cve-2026-31431-poc
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG page cache write, achieving root on major…
 mishl-dev/cve_2026_31431
Exploit for CVE-2026-31431, a Linux kernel page-cache write primitive enabling local privilege escalation and container escape via AF_ALG and…
 0range1337/cve-2022-1015
PoC exploit for CVE-2022-1015, a Linux kernel netfilter use-after-free leading to local privilege escalation.
 soralis0912/cve-2026-43499-aristotle
Local privilege escalation exploit for Xiaomi XIG04 (Android 12) via CVE-2026-43499 kernel use-after-free. Data-only direct-root technique with MTE…
 00xcanelo/cve-2025-27591
🔥 Local Privilege Escalation Exploit for CVE-2025-27591 | Abuses world-writable log dir in Below to gain root via /etc/passwd injection
 whatswrongandwhy/cve-2015-1328
Proof-of-concept exploit for CVE-2015-1328, a Linux kernel privilege escalation vulnerability, demonstrating local privilege escalation.
 turtlearm/cve-2023-0179-poc
Exploit for CVE-2023-0179, a stack buffer overflow in the Linux nftables subsystem, enabling unprivileged local privilege escalation to root via…
 carradolly/cve-2015-8660
C-based exploit for CVE-2015-8660, a Linux kernel local privilege escalation vulnerability in the overlayfs filesystem.
 kuniyal08/dirty-frag-cve-2026-43284
A report on Dirty Frag, which is a Linux Local Privilege Escalation (LPE) vulnerability chain that allows an unprivileged user to gain root access
 mfloresdacunha/cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431 in Linux kernel's algif_aead, using splice to overwrite page cache and gain root. Includes a…