
CVE-2024-30956
 leocottret/cve-2024-30956
(DOM-based XSS) HTML Injection vulnerability in TOWeb v.12.05 and before allows an attacker to inject HTML/JS code via the _message.html component.
exploitationphishing-toolssocial-engineering+2
leocottret/cve-2024-30956(DOM-based XSS) HTML Injection vulnerability in TOWeb v.12.05 and before allows an attacker to inject HTML/JS code via the _message.html component.
 mohwahyudi/poc-cve-2026-64638-
PoC exploit chain for WordPress pre-auth XSS to RCE via DOM clobbering, REST JSONP/SOME, and plugin upload, with Docker lab verification and…
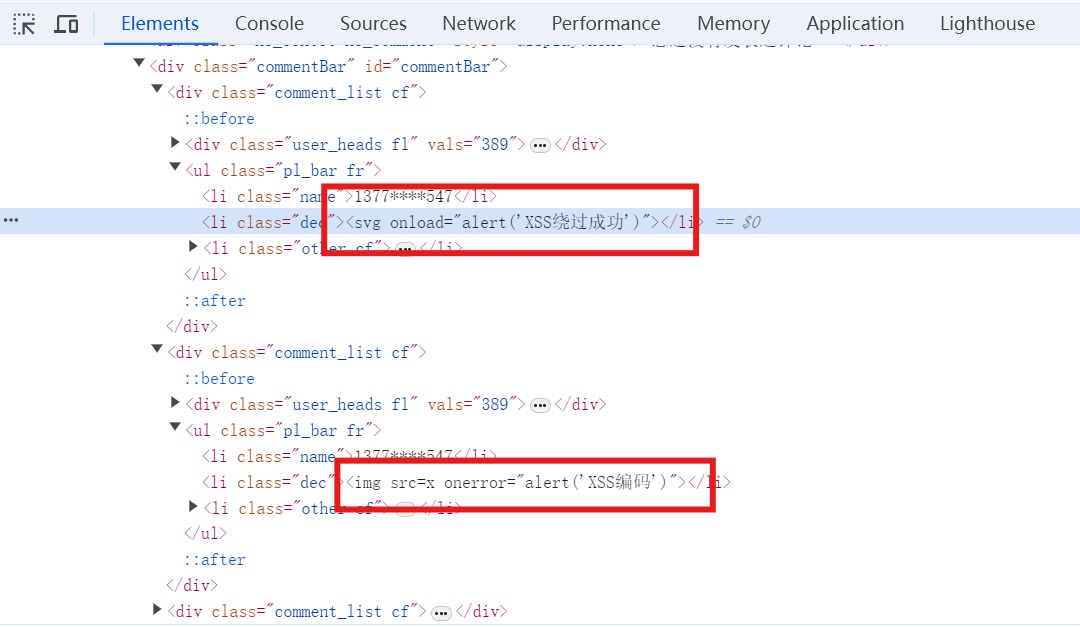 zero-day348/cve-2025-65442-dom-based-cross-site-scripting-xss-vulnerability-in-novel-v3.5.0-cwe-79-
DOM-based Cross-Site Scripting (XSS) Vulnerability in novel V3.5.0 (CWE-79)
 lq0ne/cve-2024-28715
Proof-of-concept exploit for CVE-2024-28715, a DOM-based XSS vulnerability in DoraCMS v2.18 and earlier, triggered via the markdown0 function in the…