
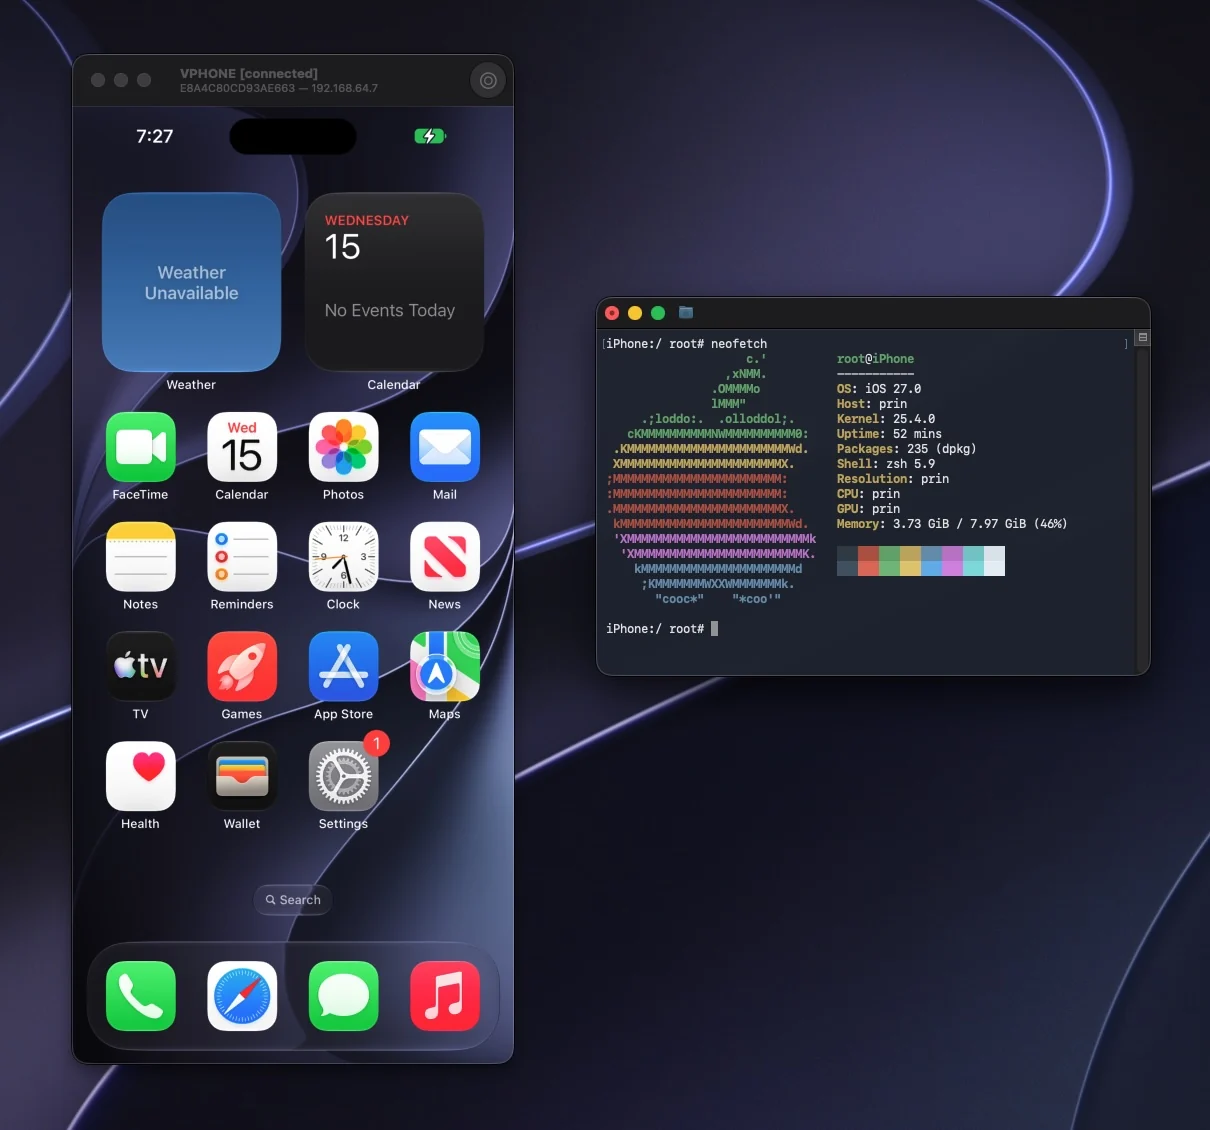
vphone-cli
 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
exploitationfirmware-analysisios-security+3
lakr233/vphone-cliBoot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 0xjohnnydev/cve-2026-20637-applesepkeystore-uaf
CVE-2026-20637: AppleSEPKeyStore Use-After-Free — iOS/macOS kernel vulnerability (patched in 26.4)
 jgoyd/ios18.6.2-persistent-automation-exploit-in-siri-shortcuts-and-apple-swc
This repo documents a vulnerability in Siri Shortcuts and Shared Web Credentials (SWC) allowing malformed payloads to persistently execute, trigger…
 billy-ellis/exr-imageio-poc
PoC for CVE-2026-28990, an ImageIO bug patched in iOS/macOS 26.5
 bomberfish/mandela-legacy
iOS customization app powered by CVE-2022-46689

 shoucheng3/asf__commons-text_cve-2022-42889_1-9
Java library for string manipulation algorithms, packaged with a proof-of-concept exploit for CVE-2022-42889 to demonstrate and test the…
 bazad/blanket
CVE-2018-4280: Mach port replacement vulnerability in launchd on iOS 11.2.6 leading to sandbox escape, privilege escalation, and codesigning bypass.
 cyberblackhole/tokenbreaker
JSON RSA to HMAC and None Algorithm Vulnerability POC
 bytev0rtex/cve-2026-65343
Proof-of-concept for CVE-2026-65343, an out-of-bounds read in AppleKeyStore that leaks kernel pointers to defeat KASLR on iOS 26.6. Includes ACM…
 icrazeios/appenumfix
Jailbreak tweak to patch CVE-2025-31207, a bug that allows sandboxed applications to enumerate a user's installed apps
 h3x0v3rl0rd/cve-2019-6447
Python exploit for CVE-2019-6447 enabling arbitrary file read on ES File Explorer 4.1.9.7.4 for Android. Demonstrates mobile vulnerability…
 phoenhex/files
Curated repository of exploits, proof-of-concept code, and vulnerability research presentations from the phoenhex team, focused on binary…
 jsherman212/iomfb-exploit
iOS 14 kernel exploit for CVE-2021-30807 targeting IOMobileFramebuffer, with tunable memory allocation for jailbreak development on A11+ devices.
 opa334/darksword-kexploit
iOS <=26.0.1 DarkSword Kernel Exploit reimplemented in Objective-C
 anonymous941/zygote-injection-toolkit
A command-line utility to exploit Android Zygote injection (CVE-2024-31317)
 0xjohnnydev/cve-2026-20687-applejpegdriver-uaf
CVE-2026-20687: AppleJPEGDriver startDecoder Timeout UAF — iOS/macOS kernel vulnerability leading to deferred panic (A19 Pro, iOS 26.3 RC)
 bytev0rtex/cve-2026-65330
Proof-of-concept for a fixed PAC diversifier bypass in the tmpfs setxattr handler on iOS 26.6, demonstrating reachability of the vulnerable signing…