

lamda
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
android-securitydynamic-analysis-sandboxingeducation+8
8.5k
firerpa/lamdaAndroid Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 bats3c/shad0w
A post exploitation framework designed to operate covertly on heavily monitored environments
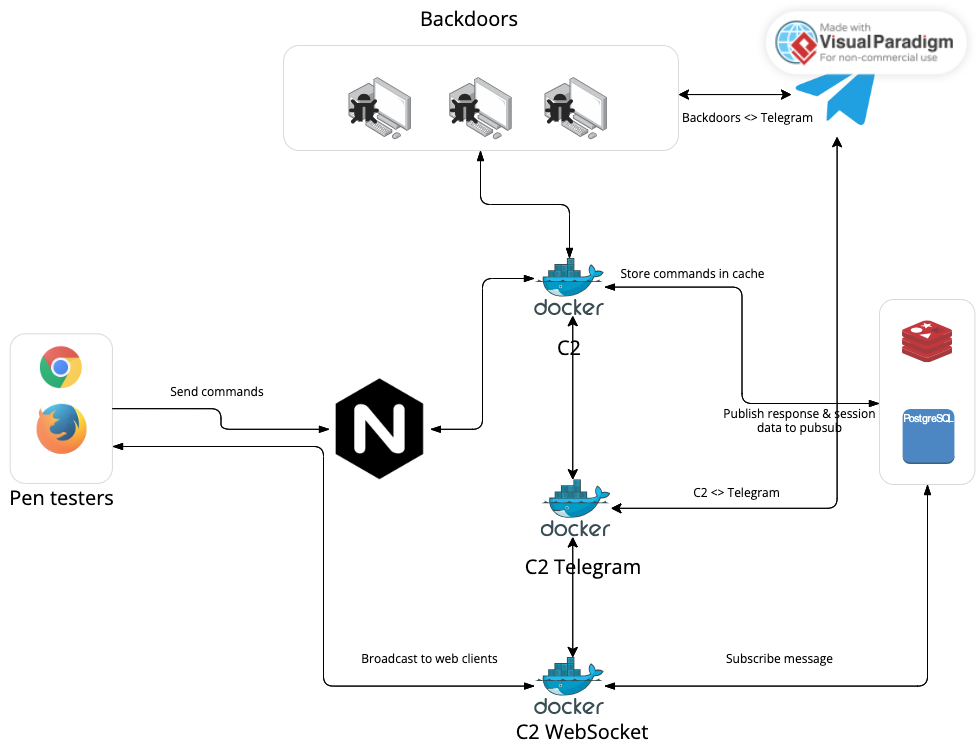 govindasamyarun/c2-cloud
The C2 Cloud is a robust web-based C2 framework, designed to simplify the life of penetration testers. It allows easy access to compromised…
 boundaryx/cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.
 al1ex/cve-2017-7269
Exploit for CVE-2017-7269, a buffer overflow in IIS 6.0 WebDAV, enabling remote code execution. Designed for use with Metasploit in penetration…
 darrynb89/cve-2004-1561
Python port of a Metasploit exploit targeting CVE-2004-1561 for remote code execution. Designed for penetration testing and vulnerability validation…
 dedsec-47/metasploit-exploits-cve-2023-6710
Welcome to the Metasploit Exploits Repository, your go-to resource for a comprehensive collection of cutting-edge exploits designed for penetration…
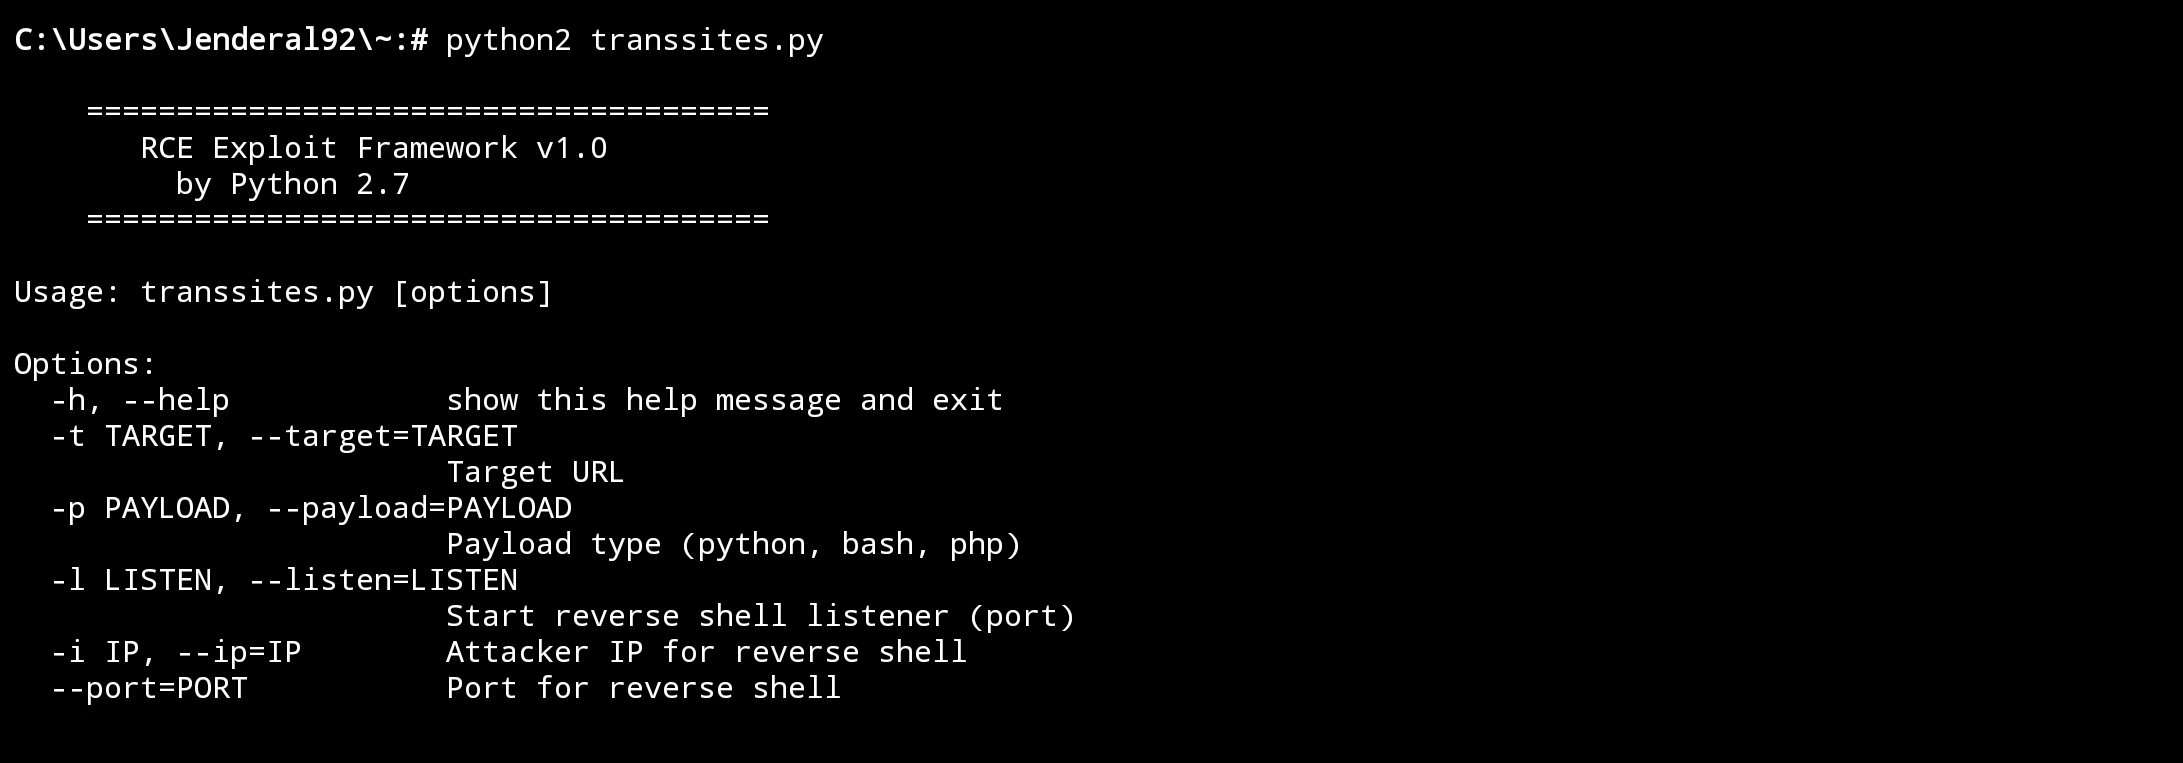 jenderal92/rce-exploit-framework
This framework is designed to assist penetration testers or developers in understanding the mechanics of remote code execution (RCE) exploitation.
 rastating/wordpress-exploit-framework
A Ruby framework designed to aid in the penetration testing of WordPress systems.
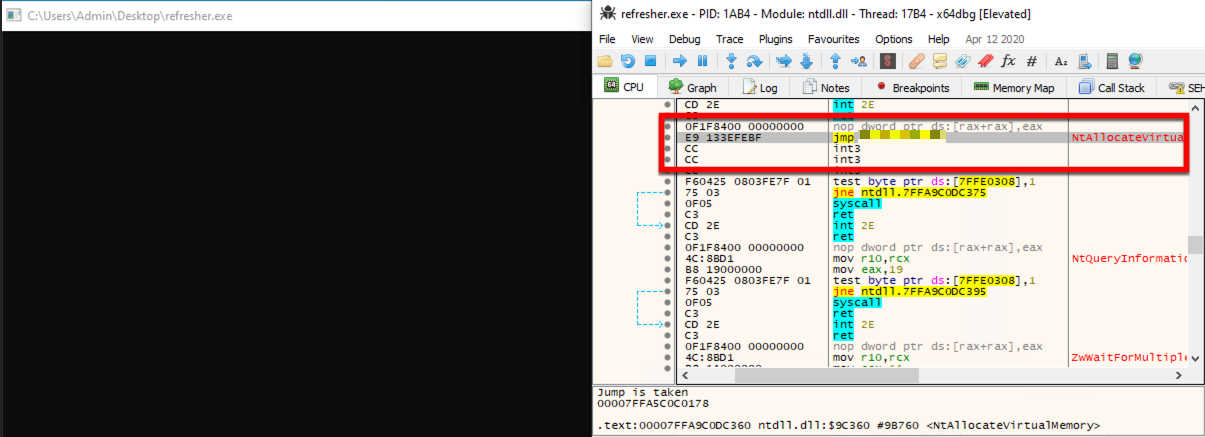 optiv/scarecrow
ScareCrow - Payload creation framework designed around EDR bypass.
 bishopfox/sliver
Adversary Emulation Framework
 apache/caldera
Automated Adversary Emulation Platform
 trustedsec/ptf
The Penetration Testers Framework (PTF) is a way for modular support for up-to-date tools.
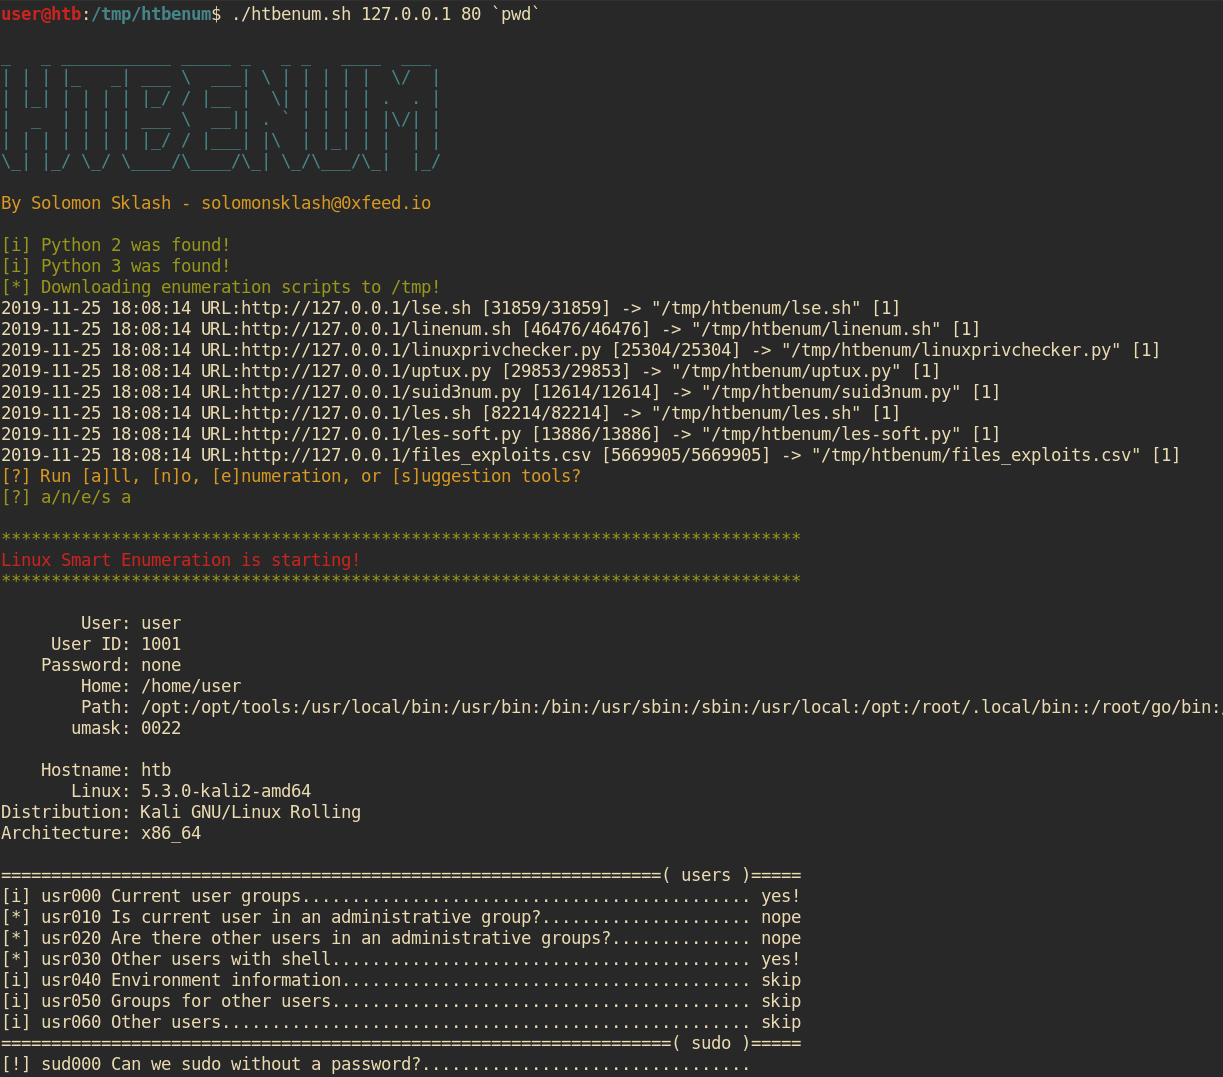 solomonsklash/htbenum
A Linux enumeration script for Hack The Box
 sysdream/pysqli
Python SQL injection framework
 leviticus-triage/chromsploit-framework
Advanced AI-Powered Exploitation Framework | CVE-2025-4664 & CVE-2025-2783 & CVE-2025-2857 & CVE-2025-30397 |