metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Fully autonomous AI Agents system capable of performing complex penetration testing tasks

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…

All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…

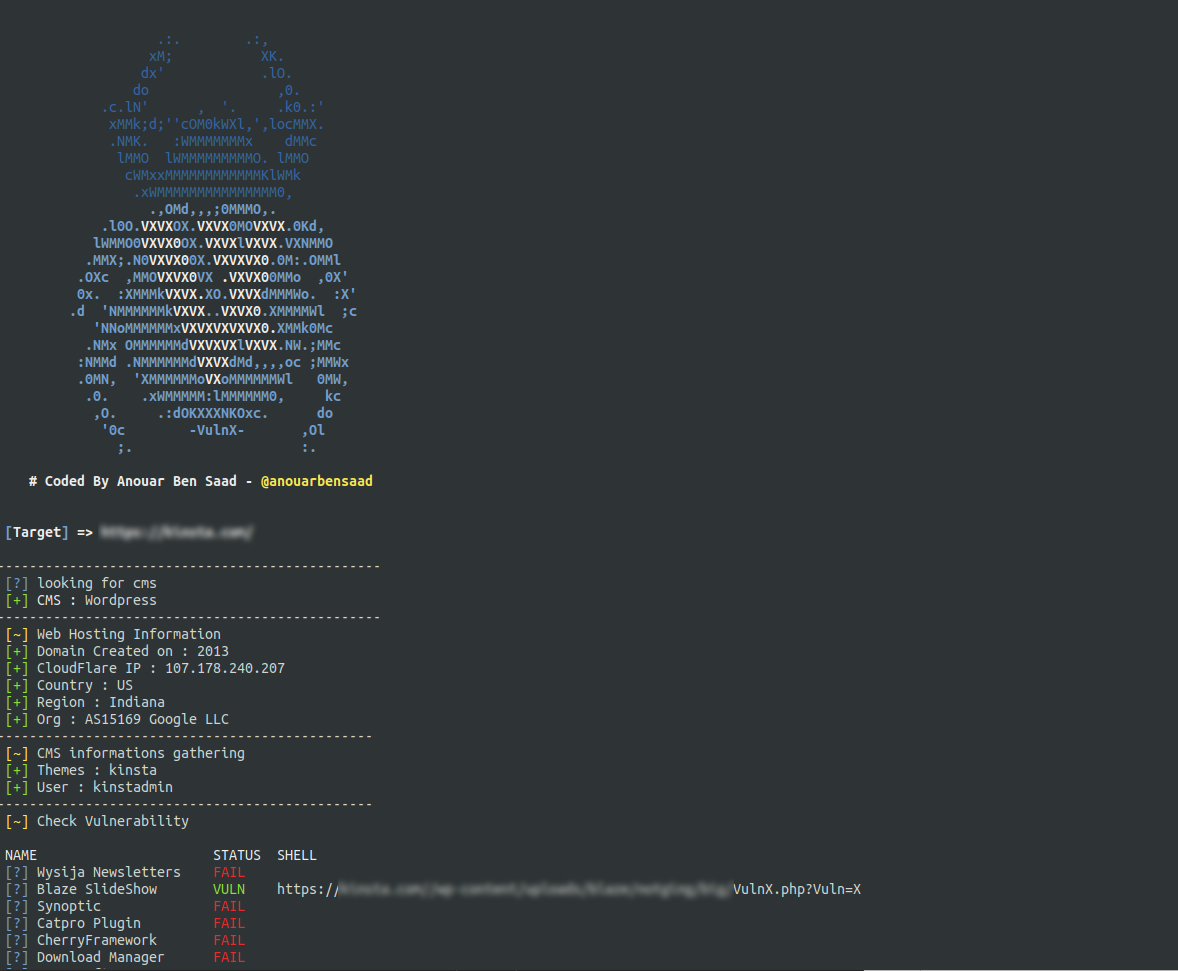
vulnx 🕷️ an intelligent Bot, Shell can achieve automatic injection, and help researchers detect security vulnerabilities CMS system. It can perform…

ARM64 ELF Virtual Machine Protection System

Tool for leaking and bypassing Android malware detection system

CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…

A Beacon Object File (BOF) for Cobalt Strike which uses direct system calls to enable WDigest credential caching.

Local privilege escalation exploit for CVE-2023-36802 targeting Windows kernel streaming service (MSKSSRV) on Windows 11 22H2, using I/O Ring…

Adaptix C2 agent using Crystal Palace PIC linker and PICO module system

Responsive Command and Control System

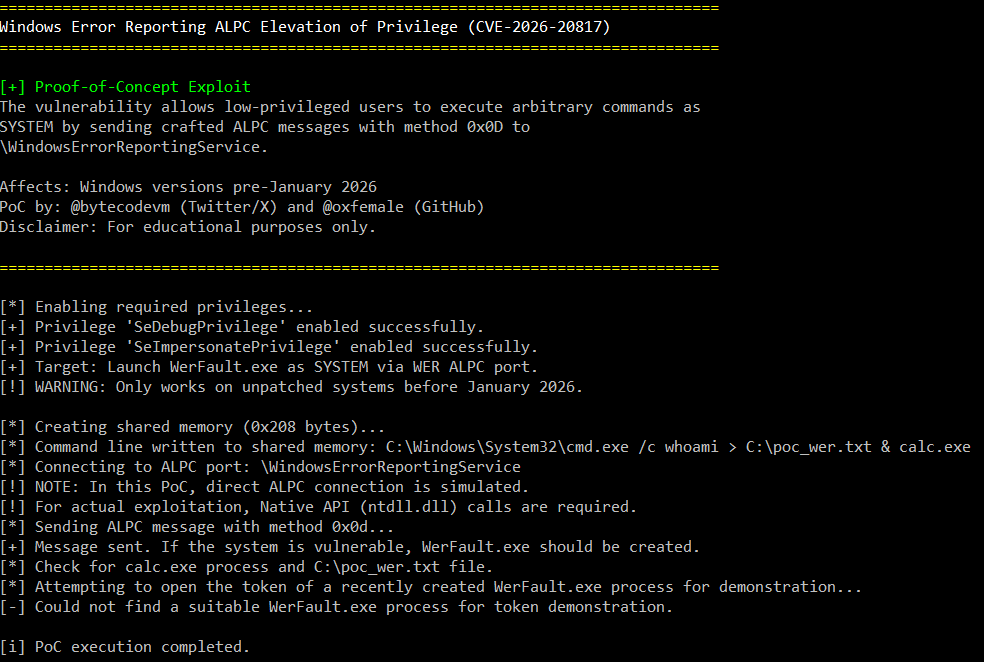
Proof-of-concept exploit for CVE-2026-20817, a local privilege escalation in Windows Error Reporting (WER) via ALPC, allowing low-privileged users to…

Proof-of-concept for CVE-2026-62735, an integer overflow in http.sys leading to heap overflow and SYSTEM shell. Includes crash log and stack trace…

A simple, extensible C&C beaconing system.

CVE-2020-17103 adapted for C2 with split-binary SYSTEM callback

Proof-of-concept exploit for CVE-2026-32223, a heap-based buffer overflow in Windows USB print driver (usbprint.sys), achieving local privilege…